themalwareguardian/cve-2025-34096
SEH-based buffer overflow in Easy File Sharing Web Server 7.2, reachable through the password recovery endpoint.

SEH-based buffer overflow in Easy File Sharing Web Server 7.2, reachable through the password recovery endpoint.
This repository was created as part of the material I use when teaching vulnerability research and exploit development, particularly when introducing the concept of SEH (Structured Exception Handler) overflows and ROP (Return-Oriented Programming) chains.
It is related to my talk "The Path That Leads to Your First CVE". In that talk, I explain that there are different entry points into vulnerability research, and that studying publicly documented CVEs in legacy software is one of the most accessible paths for beginners.
This CVE was chosen because it demonstrates a complete and realistic exploitation scenario:
The goal is to use this case as a stepping stone between introductory buffer overflow exercises and more advanced exploit development concepts.
This vulnerability affects Easy File Sharing Web Server 7.2, a lightweight Windows web server application that was widely used for simple file sharing. The software was written without modern security mitigations in mind. What makes this case particularly interesting from a teaching perspective is the combination of factors involved:
This combination makes CVE-2025-34096 an excellent case for teaching exploit development techniques in a realistic unauthenticated attack scenario.
Easy File Sharing Web Server 7.2 is a lightweight Windows application built for sharing files over HTTP. Beyond basic file browsing and user accounts, it includes a password recovery feature, a form that lets users enter their email address to receive their forgotten credentials.
That form posts to /sendemail.ghp. The handler that processes the Email field copies the value straight into a fixed-size stack buffer with no length check. The endpoint needs no authentication, so there is nothing standing between a remote attacker and the vulnerable code path.
Key technical details:
Easy File Sharing Web Server processes HTTP POST requests directed to /sendemail.ghp as part of its email notification feature. The Email parameter accepted by this endpoint is copied into a local stack buffer without any length check.
A simplified version of the vulnerable logic looks like this:
char email_buffer[256];

strcpy(email_buffer, user_input);
Since the destination buffer has a fixed size and the input length is not validated, sending a sufficiently long string in the Email field causes the copy to write past the end of the buffer.
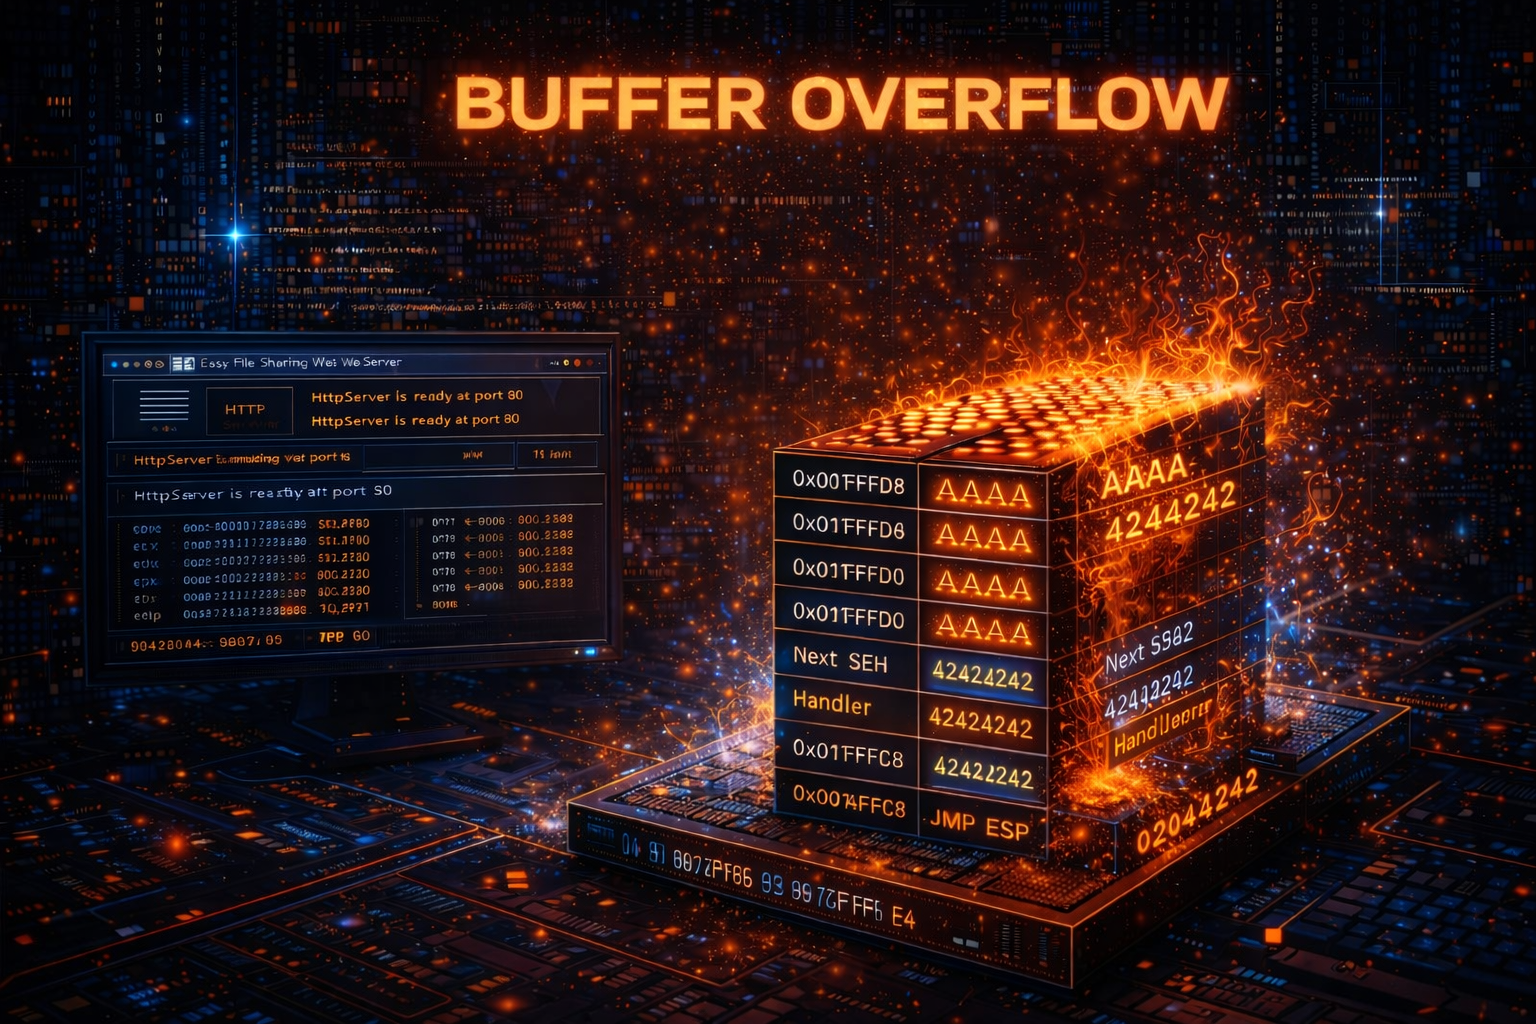
As more data is written, the stack layout becomes corrupted. Unlike a simple return address overwrite, the overflow reaches the Structured Exception Handler (SEH) chain stored on the stack. When an exception is triggered as a result of the corrupted stack, the OS walks the SEH chain and transfers control to the attacker-controlled handler address.
The exploitation flow therefore follows the SEH overwrite technique:
This makes the vulnerability more complex to exploit than a basic EIP overwrite, but also more representative of real-world scenarios.
The crash can be reproduced by sending a long string in the Email parameter of a POST request to /sendemail.ghp. No authentication is required. Example using Python:
import socket

HOST = '127.0.0.1'
PORT = 80

request = (
	'POST /sendemail.ghp HTTP/1.1\r\n'
	'Email=' + 'A' * 5000 + '&getPassword=Get+Password'
).encode('utf-8')

s = socket.socket(socket.AF_INET, socket.SOCK_STREAM)
s.connect((HOST, PORT))
s.send(request)
s.close()
When executed under a debugger, the crash shows a corrupted SEH chain and an access violation, confirming that user-controlled data has overwritten the exception handler pointer.
The goal of this repository is not only to demonstrate the crash, but also to walk through the complete exploitation process step by step, following the methodology used when developing real SEH-based exploits.
To keep the main README clean, the detailed exploitation notes, scripts, and debugger steps are placed inside the Vulnerability 📂 folder of this repository.
There you will find the complete workflow used to exploit this CVE, including: