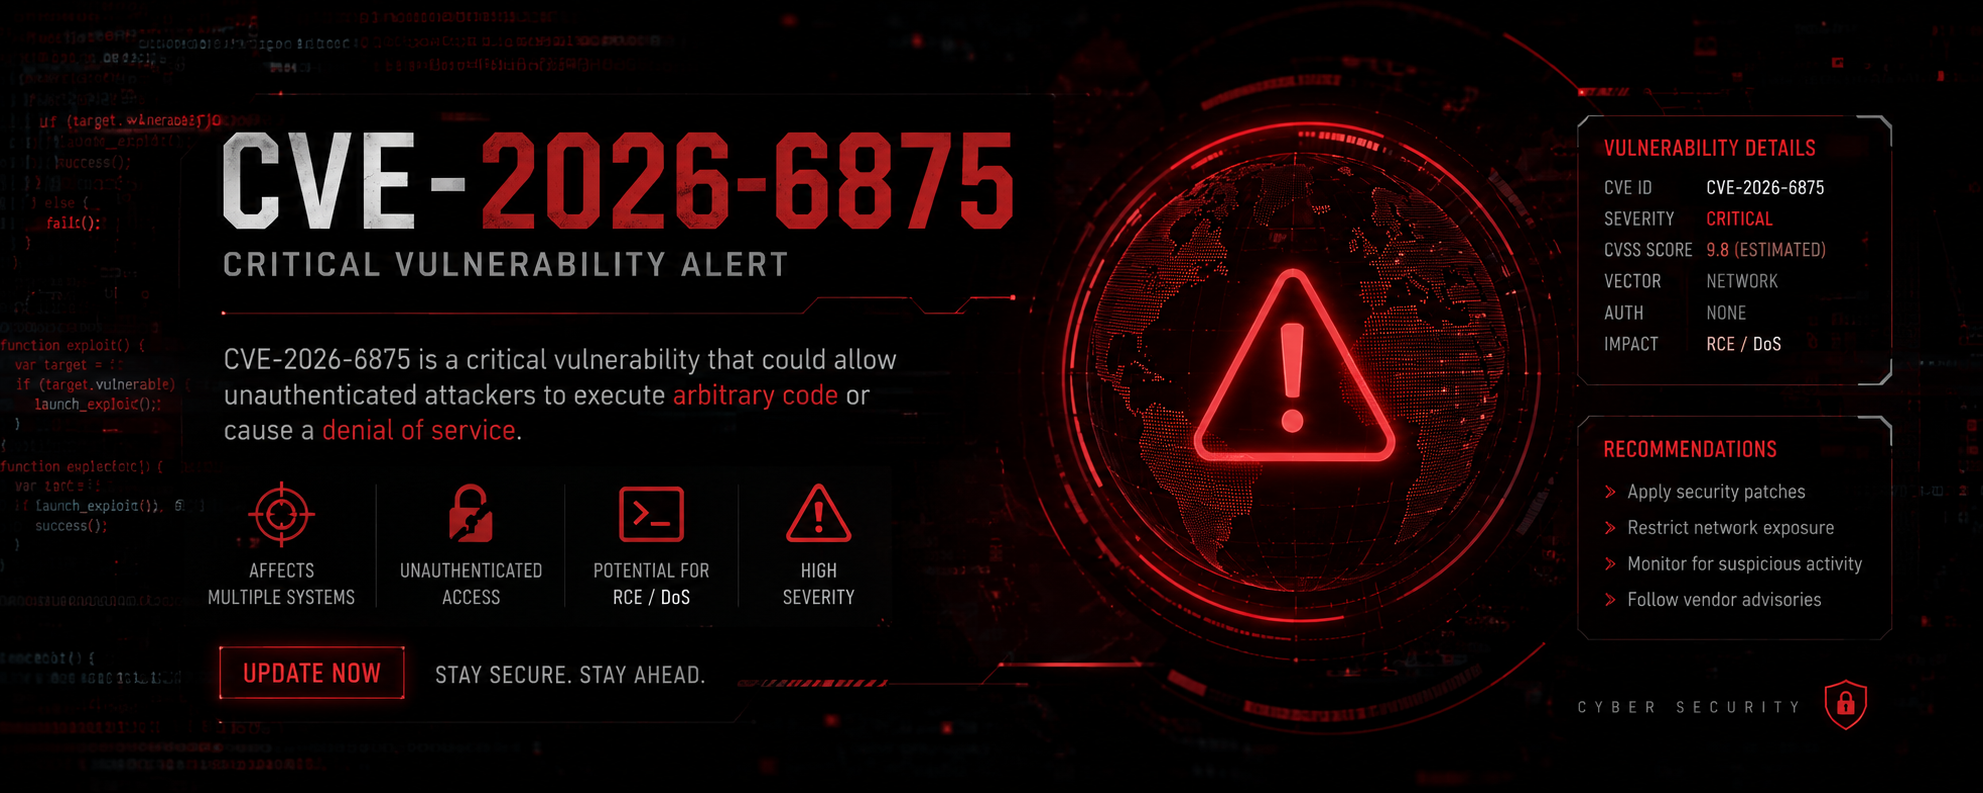
CVE-2026-6875 ServiceNow Pre-Auth RCE Framework 🔥 JS Injection → Sandbox Escape → RCE → Root. Features: --detect, --exec, reverse/interactive shell, batch threading, WAF bypass, persistence, lateral movement, credential dump, fileless exec, clean tracks. 🛡️ CVSS 9.5 actively exploited. Authorized & Legal use only. Stay Legal. 🔒
 tc4dy/cve-2026-6875-poc-exploit

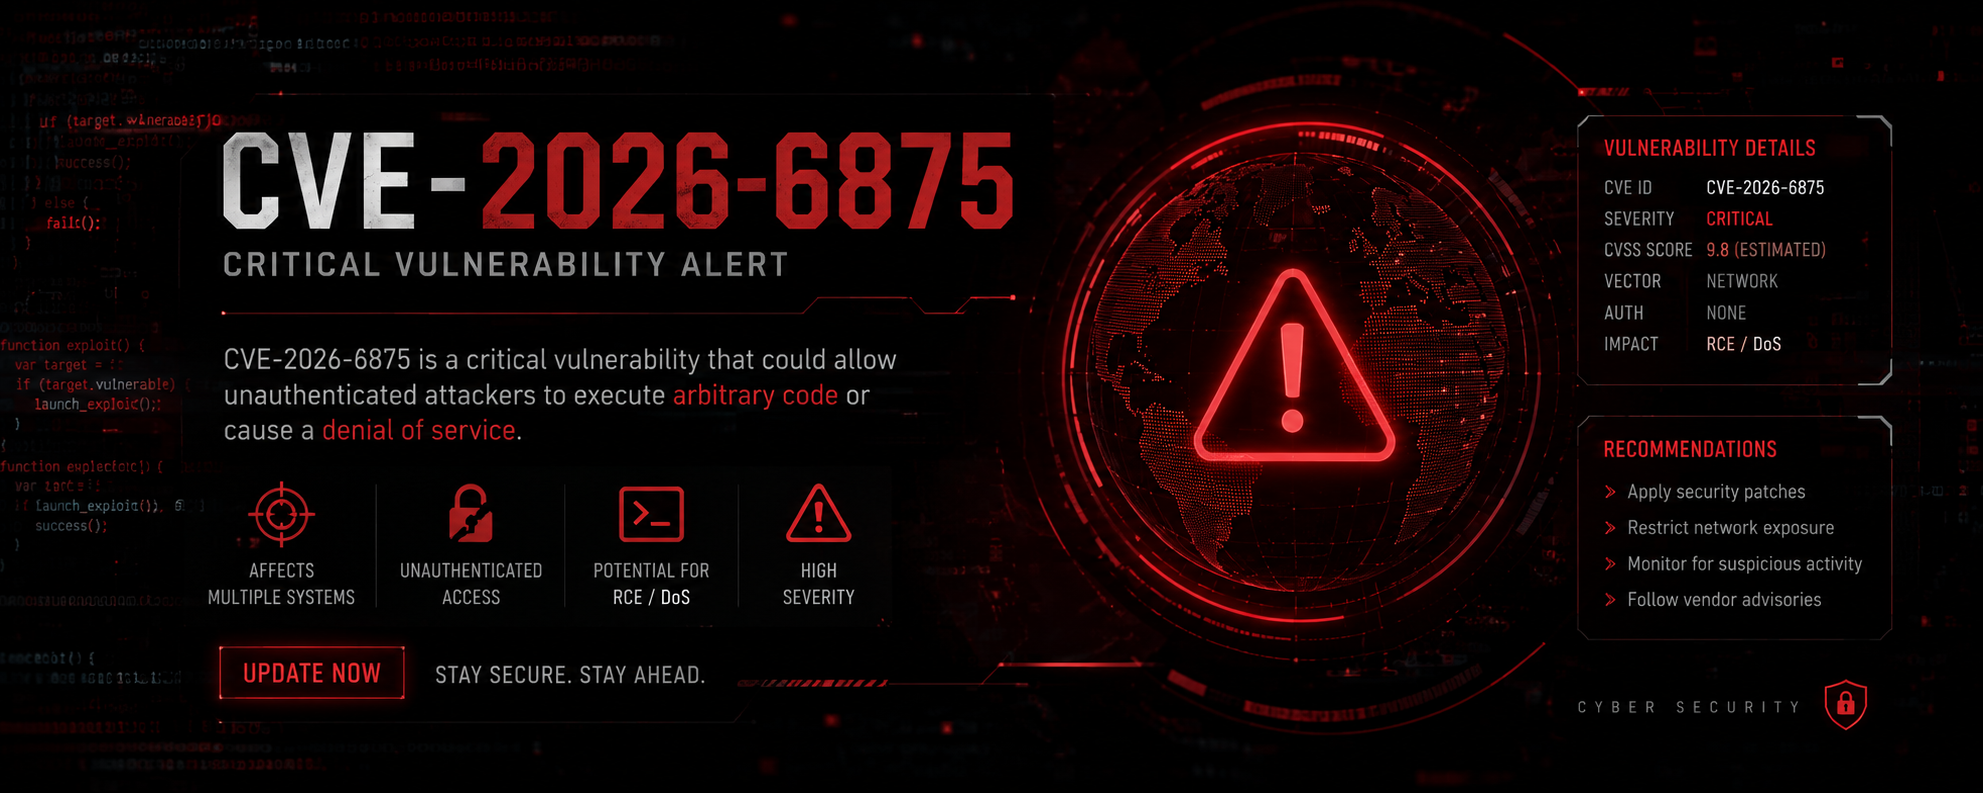


Exploit Framework & Safe Verifier
For authorized security testing only.
This tool is provided for educational and authorized penetration testing purposes only.
The authors and contributors are not responsible for any misuse or damage caused by this software. Users are solely responsible for ensuring they have explicit written permission from the target owner before testing. Unauthorized access to computer systems is illegal under the Computer Fraud and Abuse Act (CFAA) and similar laws worldwide.
By using this software, you agree to:
⚠️ WARNING: This vulnerability is actively exploited in the wild. Unauthorized use may result in severe legal consequences.
CVE-2026-6875 is a critical unauthenticated Remote Code Execution (RCE) vulnerability in the ServiceNow AI Platform (formerly Now Platform). It allows attackers to bypass the script sandbox and execute arbitrary system commands with the privileges of the ServiceNow application.
JavaScript Injection: The assessment_thanks.do endpoint accepts a sysparm_assessable_type parameter. By prefixing the value with javascript:, an attacker injects arbitrary JavaScript code.
Sandbox Escape: A sophisticated sandbox‑escape gadget (chaining DiscoveryFunctions.getCacheObjectForTable, AbstractAjaxProcessor, and Class.create) lifts the JavaScript sandbox restriction.
Remote Code Execution: The injected Java code (via java.lang.Runtime.exec()) runs with ServiceNow application privileges, enabling full system compromise.
Privilege Escalation: Post‑exploitation modules attempt to escalate to root via sudo misconfigurations, SUID binaries, writable cron jobs, or kernel exploits.
| Attribute | Value |
|---|---|
| 📅 Discovered | April 1, 2026 (Searchlight Cyber) |
| ⚠️ CVSS Score | 9.5 (CRITICAL) |
| 📋 CISA KEV | Added July 13, 2026 |
| 🎯 Affected Products | Self‑hosted ServiceNow AI Platform |
| 🔄 Fixed Versions | Brazil EA/GA, Australia Patch 2, Zurich Patch 7b/9, Yokohama Patch 12 Hot Fix 1b/13 |
| 🔓 Authentication | Not required (Pre‑Auth) |
| 🌍 Active Exploitation | Confirmed in the wild (July 2026) |
exploit.py)The full weaponized exploit chains the JavaScript injection and sandbox escape to achieve remote code execution, with advanced post‑exploitation modules for persistence, lateral movement, and credential dumping.
| Feature | Description |
|---|---|
| 🚀 JavaScript Injection | Injects payload via sysparm_assessable_type parameter. |
| 💻 Sandbox Escape | Bypasses ServiceNow's script sandbox to run arbitrary Java code. |
| 🔐 Interactive Shell | Spawn a live shell with support for multiple commands. |
| 👑 Root Privesc | Checks for sudo misconfigurations, SUID binaries, and cron jobs. |
| 📁 File Operations | Upload webshells, read/download files via base64 encoding. |
| 🌐 Batch Scanning | Mass exploit multiple targets with threading (-l flag). |
| 🎯 Safe Detection | Optional --detect flag for non‑intrusive vulnerability verification. |
| ⚙️ WAF Bypass | Built‑in obfuscation techniques to evade WAF/IDS (6 techniques). |
| 🧩 Persistence | Installs cron/systemd/schtasks backdoors. |
| 🔍 Lateral Movement | Scans local network for other vulnerable hosts and attempts SSH/SSRF propagation. |
| 🧹 Clean Tracks | Removes logs, bash history, and audit trails. |
| 💾 Fileless Execution | Uses Java ClassLoader to run memory‑resident payloads without writing to disk. |
| 🔌 Callback Server | Built‑in HTTP server to receive command output (optional). |
| 📢 Webhook Notifications | Sends results to a custom URL (Slack, Discord, etc.). |
| 🪟 Cross‑Platform | Supports Linux and Windows targets (cmd.exe / PowerShell). |
| 🔒 Thread‑Safe | Uses locking mechanisms for concurrent operations. |
| 📊 Version Detection | Detects ServiceNow version (Zurich/Brazil/Australia/Yokohama). |
| Command | Description |
|---|---|
exec <cmd> | Execute system command |
upload <local> [remote] | Upload webshell to target |
download <remote> | Download and display file content |
privesc | Attempt privilege escalation |
reverse <host> <port> | Send reverse shell |
dumpcred | Dump credentials from ServiceNow configs |
persist <host> <port> | Install persistence (cron/systemd/schtasks) |
lateral | Attempt lateral movement |
clean | Clean tracks (logs, history) |
memory <host> <port> | Execute fileless Java payload |
exit | Exit interactive shell |
verifier.py)The safe verifier performs non‑intrusive vulnerability detection without executing harmful payloads or making system changes.
| Feature | Description |
|---|---|
| 🔍 ServiceNow Detection | Identifies ServiceNow instances via multiple endpoints. |
| 📊 Version Detection | Detects specific ServiceNow releases and patch levels. |
| 🧪 JavaScript Injection Test | Tests for injection vulnerability using safe gs.print() payloads. |
| 🔒 Sandbox Escape Test | Verifies sandbox escape without destructive commands. |
| 📈 Confidence Scoring | Provides confidence percentage (85‑95%) based on evidence. |
| 📋 JSON Output | Export results to JSON format for reporting. |
| 🔄 Mass Scanning | Scan multiple targets with threading support. |
| 🎯 Non‑Intrusive | Only executes benign uname -a for system info. |
pip (for requests library)pip install requests urllib3
[!NOTE]
exploit.pyuses only the standard library for core functionality;requestsis only required for the--detectfeature,--webhooknotifications, and safe verifier.
verifier.py)