🌐 Language / Dil
English
📋 Table of Contents
🎯 Overview
CVE-2025-8088 is a fictional vulnerability demonstration tool that showcases path traversal attacks in RAR archive files. This educational tool demonstrates how malicious archives can exploit directory traversal techniques to extract files outside their intended extraction directory.
- Creates specially crafted RAR archives
- Demonstrates path traversal vulnerabilities
- Uses Advanced Data Streams (ADS) techniques
- Implements payload obfuscation with AES encryption
- Targets Windows Startup directory for persistence
✨ Features
🖥️ Modern GUI Interface
- Dark Mode Theme - Professional appearance
- Multi-language Support - English & Turkish
- Responsive Design - Adapts to different screen sizes
- Real-time File Management - Add/remove files with visual feedback
- Integrated Help System - Comprehensive FAQ and usage guide
🛠️ Advanced Capabilities
- Multiple Payload Support - Process multiple executable files
- Decoy File Integration - Hide malicious intent with innocent files
- AES Encryption - Secure payload obfuscation
- XOR Encoding - Additional layer of security
- Path Traversal Generation - Automatic target path construction
- CRC Validation - Ensures archive integrity
🎨 User Experience
- Drag & Drop Support - Easy file selection
- Progress Indicators - Visual feedback during operations
- Error Handling - Comprehensive error reporting and logging
- Context Menus - Right-click file management
- Auto-sizing - Dynamic interface adaptation
📋 Requirements
System Requirements
- Operating System: Windows 10/11 (64-bit)
- Python: 3.8 or higher
- WinRAR: Must be installed for archive creation
- Memory: Minimum 4GB RAM
- Storage: 100MB free space
Python Dependencies
customtkinter==5.2.0
pycryptodome==3.23.0
🚀 Installation
Step 1: Clone Repository
git clone https://github.com/syrins/CVE-2025-8088-Winrar-Tool.git
cd CVE-2025-8088-Winrar-Tool
Step 2: Install Dependencies
pip install -r requirements.txt
Step 3: Verify WinRAR Installation
Ensure WinRAR is installed in one of these locations:
C:\Program Files\WinRAR\rar.exeC:\Program Files (x86)\WinRAR\rar.exe
Step 4: Run the Application
python gui.py
🎮 Usage
Quick Start Guide
-
Launch Application
python gui.py
-
Add Payload Files
- Click "Add Payload" button
- Select executable files (.exe, .bat, .com, etc.)
- Multiple files supported
-
Add Decoy Files (Optional)
- Click "Add Decoy" button
- Select innocent-looking files (.txt, .pdf, .doc, etc.)
- Helps disguise malicious intent
-
Configure Settings
- Set fallback username (default: Administrator)
- Enter output archive name
- Choose language preference
-
Generate Archive
- Click "Build" button
- Archives will be created in
output/ directory
File Management
- Right-click any file to remove it
- Hover over files for visual feedback
- Files are automatically renamed if too long
🔧 Technical Details
Architecture Overview
┌─────────────────┐    ┌──────────────────┐    ┌─────────────────┐
│   GUI Layer     │───▶│  Exploit Core    │───▶│  WinRAR CLI     │
│  (gui.py)       │    │ (exploit_base.py)│    │                 │
└─────────────────┘    └──────────────────┘    └─────────────────┘
Exploitation Process
-
Payload Preparation
- AES-256-CBC encryption
- XOR encoding layer
- Random padding insertion
-
Archive Creation
- Base RAR generation with WinRAR CLI
- ADS (Alternate Data Stream) attachment
- Path traversal string injection
-
Header Manipulation
- RAR5 format parsing
- CRC32 recalculation
- Placeholder replacement
-
Target Path Construction
..\..\..\..\..\..\..\..\Users\[USERNAME]\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\
Encryption Scheme
Original Payload → AES-256-CBC → XOR Encoding → Random Padding → Final Archive
Supported File Types
- Payloads:
.exe, .bat, .com, .scr, .pif
- Decoys:
.txt, .pdf, .doc, .jpg, .png, .*
📸 Screenshots
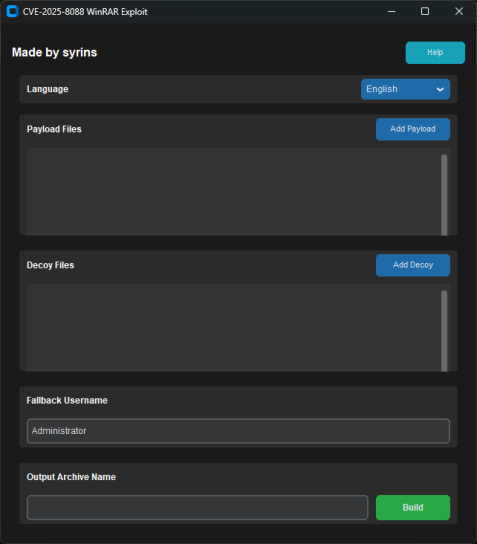
Main Interface
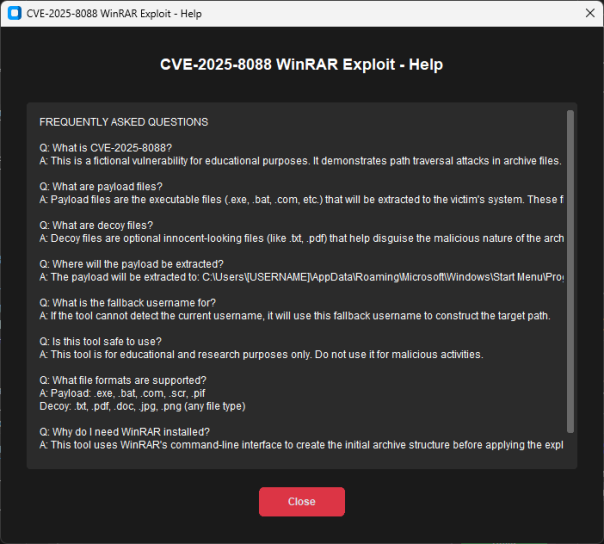
Help System
⚠️ Disclaimer
IMPORTANT LEGAL NOTICE
This tool is created for EDUCATIONAL AND RESEARCH PURPOSES ONLY. The author and contributors:
- ✅ DO NOT encourage malicious use
- ✅ ARE NOT responsible for misuse
- ✅ PROVIDE this for security research only
- ✅ RECOMMEND using in controlled environments only
Ethical Usage Guidelines
- Use only in authorized testing environments
- Obtain proper permissions before testing
- Report vulnerabilities responsibly
- Respect applicable laws and regulations
🤝 Contributing
Contributions are welcome! Please:
- Fork the repository
- Create a feature branch
- Make your changes
- Submit a pull request
Development Setup
git clone https://github.com/your-username/CVE-2025-8088-Winrar-Tool.git
cd CVE-2025-8088-Winrar-Tool
pip install -r requirements.txt
📞 Support
Türkçe
📋 İçindekiler
🎯 Genel Bakış
CVE-2025-8088, RAR arşiv dosyalarında yol geçiş saldırılarını gösteren kurgusal bir güvenlik açığı demonstrasyon aracıdır. Bu eğitim aracı, kötü niyetli arşivlerin dizin geçiş tekniklerini kullanarak dosyaları hedeflenen çıkarma dizini dışına nasıl çıkarabileceğini gösterir.
🔍 Bu Araç Ne Yapar:
- Özel olarak hazırlanmış RAR arşivleri oluşturur
- Yol geçiş güvenlik açıklarını gösterir
- Gelişmiş Veri Akışları (ADS) tekniklerini kullanır
- AES şifreleme ile yük gizleme uygular
- Kalıcılık için Windows Başlangıç dizinini hedefler
✨ Özellikler
🖥️ Modern GUI Arayüzü
- Karanlık Mod Teması - Profesyonel görünüm
- Çok Dil Desteği - İngilizce ve Türkçe
- Duyarlı Tasarım - Farklı ekran boyutlarına uyum
- Gerçek Zamanlı Dosya Yönetimi - Görsel geri bildirimle dosya ekleme/çıkarma
 syrins/cve-2025-8088-winrar-tool-gui


