
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2020-27368 — TOTOLINK-A702R-V1.0.0-B20161227.1023 Directory Indexing Vulnerability | Kitploit
Tools/GitHubGitHub/swzhouu/cve-2020-27368
Embedded Systems SecurityIoT SecurityVulnerability AnalysisInformation GatheringWeb SecurityMisconfigurationArchived
GitHubswzhouu/cve-2020-27368

CVE-2020-27368

TOTOLINK-A702R-V1.0.0-B20161227.1023 Directory Indexing Vulnerability

View Repository
1573 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2020-27368

TOTOLINK-A702R-V1.0.0-B20161227.1023 Directory Indexing Vulnerability

Description

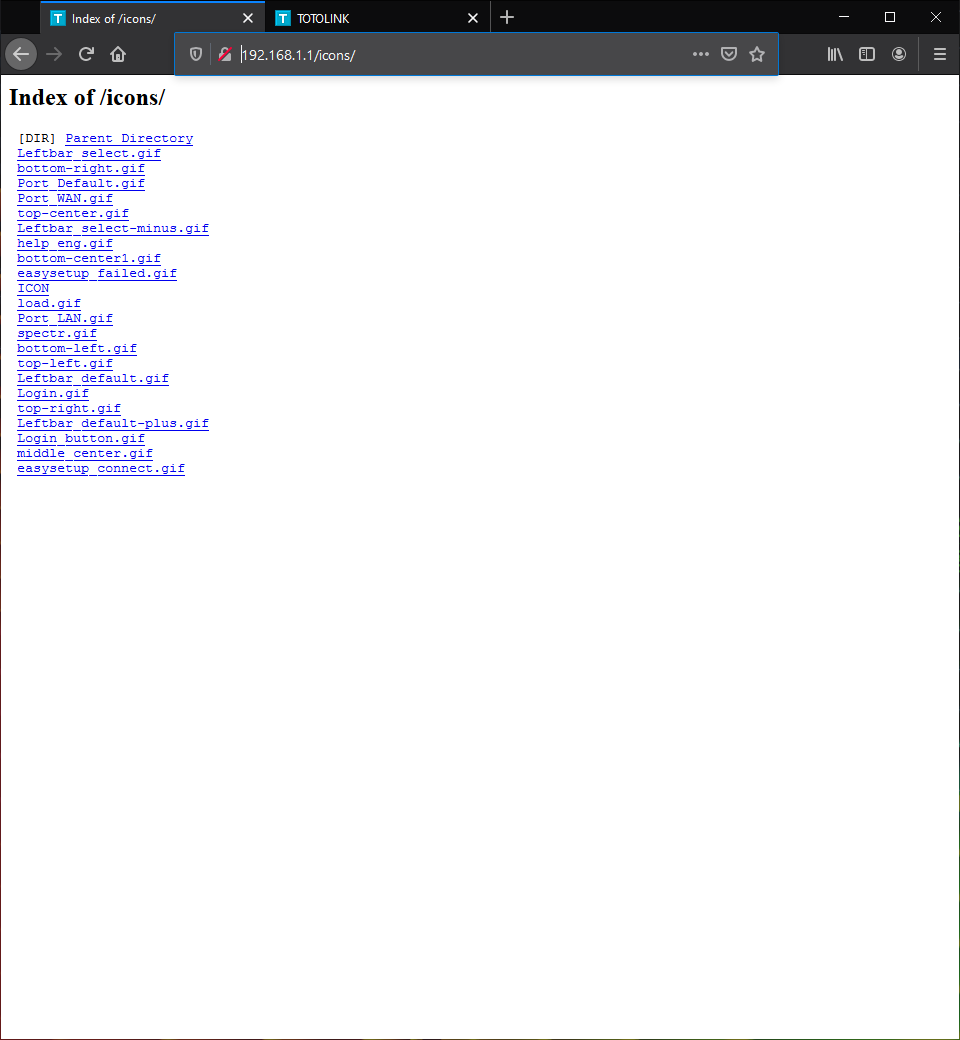
Directory Indexing in Login Portal of Login Portal of TOTOLINK-A702R-V1.0.0-B20161227.1023 allows attacker to access /icons/ directories via GET Parameter.

Additional Information

Remediation disabling directory listing for web server.

VulnerabilityType

Directory Indexing

Vendor of Product

TOTOLINK

Affected Product Code Base

TOTOLINK-A702R-V1.0.0-B20161227.1023 - Model No. A702R (Firmware V1.0.0)

Affected Component

Login Portal of TOTOLINK-A702R-V1.0.0-B20161227.1023.

Attack Type

Local

Impact Information Disclosure

true

Discoverer

Jiraput Thamsongkrah

Proof of Concept

Alt text

Download Tool