 sseshachala/conductai
Runtime governance for AI agents. Allow, warn, or block every model and tool call before it commits. Hash-chained audit for every decision. Compliance packs for SOC 2, HIPAA, PCI DSS, EU AI Act, SR 11-7, and FDA CSA. Apache 2.0.


Governance for AI agents. Ship in 60 seconds.
Built for engineering teams. Install in 10 minutes. Evidence for the CISO from day one.
curl -fsSL conductai.ai/install | sh
Prompts for email + company, provisions a 7-day trial workspace, drops ~/.conduct/env with ANTHROPIC_BASE_URL + OPENAI_BASE_URL + a trial token (200 requests/day shared across both providers). Any Anthropic- or OpenAI-SDK client on the machine (Cursor, Claude Code, LangChain, LiteLLM, raw SDK) now routes through the Guard proxy. A blocked call comes back with a Receipt: https://conductai.ai/theguard/blocks/… URL — click it to view the block, ask Lens follow-up questions, and log in to the dashboard via the magic-link the installer prints.
pip install conduct-cli
conduct login
conduct sync
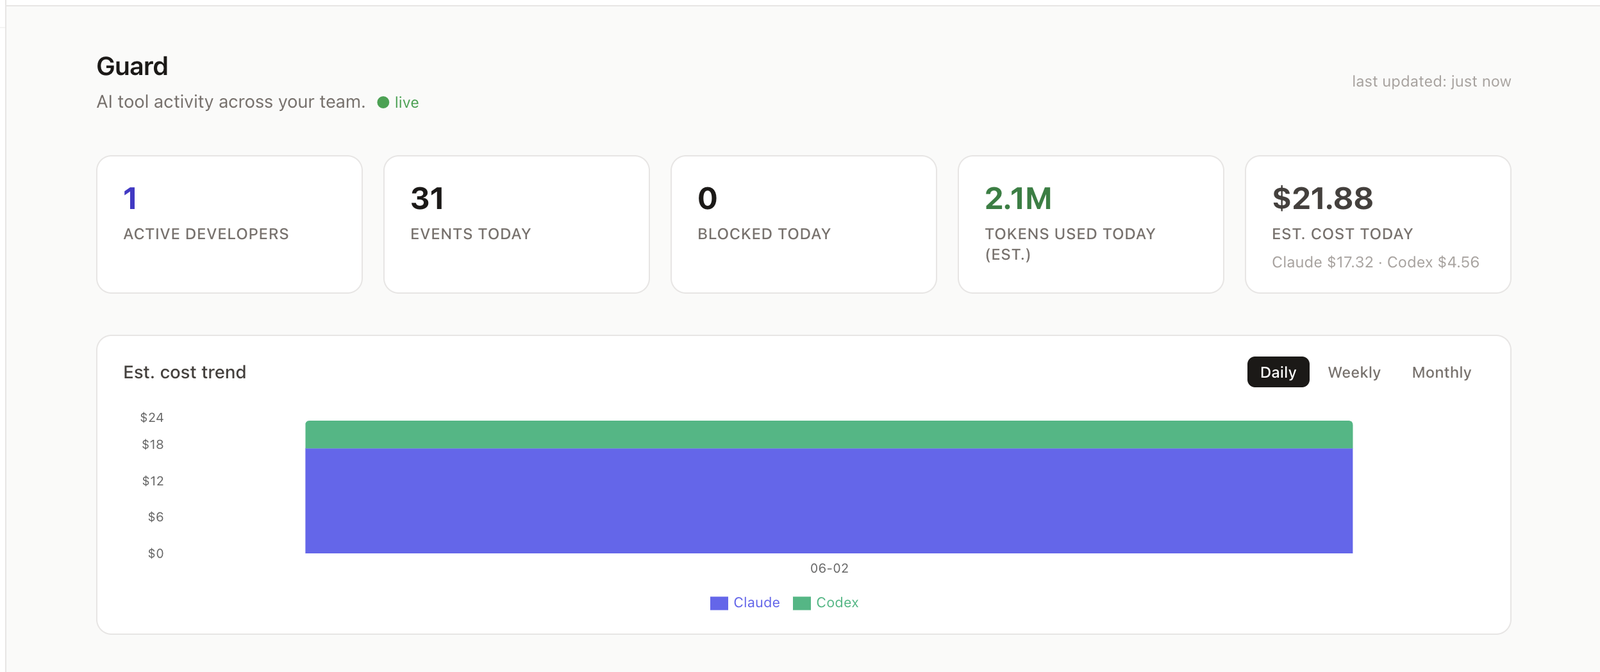
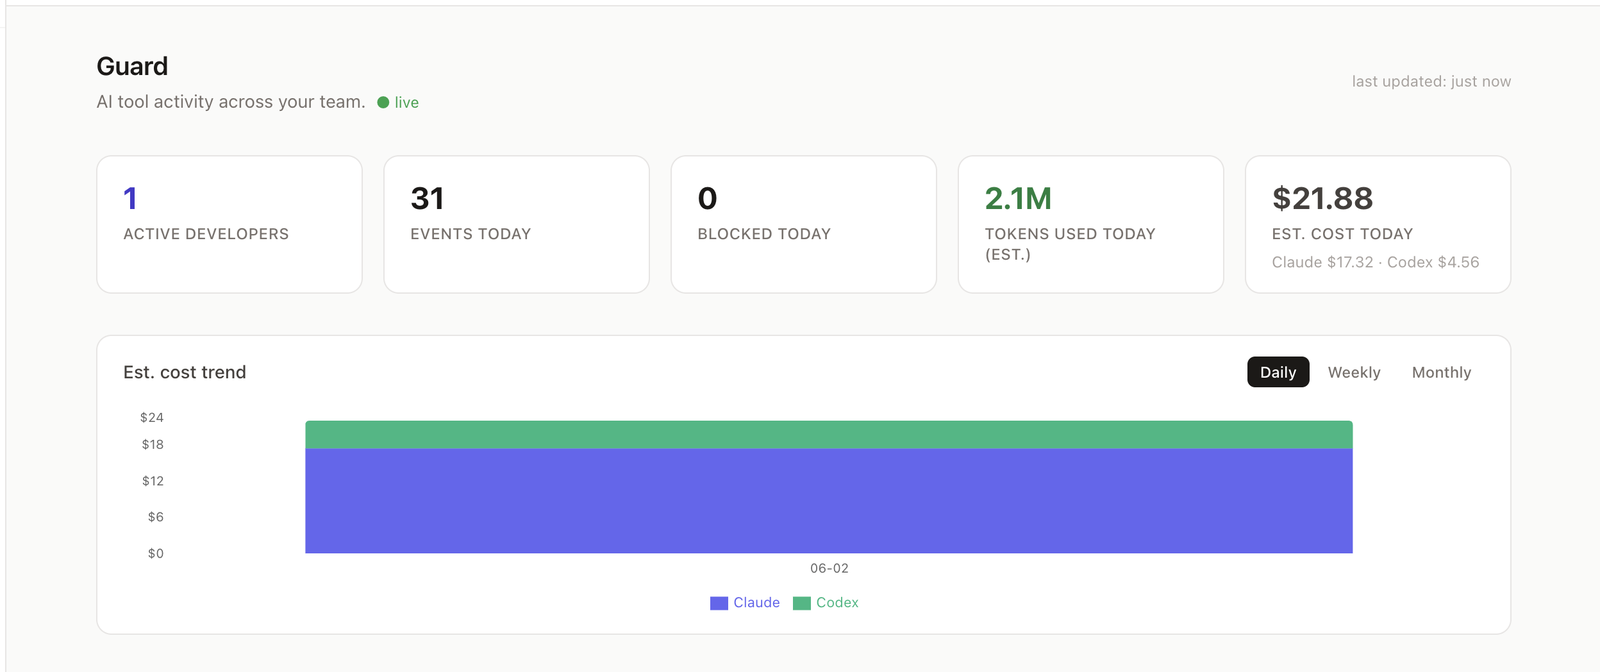
Every Claude Code, Cursor, Copilot, and Codex session on that machine is now governed. Blocks, warnings, and a hash-chained audit trail show up at conductai.ai.
git clone https://github.com/sseshachala/conductai && cd conductai && docker compose up
# API: localhost:8000  ·  Canvas UI: localhost:3000
A control plane for AI agents. One policy decides block / warn / audit / inject for every LLM call, every shell tool, every MCP invocation, before the action runs. Same policy applies to a scheduled agent, a developer running Cursor, and a chat session on the platform.
Three surfaces, one policy:
| Surface | What it does |
|---|---|
| Guard | Policy engine. Signed config, hash-chained audit, fail-closed. |
| Router | LLM proxy. Any SDK (Anthropic, OpenAI, Perplexity) points at it. |
| Lens | Chat surface. Ask your workspace anything, every tool call runs through Guard. |
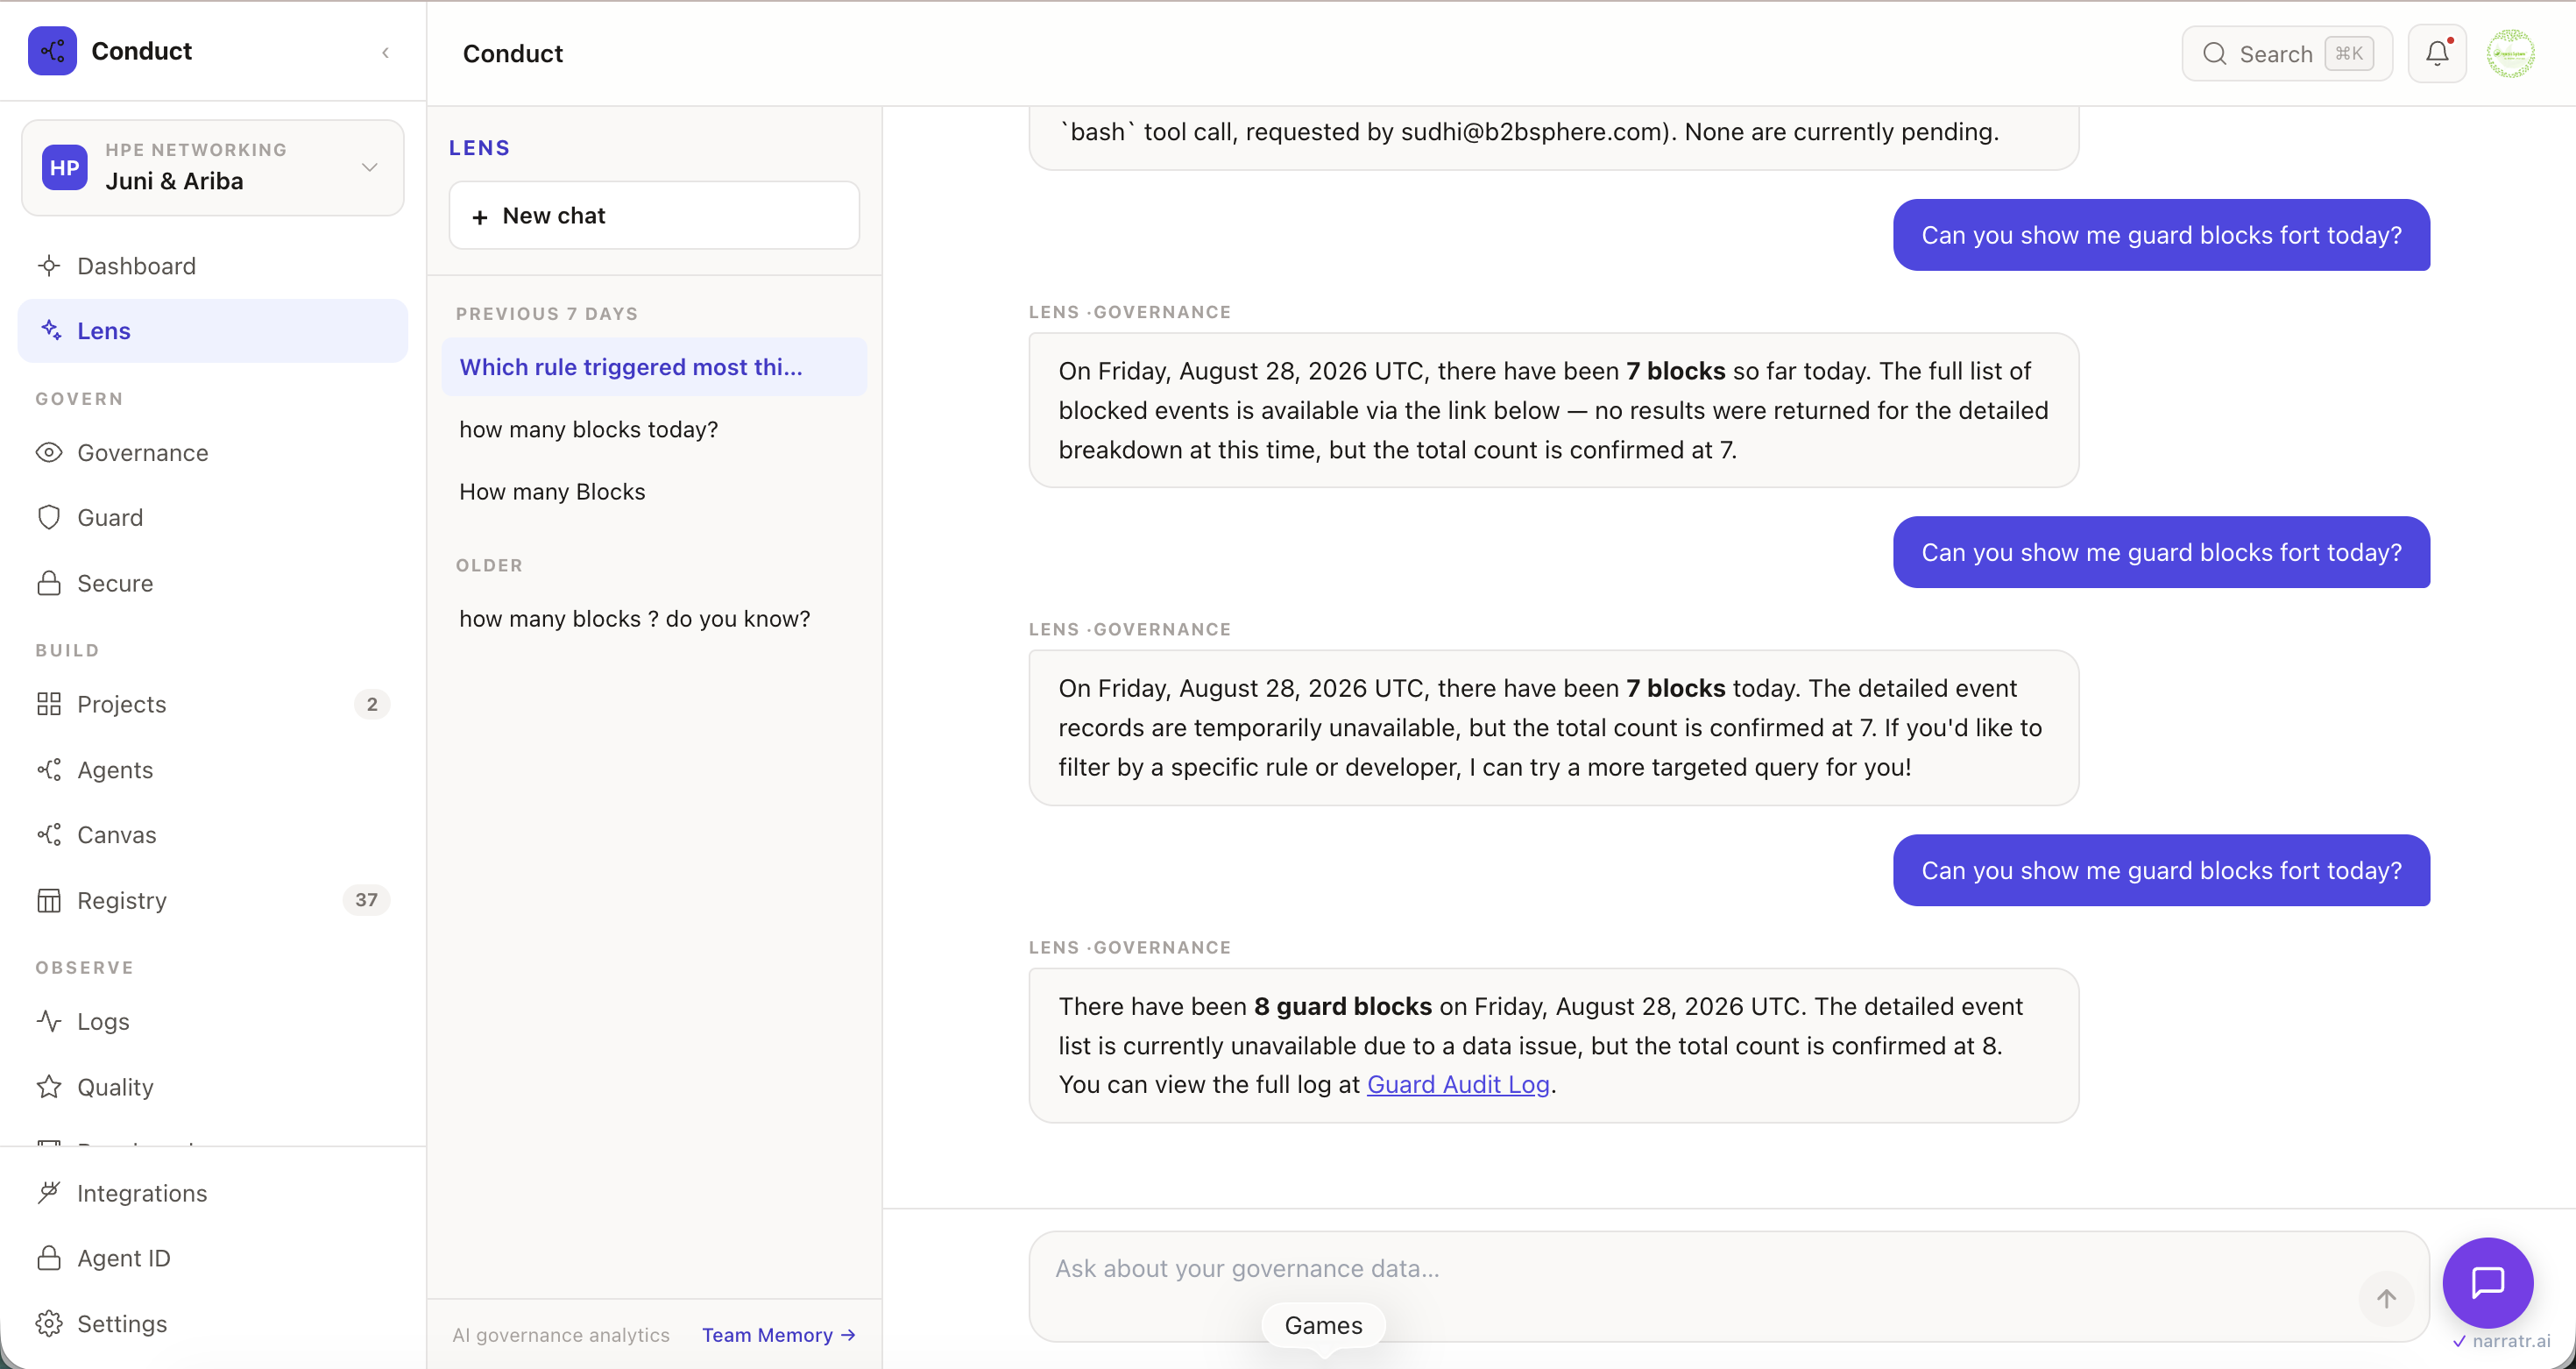
Lens is the chat surface for the whole platform. One input covers Guard activity, workflow state, compliance status, agent spend. Answers come from your workspace data, not a general model. Ask "who got blocked today" and get a table with per-row drilldown links. Lens itself runs through Guard, so the assistant is bound by the same rules as the agents it reports on.
Runtime firewalls like Straiker and Lakera tell you what an agent did. Conduct decides what it can do.
| Runtime firewalls | Conduct Guard | |
|---|---|---|
| Timing | After the action | Before the action |
| Config integrity | Trust the pack | Workspace-signed |
| Audit | Log stream | SHA-256 hash chain |
| Coverage | LLM calls only | LLM, shell, MCP |
| Failure mode | Fail-open | Fail-closed |
Three properties make the audit trail hold up in a room with an auditor:
Discovery mode is read-only visibility into every AI action your team takes for 14 days. No policy to author, no upstream install, no cost. When you see something worth blocking, promote a rule from what Discovery already saw.
curl https://gateway.conductai.ai/gateway/v1/anthropic/v1/messages \
  -H "Authorization: Bearer cond_agt_..." \
  -H "Content-Type: application/json" \
  -d '{"model":"claude-sonnet-4-6","max_tokens":1024,"messages":[{"role":"user","content":"Hello"}]}'
Every request runs through Guard (policy, budget, audit) before it reaches the upstream provider. Works with any SDK that speaks the provider's HTTP API.
| Component | Path |
|---|---|
| Guard runtime | apps/api/app/modules/guard/ |
| Router (proxy) | apps/api/app/modules/guard/routers/proxy.py |
| Compliance packs | apps/api/app/modules/guard/skill_packs/ |
| Canvas UI | apps/web/ |
| Playbook DSL loader | apps/api/app/dsl/ |
| Playbook library | apps/api/playbooks/ (35 pre-built) |
| CLI | packages/conduct-cli/ |
15 compliance packs out of the box: OWASP, SOC 2 CC7.3, HIPAA §164.312, PCI DSS 4.0, EU AI Act Art. 15/16, NIST AI RMF, ISO 42001, plus Python, Node, and Terraform.
35 pre-built playbooks: issue-to-PR, code review, incident response, prod deploy gate, CI/CD triage, security scanner triage, Slack digest. One YAML file each. Edit and run.

