Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Guide-and-theoretical-code-for-CVE-2023-35674 — Guide and theoretical code for CVE-2023-35674 | Kitploit
Tools/GitHubGitHub/spiralbl0ck/guide-and-theoretical-code-for-cve-2023-35674
Android SecurityPrivilege EscalationVulnerability AnalysisExploitationMobile SecurityLearning & EducationBinary Exploitation
GitHub
Share
spiralbl0ck/guide-and-theoretical-code-for-cve-2023-35674

Guide-and-theoretical-code-for-CVE-2023-35674

Guide and theoretical code for CVE-2023-35674

View Repository
22672 years agoNot yet reviewed

Guide-and-theoretical-code-for-CVE-2023-35674

Guide and theoretical code for CVE-2023-35674

Because android is out of my skill league please use this as a high overview from my pov on how i would exploit this cve. the code snippets are just skeletons , please help :) So first of all u can't exploit soley the CVE-2023-35674. Why ? cause CVE-2023-35674 only allows you to launch a background activity due to a logic error. So in essence you would use this cve to launch an app in the background , and use something like CVE-2021-0307 to privillege escalation. A word of advice the only way you can fully exploit these 2 vulnerability(so in essence use the chain) is only if you android is android 11.

So now for CVE-2023-35674. The root cause is essence that virtual presentation were tought that they can only be shown on private virtual displays and that shouldn't be the cause of an app be considered foreground. So i included Presentation.java the code from google docs to start a virtual presentation and inside of it start an instart of a class(which should be replaced with a way to start an app). This will by default start the app in the background.[1]

Now onto the eop part... For CVE-2021-0307 i used this(https://blog.thalium.re/posts/leveraging-android-permissions/) as a reference.... So what more presicly? this

poc

So naturally i tought coding a skeleton cause again android is out of my league and i'm lazy. Such MainActivity.java was born. Now with a little bit of better understanding i think the exploit flow should be a little bit different. How ?

Well for the start app in background [1] should still be respected. Yet for eop it should be something among the image below
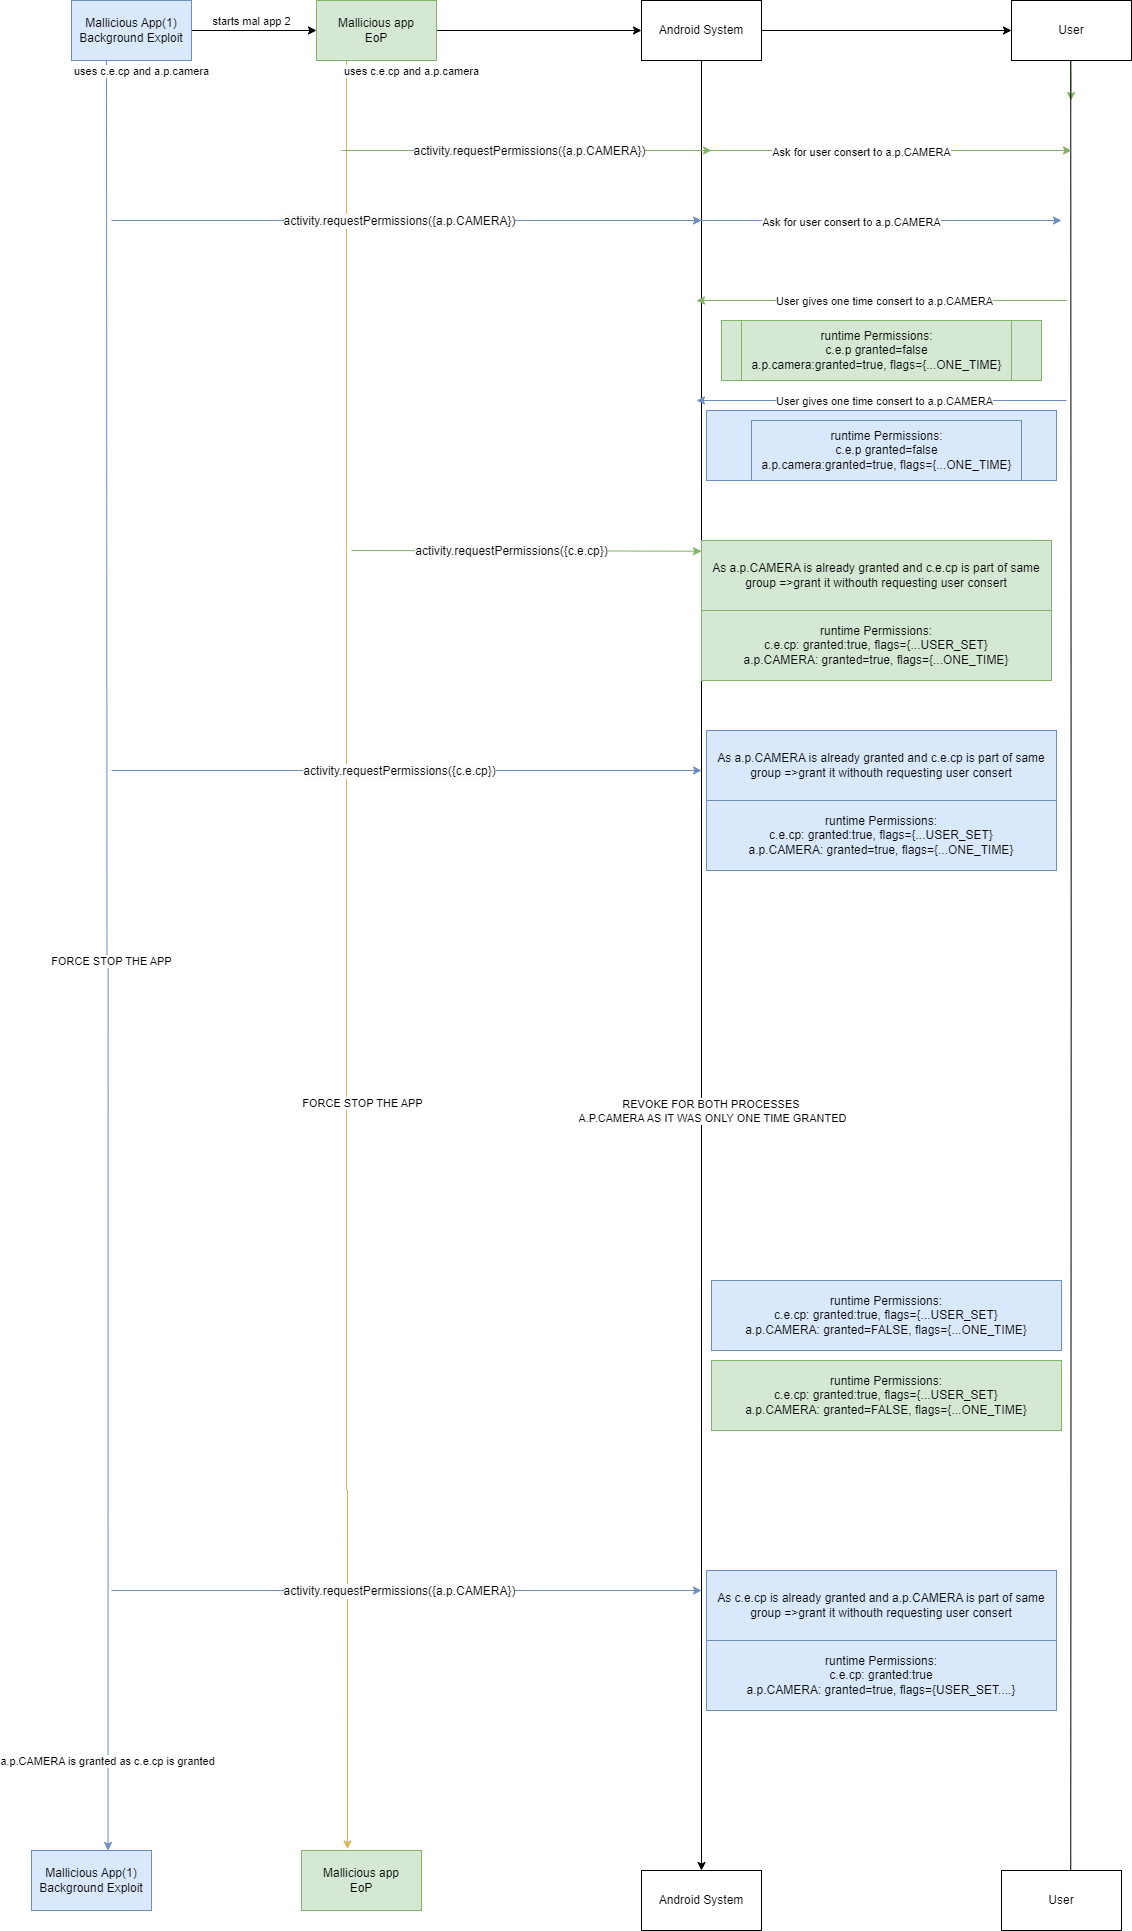
exploit

As you can see the exploit flow is identical only that instead of finishing the exploit like the eop one we finish with the app we started the exploit in background.

So generally speaking i think i described 2 ways of getting eop, tho i think only for CVE-2023-35674 u can only get to execute code in the background . But digressing i think there are 2 ways to exploit this CVE-2023-35674:

  1. by having an apk execute in background which is the first part where u use CVE-2023-35674 for background execution and further execute CVE-2021-0307
  2. the approach which u elevate the apk of CVE-2023-35674 yet with user interaction which was described earlier so yeah :/

Please take everything i write here with a grain of salt, until further notice(until i find someone to collab on this who knows android exploitation....)

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    911
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    548
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    366
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    362
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    311
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    287

Explore all tools

Browse our collection of tools

View all tools →






