

iblessing is an iOS security exploiting toolkit, it mainly includes application information gathering, static analysis and dynamic analysis. It can be used for reverse engineering, binary analysis and vulnerability mining.
☠️ ██╗██████╗ ██╗ ███████╗███████╗███████╗██╗███╗ ██╗ ██████╗ ██║██╔══██╗██║ ██╔════╝██╔════╝██╔════╝██║████╗ ██║██╔════╝ ██║██████╔╝██║ █████╗ ███████╗███████╗██║██╔██╗ ██║██║ ███╗ ██║██╔══██╗██║ ██╔══╝ ╚════██║╚════██║██║██║╚██╗██║██║ ██║ ██║██████╔╝███████╗███████╗███████║███████║██║██║ ╚████║╚██████╔╝ ╚═╝╚═════╝ ╚══════╝╚══════╝╚══════╝╚══════╝╚═╝╚═╝ ╚═══╝ ╚═════╝

iblessing is an iOS security exploiting toolkit, it mainly includes application information gathering, static analysis and dynamic analysis.iblessing is based on unicorn engine, capstone engine and keystone engine.🔥 Cross-platform: Tested on macOS and Ubuntu.
iOS App static info extract, including metadata, deeplinks, urls, etc.
Mach-O parser and dyld symbol bind simulator
Objective-C class realizing and parsing
Scanners making dynamic analysis for arm64 assembly code and find key information or attack surface
Scanners using unicorn to partially simulate Mach-O arm64 code execution and find some features
Generators that can provide secondary processing on scanner's report to start a query server, or generate script for IDA
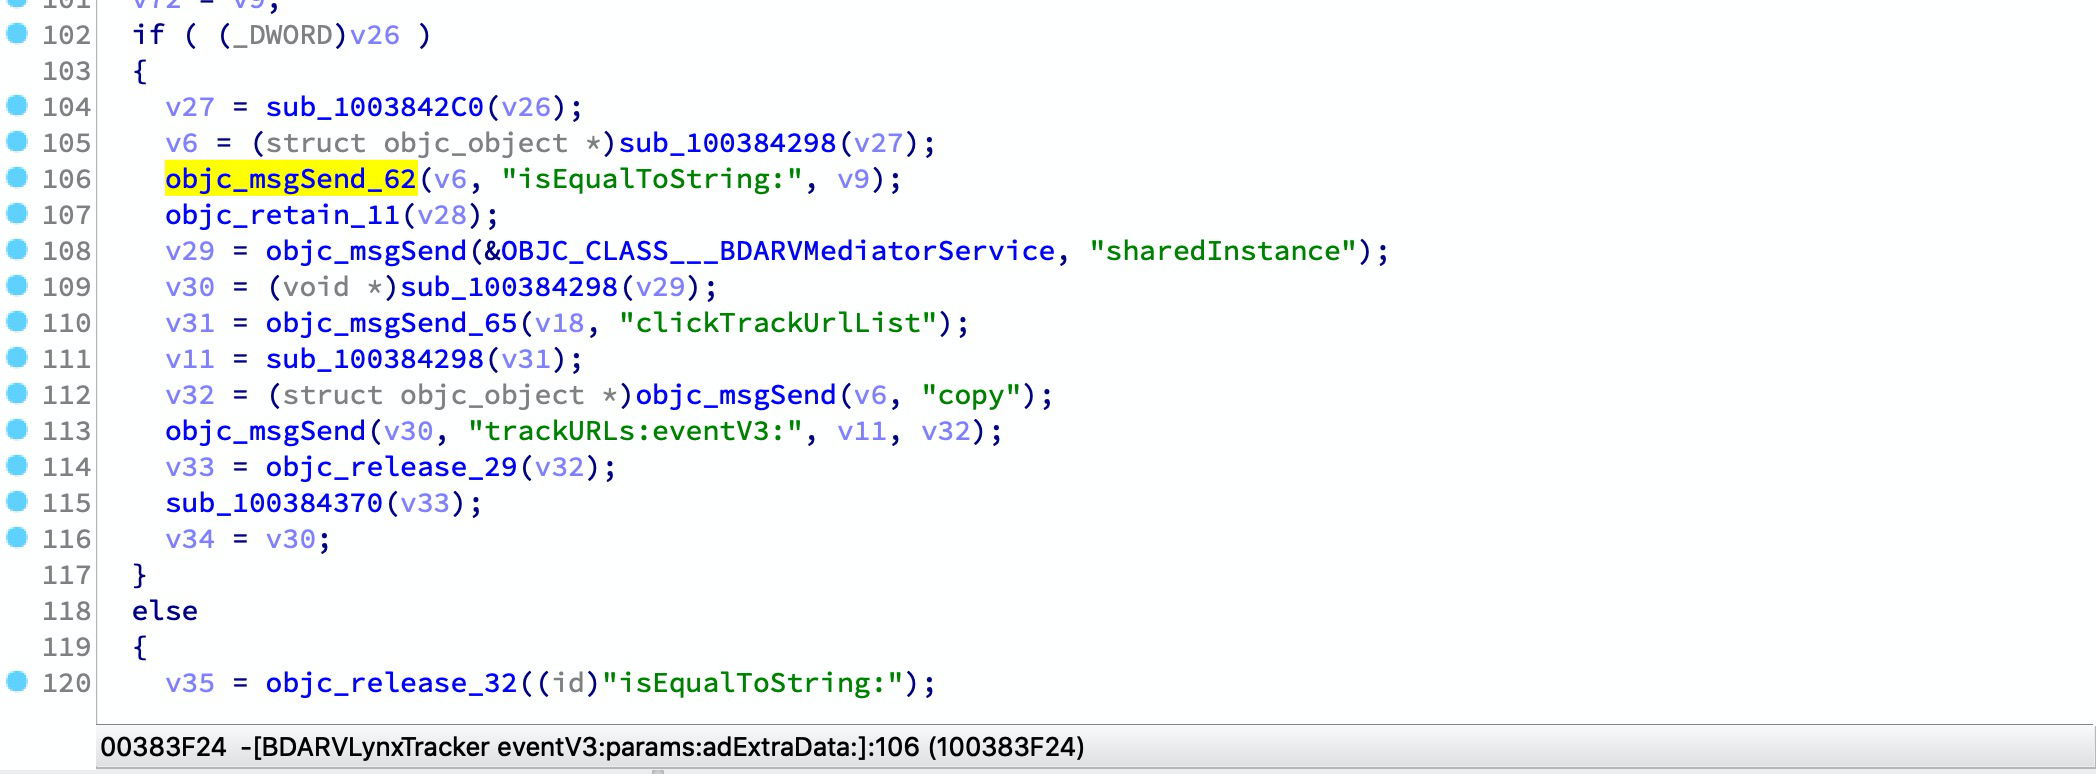
Super objc_msgSend xrefs scanner 😄
Tests
Android Scanners Suport
Diagnostic logs
More flexible scanner infrastructure for new scanner plugins
In case you need support regarding iblessing or anything associated with it, you can:
⚠️⚠️⚠️ Binary Scanners require 12GB of virtual memory space to loading a mach-o file, but won't consume so much. So you need to ensure that the physical memory of your working machine is greater than 12GB, or ensure that allocatable virtual memory is greater than 12GB through the swap file mechanism.
To get started compiling iblessing, please follow the steps below:
git clone --recursive -j4 https://github.com/Soulghost/iblessing
cd iblessing
./compile-cmake.sh
Scanners
Generators
If there are any errors, you can manully compile capstone and unicorn, then drag libcapstone.a and libunicorn.a to the Xcode project's vendor/libs.
If all of this run successfully, you can find the binary in build directory:
> ls ./build
iblessing

> file ./build/iblessing
./build/iblessing: Mach-O 64-bit executable x86_64
$ iblessing -h

           ☠️
           ██╗██████╗ ██╗     ███████╗███████╗███████╗██╗███╗   ██╗ ██████╗
           ██║██╔══██╗██║     ██╔════╝██╔════╝██╔════╝██║████╗  ██║██╔════╝
           ██║██████╔╝██║     █████╗  ███████╗███████╗██║██╔██╗ ██║██║  ███╗
           ██║██╔══██╗██║     ██╔══╝  ╚════██║╚════██║██║██║╚██╗██║██║   ██║
           ██║██████╔╝███████╗███████╗███████║███████║██║██║ ╚████║╚██████╔╝
           ╚═╝╚═════╝ ╚══════╝╚══════╝╚══════╝╚══════╝╚═╝╚═╝  ╚═══╝ ╚═════╝

[***] iblessing iOS Security Exploiting Toolkit Beta 0.1.1 (http://blog.asm.im)
[***] Author: Soulghost (高级页面仔) @ (https://github.com/Soulghost)

Usage: iblessing [options...]
Options:
    -m, --mode             mode selection:
                                * scan: use scanner
                                * generator: use generator
    -i, --identifier       choose module by identifier:
                                * <scanner-id>: use specific scanner
                                * <generator-id>: use specific generator
    -f, --file             input file path
    -o, --output           output file path
    -l, --list             list available scanners
    -d, --data             extra data
    -h, --help             Shows this page
A scanner is a component used to output analysis report through static and dynamic analysis of binary files, for example, the objc-msg-xref scanner can dynamiclly analyze most objc_msgSend cross references.

