
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
damn-vulnerable-log4j-app — Vulnerable web application to test CVE-2021-44228 / log4shell and forensic artifacts from an example attack | Kitploit
Tools/GitHubGitHub/snapattack/damn-vulnerable-log4j-app
Vulnerability AnalysisExploitationWeb Application ExploitationForensicsDigital ForensicsLearning & Education
GitHubsnapattack/damn-vulnerable-log4j-app

damn-vulnerable-log4j-app

Vulnerable web application to test CVE-2021-44228 / log4shell and forensic artifacts from an example attack

View Repository
52134 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

SnapAttack Log4j / CVE-2021-44228 / log4shell Resources

What's included?

Damn Vulnerable Log4j App

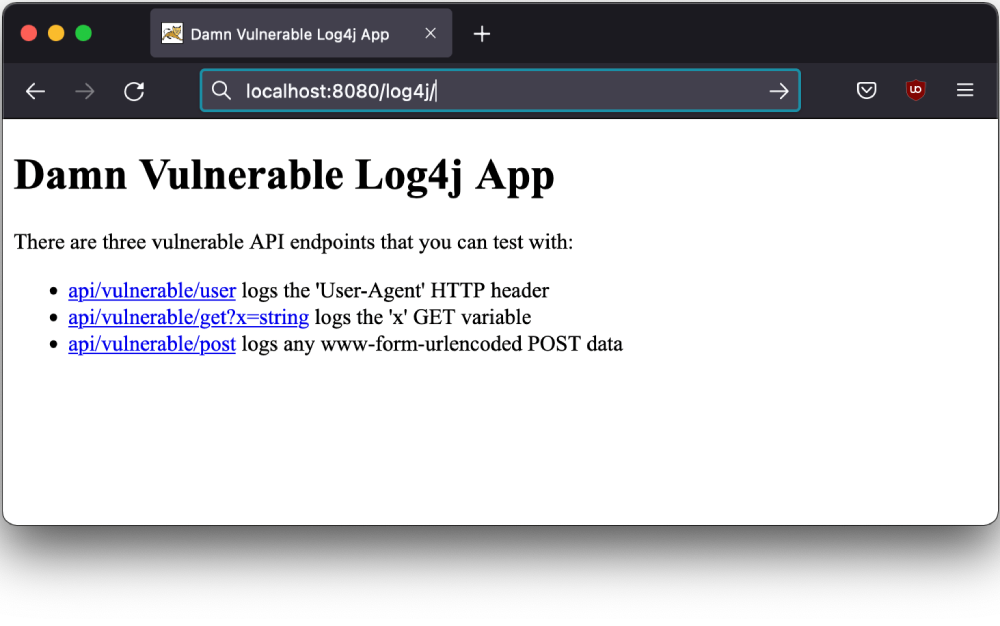
damn-vulnerable-log4j-app contains a basic vulnerable Java Servlet that logs the User Agent, HTTP GET and POST parameters with log4j. It is packaged as a .war file and can be deployed to servers like Tomcat. See the README for more information.
Attack Artifacts

attack-artifacts contains example EDR, system, and application logs, as well as a PCAP and Zeek logs from an attack against a Windows victim machine. You can see the attack in our video at https://www.youtube.com/watch?v=X7cLgDoX6KU. In the future, content like this will be freely available in the community edition of SnapAttack. If you're interested, you can request an invite.

Artifacts

License

All resources in this repository are provided under the MIT License.

Download Tool