
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
gowitness — 🔍 gowitness - a golang, web screenshot utility using Chrome Headless | Kitploit

Tools/GitHubGitHub/sensepost/gowitness
ReconnaissanceInformation GatheringWeb SecurityCrawlerTop in Crawler #11Top in Information Gathering #20Top in Reconnaissance #19
GitHubsensepost/gowitness

gowitness

🔍 gowitness - a golang, web screenshot utility using Chrome Headless

4.5k4431641 month agoReviewed by Kitploit
Share
View Repository


gowitness

A golang, web screenshot utility using Chrome Headless.

@leonjza Go Report Card Docker build & Push


introduction

gowitness is a website screenshot utility written in Golang, that uses Chrome Headless to generate screenshots of web interfaces using the command line, with a handy report viewer to process results. Both Linux and macOS is supported, with Windows support mostly working.

features

The main goal of gowitness is to take website screenshots (and do that well!), while optionally saving any information it gathered along the way. That said, a short list of features include:

  • Take website screenshots, obviously..., but fast and accurate!
  • Scan a list of URLs, CIDRs, Nmap Results, Nessus Results and more.
  • Ability to grab and save data (i.e., a request log, console logs, headers, cookies, etc.)
  • Write data to many formats (sqlite database, jsonlines, csv, etc.)
  • An epic web-based results viewer (if you saved data to SQLite) including a fully featured API!
  • And many, many more!

quick start

There are a few ways to get gowitness, the simplest (assuming your $GOBIN path is in your shell $PATH) will be to use go install:

go install github.com/sensepost/gowitness@latest

Otherwise, grab a platform specific release binary or compile from source. Then, scan your first target writing the results to a SQLite database and the screenshot to ./screenshots with:

gowitness scan single --url "https://sensepost.com" --write-db

There are many, many flags and scan types in gowitness. Just add -h anywhere and read all about it!

documentation

For advanced installation information and other documentation, please refer to the wiki here.
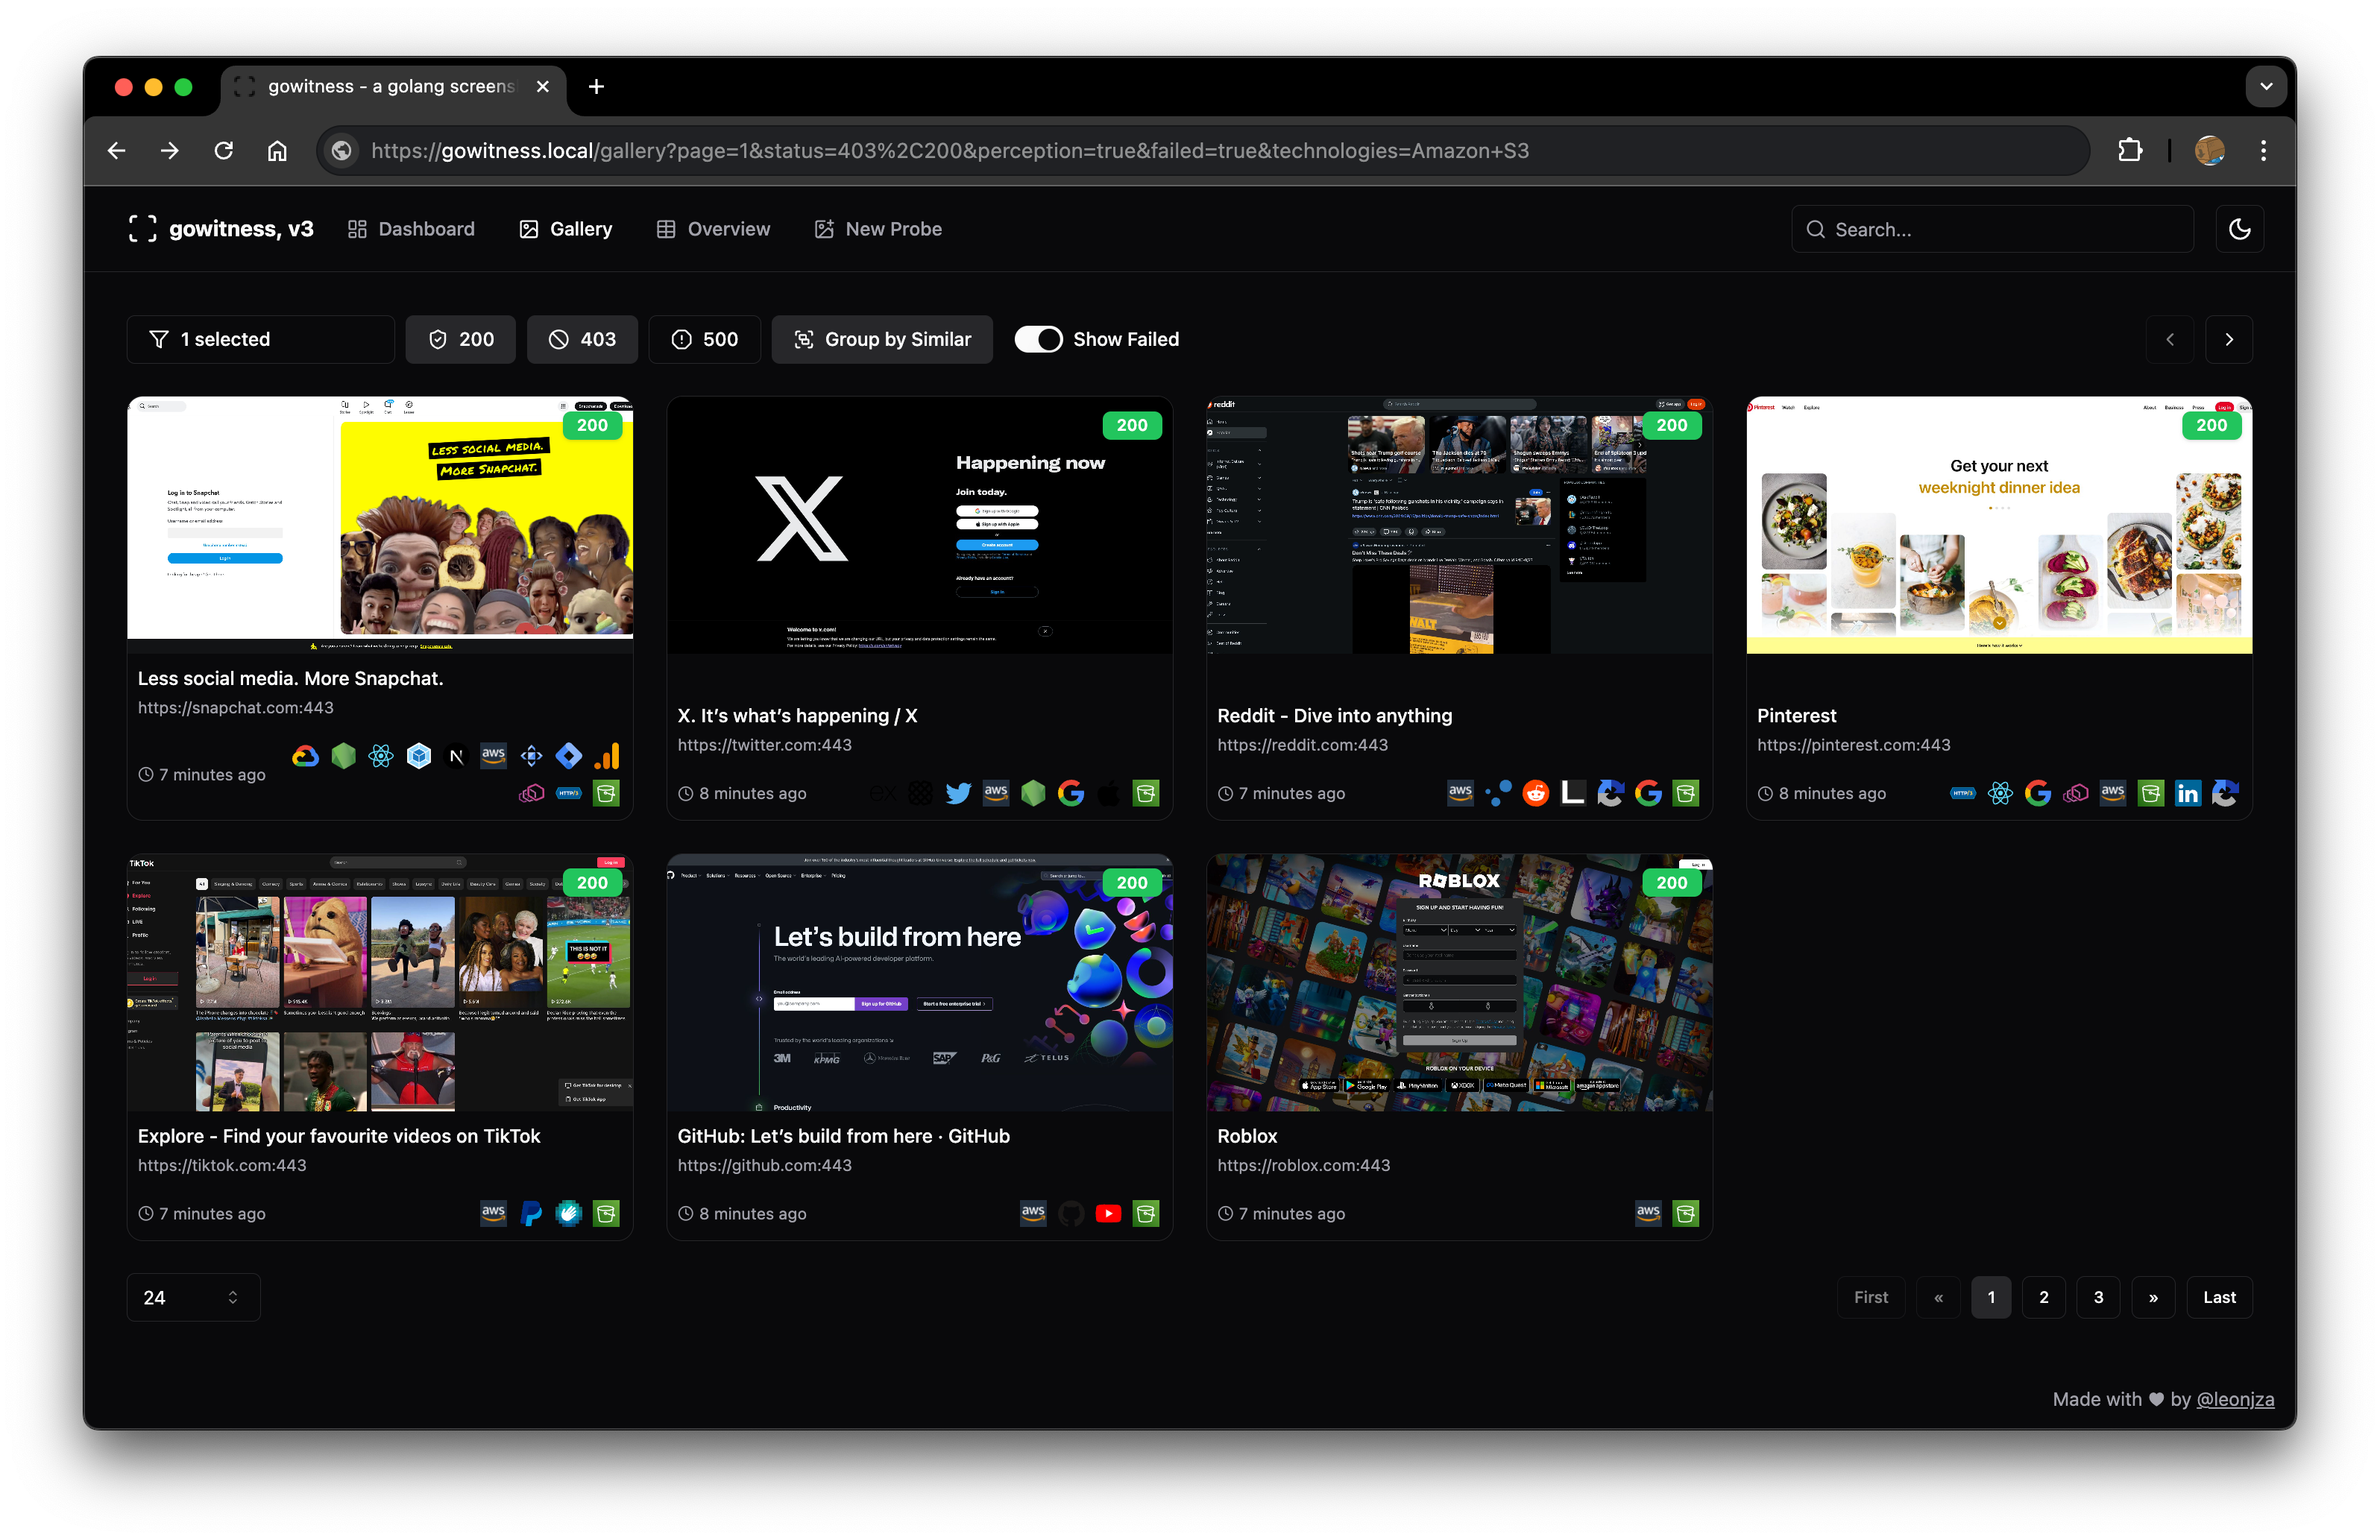
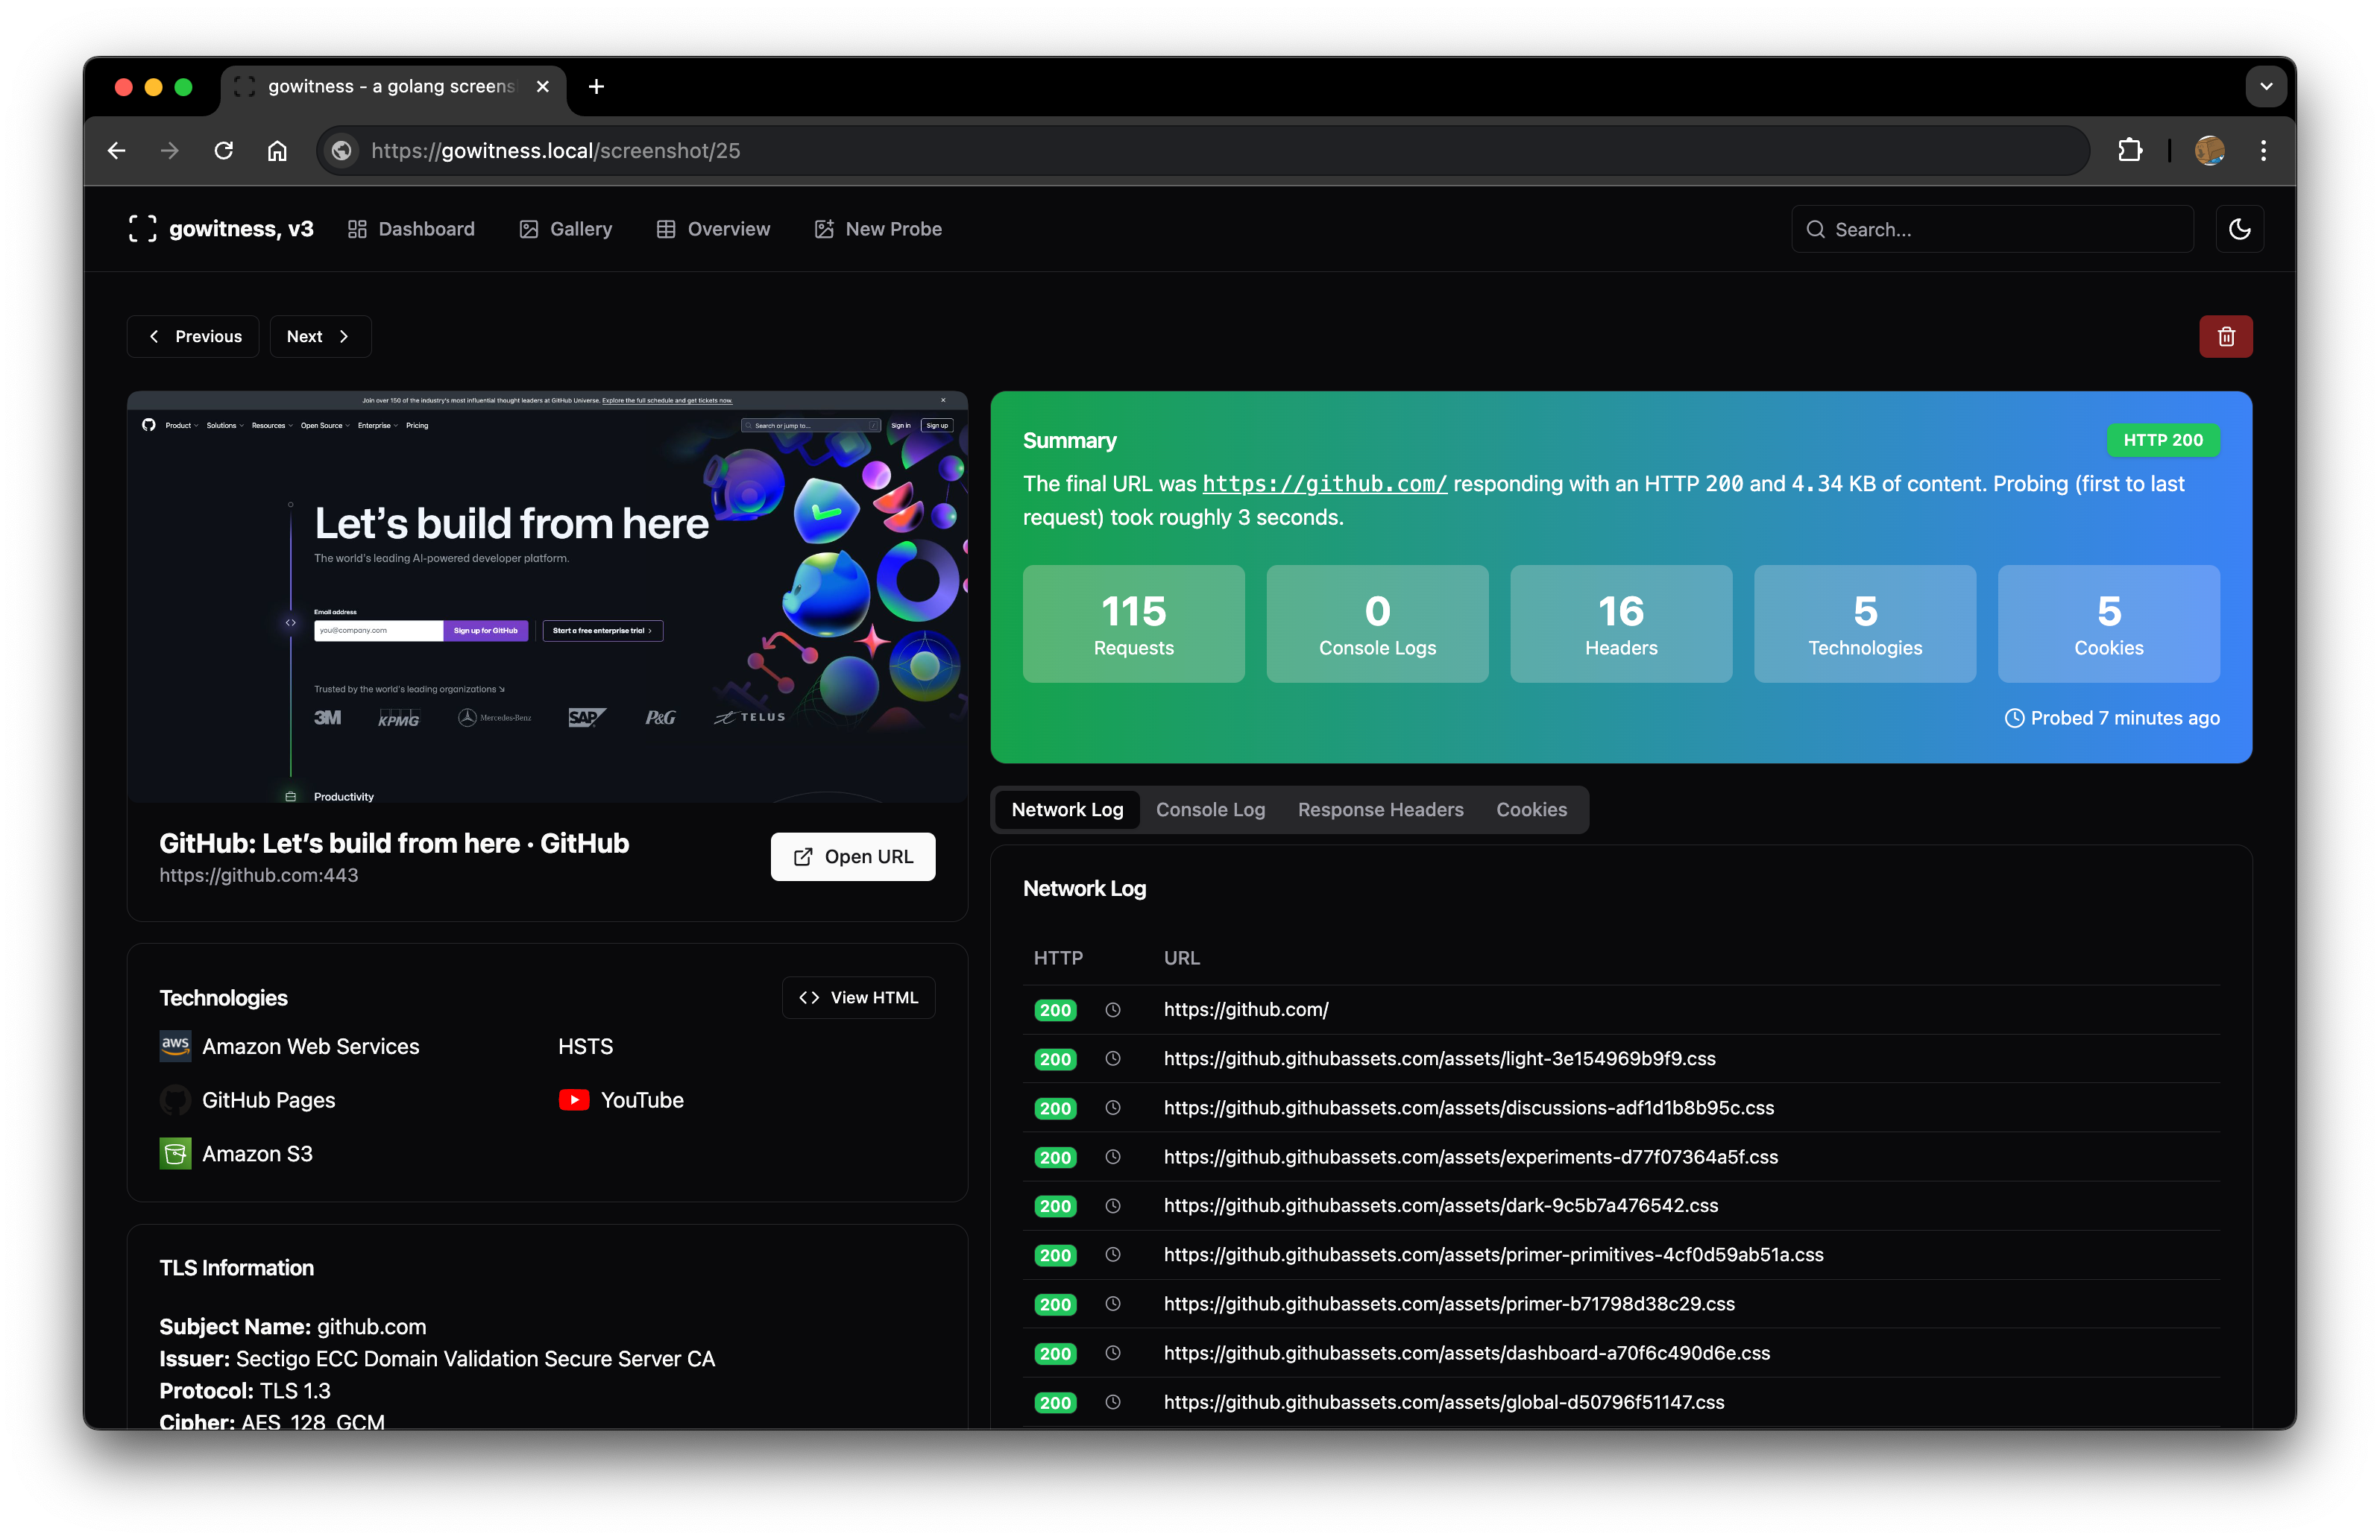
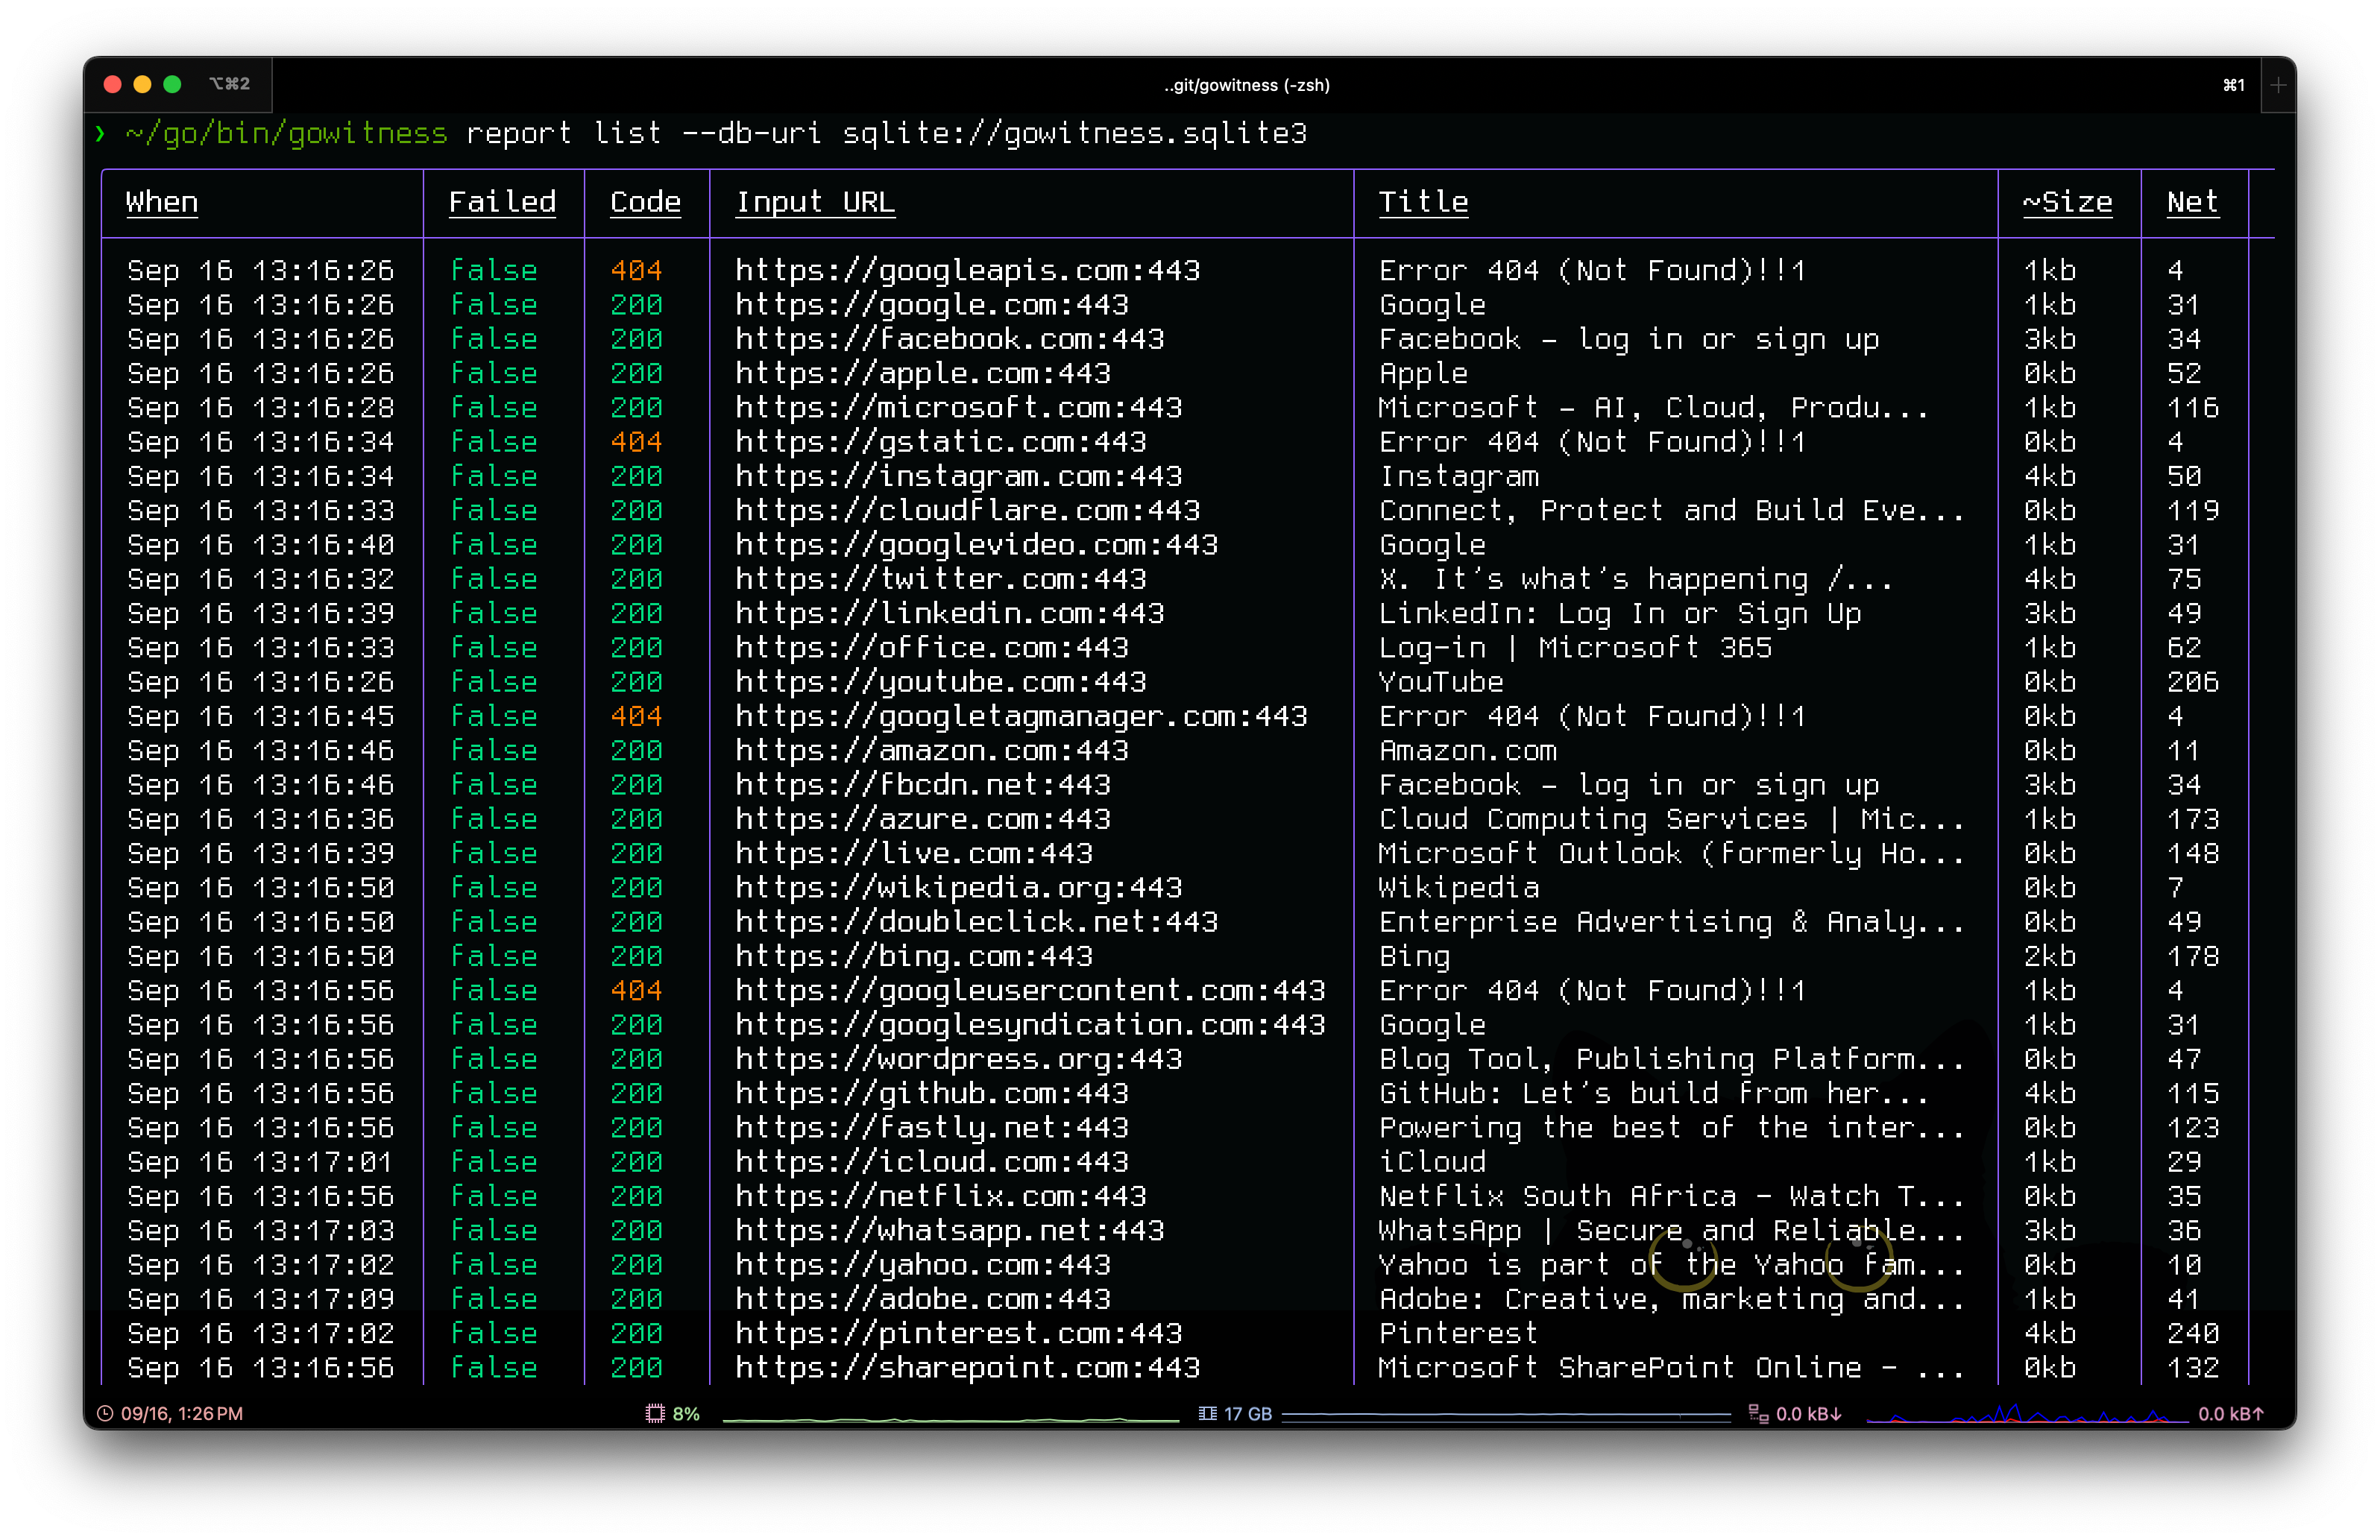
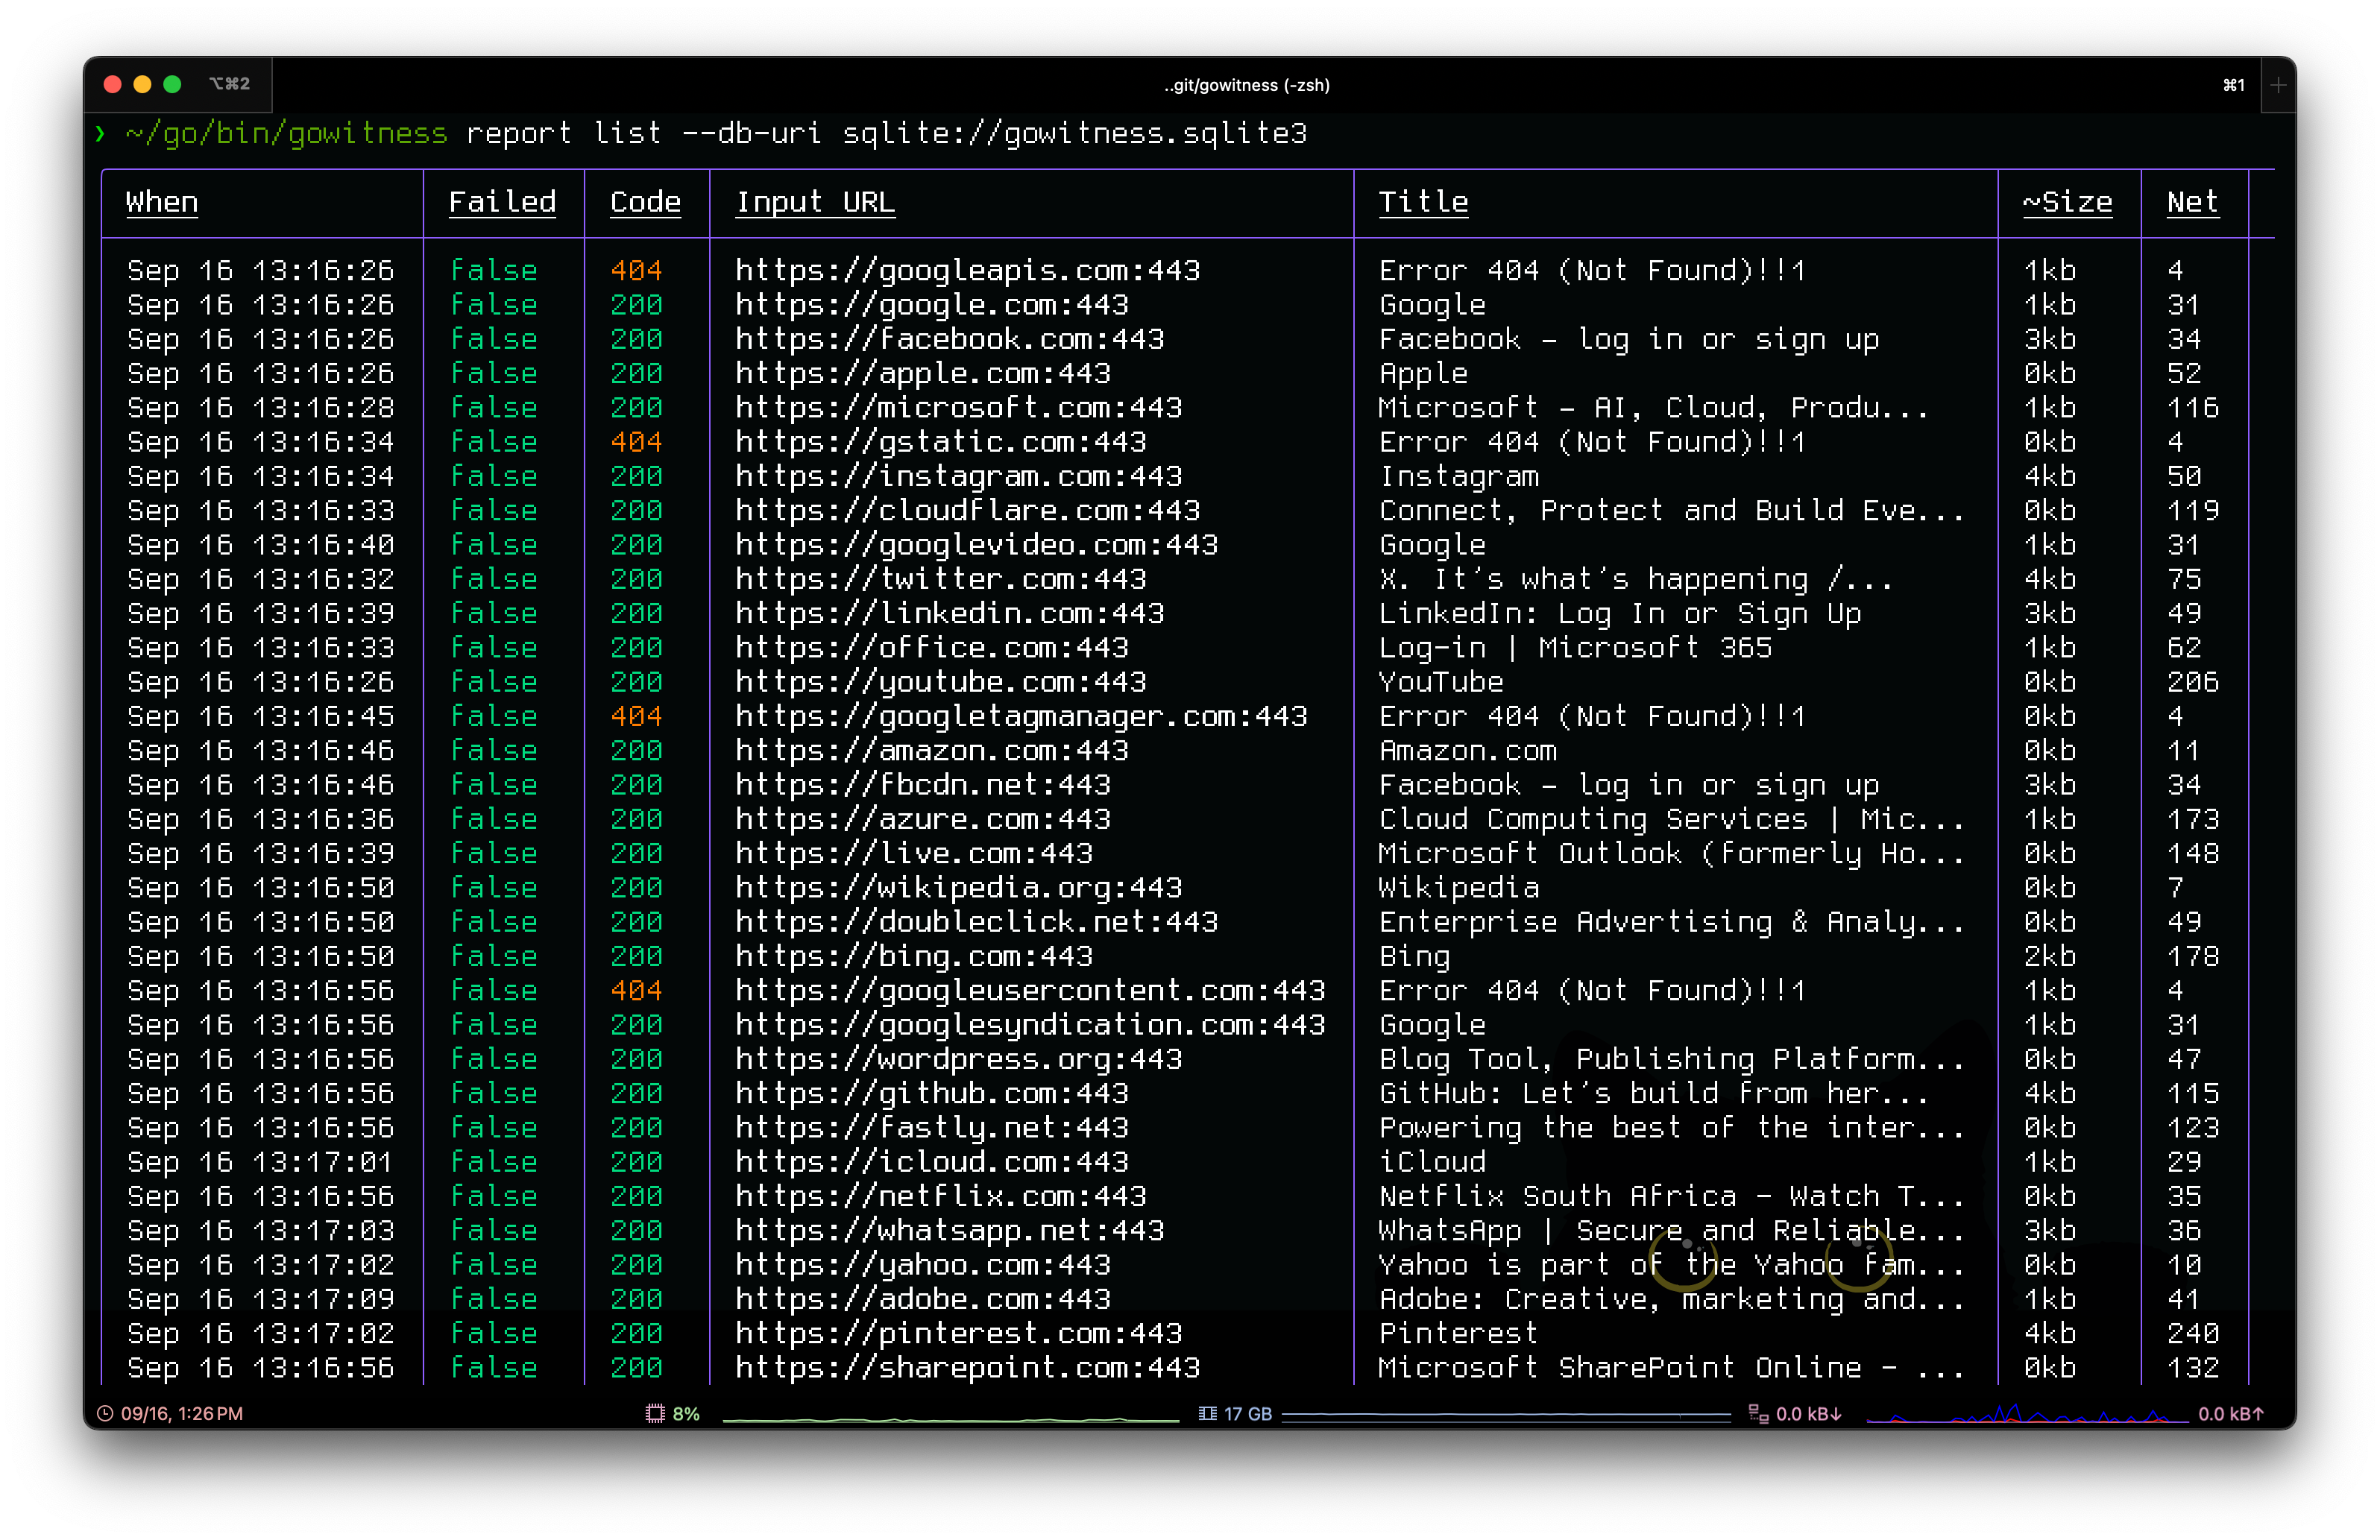
screenshots

gallery

detail

terminal

credits

gowitness would not have been possible without some of these amazing projects: chi, chromedp, go-rod, cobra, gorm, glamour, go-nmap, wappalyzergo, goimagehash.

license

gowitness is licensed under a GNU General Public v3 License. Permissions beyond the scope of this license may be available at http://sensepost.com/contact/.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    891
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    547
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    369
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    366
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    309
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    282

Explore all tools

Browse our collection of tools

View all tools →