FlatPress CMS Stored XSS in v1.3.1
CVE-2025-25460
Author: Athul S
Description
A stored Cross-Site Scripting (XSS) vulnerability was identified in FlatPress 1.3.1 within the "Add Entry" feature. This vulnerability allows authenticated attackers to inject malicious JavaScript payloads into blog posts, which execute when other users view the posts. The issue arises due to improper input sanitization of the "TextArea" field in the blog entry submission form.
Attack Vectors
- An authenticated attacker can inject a malicious JavaScript payload into the blog post entry.
- The payload executes when an admin or another user visits the affected blog entry.
- This could lead to session hijacking, phishing, or other client-side attacks.
Proof of Concept (PoC)
Steps to Reproduce:
-
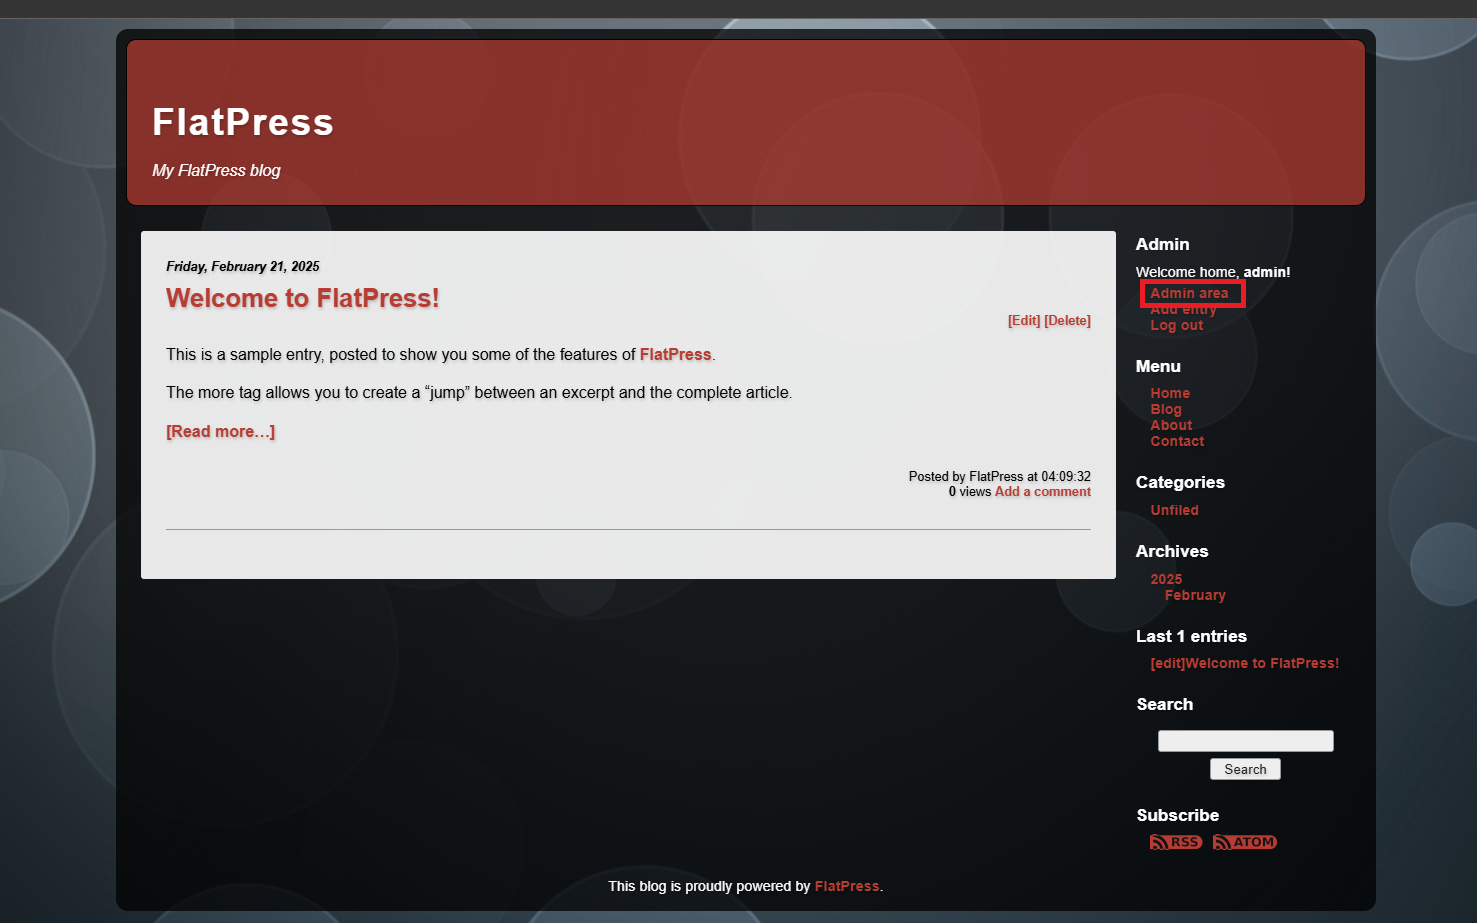
Login as an Admin in FlatPress v1.3.1.
-
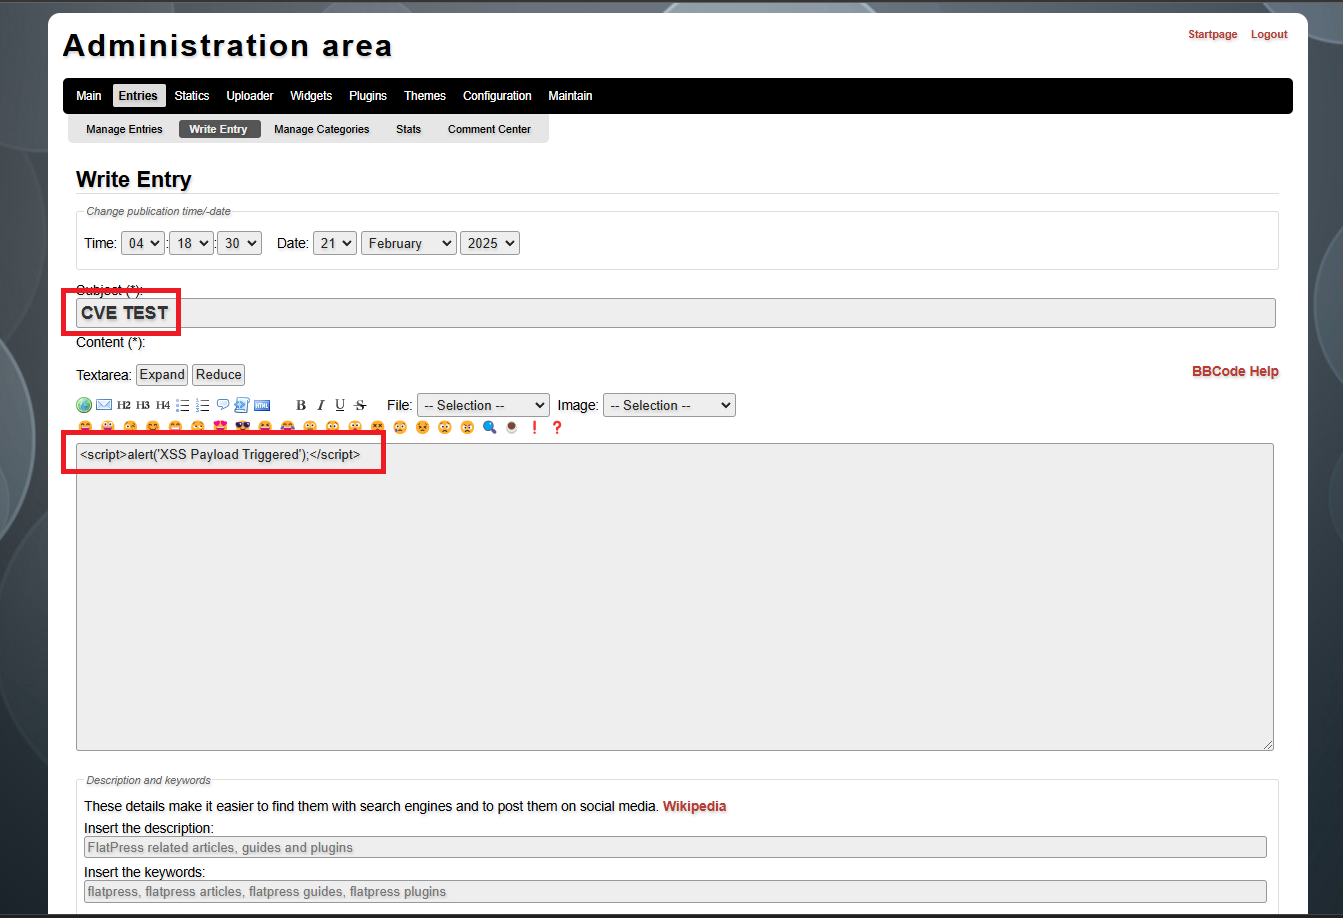
Navigate to the "Add Entry" section.
-
Insert the following XSS payload in the text area:
<script>alert('XSS Payload Triggered');</script>
-
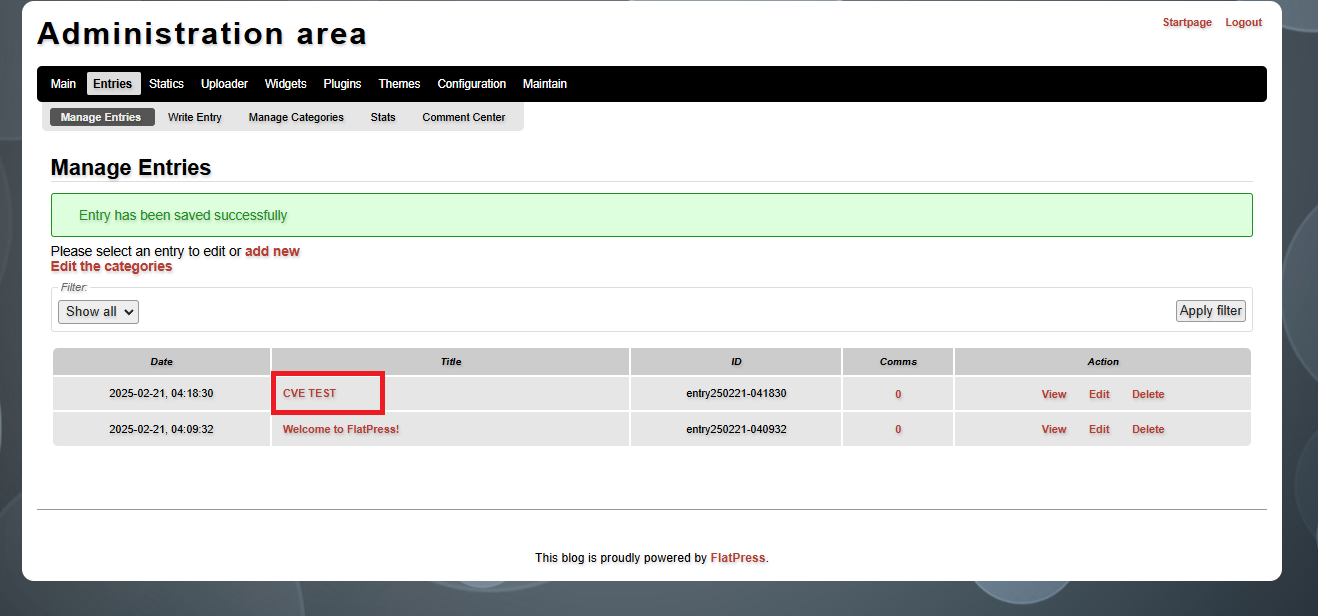
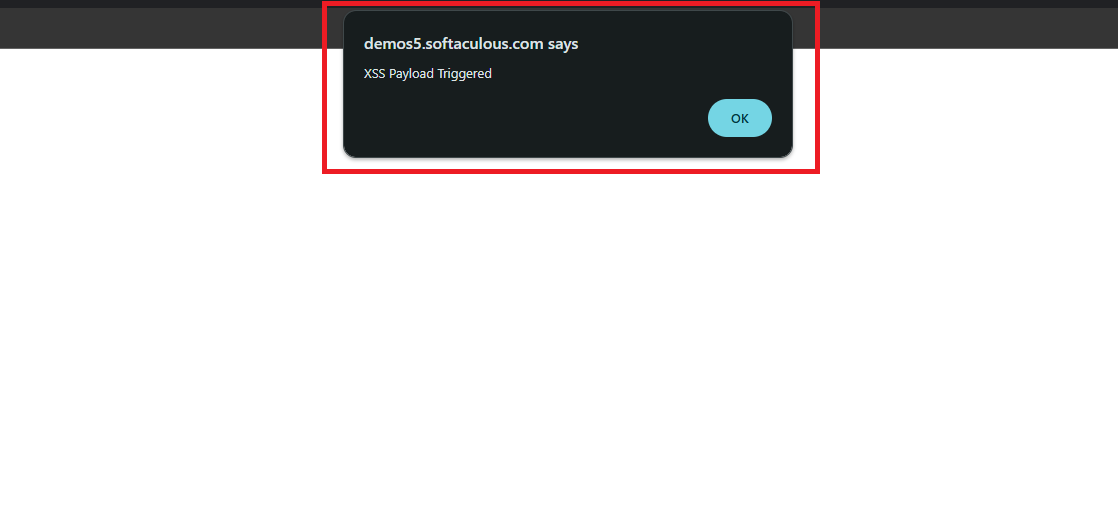
Save the Entry and View the Post
The JavaScript payload will execute when the page loads, triggering an XSS alert box.

Impact
- Code Execution: ✅ (JavaScript execution in the victim's browser)
- Potential Exploits:
- Session Hijacking (stealing admin cookies).
- Phishing Attacks (redirecting users to malicious sites).
- Defacement (injecting unwanted content into the page).
Affected Product
- Product: FlatPress
- Version: 1.3.1
- Component: Add Entry Feature (TextArea Field)
Mitigation
- Sanitize user inputs before rendering.
- Implement Content Security Policy (CSP) to block inline scripts.
- Update to FlatPress 1.4-dev, where the issue is patched.
- Contacted via email:
- Vendor confirmed the issue on January 12, 2025.
- The vulnerability is being patched in the FlatPress 1.4-dev branch.
References
Discoverer
Athul S
 ronixxcybsec0101/cve-2025-25460

