 reewardius/cve-2022-32074
Proof-of-concept exploit for CVE-2022-32074 demonstrating stored XSS in osTicket via malicious SVG file upload in the file listing directory.

1. Find the file listing directory, the root of the file download directoryм (file_uploads (this is an example)).
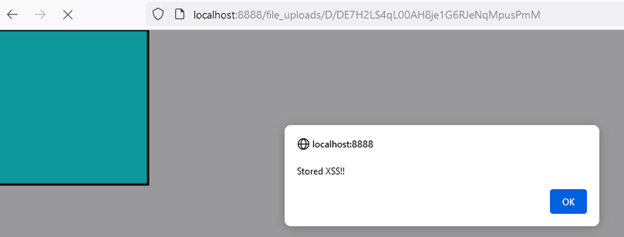
2. Load the following xssPayload.svg and open it
Example: