
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/r4ulcl/wifi_db
Password CrackingWi-Fi AuditingForensicsInformation GatheringWireless Security
GitHubr4ulcl/wifi_db

wifi_db

Script to parse Aircrack-ng captures into a SQLite database and extract useful information like handshakes, MGT identities, interesting relations between APs, clients and it's Probes, WPS information and a global view of all the APs seen.

View Repository
13811236 days agoReviewed by Kitploit

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

wifi_db

Latest release License Last commit (master) Last commit (dev) Top language

Docker Image build Docker Image (dev) build CodeFactor Lines of code Docker image size

Stars Forks Open issues Contributors Docker pulls

wifi_db

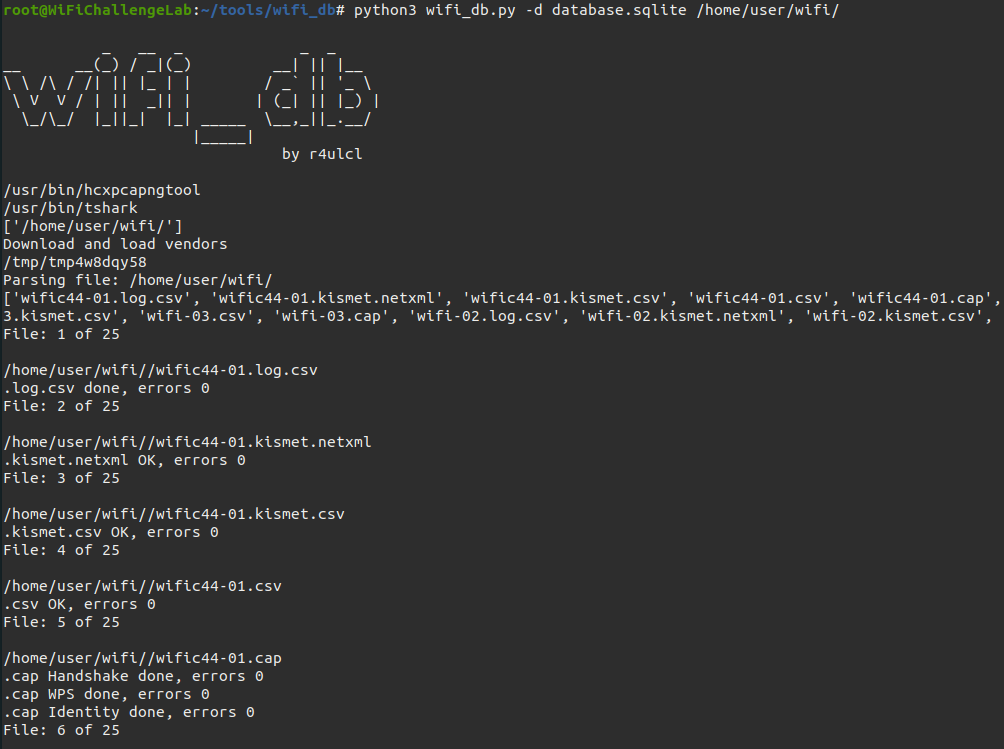
Script to parse Aircrack-ng captures into a SQLite database and extract useful information like handshakes (in 22000 hashcat format), enterprise (MGT) identities and EAP-MD5 challenge/response pairs, the X.509 certificates and RSN/WPA security configuration of each network, the 802.11r/k/v, Multiple BSSID and Channel Switch capabilities advertised by the APs, interesting relations between APs, clients and their Probes, WPS information, and a global view of all the APs seen.
Table of Contents

  • Features
  • Install
  • Usage
  • Database
  • Views
  • TODO
  • License

Features

  • Displays if a network is cloaked (hidden) even if you have the ESSID.
  • Shows a detailed table of connected clients and their respective APs.
  • Identifies client probes connected to APs, providing insight into potential security risks using Rogue APs.
  • Extracts handshakes for use with hashcat, facilitating password cracking.
  • Displays identity information from enterprise networks, including the EAP method used for authentication.
  • Extracts the X.509 certificates exchanged in enterprise (802.1X) EAP-TLS/PEAP/TTLS authentications (both AP/server and client certificates), storing all certificate fields per AP BSSID in the Certificate table.
  • Breaks down the RSN/WPA security of each AP (WPA version, AKM suites, pairwise/group ciphers, enterprise flag, and management-frame protection) from beacons into the AP table.
  • Captures EAP-MD5 challenge/response pairs for offline cracking (hashcat -m 4800) into the EAPMD5 table.
  • Detects randomized (locally administered) client MAC addresses and fingerprints clients by their probe-request information elements (stored on the Probe table).
  • Generates a summary (SummaryAP view) of the APs grouped by ESSID and encryption, showing the AP and client counts, the WPA version and PMF state, and every manufacturer per group, to give a quick overview of the security status of nearby networks (and to spot SSIDs running mixed/downgraded security).
  • Records the Wi-Fi Protected Setup (WPS) configuration of each AP directly on its AP row.
  • Logs all instances when a client or AP has been seen with the GPS data and timestamp, enabling location-based analysis.
  • Upload files with capture folder or file. This option supports the use of wildcards (*) to select multiple files or folders.
  • Docker version in Docker Hub to avoid dependencies.
  • Obfuscated mode for demonstrations and conferences.
  • Possibility to add static GPS data.
  • Reports the Management Frame Protection (802.11w / PMF) status of each AP: the mfpc (capable) and mfpr (required) flags read bitwise from the RSN capabilities, and the derived pmf state (Required, Capable when it is optional, or Disabled), stored on the AP table.
  • Detects fast-roaming and management support advertised by each AP: 802.11r Fast BSS Transition (ft_80211r, with the mobility_domain_id), 802.11k Radio Resource Measurement / neighbor reports (rrm_80211k), and 802.11v BSS Transition Management (bss_transition_80211v).
  • Flags access points that advertise a Multiple BSSID set (mbssid, with the max_bssid_indicator) and that send Channel Switch Announcements (csa, with the csa_new_channel target channel).
  • Reveals cloaked (hidden) SSIDs from probe responses and (re)association requests, filling the AP name even when the beacon hides it (ssid_revealed marks names learned this way).

Install

From DockerHub (RECOMMENDED)

docker pull r4ulcl/wifi_db

Manual installation

Debian based systems (Ubuntu, Kali, Parrot, etc.)

Dependencies:

  • python3
  • python3-pip
  • tshark
  • hcxtools
sudo apt install tshark
sudo apt install python3 python3-pip

sudo apt install pkg-config libcurl4-openssl-dev libssl-dev zlib1g-dev make gcc


git clone https://github.com/ZerBea/hcxtools.git
cd hcxtools
make 
sudo make install
cd ..

Installation (using a virtual environment)

# Download repo
git clone https://github.com/r4ulcl/wifi_db
cd wifi_db

# Create and activate a venv
sudo apt update ; sudo apt install python3-venv
python3 -m venv wifi_db_env
source wifi_db_env/bin/activate

# Install dependencies
pip3 install -r requirements.txt

The venv must be activated (source wifi_db_env/bin/activate) in every new shell before running wifi_db.py. Use deactivate to leave it.

Arch

Dependencies:

  • python3
  • python3-pip
  • tshark
  • hcxtools
sudo pacman -S wireshark-qt
sudo pacman -S python-pip python

git clone https://github.com/ZerBea/hcxtools.git
cd hcxtools
make 
sudo make install
cd ..
Download Tool