Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
codoforum — CVE-2020-5842 Stored XSS Vulnerability in Codoforum 4.8.3 | Kitploit

Tools/GitHubGitHub/prasanthc41m/codoforum
Vulnerability AnalysisExploitationWeb Application ExploitationInformation GatheringPenetration TestingLearning & Education
GitHubprasanthc41m/codoforum

codoforum

CVE-2020-5842 Stored XSS Vulnerability in Codoforum 4.8.3

View Repository
1223 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.1k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    627
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    413
  • 4

    jumpserver

    jumpserver/jumpserver

    JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH, RDP, Kubernetes, Database and RemoteApp endpoints through a web browser.

    350
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    329
  • 6

    Aliens_eye

    arxhr007/aliens_eye

    AI powered OSINT engine to discover and map 7,700+ social media identities across the web

    283

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2020-5842 Stored XSS Vulnerability in Codoforum 4.8.3

Listed in: Exploit-db, Cve Mitre and The daily swig

While I was searching for a free forum software for our community I found Codoforum. After installing it We (Vyshnav Vizz) tried a few simple XSS payloads to ensure the security and suddenly got surprised with finding of multiple critical cross site scripting vulnerability which affects admin users. Thanks a lot my brother (Vyshnav Vizz) for supporting me throughout my life.

Affected component : User Registration page

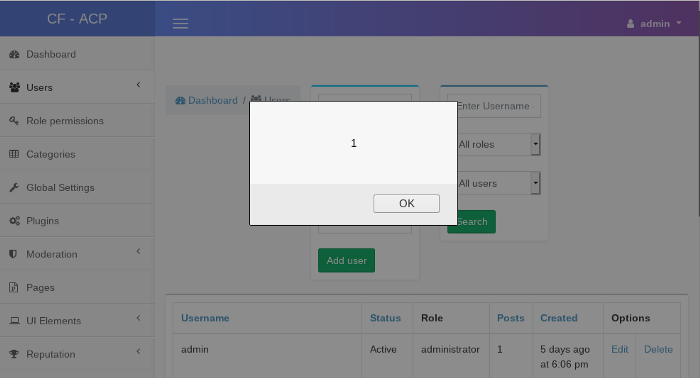
Attack vector This vulnerability can results attacker to inject the XSS payload in User Registration section and each time admin visits the manage user section from admin panel, the XSS triggers and attacker can able to steal the cookie according to the crafted payload.

Additional information A Critical (Stored XSS) Cross Site Scripting Vulnerability found in Codoforum v4.8.3 which is the latest version last updated on Oct 29th 2019.

Codoforum User registration mechanism is critically vulnerable to Stored Cross site scripting issue. A user can be created from register page using a crafted XSS payload in the user field. As a result a user will be created with XSS payload. If the admin visits the user manage section using admin dashboard section from manage user section XSS got triggers. Due to this Stored XSS vulnerability which stores in the server, each time admins visit the page the XSS payload got triggers.

Recreation Steps

  1. Download and Install Codoforum 4.8.3 in a local server. https://codoforum.com/buy image
  2. Browse http://localhost/index.php?u=/user/register and create a user with payload below.

Username : “><svg/onload=alert(1)> Password : password Email : [email protected] Injecting payload image

  1. Now browse http://localhost/admin/index.php?page=users/manage, a XSS will be triggered here. Stored XSS got triggered image

Mitigation

Input validation and output sanitization and escaping will make application safe.

Timeline

Discovered: Jan 3 2020 Reported to Codologic: Jan 3 2020 Acknowledged by Codologic: Jan 3 2020 Listed in exploit-db.com: Jan 6 2020 Listed in cve.mitre.org: Jan 6 2020


Download Tool