 pelock/powershell-pro-obfuscator-python
Automate PowerShell script source code obfuscation & virtualization with a flexible Web API for Python (pip package).

PowerShell Pro Obfuscator protects proprietary .ps1 scripts with renaming, polymorphic string and integer encryption, control-flow flattening, finite-state automata (FSA), a VM engine, self-defending integrity checks, a protection linker, and anti-debugging probes.
Obfuscate, virtualize & protect PowerShell .ps1 scripts with polymorphic string encryption, VM engine, finite-state automata transforms, self-integrity & anti-debugging checks — via GUI, CLI, online tool, or API.
More technical details, downloads, documentation available at:
https://www.pelock.com/products/powershell-pro-obfuscator
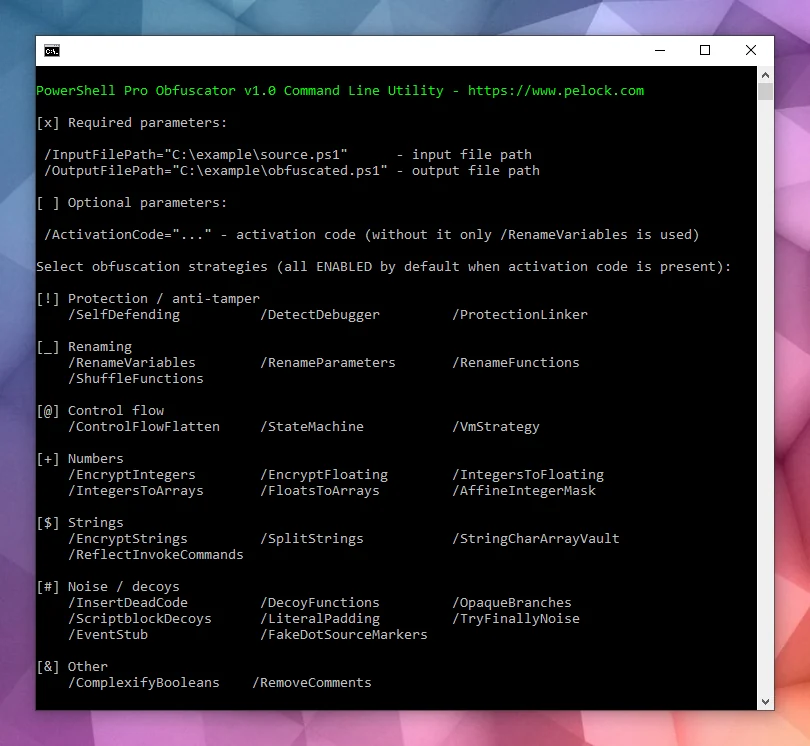
It's available for Windows & Linux:
Multiple programming APIs available:
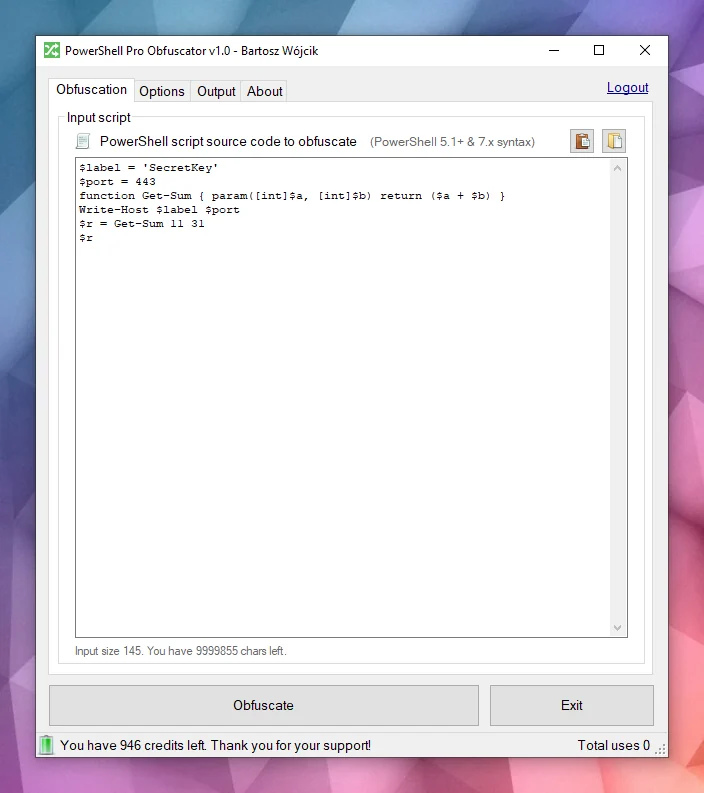
An online obfuscator interface:
Scripts are typically distributed as plain .ps1 files or embedded in modules. That convenience means anyone with file access can read the full logic, hunt for credentials or API keys in strings, and steal your algorithms unless you take extra steps to hide intent.
PowerShell is a cross-platform shell and scripting language built on .NET. It is widely used for automation, configuration, DevOps pipelines, and endpoint management on Windows and Linux.
PowerShell Pro Obfuscator comes with many advanced obfuscation, virtualization & protection strategies. You can easily tune protection versus size and performance.
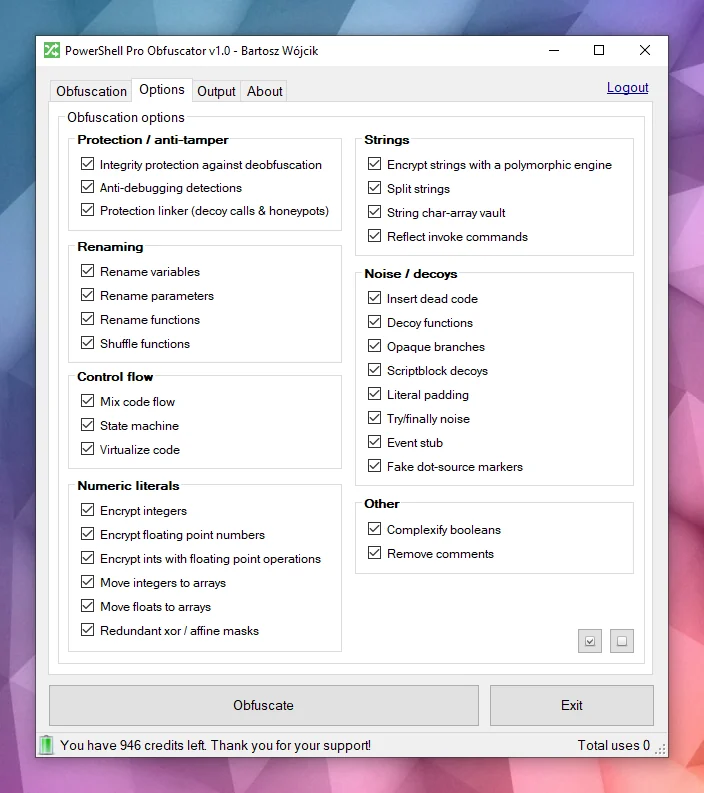
 Powerful obfuscation
PowerShell Pro Obfuscator uses state-of-the-art obfuscation strategies such as polymorphic string encryption, integers & floats encryption, and decoy noise. The result conceals literals and structure while preserving tested runtime behaviour.
 Code virtualization
Selected statements are lifted into a random generated VM engine opcodes with shuffled switch cases, decoy opcodes, and an obfuscated dispatcher loop. Analysts must interpret the virtual machine instead of reading plain PowerShell.
 Finite-state automata (FSA)
 obfuscation rewrites linear PowerShell statement blocks into dual-state automata with opaque schedulers and shuffled dispatch handlers. Instead of reading code top to bottom, analysts must follow numeric states, transition tables, and decoy paths to reconstruct the original order.
 Anti-debugging
 protection inserts polymorphic probes that detect attached debuggers, PowerShell breakpoints, debug preference and tracing modes, and related host signals. When a check fires, the obfuscated script exits silently instead of revealing protected logic under interactive analysis.
 Self-integrity checks
A bootstrap probe verifies on-disk script shape (function counts and integrity tokens) and sets a tamper key when the file no longer matches the obfuscated build. String decryptors consume that key, so patched scripts return garbage instead of plaintext. This self-defending layer raises the cost of casual deobfuscation and file edits.
 Protection linker
A late pass wires honeypot resolvers, bogus helper calls with random arguments, and shallow-stack tripwires that stay active only before bootstrap completes. Extracted snippets keep noisy call surfaces that look real under static review. Normal execution after a successful integrity check remains unchanged.
Look at this example — the same script becomes harder to read at a glance after obfuscation.
function Get-Greeting {
    param([string]$Name)
    Write-Host "Hello World from $Name!"
}
Get-Greeting "PowerShell Pro Obfuscator"
