

 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets



Welcome to the OWASP WrongSecrets game! The game is packed with real life examples of how to not store secrets in your software. Each of these examples is captured in a challenge, which you need to solve using various tools and techniques. Solving these challenges will help you recognize common mistakes & can help you to reflect on your own secrets management strategy.
Can you solve all the 72 challenges?
Try some of them on our Heroku demo environment.
Want to play the other challenges? Read the instructions on how to set them up below.
New to WrongSecrets? Start here:
docker run -p 8080:8080 -p 8090:8090 jeroenwillemsen/wrongsecrets:latest-no-vault
docker run -p 8080:8080 -p 8090:8090 ghcr.io/owasp/wrongsecrets/wrongsecrets-master:latest-master
What you'll learn:
How it works: This repository contains intentionally vulnerable code and configuration files with real and fake secrets hidden throughout the codebase. You'll examine source code, configuration files, Docker containers, and cloud deployments to discover these secrets. Each challenge teaches you different ways secrets can be accidentally exposed in real-world applications.
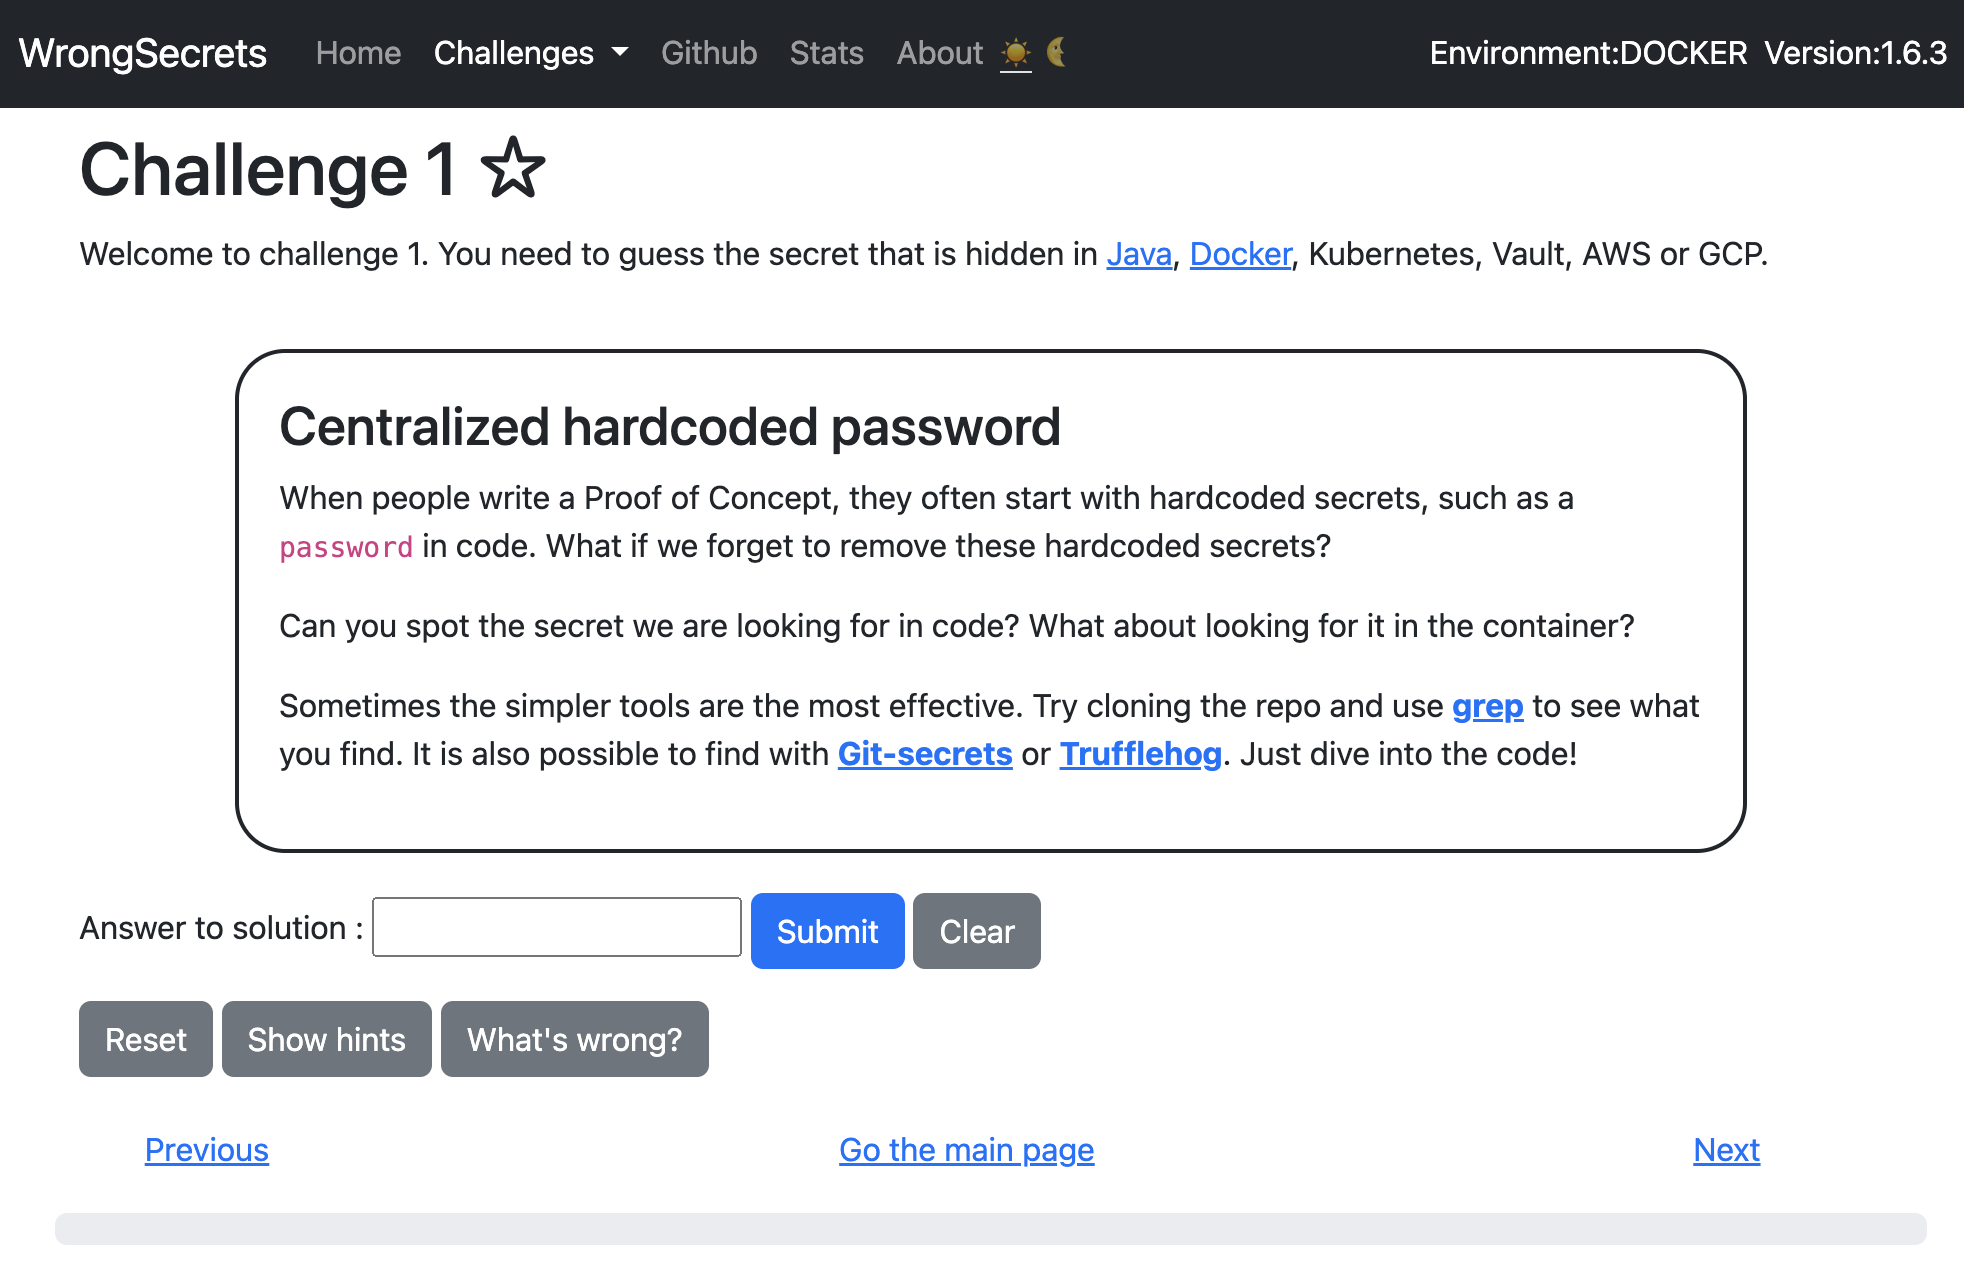
For basic usage:
For advanced setups:

