 nextronsystems/gimphash
Imphash-like calculation on Golang binaries

gimphash is a proposed method to calculate an imphash equivalent for Go binaries. It's name stands for Go-import-hash.
Golang binaries contain their dependencies as part of the executable. These dependencies include both standard library packages and third party dependencies and can be used, analogous to a classical imphash, to identify a Golang project.
The dependencies can be listed using the pclntab that is part of each Golang binary (also see this blog post by Mandiant). The pclntab contains a number of interesting elements for reverse engineering; for the gimphash we will use the function names that are contained there.
go. or type. (compile artefacts, runtime internals)vendor/, discard that substring and everything before it
(e.g. transform vendor/golang.org/x/text to golang.org/x/text)internal/runtimesyncsyscalltypetimeunicodereflectstrconv/ in the function name. If no / is found, use the start instead. Starting from that position, find the next .... If no . was found, use everything after the / index calculated in the previous step.. exists within the base function name, ignore the function if the first alphanumeric character after that . is a lower case character.This repository contains proof-of-concept code in the following languages:
The release section contains prebuilt binaries for Windows and Linux.
Run the Gimphash calculator on a single file
./c_gimphash_linux /mnt/malware-repo/Godoh/godoh-windows64.exe
8200e76e42c4e9cf2bb308d76c017cbdcde5cbbf95e99e02b14d05e7b21505f3 /mnt/mal/Godoh/godoh-windows64.exe
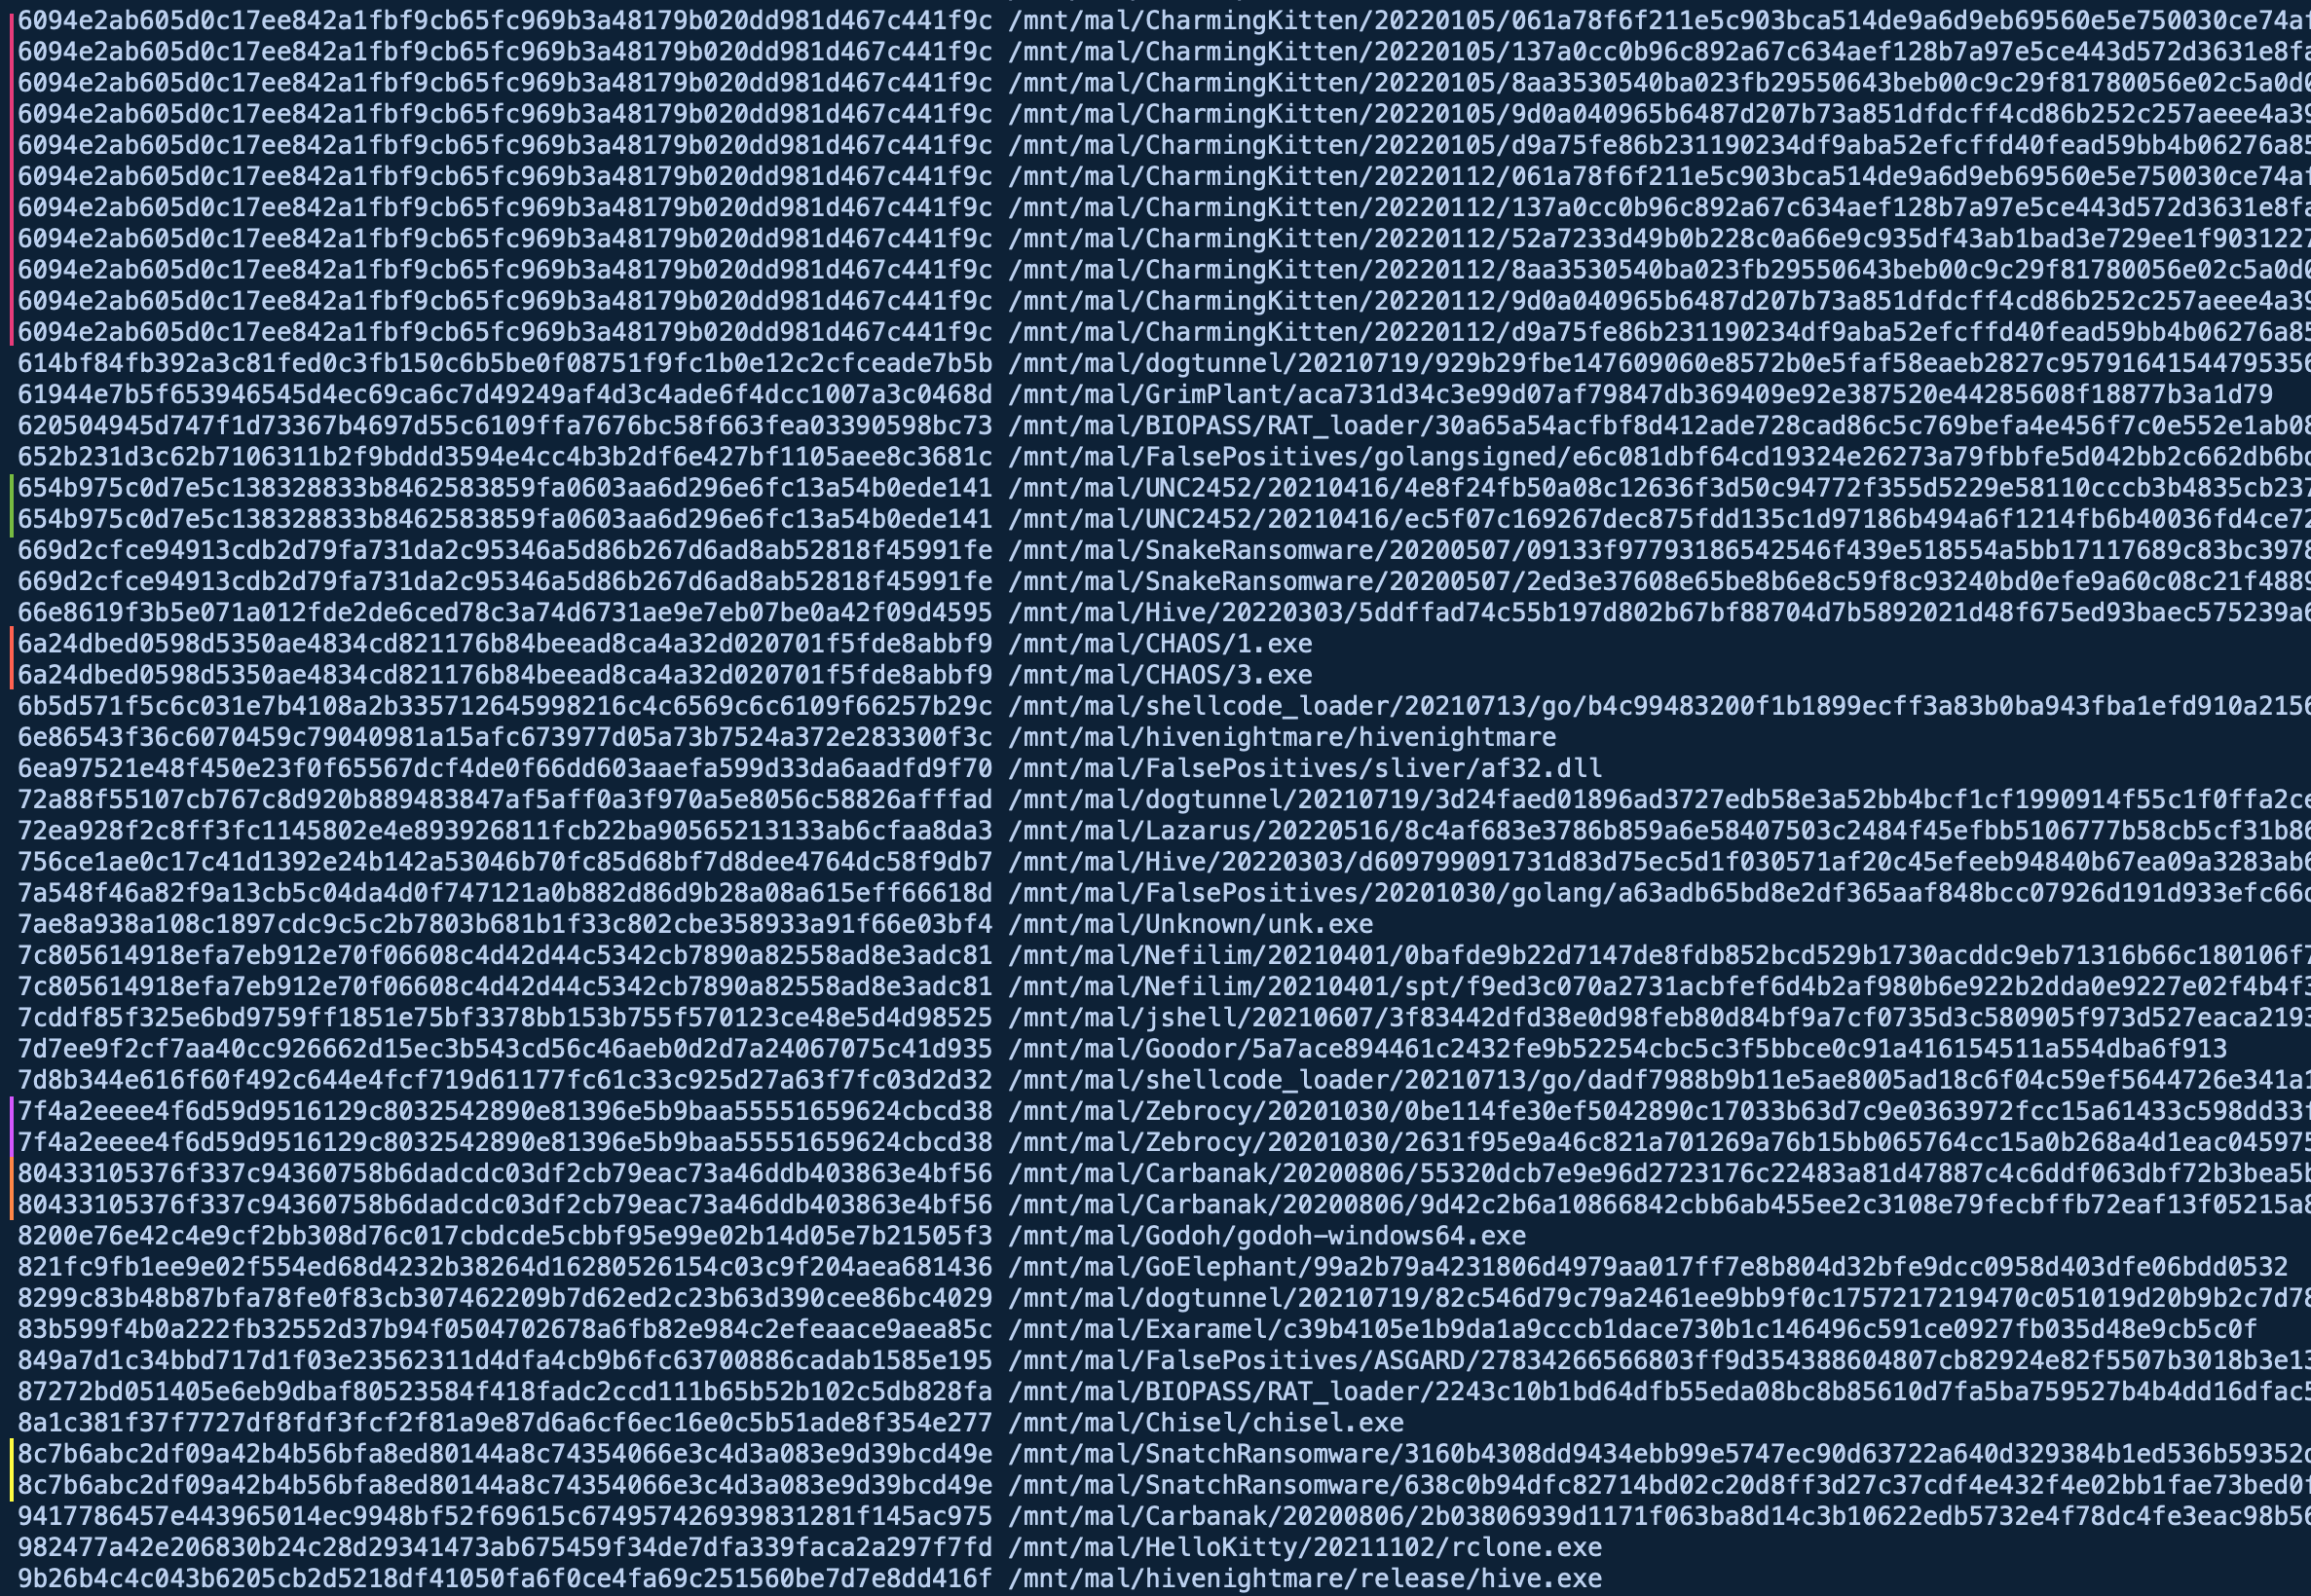
Run the Gimphash calculator on a malware repository
find /mnt/malware-repo/ -type f -exec ./go_gimphash_linux {} \; 2>/dev/null
...

