Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/ncsa/ssh-auditor
Vulnerability ScannersPassword AttacksNetwork Security
GitHubncsa/ssh-auditor

ssh-auditor

The best way to scan for weak ssh passwords on your network

View Repository
62086305 years agoReviewed by Kitploit
Share

Build Status

SSH Auditor

Features

ssh-auditor will automatically:

  • Re-check all known hosts as new credentials are added. It will only check the new credentials.
  • Queue a full credential scan on any new host discovered.
  • Queue a full credential scan on any known host whose ssh version or key fingerprint changes.
  • Attempt command execution as well as attempt to tunnel a TCP connection.
  • Re-check each credential using a per credential scan_interval - default 14 days.

It's designed so that you can run ssh-auditor discover + ssh-auditor scan from cron every hour to to perform a constant audit.
Demos

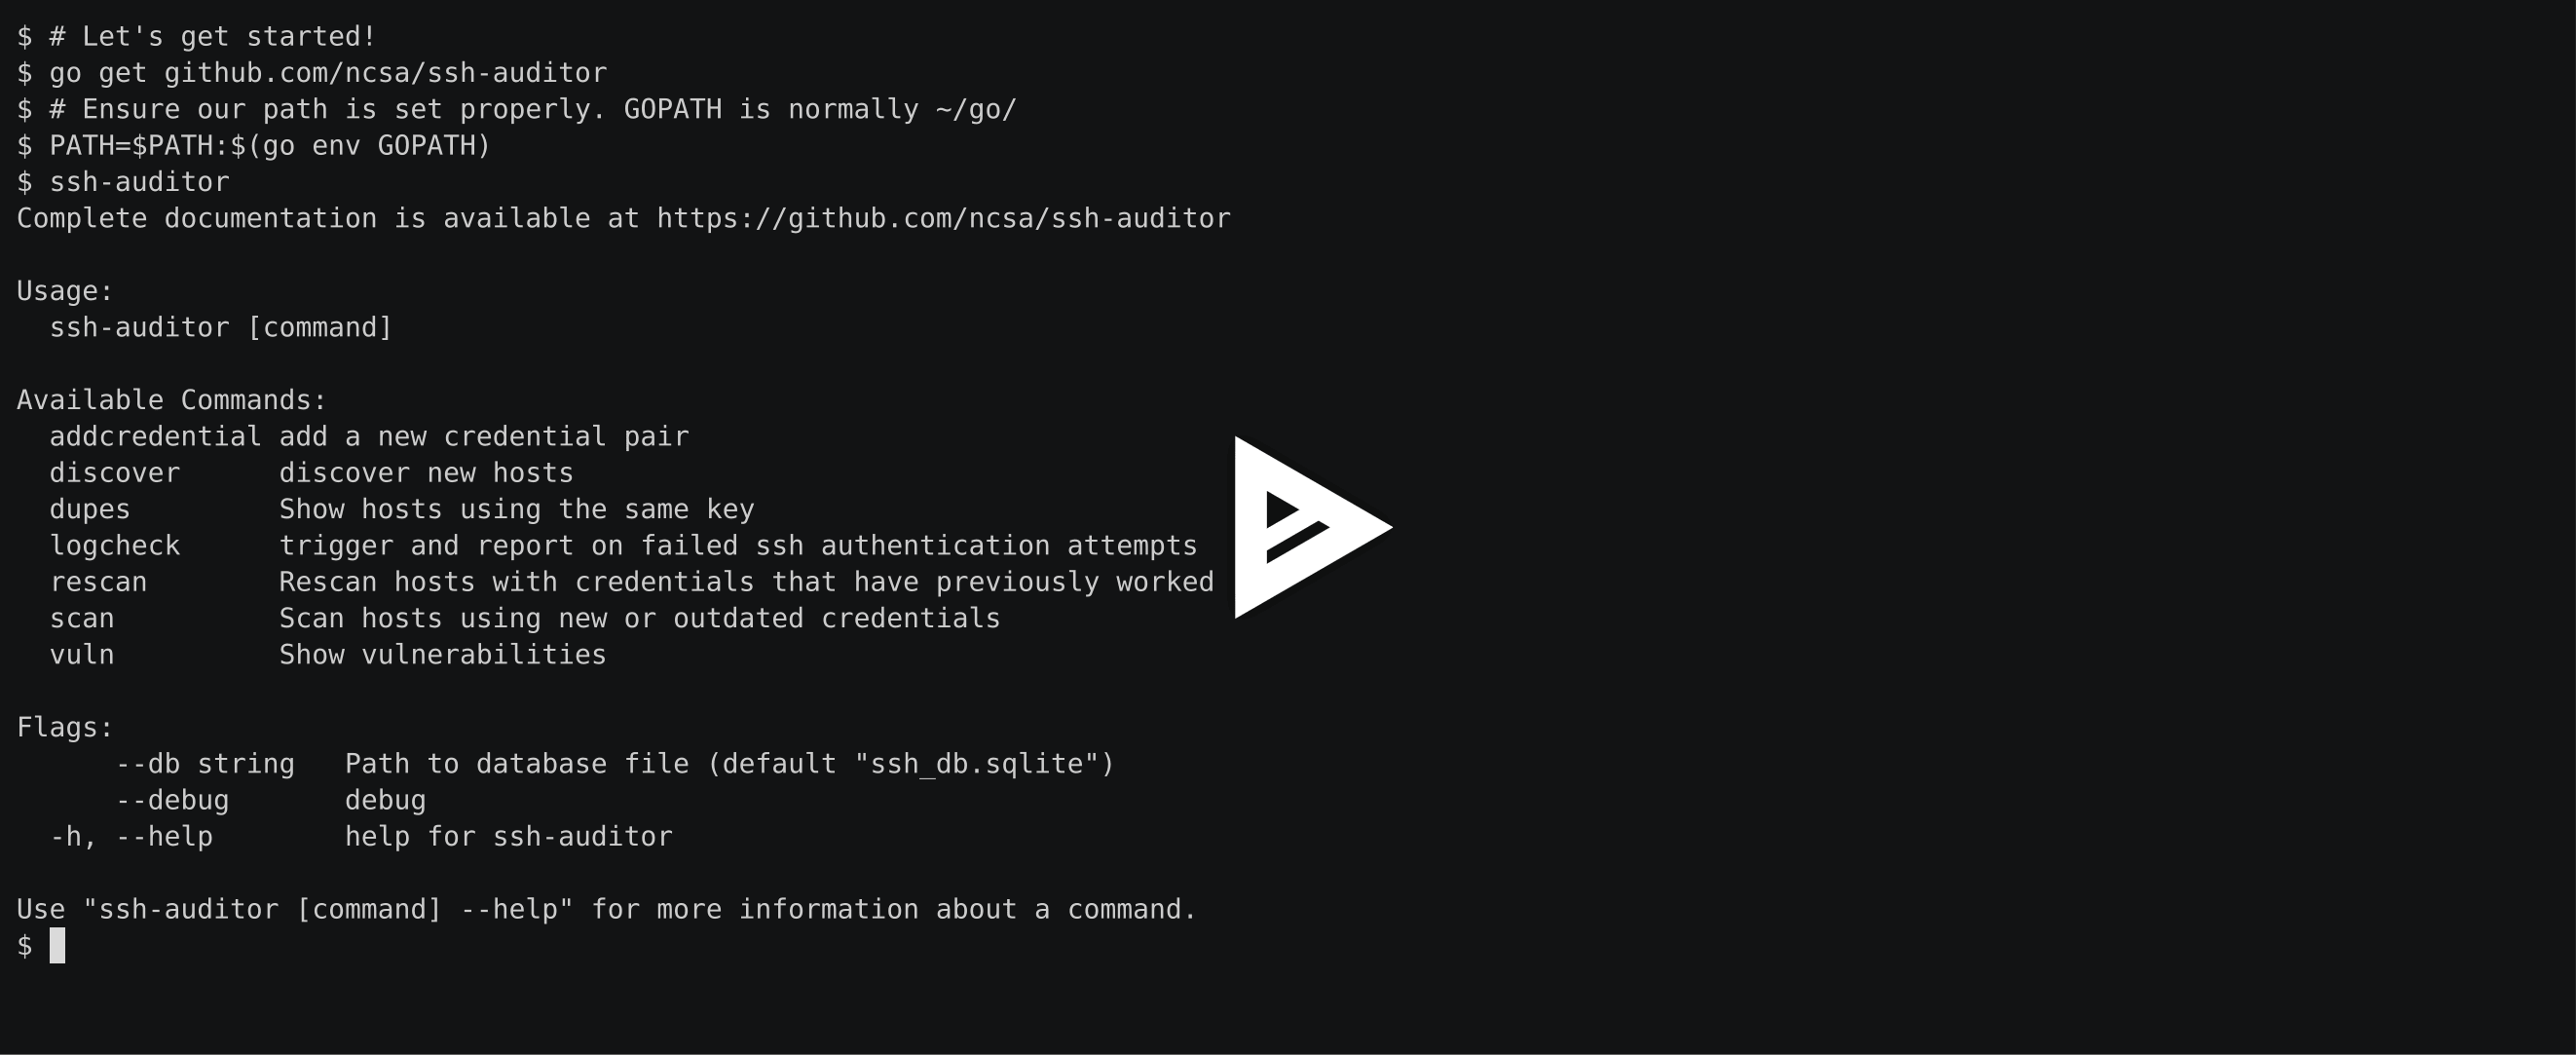
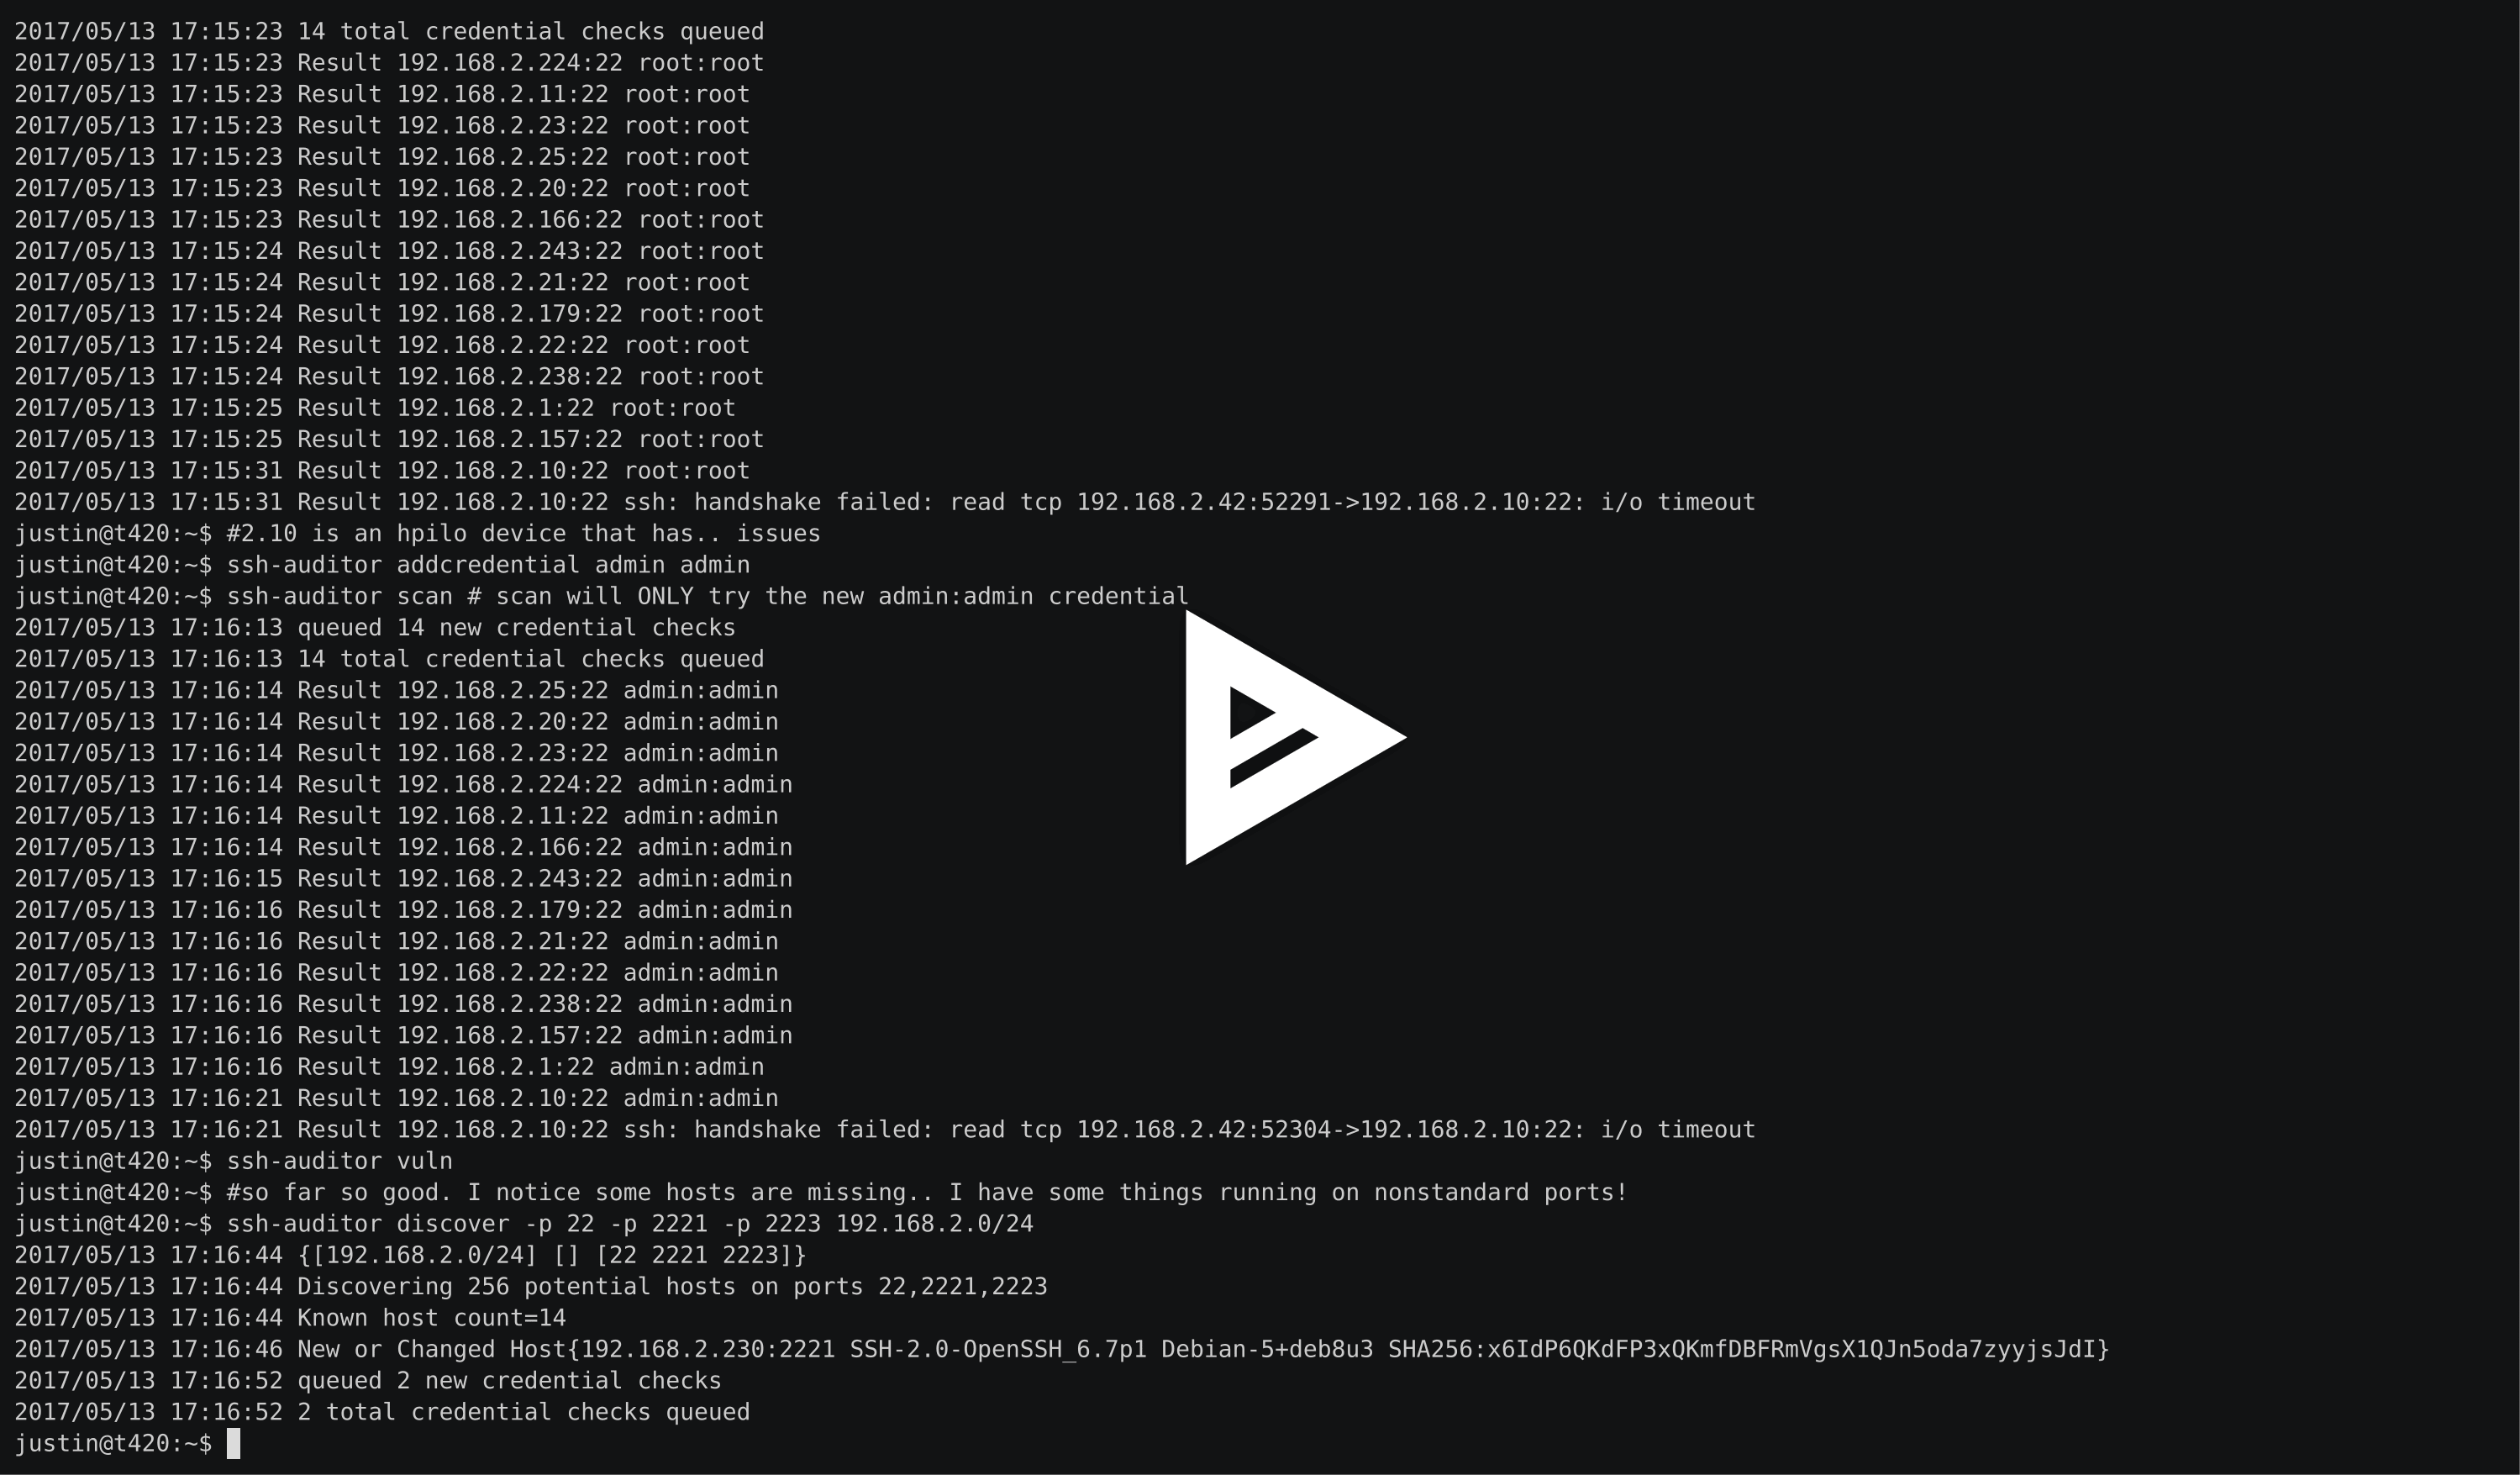
Earlier demo showing all of the features

demo

Demo showing improved log output

demo

Usage

Install

$ brew install go # or however you want to install the go compiler
$ go get github.com/ncsa/ssh-auditor

or Build from a git clone

$ go build

Build a static binary including sqlite

$ make static

Ensure you can use enough file descriptors

$ ulimit -n 4096

Create initial database and discover ssh servers

$ ./ssh-auditor discover -p 22 -p 2222 192.168.1.0/24 10.0.0.1/24

Add credential pairs to check

$ ./ssh-auditor addcredential root root
$ ./ssh-auditor addcredential admin admin
$ ./ssh-auditor addcredential guest guest --scan-interval 1 #check this once per day

Try credentials against discovered hosts

$ ./ssh-auditor scan

Output a report on what credentials worked

$ ./ssh-auditor vuln

RE-Check credentials that worked

$ ./ssh-auditor rescan

Output a report on duplicate key usage

$ ./ssh-auditor dupes

TODO

  • update the 'host changes' table
  • handle false positives from devices that don't use ssh password authentication but instead use the shell to do it.
  • variable re-check times - each credential has a scan_interval in days
  • better support non-standard ports - discover is the only thing that needs to be updated, the rest doesn't care.
  • possibly daemonize and add an api that bro could hook into to kick off a discover as soon as a new SSH server is detected.
  • make the store pluggable (mysql, postgresql).
  • differentiate between a failed password attempt and a failed connection or timeout. Mostly done. Things like fail2ban complicate this.
  • add go implementations for the report sqlite3 command.

Report query.

This query that ssh-auditor vuln runs is

select
        hc.hostport, hc.user, hc.password, hc.result, hc.last_tested, h.version
 from
        host_creds hc, hosts h
 where
        h.hostport = hc.hostport
 and    result!='' order by last_tested asc

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    806
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    523
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    441
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    270
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    264

Explore all tools

Browse our collection of tools

View all tools →